
CVE-2026-87796
 abraxas/cve-2026-87796
Reproduction pack and PoC script for CVE-2026-87796, an unauthenticated arbitrary file upload RCE in Multi Uploader for Gravity Forms <= 1.1.9, with…
educationexploitationlabs-practice+6
abraxas/cve-2026-87796Reproduction pack and PoC script for CVE-2026-87796, an unauthenticated arbitrary file upload RCE in Multi Uploader for Gravity Forms <= 1.1.9, with…
 dzmind2312/mass-cve-2026-23550-exploit
Multi-threaded Python scanner for CVE-2026-23550, detecting unauthenticated admin takeover in WordPress Modular DS plugin with full wp-admin…
 sachinart/cve-2025-61882
Multi-threaded scanner for CVE-2025-61882 in Oracle E-Business Suite, exploiting HTTP request smuggling to achieve unauthenticated remote code…
 zedxod/cve-2026-41940-poc
Proof-of-concept exploit for CVE-2026-41940, demonstrating authentication bypass in cPanel/WHM via CRLF injection and session poisoning to gain…
 graysignal/cve-2024-28995-solarwinds-serv-u
Exploit for CVE-2024-28995 affecting SolarWinds Serv-U 15.4.2 HF 1 and previous versions
 graysignal/cve-2024-4040-crushftp-server
Exploit for CVE-2024-4040 affecting CrushFTP server in all versions before 10.7.1 and 11.1.0 on all platforms
 k3ystr0k3r/intrack
A flexible internet crawler used for scanning technologies, instances and vulnerabilities worldwide across the internet.
 blue0x1/xpath
xpath is a fast, multi-technique XPath injection scanner written in Nim. It focuses on practical detection, response comparison, visible extraction,…
 ef3tr/cve-2026-4106
WordPress HTMega Unauthenticated PII Disclosure Exploit (CVE-2026-4106)
 smaash/fuckshitup
php-cli vulnerability scanner
 yezeting/cve-2021-41730
Proof-of-concept exploit for CVE-2021-41730, demonstrating remote command execution in TENDA AC15/AC6 routers via unvalidated formSetIptv()…
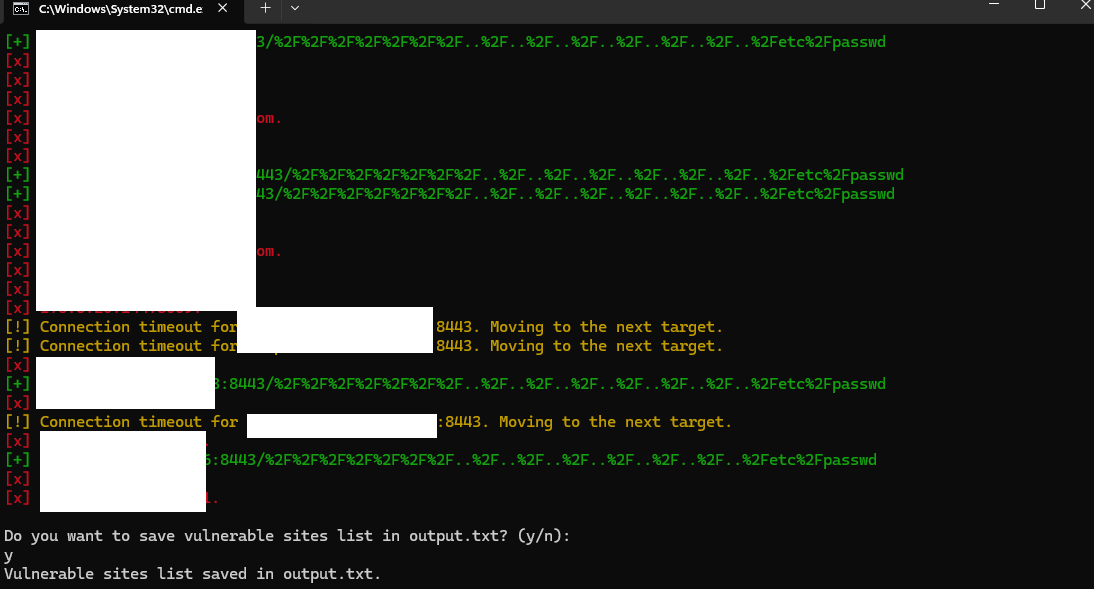 goatsecurity/cve-2024-4956
CVE-2024-4956 : Nexus Repository Manager 3 poc exploit
 sumanrox/rschunter
Mass Hunting & Exploitation PoC for CVE-2025-55182 & CVE-2025-66478
 jsec1337/rce-cve-2020-5902
BIG-IP F5 Remote Code Execution
 madexploits/ninja-form-exploit
CVE-2026-0740
 kouf320/docker-lab-cve-2017-5638-cve-2021-41773
Docker-based multi-stage attack emulation lab demonstrating CVE-2017-5638 and CVE-2021-41773 exploitation, lateral movement, and Suricata IDS…
 jenderal92/cve-2026-8181
CVE-2026-8181: Burst Statistics Auth Bypass → REST API takeover & admin creation. Python 2.7. Educational use only.
 mrsol0/cve-2025-55182-terminal
This is a POC for testing your projects that are vulnerable to CVE-2025-55182 with a terminal and ability to scan a list