
CVE-2026-29053
 k3ystr0k3r/cve-2026-29053
Python PoC and version scanner for CVE-2026-29053, an authenticated RCE in Ghost CMS below 6.19.1 via malicious Handlebars theme templates.
exploitationpayload-developmentpenetration-testing+5
1
k3ystr0k3r/cve-2026-29053Python PoC and version scanner for CVE-2026-29053, an authenticated RCE in Ghost CMS below 6.19.1 via malicious Handlebars theme templates.
 zined/cve-2023-4762
Proof-of-concept exploit for CVE-2023-4762, a Chromium V8 type confusion vulnerability enabling remote code execution via crafted JavaScript.
 r3vpwnx/cve-2025-58434
Exploit chain for Flowise 3.0.5: unauthenticated account takeover via password-reset token disclosure (CVE-2025-58434) chained to CustomMCP…
 venablee/cve-2026-30251
Reflected XSS vulnerability disclosure for ZenShare Suite login_newpwd.php, allowing arbitrary JavaScript execution via crafted URL in codice_azienda…
 mbanyamer/cve-2026-27574-oneuptime-rce
Proof-of-concept exploit for CVE-2026-27574, a critical code injection in OneUptime enabling remote code execution and environment variable leakage.
 r3db34rdh4x/cve-2024-21683-rce
Exploit for CVE-2024-21683, a post-authentication remote code execution vulnerability in Atlassian Confluence Server and Data Center, allowing…
 galaxy-sc/cve-2026-23830-sandbreak
Generates and delivers exploit payloads for CVE-2026-23830, a SandboxJS escape, with modes for blind OOB exfiltration and local calc PoC. Supports…
 bfdfhdsfdd-crypto/cve-2026-22444
Exploit for Apache Solr CVE-2026-22444, leveraging UNC path injection and SMB server to achieve remote code execution via malicious configset and…
 defineid/wildfire
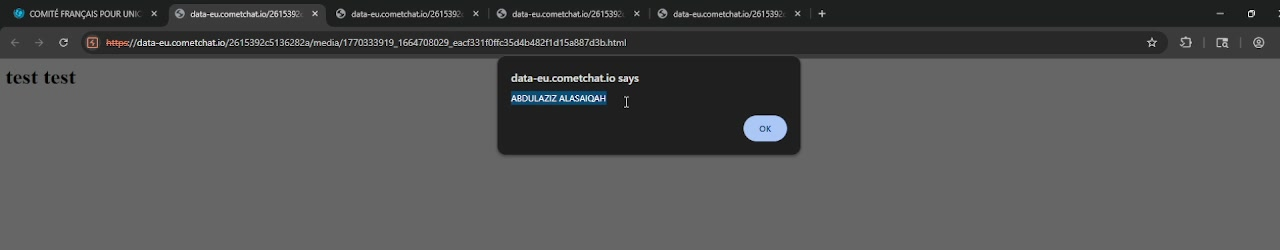
CVE-2026-39154, Stored XSS in CometChat JS SDK
 alixploit22/cvex2shel
CVE-2026-64638 adalah kerentanan Pre-Auth Reflected Cross-Site Scripting (XSS) di WordPress yang ditemukan pada tahun 2026. Kerentanan ini…
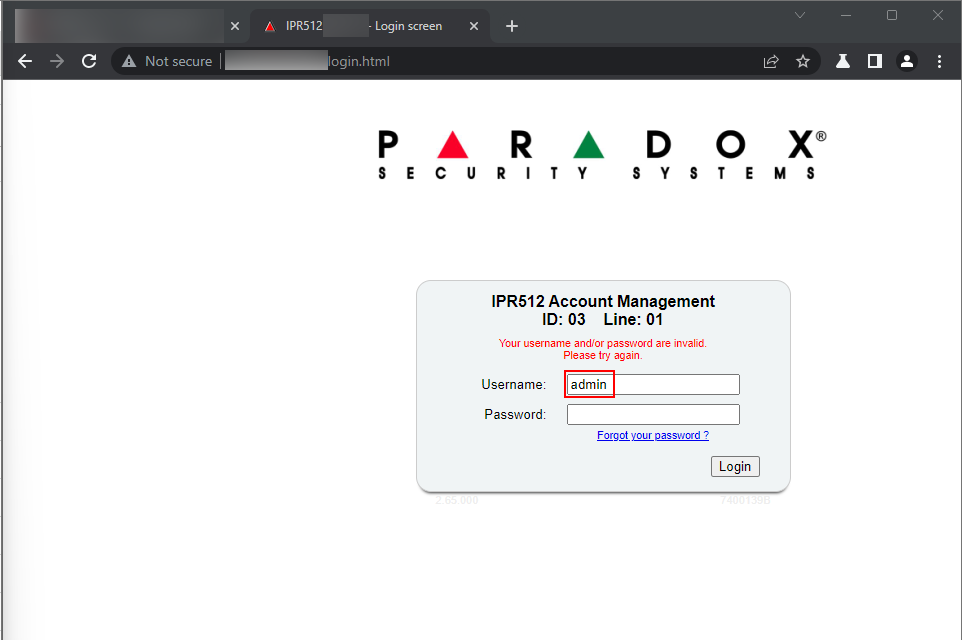 darknesschieftain/injection-vulnerability-in-paradox-security-systems-ipr512-cve-2023-24709-poc
In Paradox Security System IPR512 Web console login form page, attacker can input JavaScript string, such as "</script>" that will overwrite…
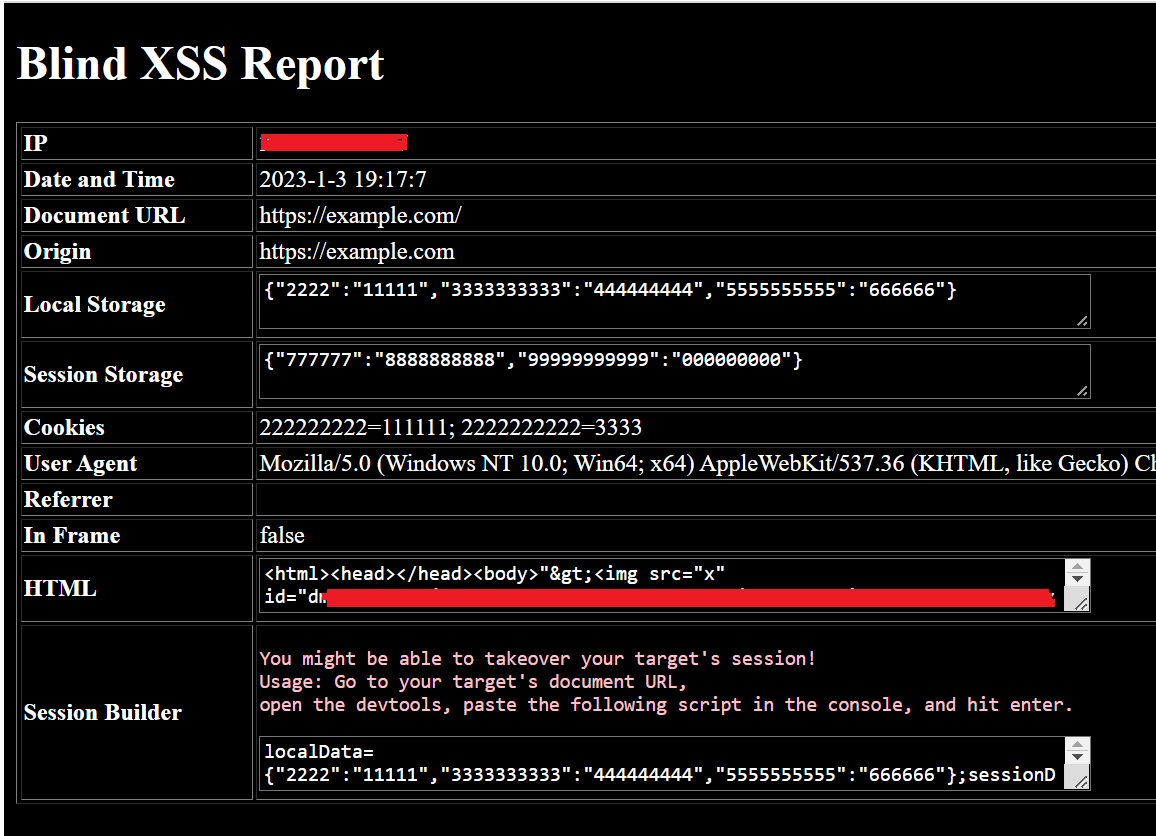 seifelsallamy/xssfire
A standalone Blind XSS Script.
 0xdak/cve-2026-67340_exploit
Post-auth RCE exploit for ArcadeDB via JavaScript trigger GraalVM sandbox escape, executing OS commands over HTTP API with reverse shell or blind…
 h3x0v3rl0rd/nodejsshell
Node.js reverse shell payload generator for penetration testing. Creates bind and reverse shells in JavaScript.
 se1zer/nextjs_exploit_tool
Next.js RSC RCE Exploit Tool (CVE-2025-55182)
 raphy76/wp2shell-poc-fulljs
full javascript reproduction of CVE-2026-63030 (author_exclude, author__not_in and misalignment between validations and matches)
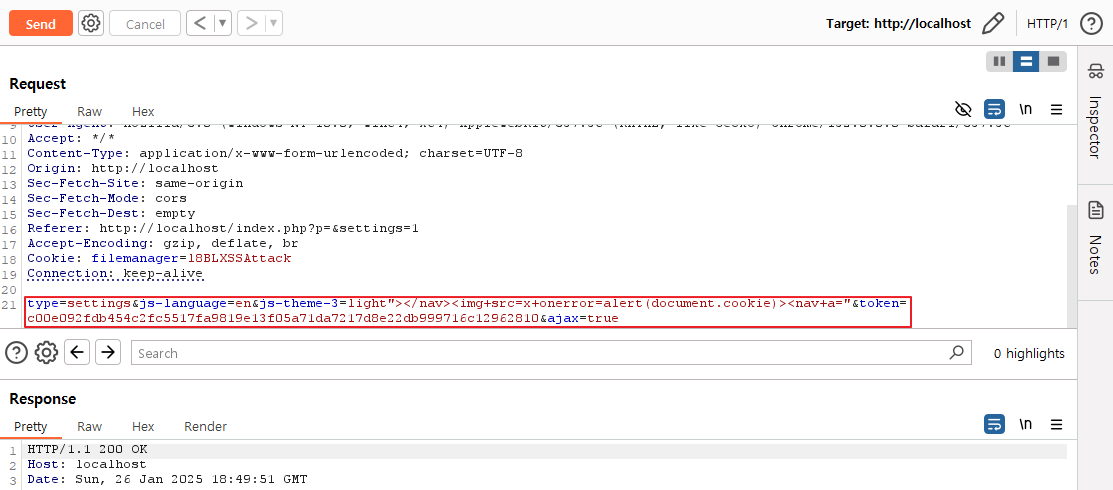 l8bl/cve-2025-44998
Proof-of-concept exploit for a stored XSS vulnerability in TinyFileManager v2.4.7, enabling arbitrary JavaScript execution and session cookie…
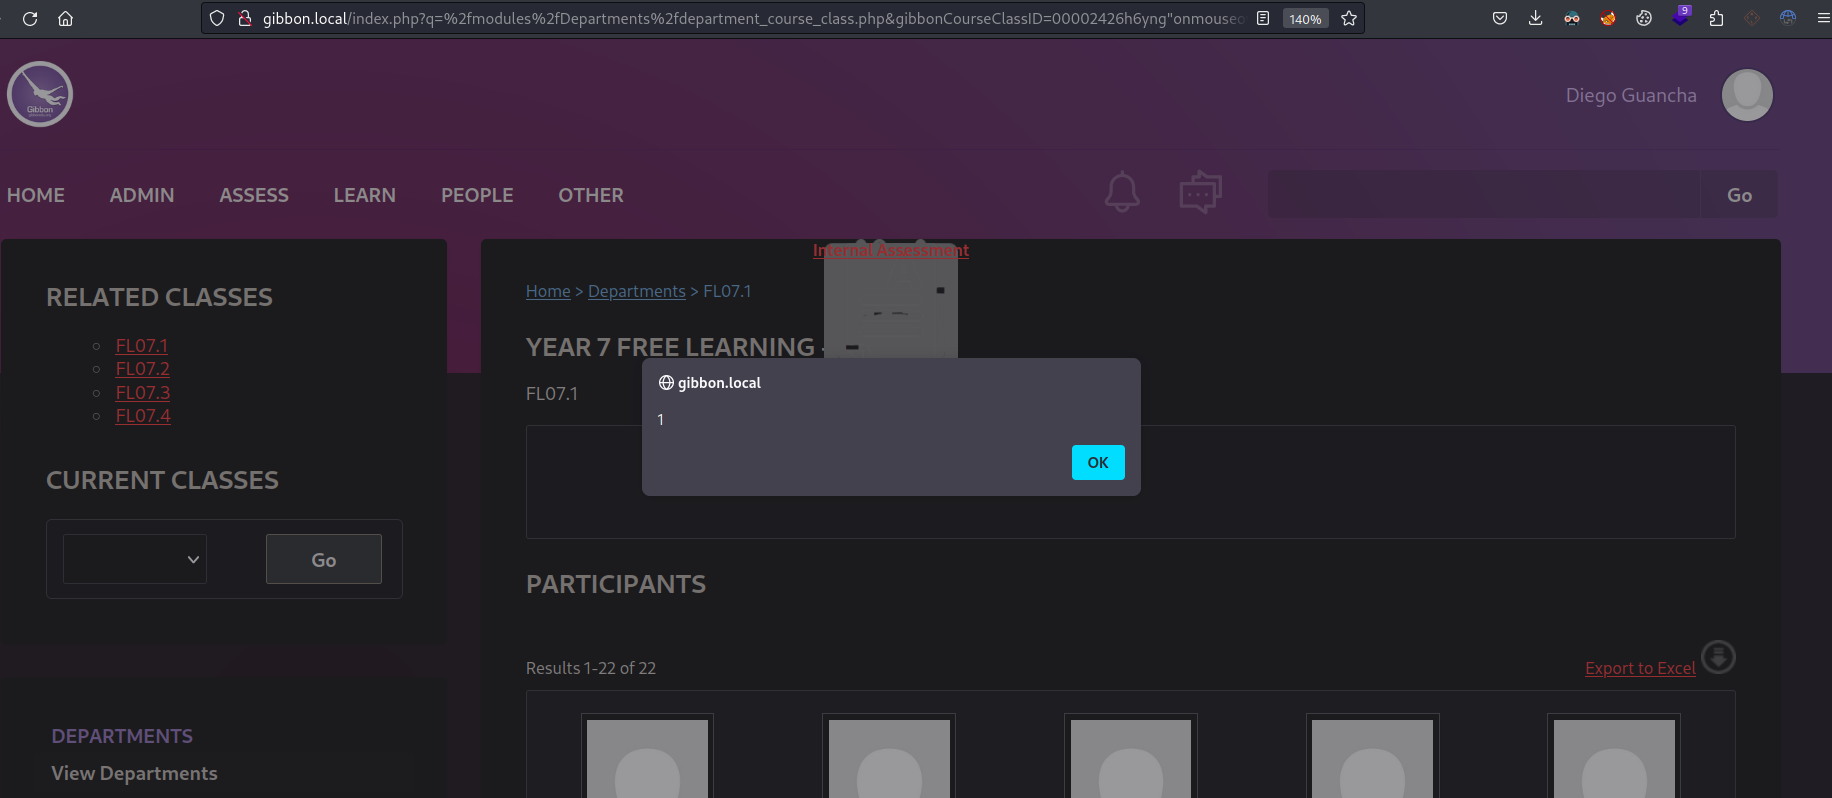 maddsec/cve-2023-34599
Multiple Cross-Site Scripting (XSS) vulnerabilities have been identified in Gibbon v25.0.0, which enable attackers to execute arbitrary Javascript…