
comfyui-CVE-2026-68771-PoC
 oscar-collado/comfyui-cve-2026-68771-poc
Security research lab — Unauthenticated RCE via insecure deserialization in ComfyUI v0.23.0 (CVSS 9.8). Isolated Docker environment, technical…
ai-securityeducationexploitation+3
oscar-collado/comfyui-cve-2026-68771-pocSecurity research lab — Unauthenticated RCE via insecure deserialization in ComfyUI v0.23.0 (CVSS 9.8). Isolated Docker environment, technical…
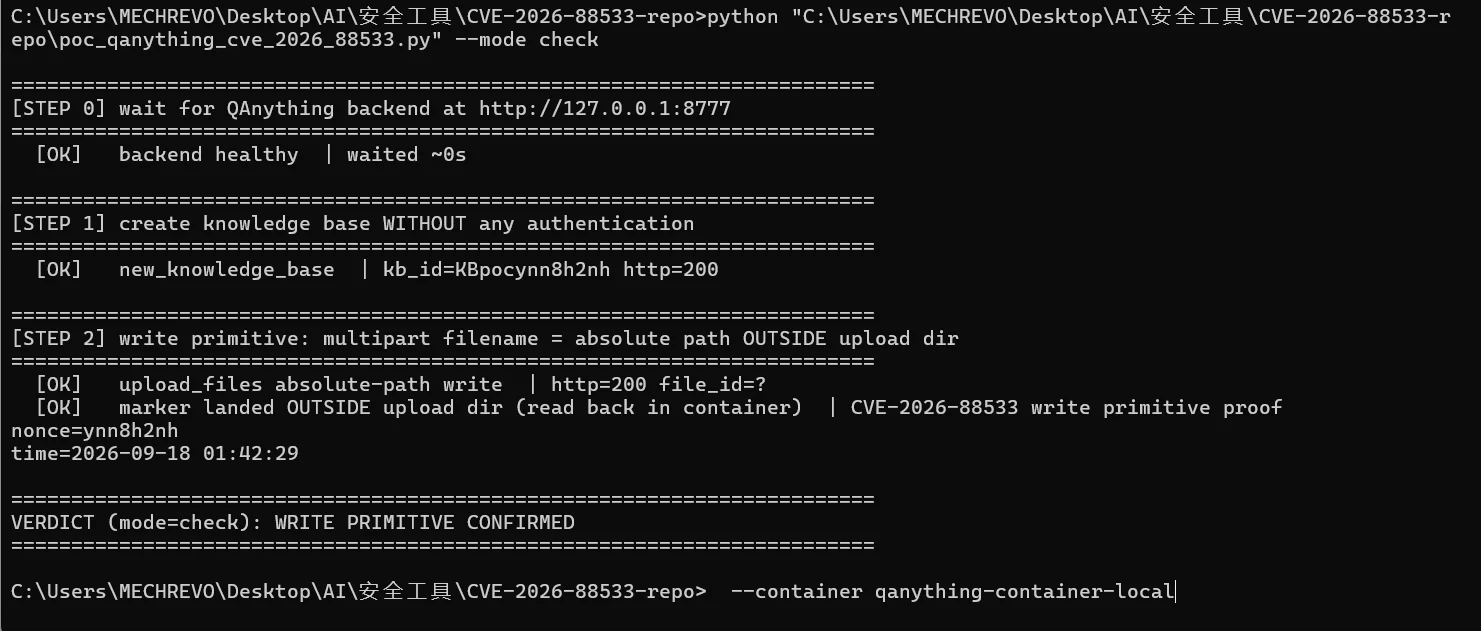 hemlock-lyk/cve-2026-88533
PoC and lab reproduction for CVE-2026-88533, an unauthenticated arbitrary file write leading to root RCE in QAnything via path traversal in the…
 oscar-collado/langflow-cve-2026-17633-poc
PoC for CVE-2026-17633 — Authenticated RCE in IBM Langflow OSS 1.0.0–1.10.3 via custom_component endpoint. Includes CVE-2026-17632 AST scanner bypass…
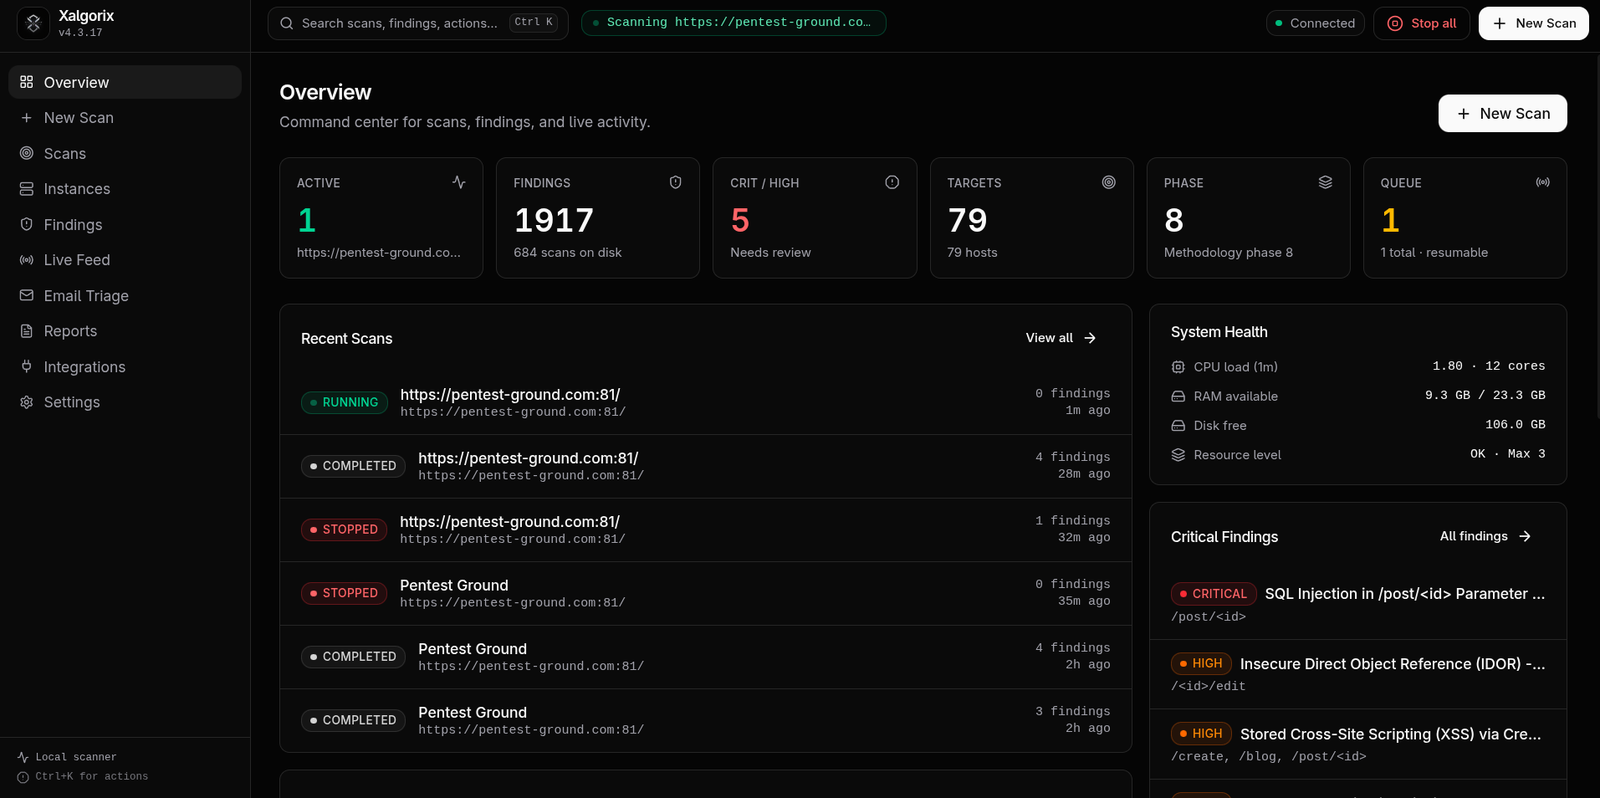 xalgorix/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.
 bugbasesecurity/pentest-copilot
AI-driven penetration testing agent that connects to a Kali box, autonomously runs security tools, analyzes results, and iterates through…
 fortbridge/stylesmuggler
Python PoC reproducing CVE-2026-75650 StyleSmuggler, an unauthenticated Magento RCE via report poisoning and failed-payment rendering, with canary…
 ghxstsec/cve-2026-39987
Exploit for Marimo pre-auth RCE via terminal WebSocket, providing command execution, interactive PTY shell, and reverse shell capabilities for…
 mbanyamer/cve-2026-25939-scada-fuxa-unauthenticated-remote-arbitrary
Proof-of-concept exploit for CVE-2026-25939, an unauthenticated authorization bypass in FUXA SCADA software allowing arbitrary scheduler manipulation…
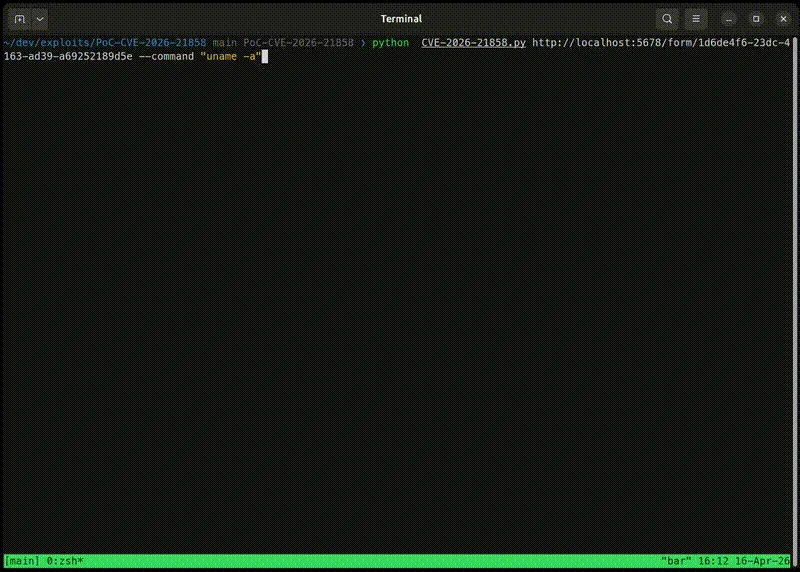 masterwok/poc-cve-2026-21858
Proof-of-concept exploit for CVE-2026-21858 (ni8mare) impacting n8n versions < 1.121.0
 keraattin/cve-2026-39987
Detection and exploitation toolkit for CVE-2026-39987, a pre-auth RCE in Marimo notebooks. Includes Python scanner and Nmap NSE script to identify…
 enzocipher/cve-2025-25198
Captures password reset tokens from Mailcow Host header injection attacks.
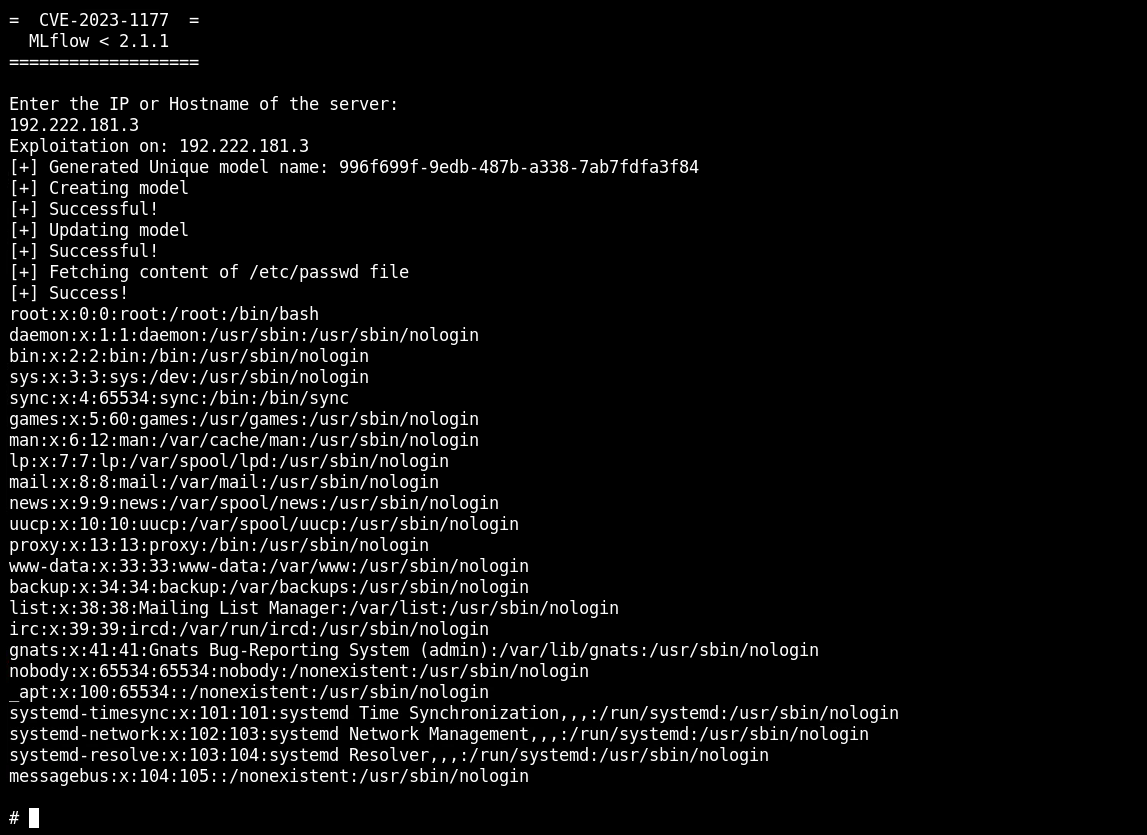 alphandbelt1/cve-2023-1177-mlflow
Proof-of-concept exploit for CVE-2023-1177, a path traversal vulnerability in MLflow, demonstrating unauthorized file access via crafted model names.
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
 graysignal/apache-ofbiz-auth-bypass-and-rce-exploit-cve-2023-49070-cve-2023-51467
This exploit scans whether the provided target is vulnerable to CVE-2023-49070/CVE-2023-51467 and also exploits it depending on the choice of the…
 graysignal/cve-2024-38856-apacheofbiz
Exploit for CVE-2024-38856 affecting Apache OFBiz versions before 18.12.15
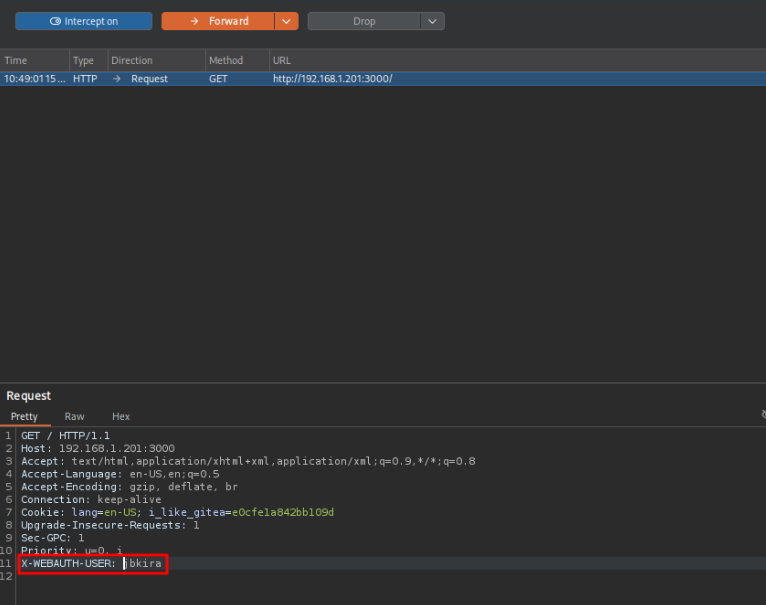 judgedbykira/cve-2026-20896-gitea-authentication-bypass
An explanation and PoC to exploit CVE-2026-20896 Authentication Bypass Vulnerability on Gitea. Being able to steal session tokens for valid users in…
 judgedbykira/cve-2026-25938-fuxa-unauthenticated-rce
An explanation and PoC to exploit CVE-2026-25938 Unauthenticated RCE Vulnerability on FUXA
 tennc/webshell
This is a webshell open source project