
dotdotpwn
 wireghoul/dotdotpwn
DotDotPwn - The Directory Traversal Fuzzer
fuzzinginformation-gatheringnetwork-security+3
wireghoul/dotdotpwnDotDotPwn - The Directory Traversal Fuzzer
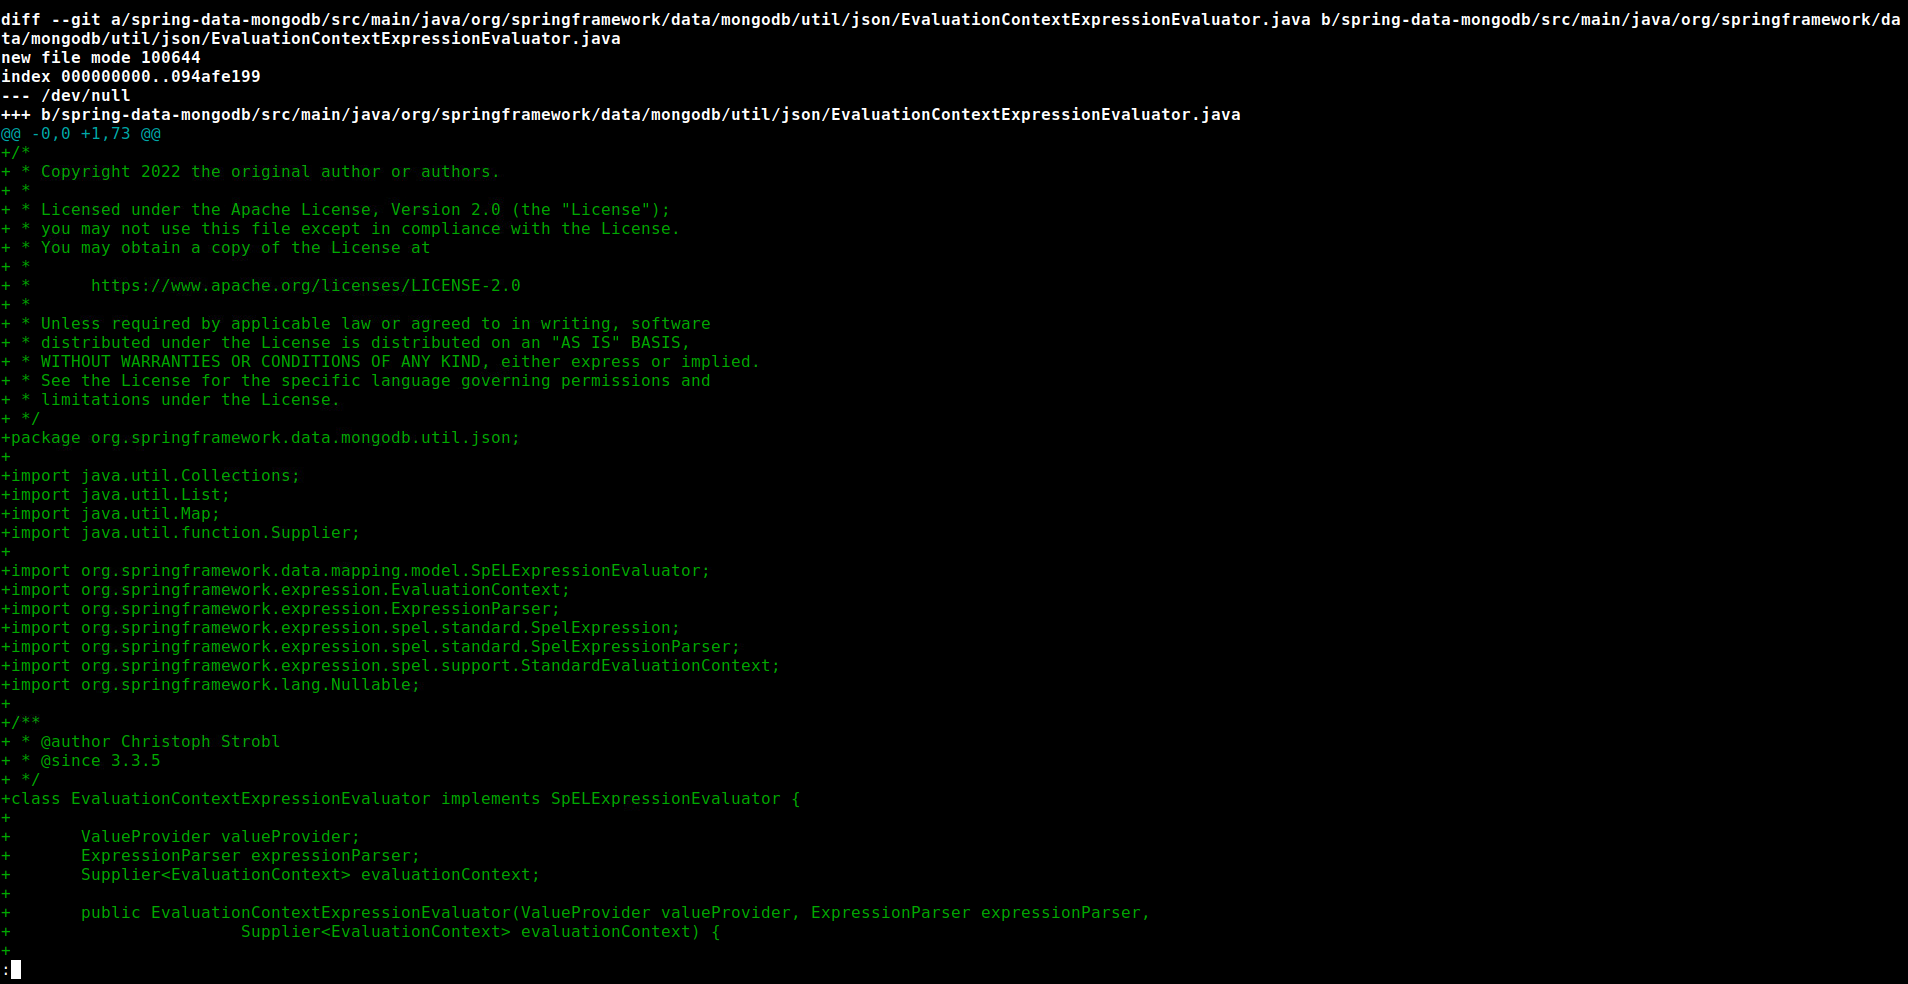 murataydemir/cve-2022-22980
[CVE-2022-22980] Spring Data MongoDB SpEL Expression Injection
 shoucheng3/apache__rocketmq_cve-2019-17572_4-6-0
Exploit for Apache RocketMQ CVE-2019-17572 targeting distributed messaging platforms with authentication and encryption features.
 mcornaglia/cve-2019-15715
Replica of CVE-2019-15715 in Python3
 vanishedpeople/cve-2017-7269
Python proof-of-concept for CVE-2017-7269, a buffer overflow in IIS 6.0 WebDAV, enabling remote code execution on Windows Server 2003 R2.