
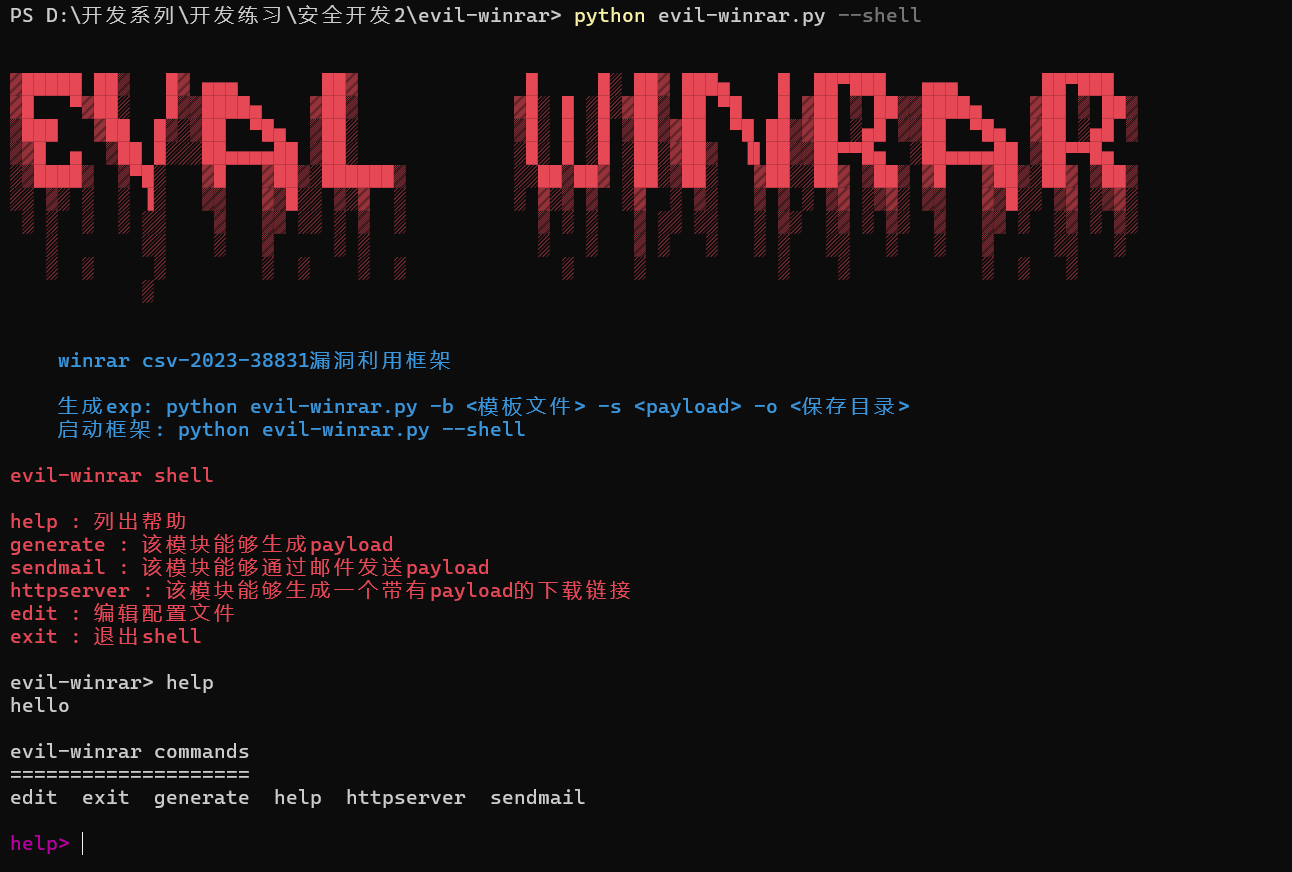
evil-winrar
 youmulijiang/evil-winrar
evil-winrar,CVE-2023-38831漏洞利用和社会工程学攻击框架 (evil-winrar, CVE-2023-38831 Vulnerability Exploitation and Social Engineering Attack Framework)
exploitationpayload-generationphishing-tools+3
11
youmulijiang/evil-winrarevil-winrar,CVE-2023-38831漏洞利用和社会工程学攻击框架 (evil-winrar, CVE-2023-38831 Vulnerability Exploitation and Social Engineering Attack Framework)
 kienhosd/wp-file-manager-exploit-cve-2020-25213-with-zerologon
Exploit Windows server 2019 vulnerable to Zerologon with Garble, Chisel, wp-file-manager vulnerability (have video demo)
 fa1c0n35/cve-2023-38831-winrar-exploit
Python-based exploit generator for CVE-2023-38831 WinRAR vulnerability. Creates malicious RAR archives with bait files (PDF, images) and payload…
 ngothienan/cve-2023-38831
Python-based exploit generator for CVE-2023-38831 (WinRAR remote code execution). Creates malicious RAR archives with bait files and payload scripts…
 jbaines-r7/staystaystay
Proof of Concept for CVE-2021-1585: Cisco ASA Device Manager RCE
 gmh5225/cve-2025-1562
Proof-of-concept exploit for CVE-2025-1562, a WordPress plugin activation vulnerability allowing remote code execution via crafted REST API requests.
 crowsec-edtech/cve-2022-22947
Spring Cloud Gateway < 3.0.7 & < 3.1.1 Code Injection (RCE)
 b1tg/cve-2023-38831-winrar-exploit
CVE-2023-38831 winrar exploit generator
 that-guy-steve/cve-2018-1133-exploit
Python exploit for Moodle Evil Teacher vulnerability (CVE-2018-1133) enabling authenticated remote command execution with proxy support.
 chybeta/cve-2017-11427-demo
The Demo for CVE-2017-11427
 wifiphisher/wifiphisher
Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…