file-notification-attacks

Research artifacts for file-notification side-channel attacks on Linux, Windows, and macOS, demonstrating inotify/FSEvents leakage, keystroke timing,…

Research artifacts for file-notification side-channel attacks on Linux, Windows, and macOS, demonstrating inotify/FSEvents leakage, keystroke timing,…

ZTE SmartLife security findings leading to account takeover: 100K+ Google Play downloads and CVE-2026-86552 through CVE-2026-86555.

CVE-2026-82090 · CVSS 9.2 CRITICAL · 0-click stored XSS in Mozilla Pocket — all versions (v0 → v8.33.0.0) · 18-year forever-day · no patch · MITRE…

PoC for CVE-2026-78997, a Universal XSS in UC Browser for Android. Includes a crafted URL builder, a callback-dispatch oracle, and Frida hooks to…

Educational proof-of-concept demonstrating a SQL injection vulnerability in Android 17's Contacts Provider, allowing a zero-permission app to…

CVE-2026-0073 - ADB Wireless Mutual Authentication Bypass PoC

Full-chain exploit for Android Chromium combining CVE-2026-11057 info leak and CVE-2026-5281 use-after-free to achieve vtable hijack and arbitrary…

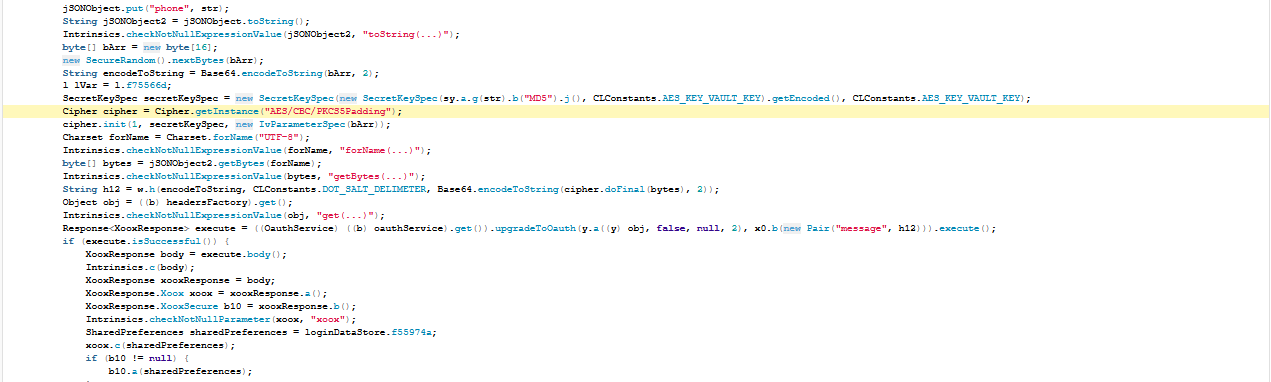
Proof of concept demonstrating insecure AES-CBC encryption with MD5 key derivation in the Meesho Android app, enabling ciphertext tampering and…

Python PoC for CVE-2026-18907 path traversal in TECNO Hi Browser's download handler. Includes malicious HTTP server and naive downloader to…

Magisk module for Android 14 that adds user-installed CA certificates to the system's Conscrypt trust store, enabling HTTPS interception with proxy…

A deliberately vulnerable mobile banking application designed for practicing mobile security testing. Features common vulnerabilities found in…

SQLi CVE-2019-5454

[CVE-2019-8389] An exploit code for exploiting a local file read vulnerability in Musicloud v1.6 iOS Application

Reporte técnico sobre vulnerabilidad crítica de Xiaomi

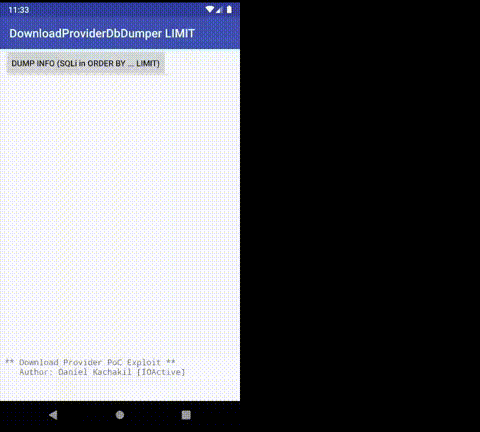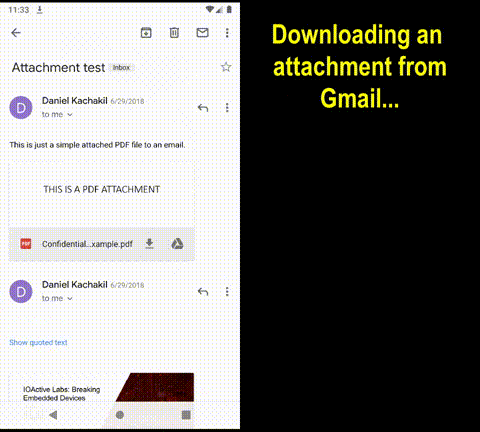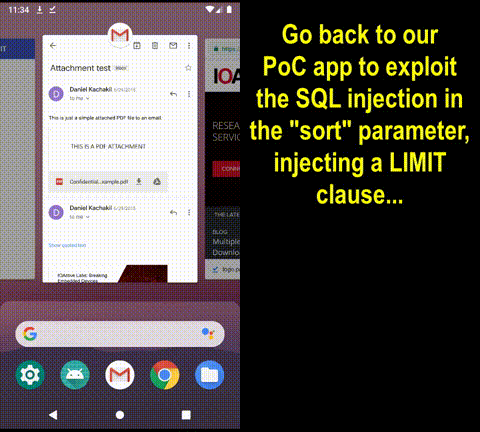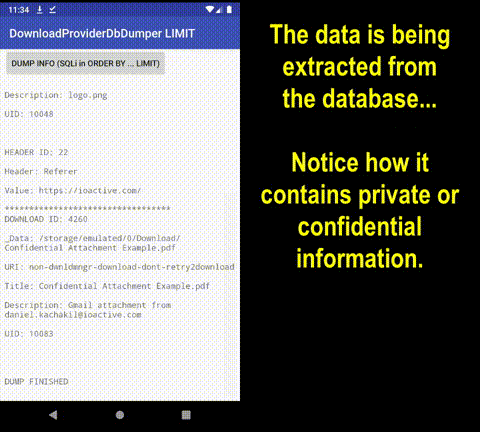
PoC Exploiting SQL Injection in Android's Download Provider in Sort Parameter (CVE-2019-2196)

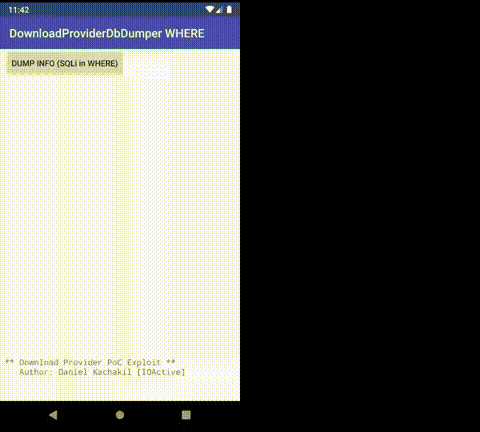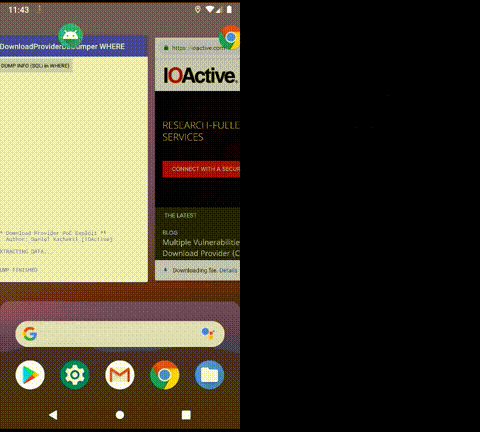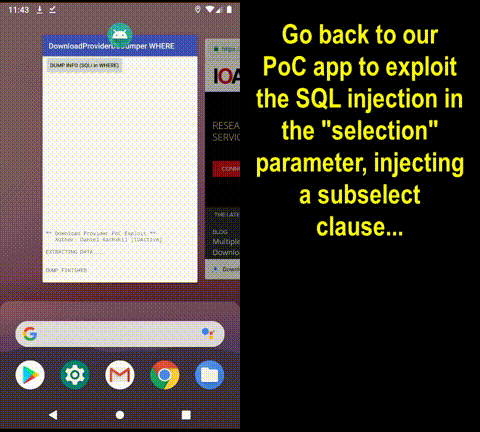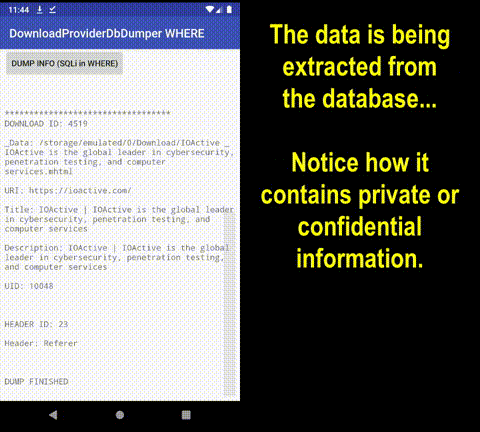
PoC Exploiting SQL Injection in Android's Download Provider in Selection Parameter (CVE-2019-2198)

Ekoparty Miami | Interface Anti-Patterns: Exploiting Insecure Navigation in 3rd Party Android App Lockers

Proof-of-concept exploit for Same-Origin Policy bypass in Samsung Internet Browser for Android, demonstrating a cross-origin data access…