
w3-total-cache-cve-2013-2010
 spyata123/w3-total-cache-cve-2013-2010
Remote code execution running on w3 total cache cve 2013-2010
exploitationpayload-generationpenetration-testing+3
spyata123/w3-total-cache-cve-2013-2010Remote code execution running on w3 total cache cve 2013-2010
 phusion/rails-cve-2012-5664-test
Demo app showing how the Rails CVE-2013-5664 vulnerability works.
 theratpack/grails-javamelody-sample-app
Grails sample application using the Javamelody 1.44 plugin to illustrate the CVE-2013-4378 vulnerability.
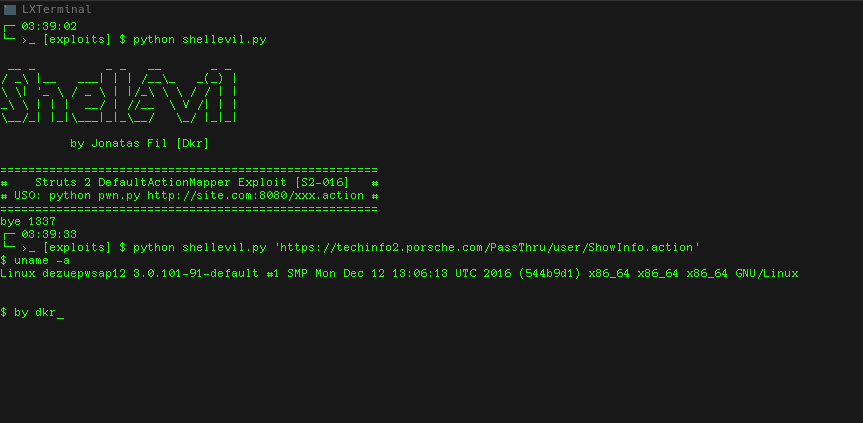 pentestingxroot/shellevil
Struts 2 DefaultActionMapper Interactive Shell Exploit for CVE-2013-225 [S2-016]
 srvaccount/cve-2021-26855-poc
PoC exploit code for CVE-2021-26855
 motikan2010/cve-2013-3651
CVE-2013-3651 PoC - EC-CUBE 2
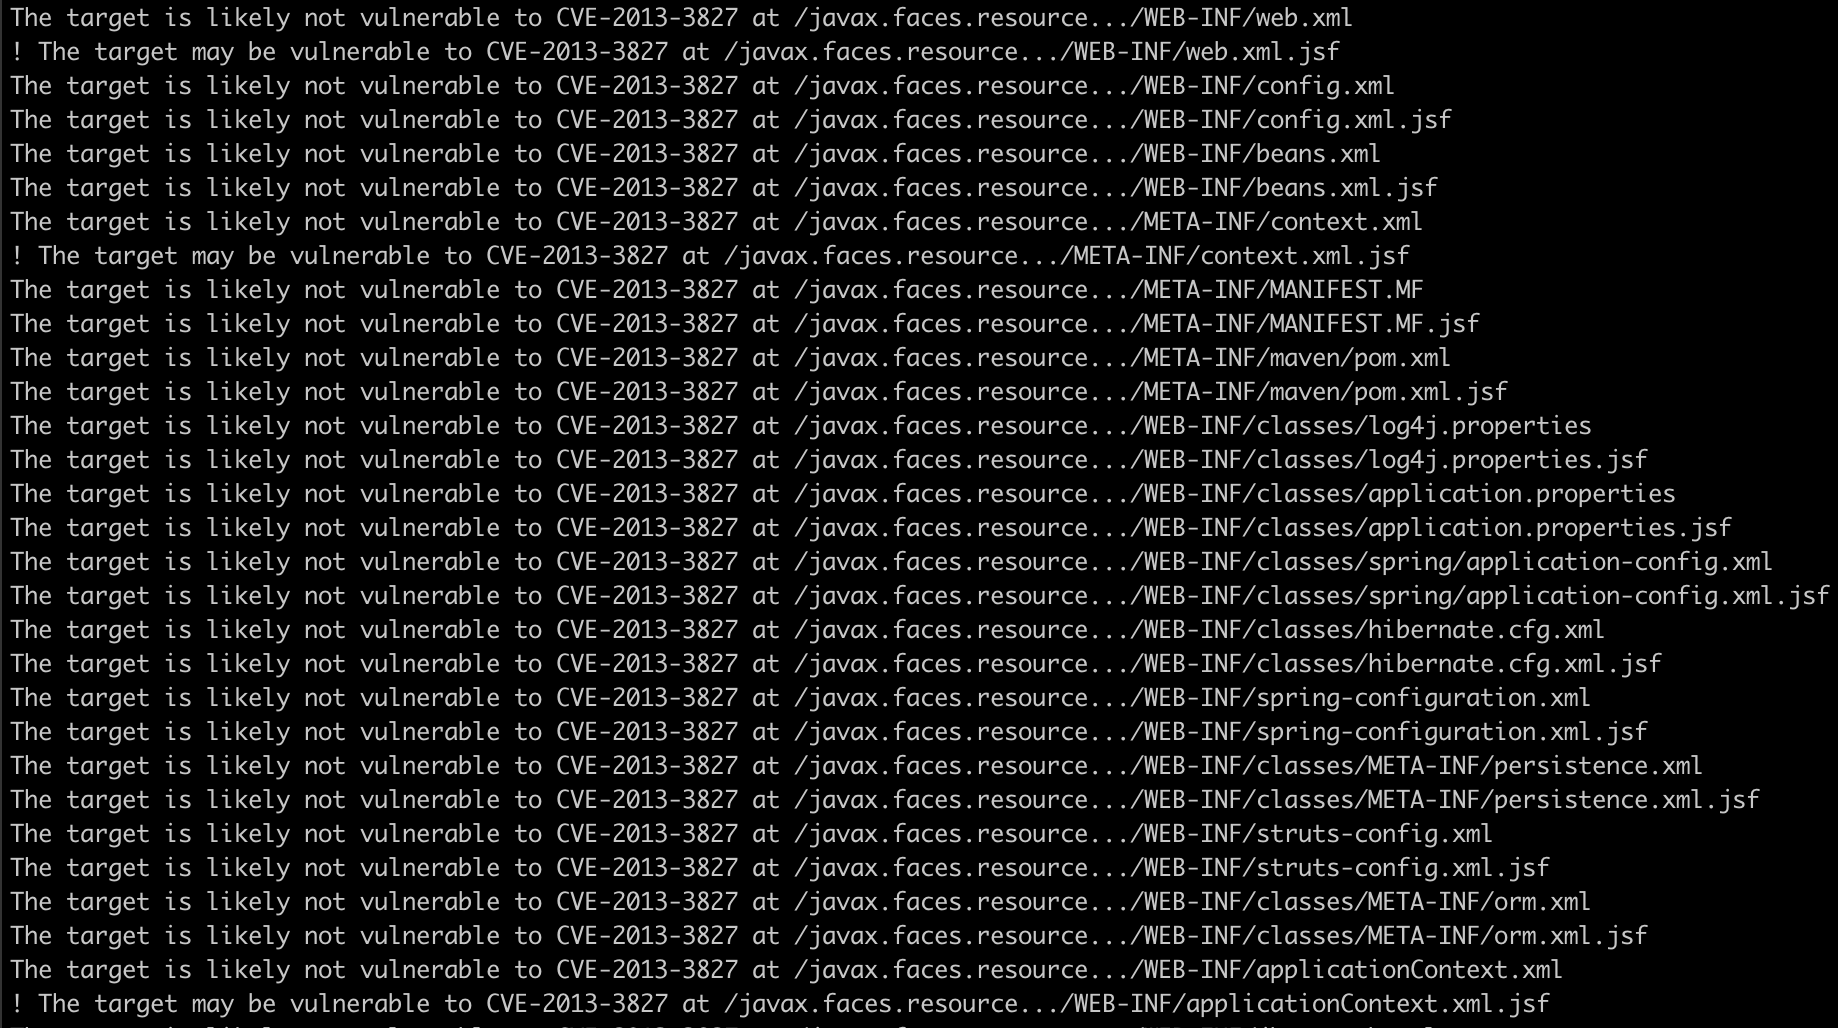 thistehneisen/cve-2013-3827
Quick PoC checker for common configurations that might be available via directory traversal due to CVE-2013-3827
 oxben10/cve-2013-0156
This script is specifically designed to solve the challenge on PentesterLab for the CVE-2013-0156 exploit
 grrrdog/acedcup
Payload generator for Java Binary Deserialization attack with Commons FileUpload (CVE-2013-2186)
 feliam/cve-2013-2729
Python-based exploit generator for Adobe Reader BMP/RLE heap corruption (CVE-2013-2729). Demonstrates arbitrary code execution via malicious BMP…
 devoteam-cybertrust/cve-2013-3319
metasploit module for CVE-2013-3319 / SAP Security Note 1816536
 cinno/cve-2013-1965
Proof-of-concept exploit for CVE-2013-1965 targeting Apache Struts 2, demonstrating remote code execution via crafted request parameters.
 hackerxj007/cve-2021-26855
CVE-2021-26855 exp
 cyberharsh/nginx-cve-2013-4547
Docker-based lab demonstrating Nginx CVE-2013-4547 URI parsing vulnerability with step-by-step exploitation for privilege bypass and code execution.
 bsodmike/rails-exploit-cve-2013-0156
Bootstrapped Rails 3.2.10 to test the remote code exploit CVE-2013-0156
 dannyendortest/java-vulnerable
EXPOSURE demo target: Tomcat (CVE-2016-0714) + Apache Rave (CVE-2013-1814) + Java filter-padding deps
 retr0-code/signhere
SignHere is implementation of CVE-2017-11882. SignHere is builder of malicious rtf document and VBScript payloads.