CVE-2026-12227-visualcomposer-lfi-poc

Docker validation lab and safe-oracle PoC for CVE-2026-12227, an unauthenticated LFI in Visual Composer via vcv-template, with a nuclei detection…

Docker validation lab and safe-oracle PoC for CVE-2026-12227, an unauthenticated LFI in Visual Composer via vcv-template, with a nuclei detection…

Python 3 PoC and scanner for CVE-2026-12227, an unauthenticated local file inclusion in WordPress Visual Composer Website Builder via the…

Python PoC and scanner for CVE-2026-87902, a WordPress core path traversal leading to LFI and PEAR-based RCE, with WAF bypass and automated…

WordPress CVE-2026-87902 LFI-to-RCE toolkit with a weaponized exploit chain (PEAR RCE, webshell, admin creation, loot) and a non-intrusive…

WordPress Core <= 7.1.1 unauthenticated LFI to RCE - validation lab, PoC, nuclei template (GHSA-7hp8-65ch-5whp)

Proof-of-concept for CVE-2026-90847, an authenticated RCE in iux_set.cgi via malicious .cfg tar upload that writes commands into crontab for…

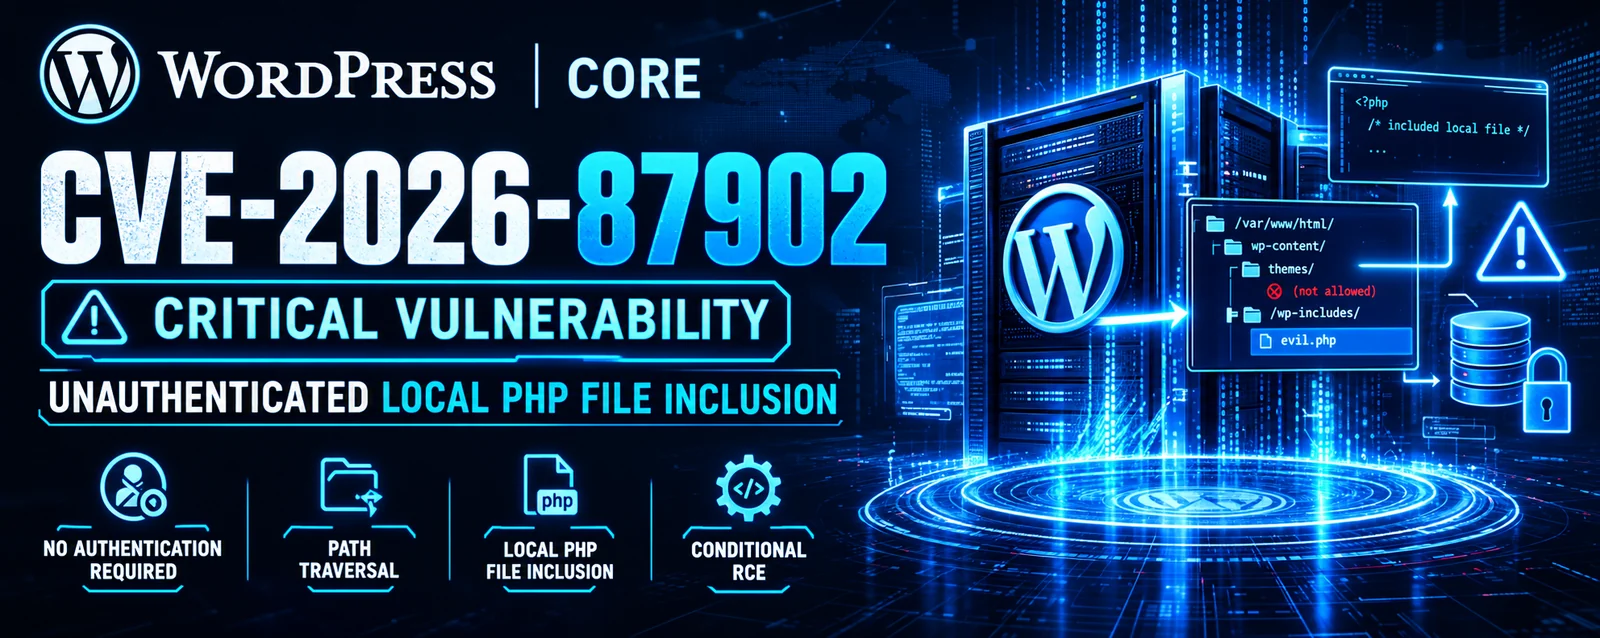
Python PoC for CVE-2026-87902, an unauthenticated WordPress path traversal RCE via get_page_template(), with version fingerprinting, theme checks,…

Web application penetration testing lab — vulnerable Flask app, automated scanner, and professional pentest report. Covers OWASP Top 10, SQLi, XSS,…

Proof-of-concept and disclosure pack for CVE-2026-87902, an unauthenticated local file inclusion in WordPress Core via locate_template(), with a…

Technical analysis and PoC for CVE-2026-14856, a stored XSS in TastyIgniter v4.3.0 Media Manager that chains with CSRF to achieve admin account…

Python PoC validating CVE-2025-6325 unauthenticated privilege escalation and CVE-2025-6327 arbitrary file upload RCE in King Addons for Elementor <=…

Proof-of-concept exploit and lab for CVE-2026-81648, an unauthenticated arbitrary file deletion flaw in the WordPress CryptoPayment Gateway plugin.

Python PoC scanner and exploit for CVE-2026-84434, an unauthenticated arbitrary file upload in Gravity Forms <=3.1.0.4 via hidden File Upload fields.…

Python exploit for CVE-2023-4220 in Chamilo LMS that uploads a file and delivers an unauthenticated reverse shell to a netcat listener.

Python mass-exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in the WordPress Divi Form Builder plugin, with webshell upload and…

Proof-of-concept and disclosure pack for CVE-2026-19952, an unauthenticated arbitrary file deletion in the WordPress Frontend Admin plugin, with lab…

Proof-of-concept and lab for CVE-2026-75827, a Grav arbitrary file write via Blueprint dynamic-data error_log, with reproduction script and Docker…

Reproduction pack and PoC script for CVE-2026-87796, an unauthenticated arbitrary file upload RCE in Multi Uploader for Gravity Forms <= 1.1.9, with…