
wpscan
 wpscanteam/wpscan
WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
crawlerdynamic-code-analysisinformation-gathering+7
wpscanteam/wpscanWordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
 0xcyp1337/cve-2026-82222-massexploit
Exploit tool for CVE-2026-82222, an unauthenticated RCE in GiveWP WordPress plugin. Supports single-target and batch exploitation with…
 evillm/cve-2023-4634-poc
Proof-of-concept exploit for CVE-2023-4634, a remote code execution vulnerability in the WordPress Media Library Assistant plugin. Includes a…
 ill-deed/cve-2025-34085-multi-target
Multi-target unauthenticated RCE scanner for CVE-2025-34085 affecting WordPress Simple File List plugin. Uploads, renames, and triggers PHP webshells…
 xshadow-here/cve-2026-0740
Automated mass exploiter for CVE-2026-0740, an unauthenticated arbitrary file upload in Ninja Forms File Uploads plugin, enabling remote code…
 randomrobbiebf/cve-2026-28134
JetEngine <= 3.7.2 - Authenticated (Contributor+) Remote Code Execution
 fleetcaptain/everest-backup-cve-2025-11380
Proof-of-concept exploit for CVE-2025-11380 demonstrating unauthenticated backup access in the Everest Backup WordPress plugin, enabling security…
 0xcyp1337/cve-2026-57811
Exploits CVE-2026-57811, an unauthenticated RCE in Realtyna Organic IDX + WPL Real Estate WordPress plugin, enabling shell upload and command…
 murrez/cve-2026-1306
Multi-target PoC runner for CVE-2026-1306 in WordPress midi-Synth plugin: fetches nonce, sends export AJAX request to upload files, and verifies…
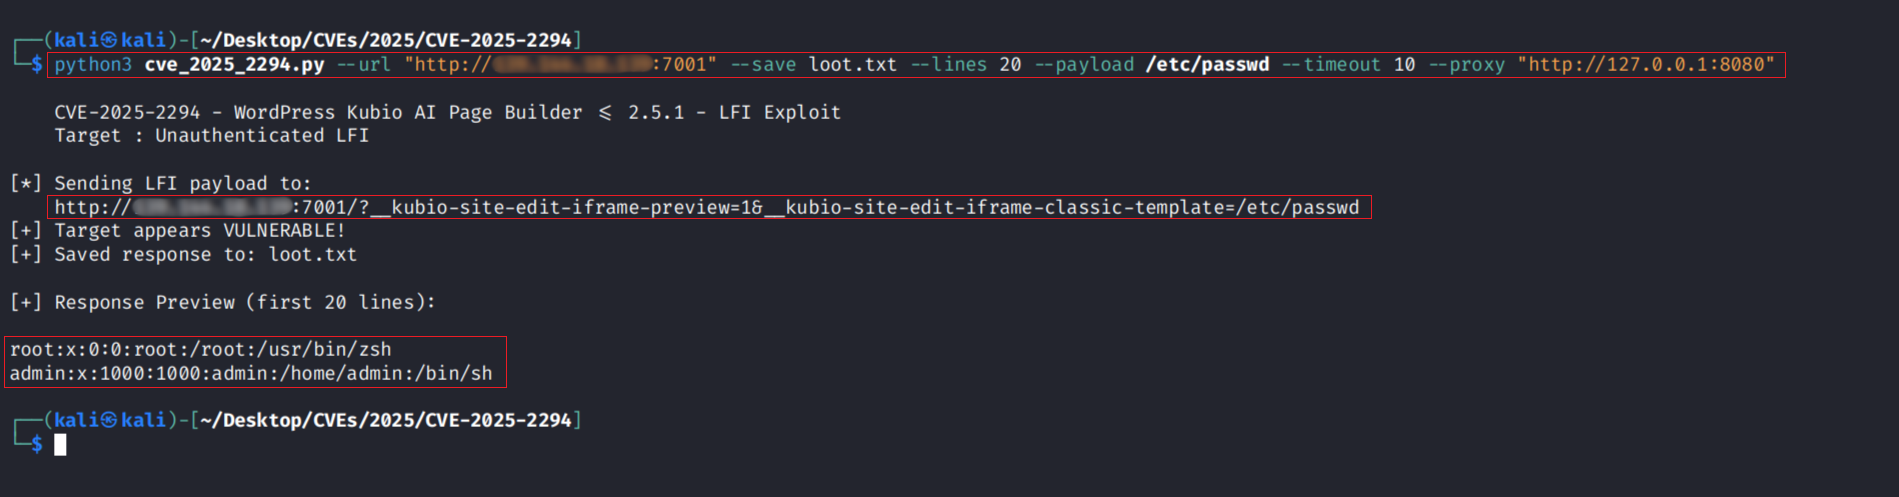 r0otk3r/cve-2025-2294
Python exploit script for CVE-2025-2294, an unauthenticated Local File Inclusion vulnerability in WordPress Kubio AI Page Builder ≤ 2.5.1. Supports…
 yukinime/cve-2025-34085
Automated scanner and exploit for CVE-2025-34085, an unauthenticated RCE in the WordPress Simple File List plugin. Supports multi-target scanning,…
 soltanali0/cve-2024-12877-exploit
Educational CVE-2024-12877 exploit demo for PHP Object Injection in GiveWP WordPress plugin. Includes root cause analysis, regex bypass techniques,…
 anothersec/cve-2025-6440
WooCommerce Designer Pro 1.9.26 - Arbitrary File Upload
 madexploits/cve-2026-14483
CVE-2026-14483 POC EXPLOIT BY MADEXPLOITS
 nxploited/cve-2024-56071
Simple Dashboard <= 2.0 - Unauthenticated Privilege Escalation
 nxploited/cve-2026-13714
Realtyna Organic IDX plugin + WPL Real Estate < 5.3.0 - Unauthenticated Arbitrary File Upload to Remote Code Execution
 itsismarcos/exploit-cve-2026-1357
Exploit for CVE-2026-1357 in WordPress WPVivid plugin, enabling remote code execution via crafted AES-encrypted payloads and directory traversal to…
 r0otk3r/cve-2024-25600
Python-based exploit for CVE-2024-25600 targeting Bricks Builder WordPress plugin RCE. Automates nonce extraction, payload injection, and arbitrary…