
CVE-2023-27100
 fabdotnet/cve-2023-27100
Exploit for CVE-2023-27100 bypassing pfSense anti-brute force protection via crafted X-Forwarded-For headers and anti-CSRF tokens to evade sshguard…
authenticationexploitationids-ips-evasion+3
fabdotnet/cve-2023-27100Exploit for CVE-2023-27100 bypassing pfSense anti-brute force protection via crafted X-Forwarded-For headers and anti-CSRF tokens to evade sshguard…
 xthalach/cve-2024-11318
This repository details an IDOR vulnerability in AbsysNet 2.3.1, which allows a remote attacker to brute-force session IDs via the /cgi-bin/ocap/…
 horizon3ai/cve-2023-34051
VMware Aria Operations for Logs CVE-2023-34051
 zzz66686/cve-2017-14262
Exploit for CVE-2017-14262 targeting Samsung NVR devices: extracts admin MD5 password hash via unauthenticated CGI request and logs in with the hash…
 ch1nghz/cve-2020-11851
Remote Code Execution vulnerability on ArcSight Logger
 0x2458bughunt/cve-2023-25157
Scans host lists for GeoServer endpoints vulnerable to CVE-2023-25157 SQL injection, verifies exposed paths with keyword checks, and logs confirmed…
 makavellik/poc-cve-2021-42013-exploit
Una herramienta avanzada de escaneo, explotación e interacción remota diseñada para detectar y aprovechar la vulnerabilidad Apache Path Traversal +…
 snapattack/damn-vulnerable-log4j-app
Vulnerable web application to test CVE-2021-44228 / log4shell and forensic artifacts from an example attack
 win3zz/cve-2023-43261
CVE-2023-43261 - Credential Leakage Through Unprotected System Logs and Weak Password Encryption
 hxuu/moodle-cve
Web CTF challenge highlighting moodle CVE-2025-26529 (in 2 flavors)
 nulltrace0x/cve-2025-31324
Proof-of-concept exploit for CVE-2025-31324, a remote code execution vulnerability in SAP NetWeaver, with Shodan dorks for target discovery and…
 schn1tzelme1ster/cve-2025-6002
Python exploit for CVE-2025-6002 targeting authenticated arbitrary file upload in VirtueMart < 4.4.10. Logs in, uploads a PHP webshell, and triggers…
 hakaioffsec/cve-2026-4802
Proof-of-concept exploit for CVE-2026-4802, a command injection vulnerability in Cockpit's system logs UI, enabling arbitrary command execution and…
 geniuszly/cve-2022-46080
it is script that enables Telnet on routers by sending a specially crafted request. The script allows users to specify the router's URL, Telnet port,…
 thestingr/cve-2024-36991-tool
This binary POC automates the exploitation of CVE-2024-36991 by sending crafted curl requests to a vulnerable Splunk instance. It retrieves sensitive…
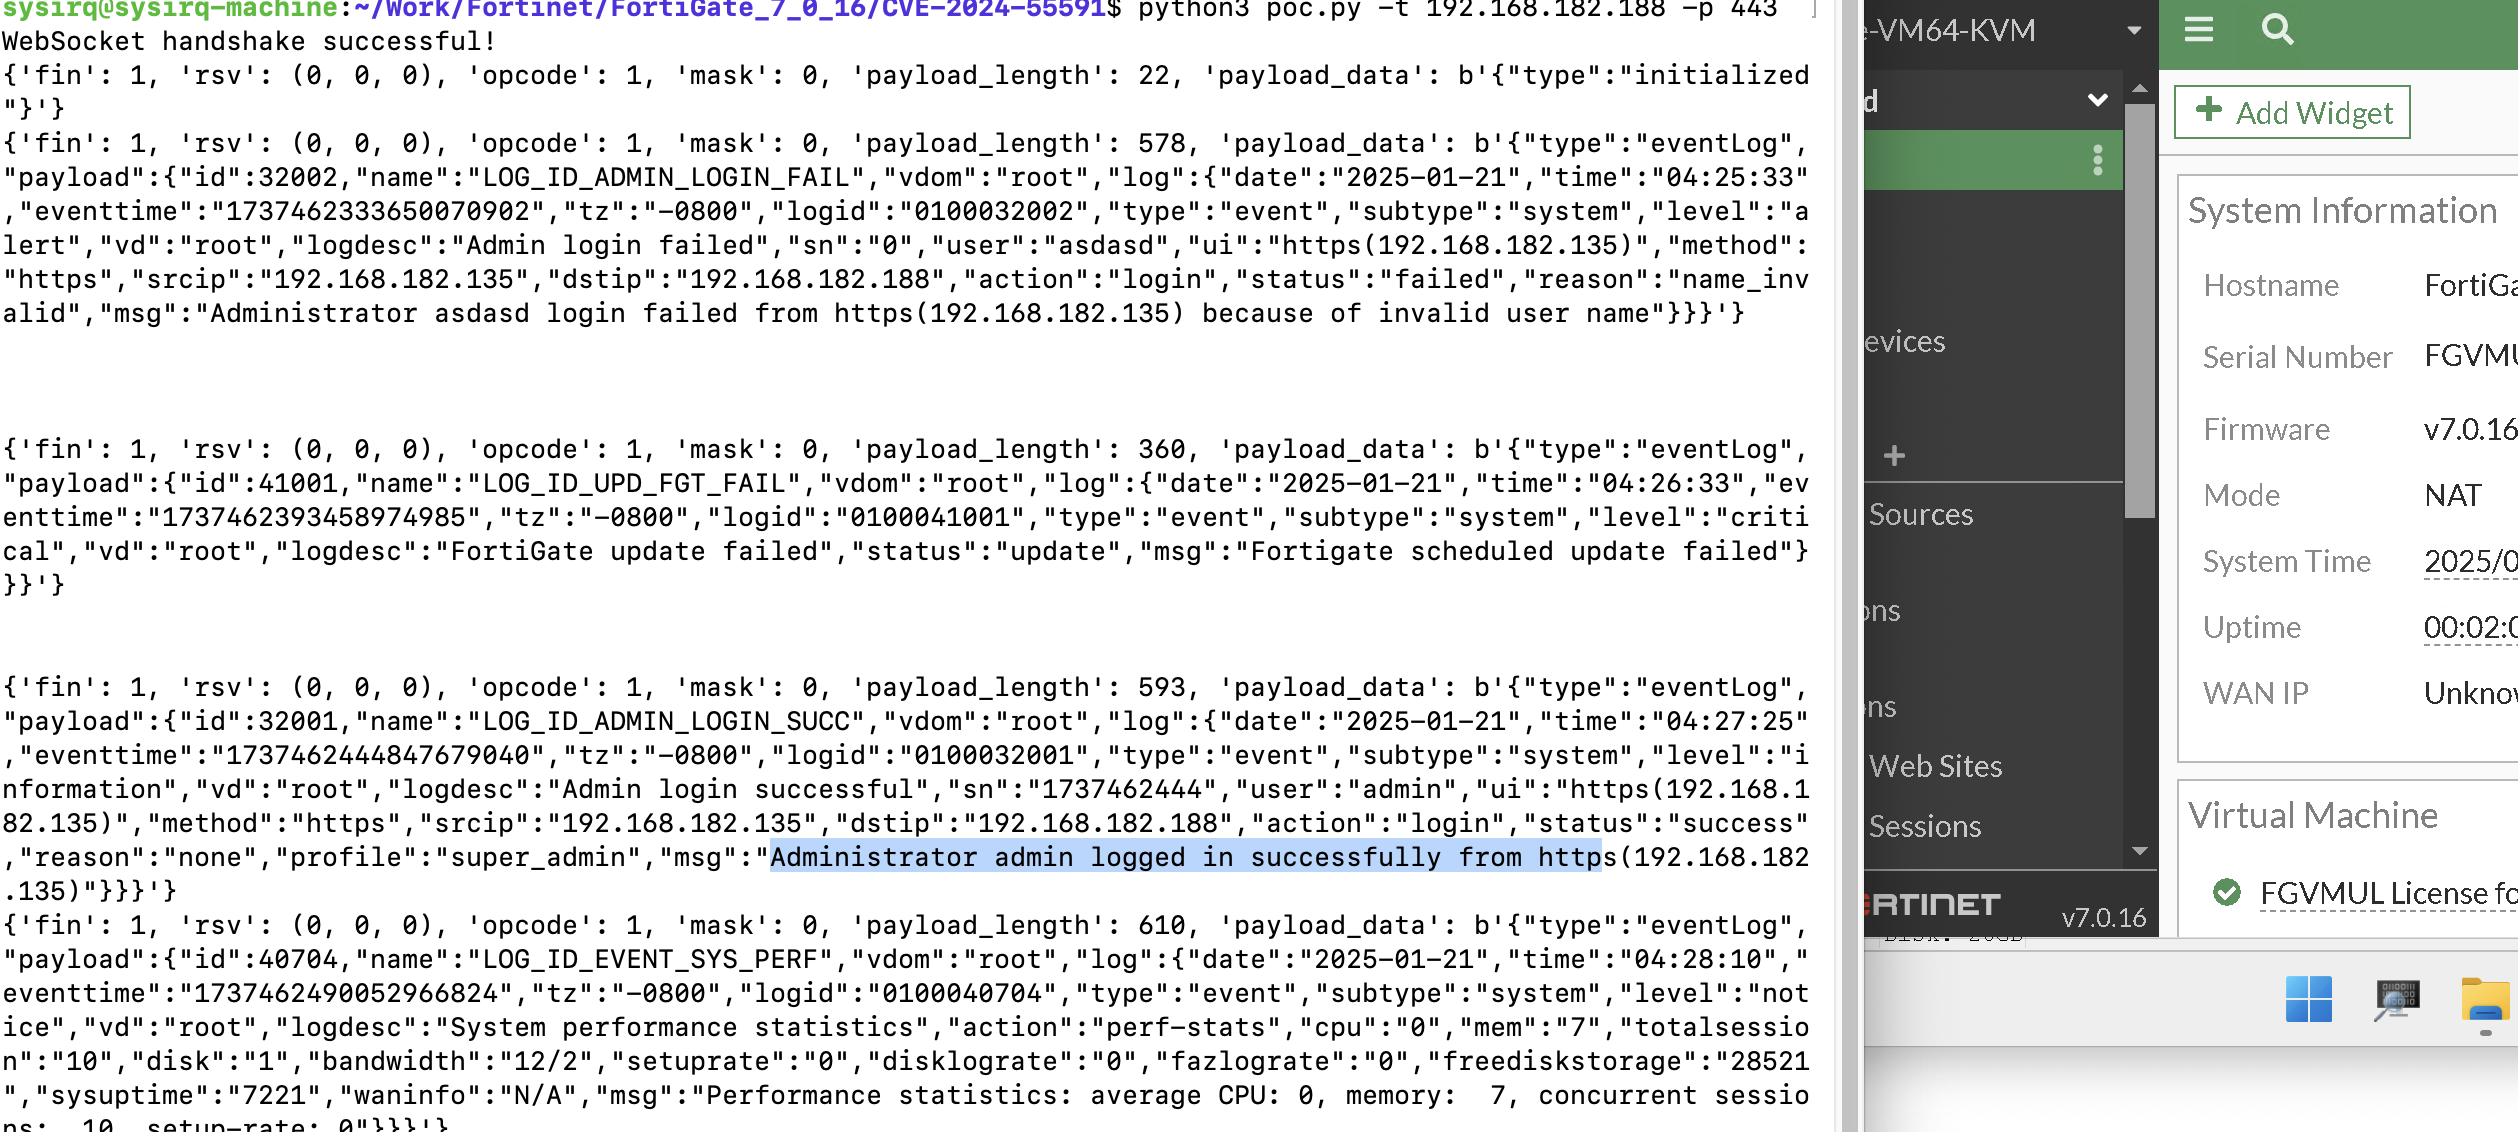 sysirq/fortios-auth-bypass-poc-cve-2024-55591
Proof-of-concept exploit for FortiOS authentication bypass (CVE-2024-55591) that allows unauthenticated access to system logs via WebSocket on…
 jeffli1024/log4j-rce-test
Quick test environment for CVE-2021-44228 Log4j RCE vulnerability with a built-in exploit server and customizable payload execution.
 pickl31/cve-2026-59827
Metabase CVE-2026-59827 Vulnerability Scanner