
fsociety
 manisso/fsociety
fsociety Hacking Tools Pack – A Penetration Testing Framework
exploitationinformation-gatheringpassword-attacks+6
manisso/fsocietyfsociety Hacking Tools Pack – A Penetration Testing Framework
 hoodoer/js-tap
JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…
 521526/cve-2019-1006
Checks Remote Desktop Gateway servers for CVE-2019-1006 by sending crafted requests to a user-supplied URL and reporting whether the target is…
 fivex3/cve-2023-27035
Proof-of-concept exploit demonstrating unauthorized microphone recording and desktop notification abuse via embedded web pages in Obsidian Canvas,…
 rootdirective-sec/cve-2026-55255-lab
Local Docker lab for reproducing CVE-2026-55255, an IDOR vulnerability in Langflow's Responses API. Validates cross-user flow execution in vulnerable…
 cduram/notcve-2026-0009
Path Traversal Vulnerability in NitroShare v0.3.4
 jun2e0/cve-2025-26788
Proof-of-concept exploit for CVE-2025-26788 demonstrating WebAuthn credential ID manipulation via JavaScript hooking to bypass authentication in…
 shinycolumn/cve-2025-56799
OS Command Injection Vulnerability via Cache Clearing Scheduler in Reolink Desktop Application
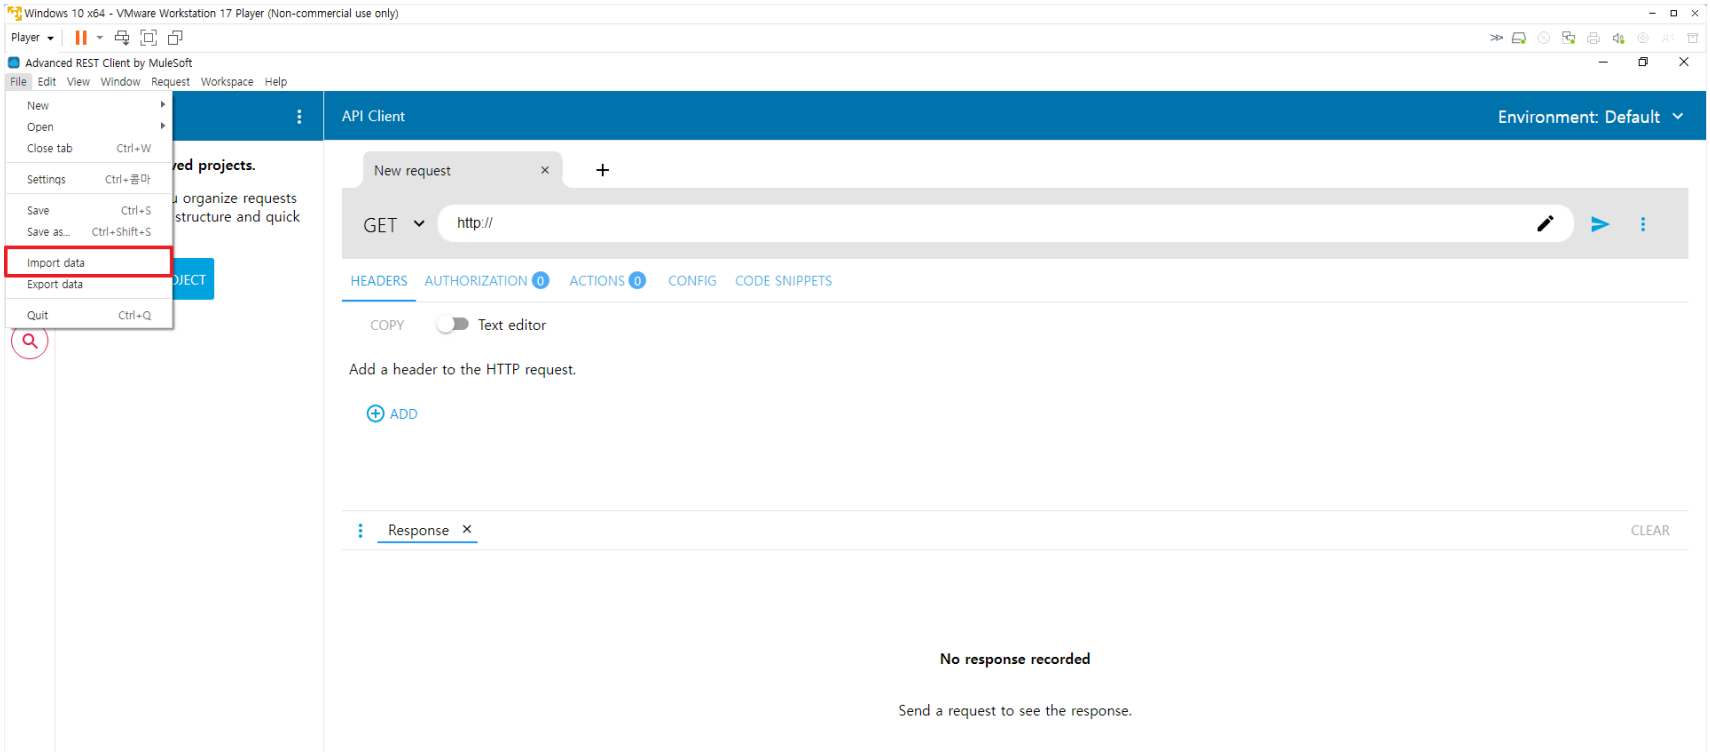 eqstlab/cve-2024-25503
Cross-Site Scripting vulnerability in Advanced REST Client v.17.0.9 exploit
 psl-b/cve-2024-38077-check
CVE-2024-38077 vulnerability checker with proof-of-concept exploit targeting Windows Remote Desktop Licensing Service. Validates by connecting to a…
 mbadanoiu/cve-2020-8254
CVE-2020-8254: Zip Slip in Pulse Secure VPN Windows Client
 revengsmk/cve-2024-10511
Schneider Electric PowerChute Serial Shutdown vulnerability.
 cve-2019-0708-poc/cve-2019-0708
Exploit tool targeting CVE-2019-0708 in Remote Desktop Services, enabling remote code execution on vulnerable Windows systems for penetration testing…
 shinycolumn/cve-2025-56800
Local Authentication Bypass Vulnerability in Reolink Desktop Application
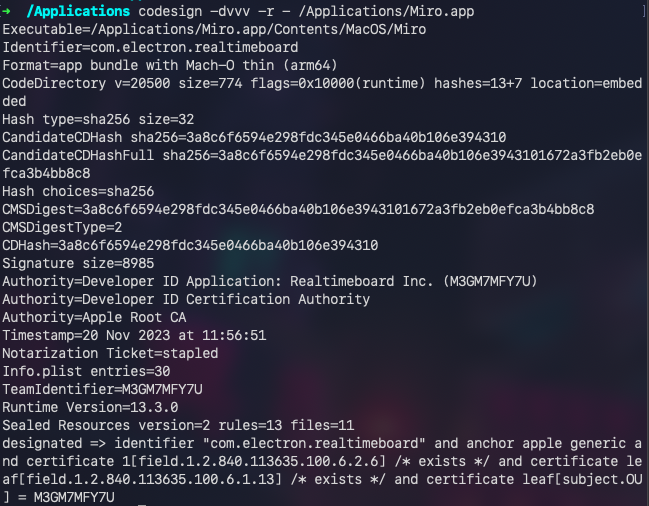 louiselalanne/cve-2024-23746
Miro Desktop 0.8.18 on macOS allows Electron code injection.
 freeide/cve-2019-0708-poc-exploit
Proof-of-concept exploit for CVE-2019-0708 (BlueKeep), a critical remote code execution vulnerability in Microsoft Remote Desktop Services, enabling…
 blacksunwen/cve-2019-0708
CVE-2019-0708
 yosasasutsut/cve-2025-56803
OS Command Injection Vulnerability via Plugin Execution in Figma Desktop Application