
CVE-2017-8056
 itzexploit/cve-2017-8056
Python-based exploit for CVE-2017-8056 targeting XML-RPC denial-of-service vulnerability in web applications.
exploitationpenetration-testingvulnerability-analysis+1
itzexploit/cve-2017-8056Python-based exploit for CVE-2017-8056 targeting XML-RPC denial-of-service vulnerability in web applications.
 sl4cky/cve-2018-7600
Testing and exploitation tool for Drupalgeddon 2 (CVE-2018-7600)
 r4v3nbl4ck/apache-struts-2-cve-2017-5638-exploit-
Exploit created by: R4v3nBl4ck end Pacman
 adfortunato/metasploitable3-pentest-writeup
Home-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…
 kentox493/cve-2026-42945_nginxrift
Automates CVE-2026-42945 exploitation in NGINX containers: verifies vulnerable targets, brute-forces heap offsets, executes commands, and opens an…
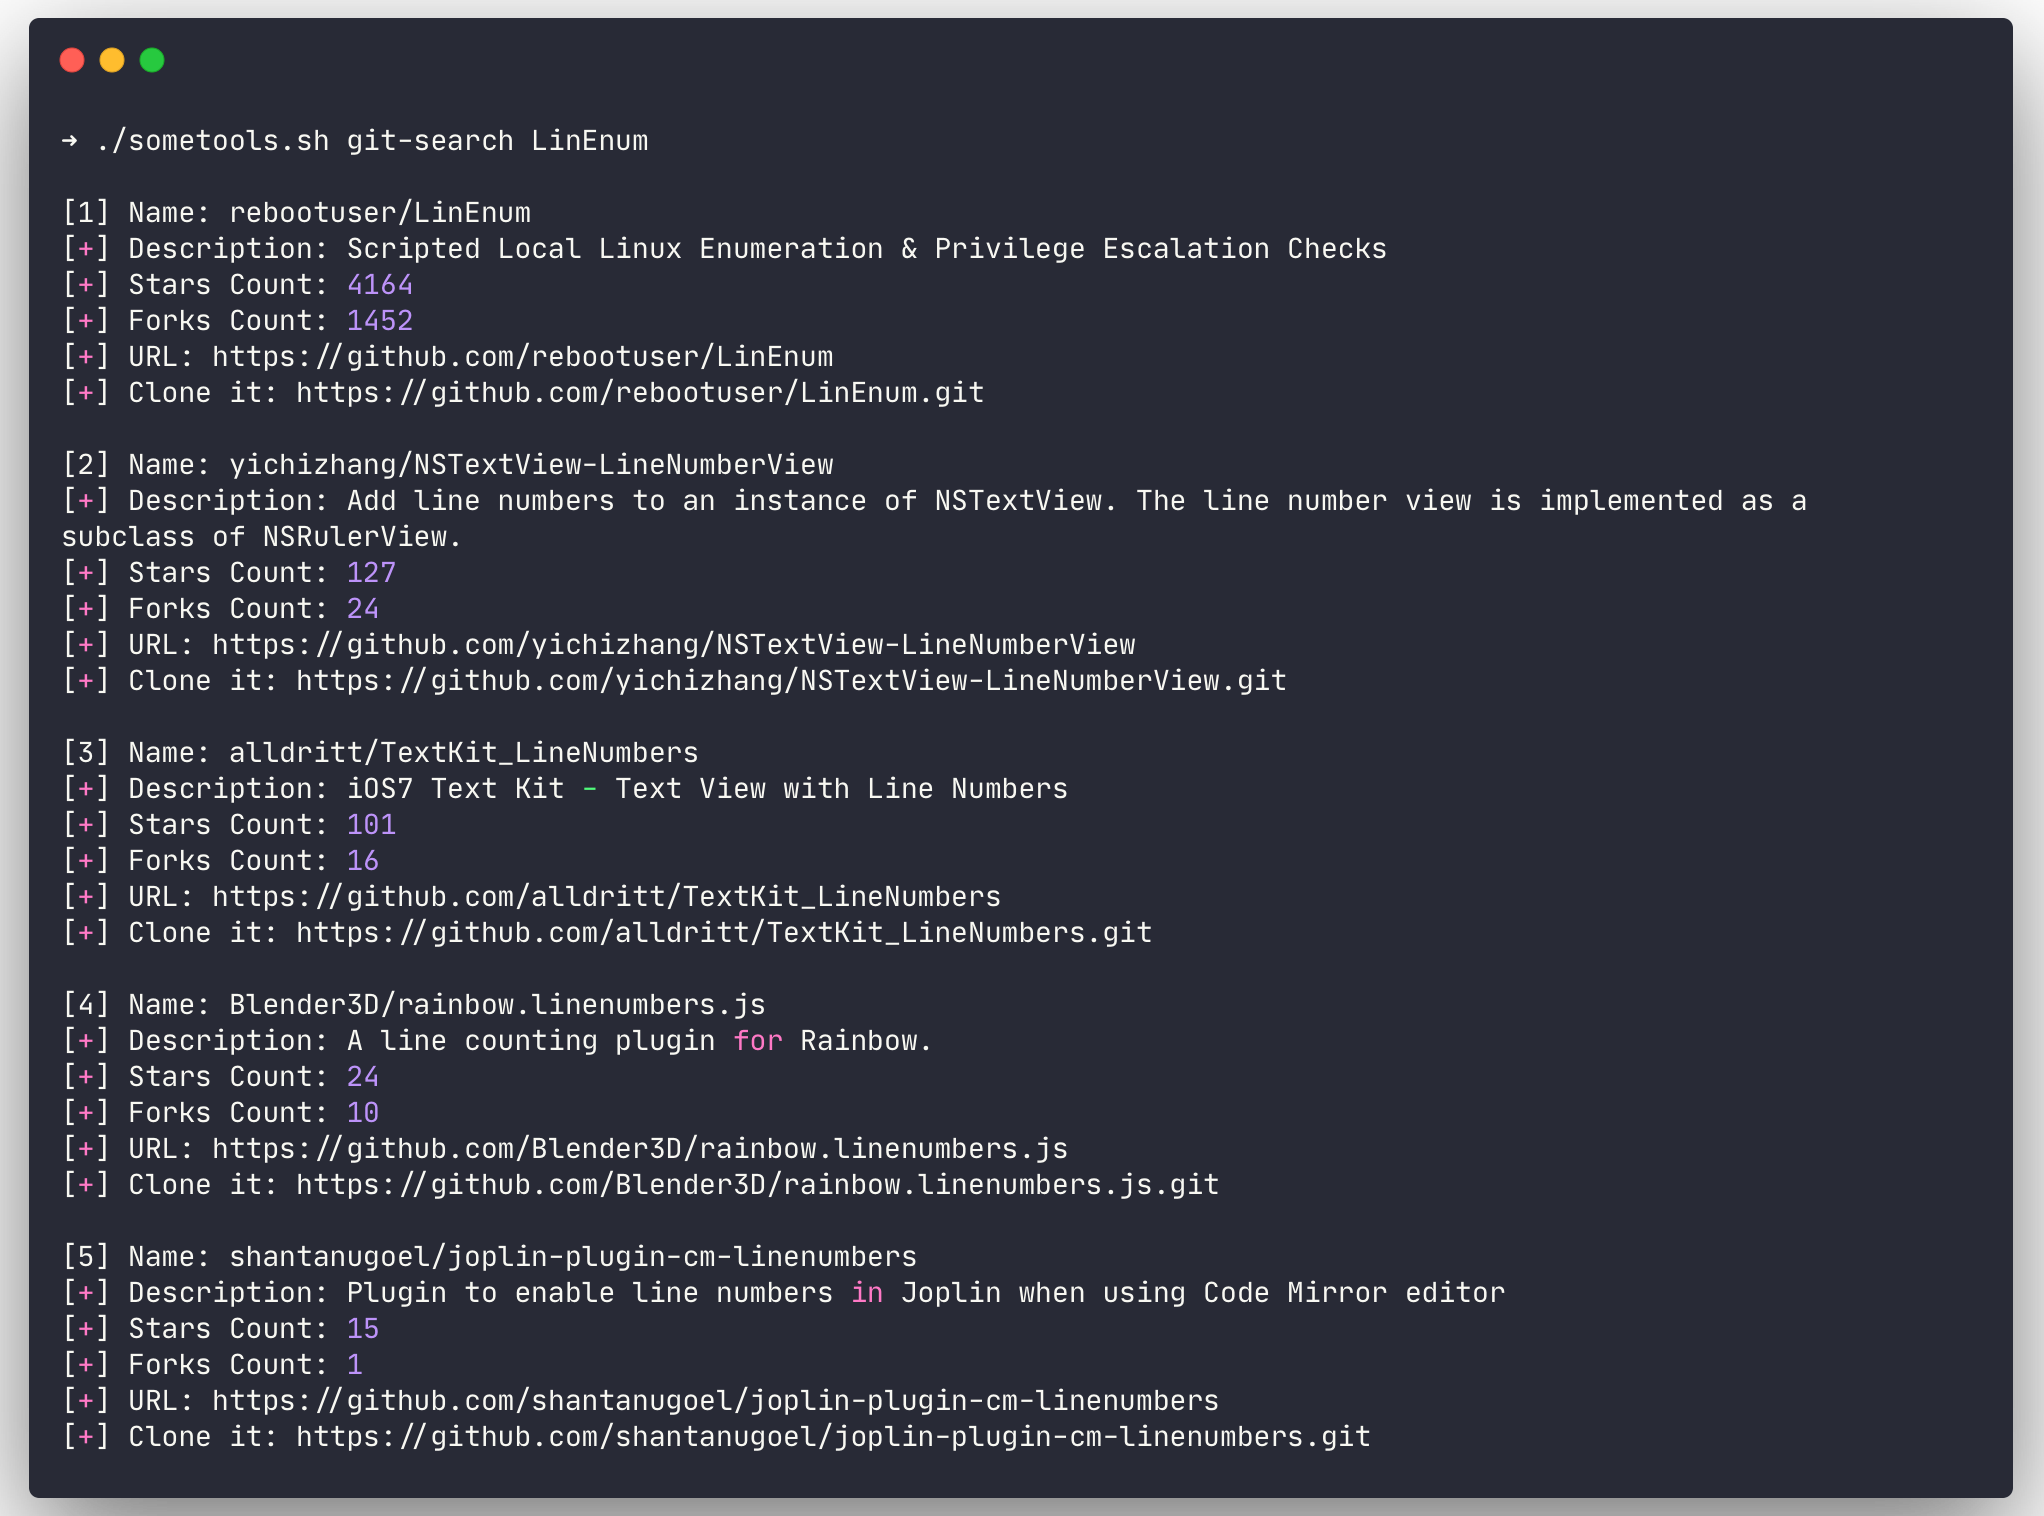 som3canadian/some-tools
Some Pentest Tools. Install and keep up to date some pentesting tools. I used this to pass my OSCP exam.
 jpiechowka/jenkins-cve-2016-0792
Exploit for Jenkins serialization vulnerability - CVE-2016-0792
 adityabhatt3010/room-walkthrough-billing
A detailed walkthrough of Billing room exploiting CVE-2023-30258 and escalating via fail2ban misconfig
 afifudinmtop/cve-2021-21425
Python exploit for CVE-2021-21425 that executes a reverse shell payload against a target IP, with instructions for setting up a netcat listener.
 suriyaboon/hackthebox-facts
HTB Facts is a Easy Linux box featuring Camaleon CMS and MinIO. Gain admin access via open registration and a mass assignment vulnerability, then…
 rajchowdhury240/cve-2018-13341
This Tool Aims to Exploit the CVE-2018-13341
 r3fr4kt/shocker-tjnull-oscp-
Structured HTB walkthrough demonstrating Shellshock (CVE-2014-6271) exploitation via CGI directory fuzzing and privilege escalation through…
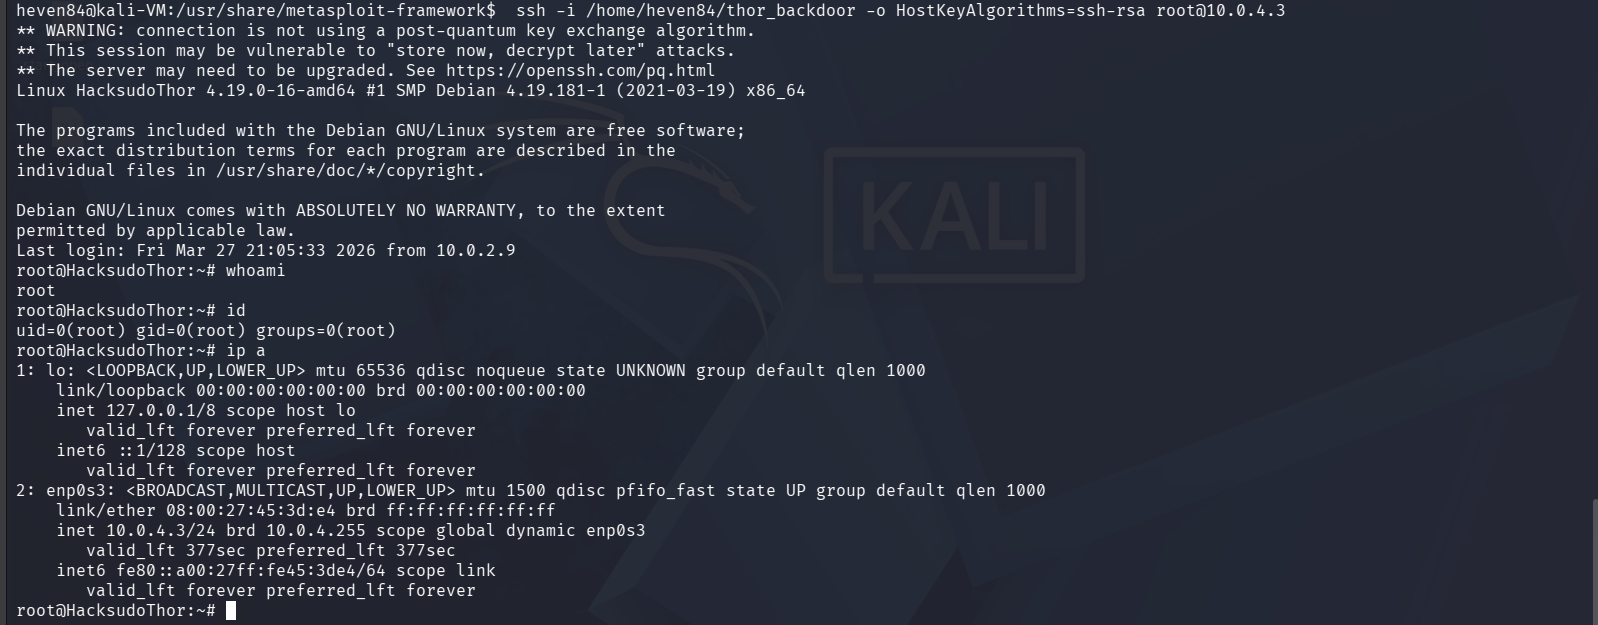 heventafese/penetration-testing-walkthrough-hacksudo-thor
Black-box penetration test against HackSudo Thor : CVE-2014-6271 Shellshock RCE through Apache mod_cgi, chained with sudo misconfiguration and bash…
 cves-labs/cve-2026-1357
Lab environment and proof-of-concept exploit for CVE-2026-1357, a WordPress plugin vulnerability, with Docker setup and automated exploitation…
 s1gh/quickbox-pro-2.1.8-authenticated-rce
Authenticated command injection exploit for QuickBox Pro v2.1.8, providing remote code execution as www-data and privilege escalation to root via…
 aviksaikat/cve-2016-0792
Modified Verion of CVE-2016-0792
 cyfare/cve-2026-23918-apache-http-server-doublefree-poc
Proof-of-concept exploit for CVE-2026-23918, a double-free vulnerability in Apache HTTP Server, demonstrating remote crash via crafted requests.