

w3af
 andresriancho/w3af
Open-source web application security scanner that identifies and exploits 200+ vulnerabilities including XSS, SQL injection, and OS commanding.…
exploitationpenetration-testingvulnerability-scanners+3
4.9k
andresriancho/w3afOpen-source web application security scanner that identifies and exploits 200+ vulnerabilities including XSS, SQL injection, and OS commanding.…
 boundaryx/cloudrasp-log4j2
一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.
 neex/http2smugl
Detects and exploits HTTP request smuggling vulnerabilities via HTTP/2 to HTTP/1.1 conversion, using automated header smuggling techniques to…
 webgoat/webgoat
Deliberately vulnerable web application with interactive lessons and challenges for learning web application security and penetration testing…
 urbanadventurer/whatweb
Next generation web scanner
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 swisskyrepo/payloadsallthethings
A list of useful payloads and bypass for Web Application Security and Pentest/CTF
 itzexploit/cve-2017-8056
Python-based exploit for CVE-2017-8056 targeting XML-RPC denial-of-service vulnerability in web applications.
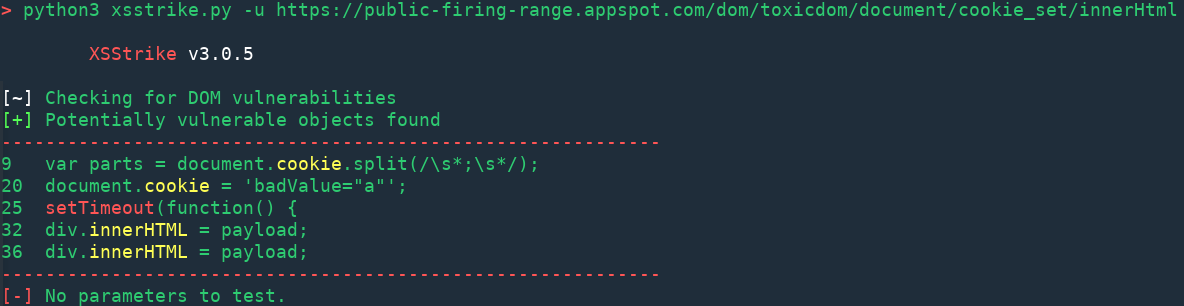
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 wpscanteam/wpscan
WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
 skyllpro/cve-2021-44026-poc
Bug Chain XSS (CVE-2020-35730 and CVE-2023-43770) to SQLi (CVE-2021-44026)
 sarthak4126/web-app-pentesting
Web application penetration testing lab — vulnerable Flask app, automated scanner, and professional pentest report. Covers OWASP Top 10, SQLi, XSS,…
 happynote3966/cve-2018-7600
Exploit for CVE-2018-7600, a critical remote code execution vulnerability in Drupal core. Enables automated exploitation of unpatched Drupal sites…
 theqmaks/resolver
This extension integrates popular CAPTCHA solution services into BurpSuite to process different types of CAPTCHAs without manual intervention.
 karthikuj/cve-2022-31101
Exploit for PrestaShop bockwishlist module 2.1.0 SQLi (CVE-2022-31101)
 iczc/ethermint-cve-2021-25837
Proof-of-concept exploit for CVE-2021-25837 targeting Ethermint, demonstrating a critical vulnerability in Ethereum-compatible blockchain nodes.