
php_reverse_shell
Simple PHP reverse shell script for establishing remote command execution on target systems. Ideal for penetration testing and security assessments.

Simple PHP reverse shell script for establishing remote command execution on target systems. Ideal for penetration testing and security assessments.

This is a simple POC to for show the pfsense 2.7 Command injection Vulnerability ( CVE-2023-42326)

Nginxpwner is a simple tool to look for common Nginx misconfigurations and vulnerabilities.

A Two-Factor Authentication (2FA) bypass vulnerability in "Simple 2FA Plugin for Moodle" by LMS Doctor

Tool check: CVE-2021-41773, CVE-2021-42013, CVE-2020-17519

Simple flask application to implement an intentionally vulnerable web app to demo CVE-2023-2822.

Proof-of-concept for SQL injection in CodeAstro Simple Attendance Management System 1.0, demonstrating authentication bypass via crafted username…

Simple python3 script to automate CVE-2018-9995

CVE-2022-0169 - WordPress Photo Gallery SQLi PoC

CVE-2018-1000861 Exploit

Scanner for CVE-2023-22515 - Broken Access Control Vulnerability in Atlassian Confluence

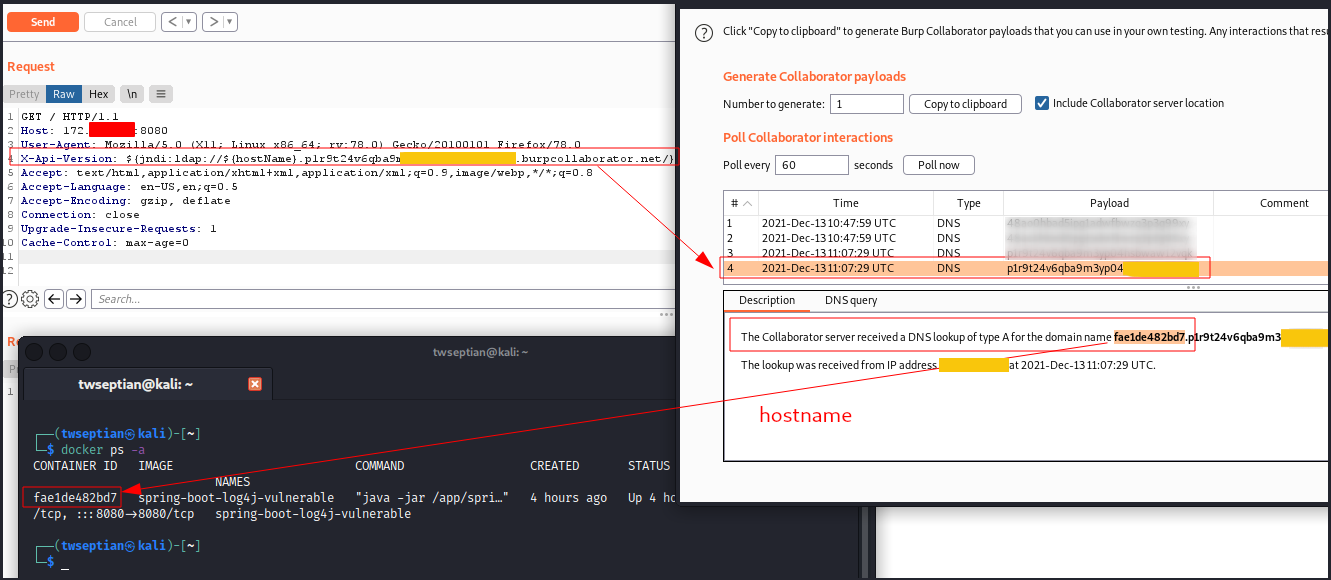
Spring Boot Log4j - CVE-2021-44228 Docker Lab

A fast, simple, recursive content discovery tool written in Rust.

CMS Made Simple ≤ 2.2.9 SQL Injection Vulnerability CVE-2019-9053 is a vulnerability found in CMS Made Simple (CMSMS) versions up to 2.2.9, where the…

CMS Made Simple < 2.2.10 - SQL Injection (rewritten for python3), CVE-2019-905

Python tool to check and exploit CVE-2026-22812 in OpenCode, supporting command execution, file read, and multi-target scanning on ports 4095-4100.

Demonstrates detection of CVE-2023-50164 (Apache Struts RCE) with a simple Java app, intended for security testing and educational purposes.

User Enumeration vulnerability in Kaiten (workflow management system)