
CVE-2026-44011-poc
 khush-613/cve-2026-44011-poc
Python proof-of-concept exploit for CVE-2026-44011, an authenticated RCE in Craft CMS via Yii behavior injection, with two-stage command output…
exploitationpayload-developmentpenetration-testing+4
1
khush-613/cve-2026-44011-pocPython proof-of-concept exploit for CVE-2026-44011, an authenticated RCE in Craft CMS via Yii behavior injection, with two-stage command output…
 kitsuneshade/winrar-exploit-tool---rust-edition
A high-performance, memory-safe implementation of the WinRAR CVE-2025-8088 exploit tool, rewritten in Rust for better reliability and performance.
 wifiphisher/wifiphisher
Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…
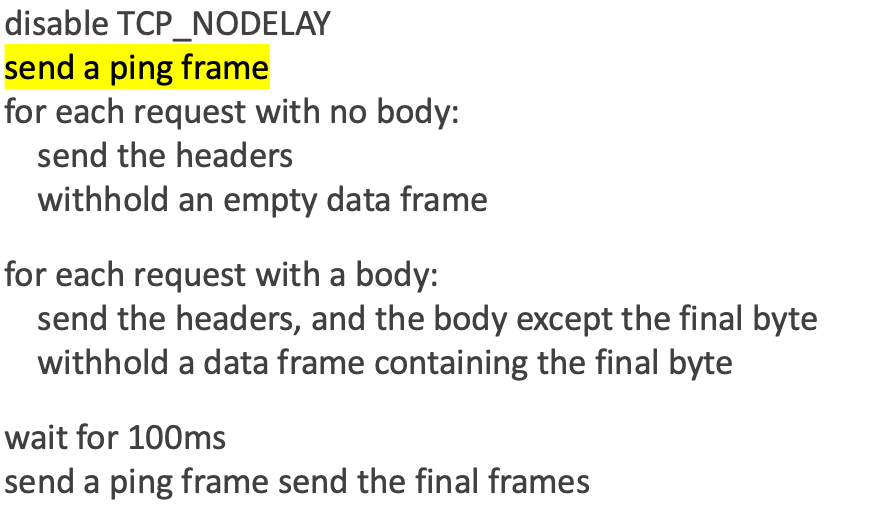 nxenon/h2spacex
HTTP/2 Last Frame Synchronization (also known as Single Packet Attack) low Level Library / Tool based on Scapy + Exploit Timing Attacks
 pericena/ciclopeclic
Security awareness training tool for authorized phishing simulations and internal IT audits
 mrcl0wnlab/simplesapachepathtraversal
Tool check: CVE-2021-41773, CVE-2021-42013, CVE-2020-17519
 ixzodiak/cve-2025-8110
Gogs service Exploit and get the root user
 ustayready/credsniper
CredSniper is a phishing framework written with the Python micro-framework Flask and Jinja2 templating which supports capturing 2FA tokens.
 stahlz/jqshell
Automated exploit tool for CVE-2018-9206 (jQuery File Upload) with single/multi-target scanning, Tor proxy support, and output logging for…
 cchopin/cve-arsenal-lab
TomcatScanner is a comprehensive security tool designed for detecting and exploiting the CVE-2025-24813 vulnerability in Apache Tomcat servers.
 speatx/react2shell-cve-2025-55182
CVE-2025-55182 — Unauthenticated RCE in React Server Components (React2Shell). CVSS 10.0 exploit tool for authorized penetration testing.
 mbechler/marshalsec
Java deserialization vulnerability exploitation tool with payload generators for multiple marshallers (Jackson, XStream, SnakeYAML) and JNDI…
 boreas37/cve-2026-56705
PoC exploit for Adminer < 5.4.3 unauthenticated RCE via MSSQL PDO DSN injection, including Docker lab and negative test.
 deadexpl0it/wp2shell-poc
wp2shell — WordPress Core Pre-Auth RCE Chain poc for CVE-2026-63030 and CVE-2026-60137
 frohoff/ysoserial
A proof-of-concept tool for generating payloads that exploit unsafe Java object deserialization.
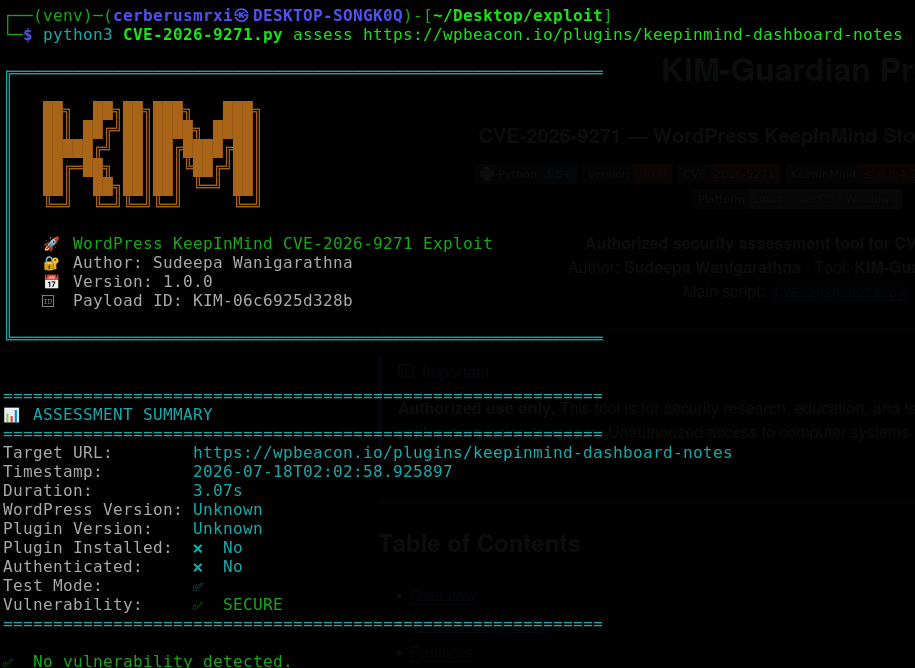 cerberusmrxi/wordpress-keepinmind-cve-2026-9271-exploit
Authorized stored XSS assessment tool for CVE-2026-9271 in WordPress KeepInMind plugin. Detects vulnerable versions, injects safe test payloads, and…
 jseidl/goldeneye
GoldenEye Layer 7 (KeepAlive+NoCache) DoS Test Tool
 bitt0n/cve-2026-0766
Proof-of-concept exploit for CVE-2026-0766, a remote code execution vulnerability in OpenWebUI via tool code injection. Includes command execution,…