

Hacking-Cheatsheets
 ilias1988/hacking-cheatsheets
A comprehensive collection of penetration testing cheatsheets, guides, and tools.
curated-resourcesdigital-forensicseducation+9
567
ilias1988/hacking-cheatsheetsA comprehensive collection of penetration testing cheatsheets, guides, and tools.
 enaqx/awesome-pentest
A collection of awesome penetration testing resources and tools
 efchatz/easy-exploits
Curated collection of proof-of-concept exploits for 16 CVEs targeting web applications (ASUS, D-Link, Netgear, TP-Link, Xiaomi) and Wi-Fi WPA3-SAE,…
 aramosf/joomla_exploits
Curated collection of validated Joomla exploit artifacts with Docker lab environments. Includes RCE, SQLi, XSS, and privilege escalation scripts…
 appsecco/vulnerable-mcp-servers-lab
A collection of servers which are deliberately vulnerable to learn Pentesting MCP Servers.
 redwaysecurity/cves
A collection of proof-of-concept exploit scripts written by the team at Redway Security for various CVEs.
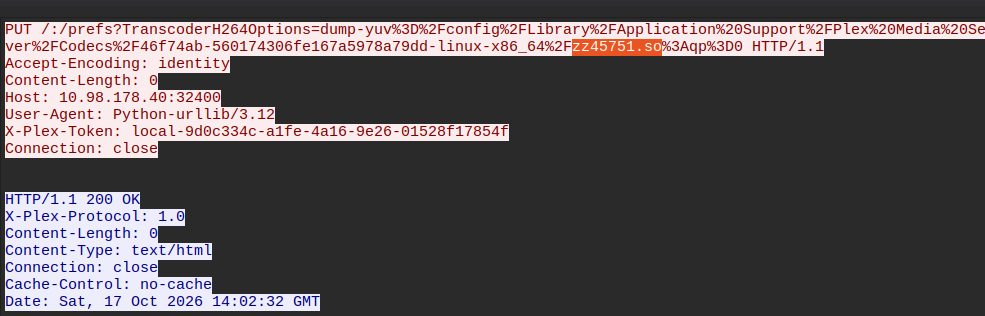 boredhackerblog/plex2shell_pcap
Packet capture artifacts of plex2shell exploitation against Plex, including lab and in-the-wild traffic, for building and validating detection…
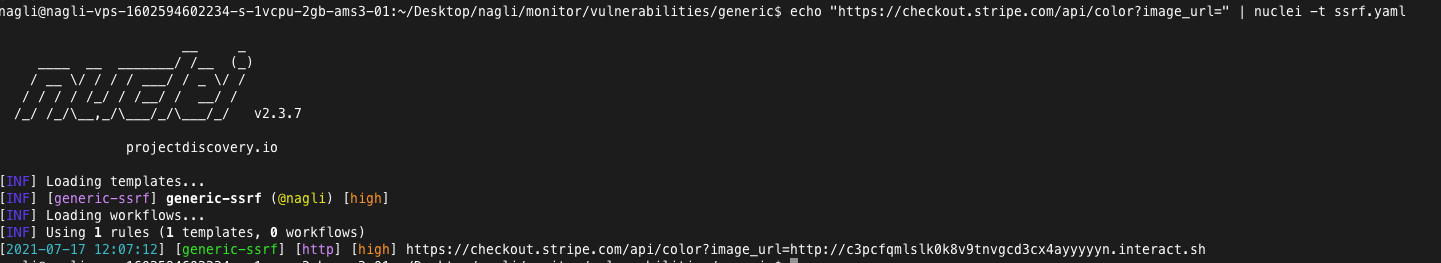 gal-nagli/shockwave-oss
Curated collection of bug bounty tips, one-liners, and automation workflows for recon, fuzzing, and web exploitation, with private nuclei templates…
 stealthcopter/wordpress-hacking
A collection of useful resources for hacking WordPress and it's plugins and themes
 0xblackash/cve-2026-72898
CVE-2026-72898
 hainhc/cve-2026-73570
Proof-of-concept exploit for CVE-2026-73570, an unauthenticated OS command injection in Zimbra Collaboration Suite via zimbra-snmp log injection,…
 0xdtc/js2py-sandbox-escape-cve-2024-28397-rce
Exploit scripts for CVE-2024-28397, a js2py sandbox escape that executes arbitrary Python code to spawn a reverse shell on a target endpoint.
 proviesec/xss-payload-list
Curated collection of cross-site scripting payloads, polyglots, and injection test rules for web application penetration testing and bug bounty…
 nu11secur1ty/payload-lists
Curated collection of injection payloads for web application security testing, covering SSTI, XXE, XSS, SSRF, SQLi, NoSQLi, LDAP, command injection,…
 protectai/ai-exploits
A collection of real world AI/ML exploits for responsibly disclosed vulnerabilities
 ananay/wp2shell-lab
Validation target: minimal WordPress core slice reproducing the wp2shell (CVE-2026-63030 + CVE-2026-60137) REST-to-SQLi chain
 onapsis/onapsis_cve-2025-31324_scanner_tools
Python-based scanner for CVE-2025-31324 that identifies vulnerable SAP NetWeaver Visual Composer instances and detects indicators of compromise from…
 serotav/writeups
Collection of detailed and optimized(?) write-ups for various CTF challenges