
 blacklanternsecurity/trevorproxy
A SOCKS proxy written in Python that randomizes your source IP address. Round-robin your evil packets through SSH tunnels or give them billions of…
 d4vinci/cuteit
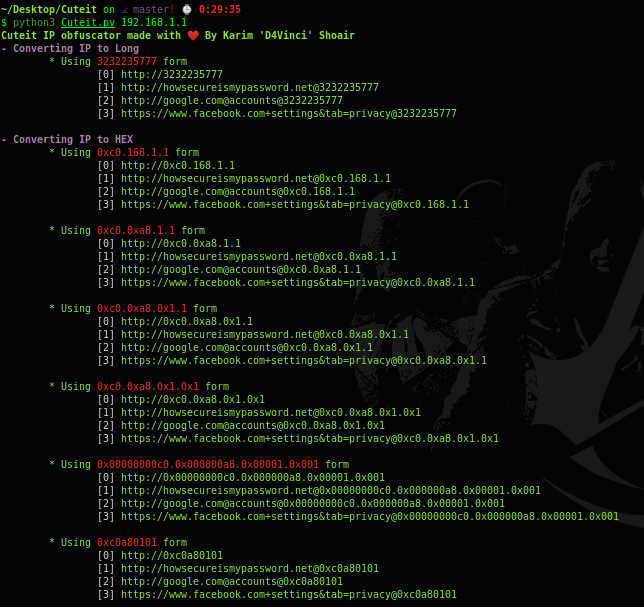
IP obfuscator made to make a malicious ip a bit cuter
 warflop/cloudbunny
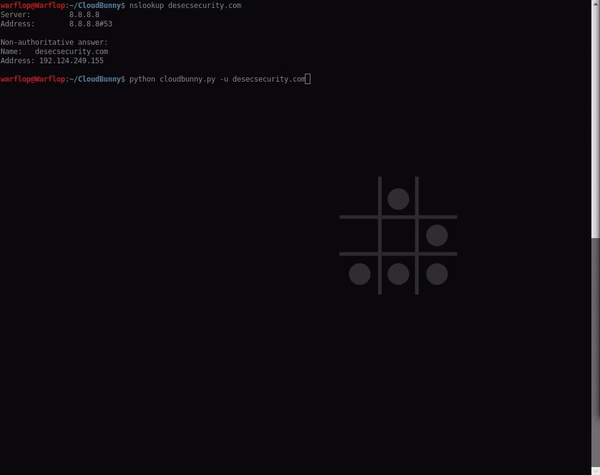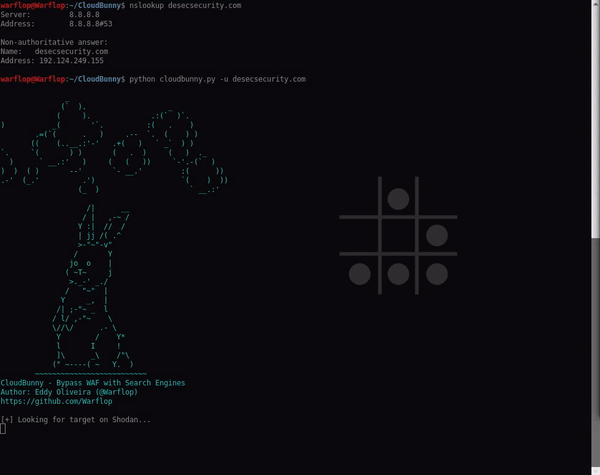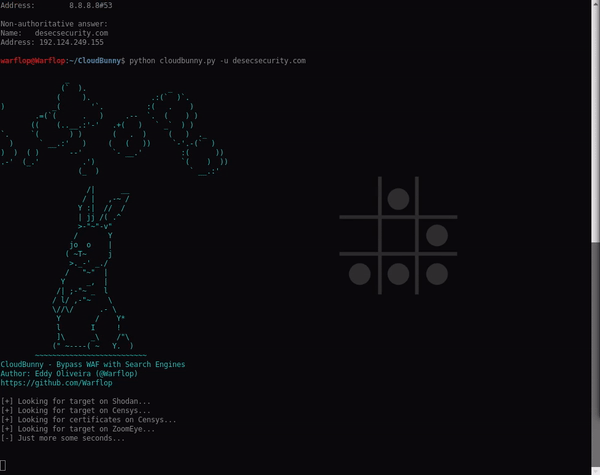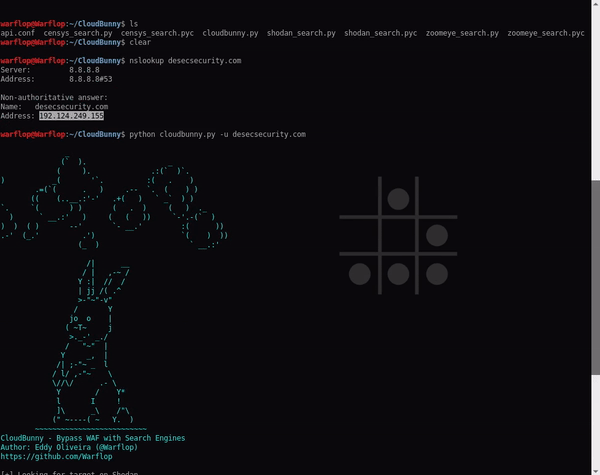
CloudBunny is a tool to capture the real IP of the server that uses a WAF as a proxy or protection. In this tool we used three search engines to…
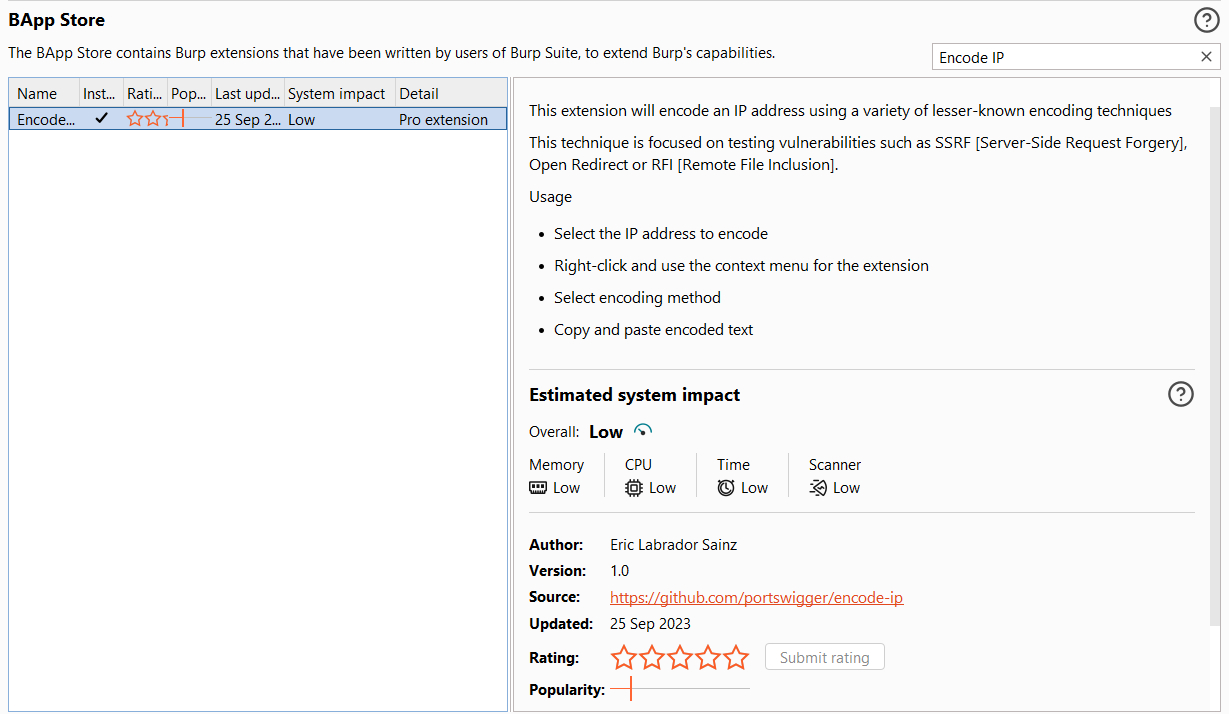 e1abrador/burp-encode-ip
Burp Suite extension to encode an IP address focused to bypass application IP / domain blacklist.
 ge0rg3/requests-ip-rotator
A Python library to utilize AWS API Gateway's large IP pool as a proxy to generate pseudo-infinite IPs for web scraping and brute forcing.
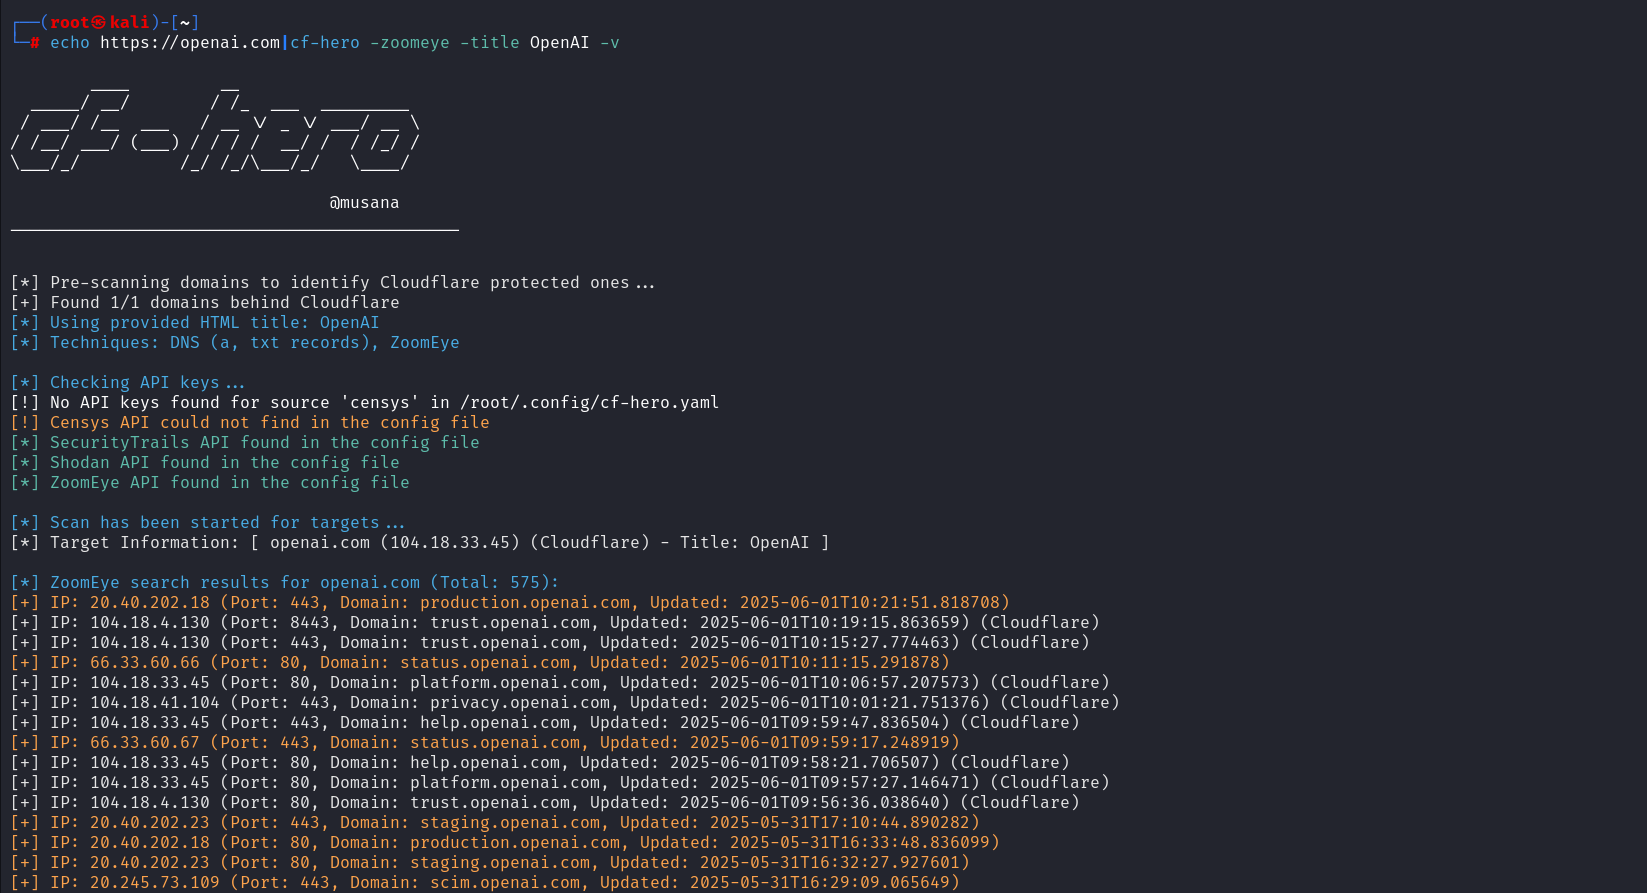 musana/cf-hero
CF-Hero is a reconnaissance tool that uses multiple data sources to discover the origin IP addresses of Cloudflare-protected web applications
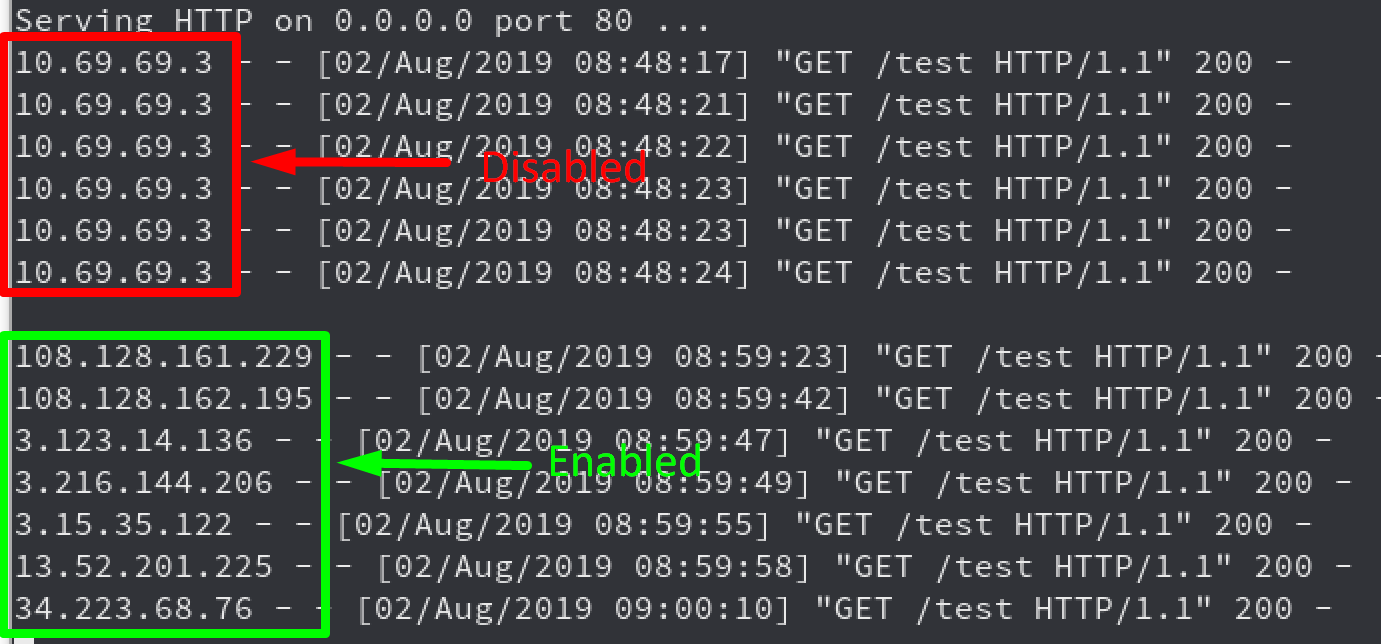 rhinosecuritylabs/iprotate_burp_extension
Extension for Burp Suite which uses AWS API Gateway to rotate your IP on every request.
 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
 immunit/xip
XIP generates a list of IP addresses by applying a set of transformations used to bypass security measures e.g. blacklist filtering, WAF, etc.
 hackinglz/ip-obfuscation
Generates obfuscated IP addresses and URLs using DWORD, octal, hex, IPv6-mapped, and fake-domain @ tricks for penetration testing, phishing…
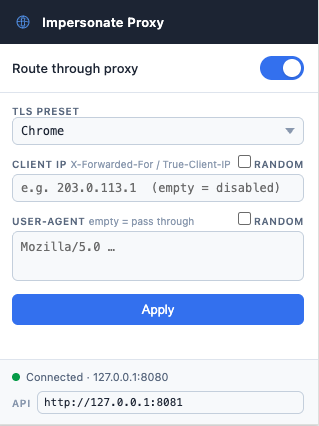 ytkoka/impersonate-proxy
A local MITM proxy that lets you control TLS fingerprints (JA3/JA4), HTTP/2 fingerprints, HTTP header order, and User-Agent — all from a single YAML…
 abdurahmon3236/cve-2022-4539
Exploit for CVE-2022-4539 that spoofs X-Forwarded-For headers to bypass WordPress WAF IP-based login and logging restrictions. Includes scalable…