

teler-waf
 teler-sh/teler-waf
teler-waf is a Go HTTP middleware that protects local web services from OWASP Top 10 threats, known vulnerabilities, malicious actors, botnets,…
api-securitydefensive-toolsids-ips-evasion+5
teler-sh/teler-wafteler-waf is a Go HTTP middleware that protects local web services from OWASP Top 10 threats, known vulnerabilities, malicious actors, botnets,…

 lobuhi/byp4xx
40X/HTTP bypasser in Go. Features: Verb tampering, headers, #bugbountytips, User-Agents, extensions, default credentials...
 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
 m4xsec/wp2shell-exploit-waf-bypass
WordPress Pre-Auth RCE Exploit + Scanner + WAF Bypass | CVE-2026-63030 + CVE-2026-60137 | Go + Python + Metasploit modules + Docker lab
 c00ln3t/log4shellauditor
An autonomous reflective Go agent for full-cycle security auditing, WAF evasion, OOB LDAP verification, self-remediation (auto-patching), and…
 ummitkin/cve-2025-55182-poc
react2shell PoC with Go / CVE-2025-55182
 h0tak88r/next88
High-performance Go implementation for detecting React Server Components RCE vulnerabilities (CVE-2025-55182 & CVE-2025-66478).
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 sleeyax/burp-awesome-tls
Burp extension to evade TLS fingerprinting. Bypass WAF, spoof any browser.
 devploit/nomore403
🚫 Advanced tool for security researchers to bypass 403/40X restrictions through smart techniques and adaptive request manipulation. Fast. Precise.…
 fzakaria/anubis-fetch
Like curl, but it gets past Anubis and Cloudflare bot-walls.
 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
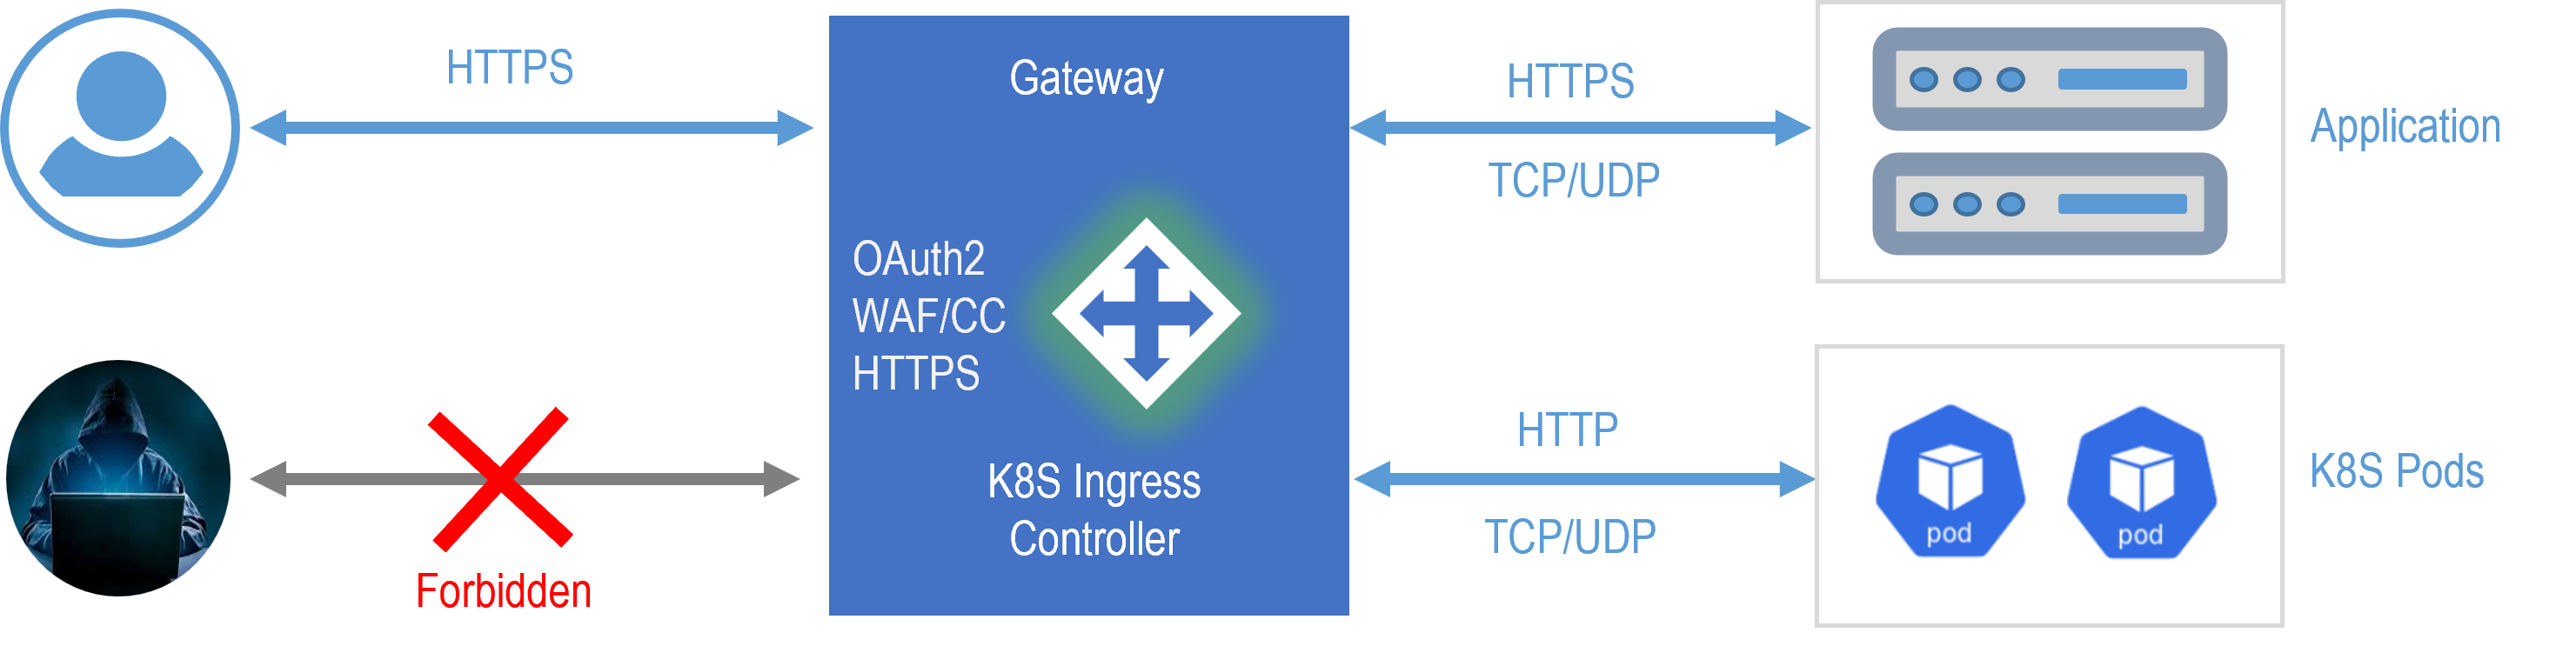 janusec/janusec
Unified application gateway providing reverse proxy, WAF, CC defense, OAuth2 authentication, ACME certificate automation, and GSLB for secure,…
 assetnote/nowafpls
Burp Plugin to Bypass WAFs through the insertion of Junk Data
 c0dejump/hawkscan
Security Tool for Reconnaissance and Information Gathering on a website. (python 3.x)
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
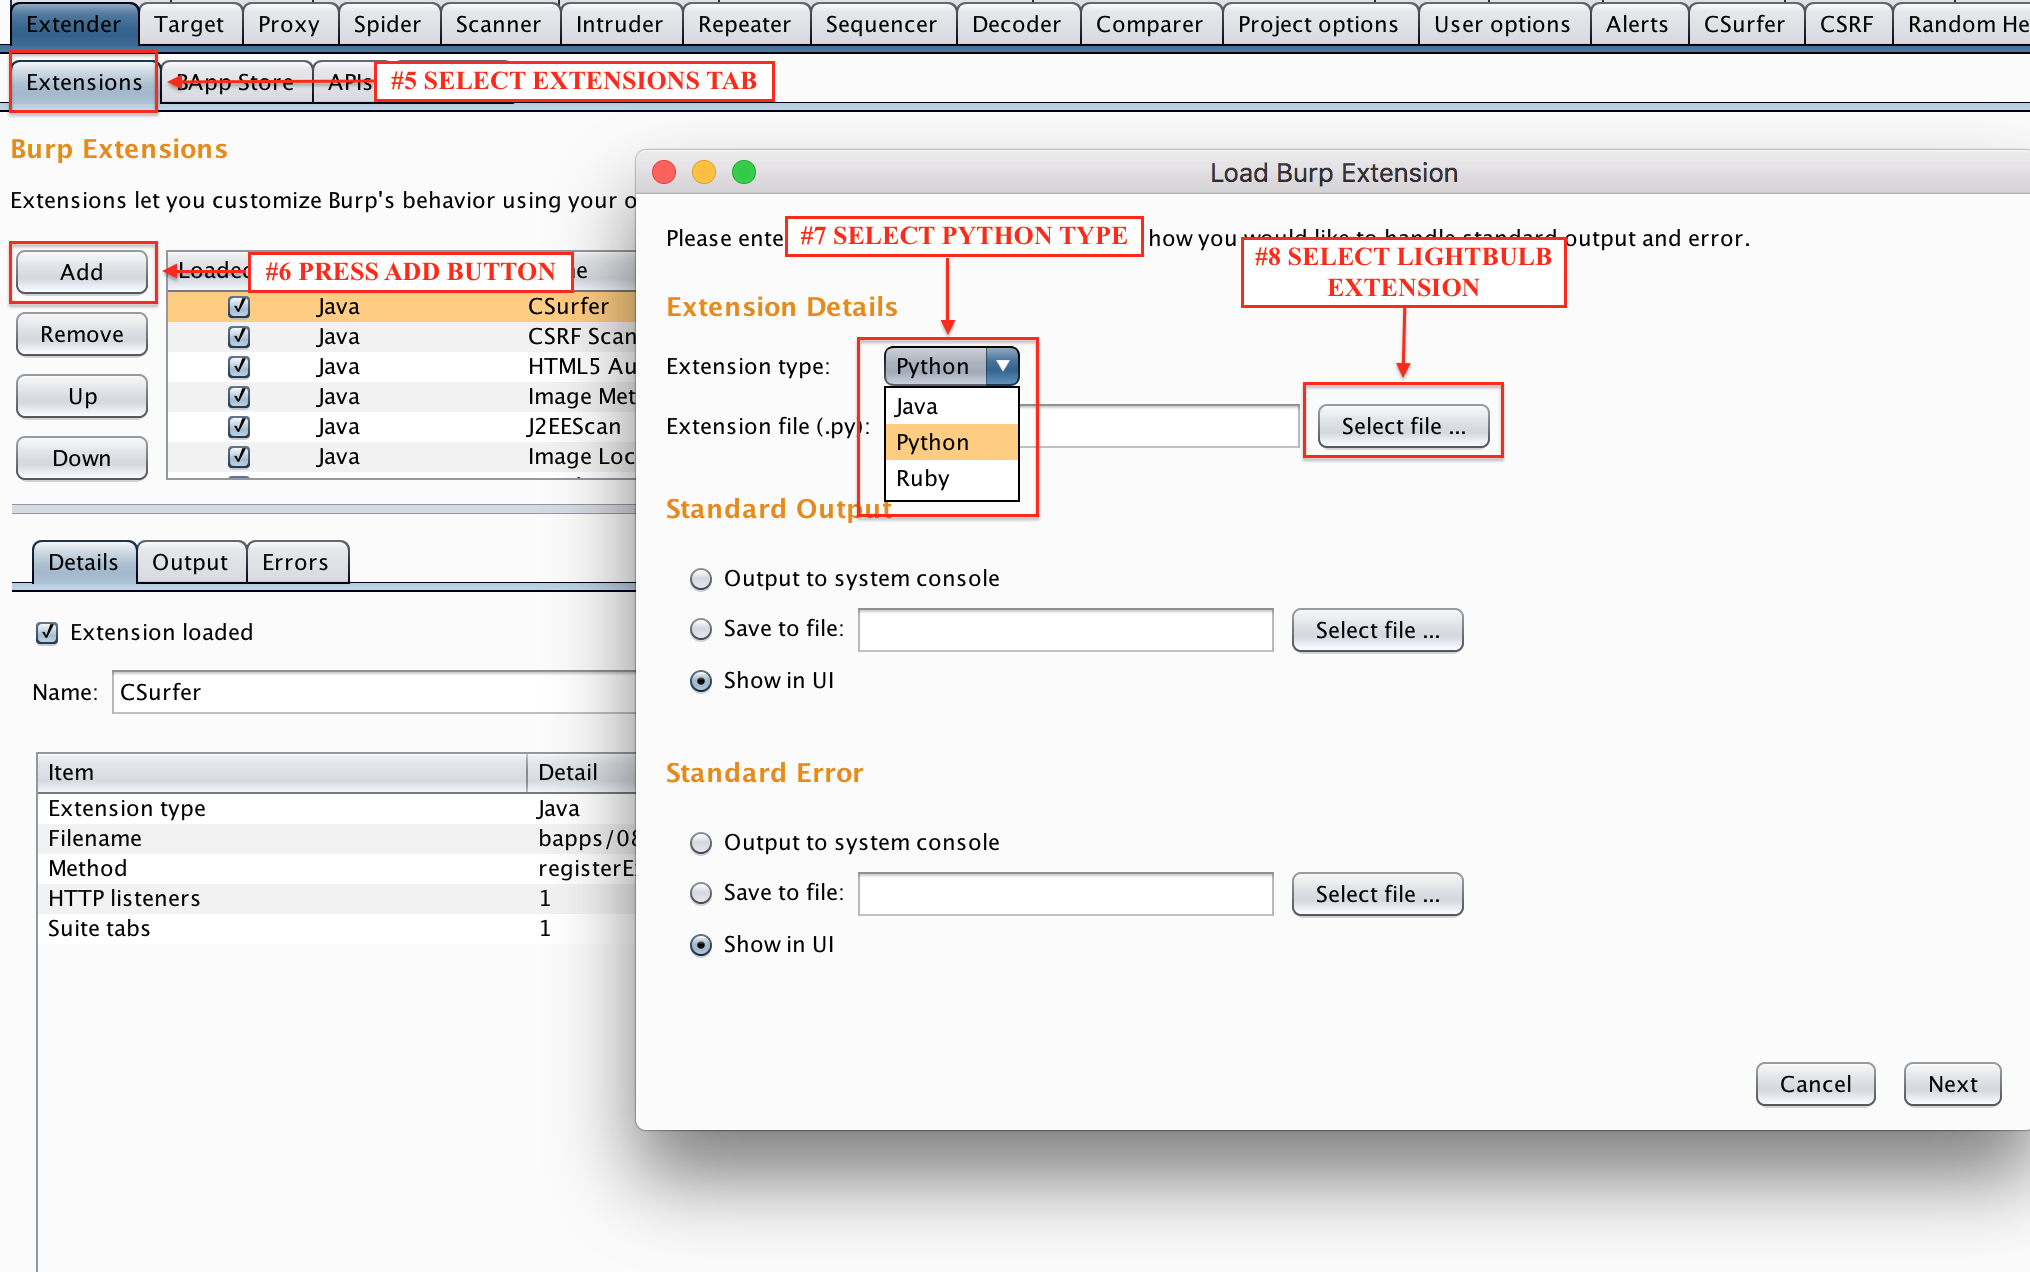 lightbulb-framework/lightbulb-framework
Tools for auditing WAFS