bypass-firewalls-by-DNS-history

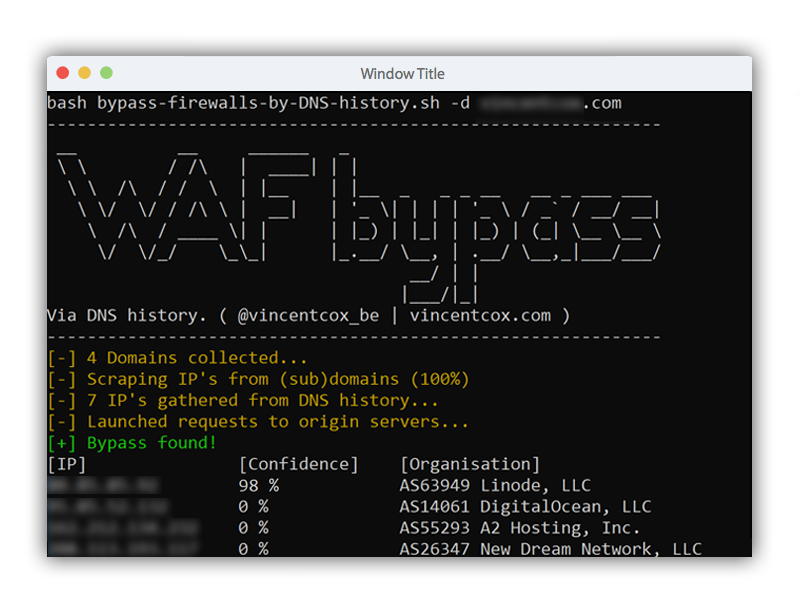
Firewall bypass script based on DNS history records. This script will search for DNS A history records and check if the server replies for that…

Firewall bypass script based on DNS history records. This script will search for DNS A history records and check if the server replies for that…

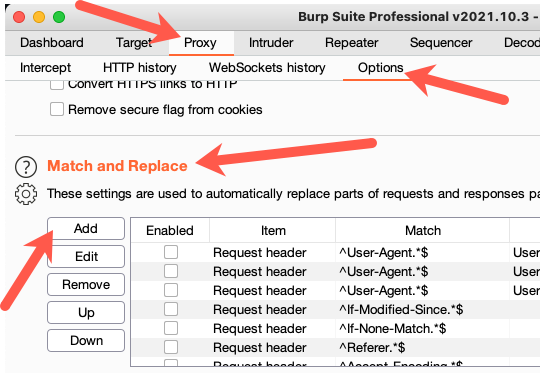
Extension for Burp Suite which uses AWS API Gateway to rotate your IP on every request.

Security Tool for Reconnaissance and Information Gathering on a website. (python 3.x)

Bash 403/401 access bypass tester that probes a URL with header spoofing, method tampering, path normalization, and encoding techniques, returning a…

Stealth dropper executing remote binaries without dropping them on disk .(HTTP3 support, ICMP support, invisible tracks, cross-platform,...)

PHP CVE-2026-109618/109619 — self-contained unauthenticated RCE on stock PHP 8.5.11 (in-band PS(id)→cookie memory disclosure + UAF chain), full…

Multi-domain HTTP 403 bypass scanner that tests header manipulation techniques to discover hidden access paths on web servers, supporting bulk domain…

Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.

Exploit for Imperva Cloud WAF bypass using gzip Content-Encoding header to evade WAF rules on HTTP POST requests. Includes detection script and…

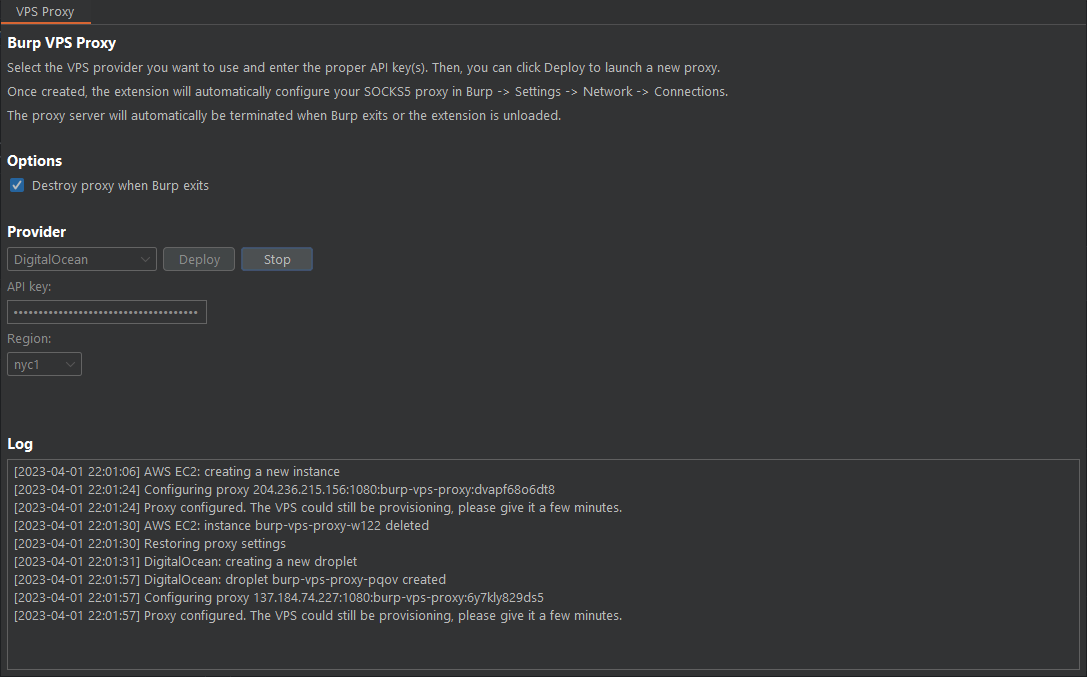
This Burp Suite extension allows for the automatic creation and deletion of an upstream SOCKS5 proxy on popular cloud services.

SQL injection script for MSSQL that extracts domain users from an Active Directory environment based on RID bruteforcing

XSS Fuzzer is a tool which generates XSS payloads based on user-defined vectors and fuzzing lists.

Bash script that adds custom HTTP headers to requests for bulk testing of 403 bypass techniques on web applications.

This repository contains all gathered resources we used during our Incident Reponse on CVE-2021-44228 and CVE-2021-45046 aka Log4Shell.

xpath is a fast, multi-technique XPath injection scanner written in Nim. It focuses on practical detection, response comparison, visible extraction,…

This room is based on exploiting the notorious Log4j vulnerability ( CVE-2021-44228), also referred to as the Log4Shell. The weakness enables…

Demonstration on exploitation on Drupal 7.57 (CVE-2018-7600) with and without WAF(Web Application Firewall)

Hands-on lab on detecting and mitigating web app threats using OWASP ZAP, Burp Suite, and ModSecurity WAF (with OWASP CRS). Case study: Spring4Shell…