CVE-2025-55182-POC
Go-based scanner and exploitation tool for CVE-2025-55182 (Next.js RCE). Supports batch scanning, command execution, Godzilla memory shell injection,…

Go-based scanner and exploitation tool for CVE-2025-55182 (Next.js RCE). Supports batch scanning, command execution, Godzilla memory shell injection,…

Exploit for CVE-2024-4577 PHP-CGI RCE on Windows, with WAF bypass and SSRF support. Provides multiple exploit variants for default, WAF, and SSRF…

Precision-Based Detection of RSC/Next.js Remote Code Execution Vulnerabilities (CVE-2025-55182, CVE-2025-66478)

SQL injection script for MSSQL that extracts domain users from an Active Directory environment based on RID bruteforcing

Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…

An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses

High Fidelity Detection Mechanism for RSC/Next.js RCE (CVE-2025-55182 & CVE-2025-66478)

Firewall bypass script based on DNS history records. This script will search for DNS A history records and check if the server replies for that…

A Burp Suite extension for identifying injection flaws (LFI, RCE, SQLi), authentication/authorization issues, and HTTP 403 access violations. It…

Advanced security testing tool for CVE-2025-55182 vulnerability assessment in Next.js applications. Features interactive shell, batch scanning, WAF…

An advanced command-line framework for discovery, validation, and exploitation of CVE-2025-55182 and CVE-2025-66478 affecting Next.js applications…

Multi-technique vulnerability detector for CVE-2025-55182 in React/Next.js applications. Tests gadget chains, RCE payloads, and WAF bypass variants…

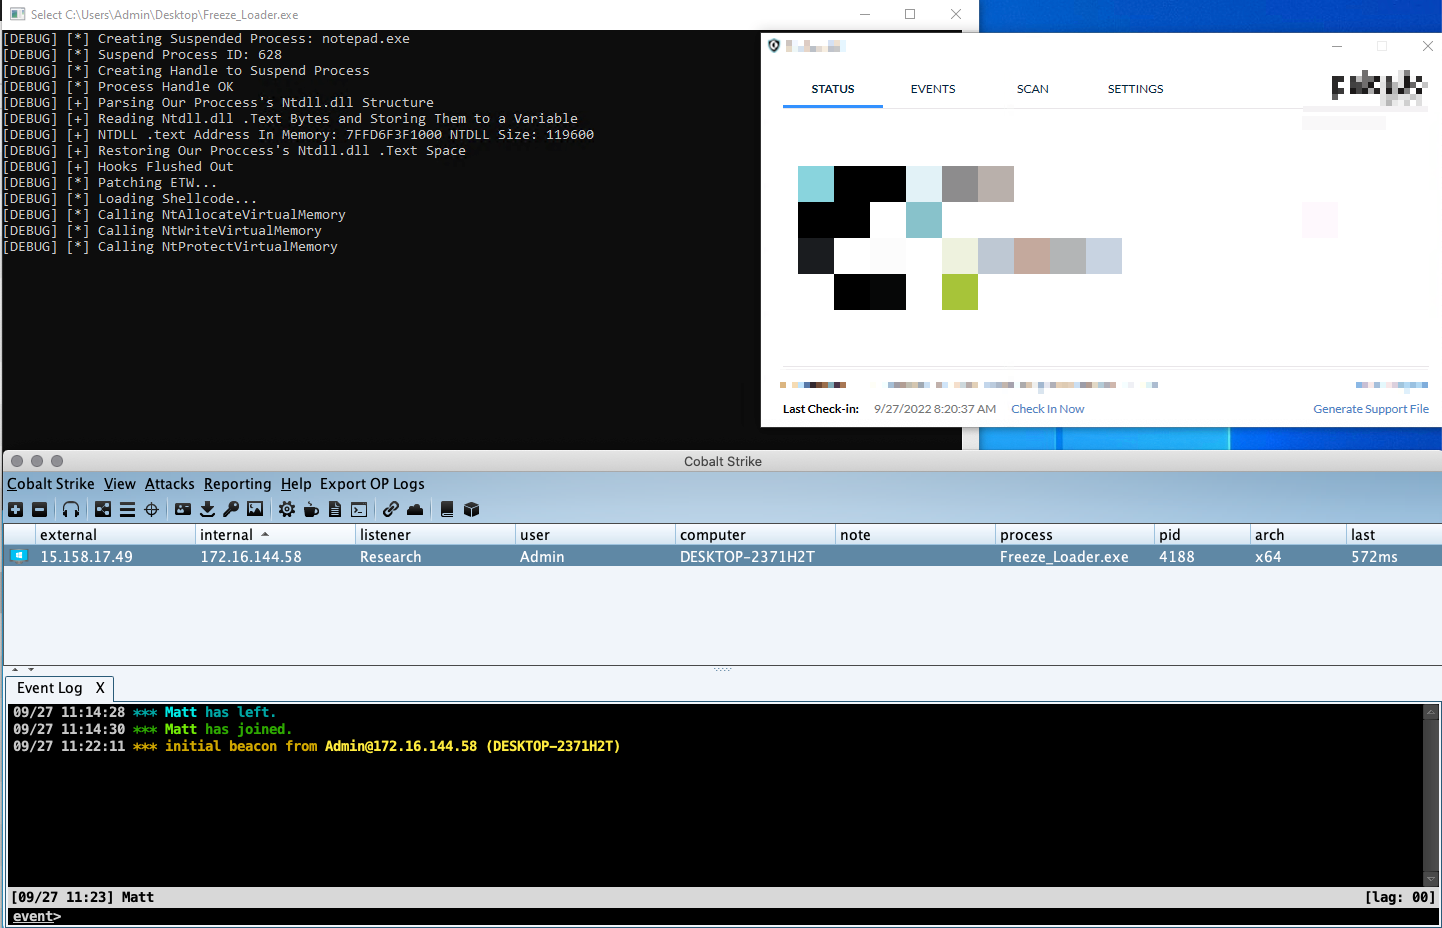
Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods

Automated Tool That Generates The Perfect Meterpreter Powershell Payload

Local file inclusion exploitation tool

Stealth dropper executing remote binaries without dropping them on disk .(HTTP3 support, ICMP support, invisible tracks, cross-platform,...)

XSSYA (Cross Site Scripting Scanner & Vulnerability Confirmation)

RSC/Next.js RCE (CVE-2025-55182 & CVE-2025-66478)