

coreruleset
 coreruleset/coreruleset
Generic attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…
anti-botids-ips-evasionmisconfiguration+4
3.3k
coreruleset/corerulesetGeneric attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…
 urbanadventurer/whatweb
Next generation web scanner
 kaliiiiiiiiii-vinyzu/patchright
Undetected version of the Playwright testing and automation library.
 enablesecurity/wafw00f
Automated Web Application Firewall fingerprinting tool that identifies and detects over 200 WAF products by analyzing HTTP responses to normal and…
 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
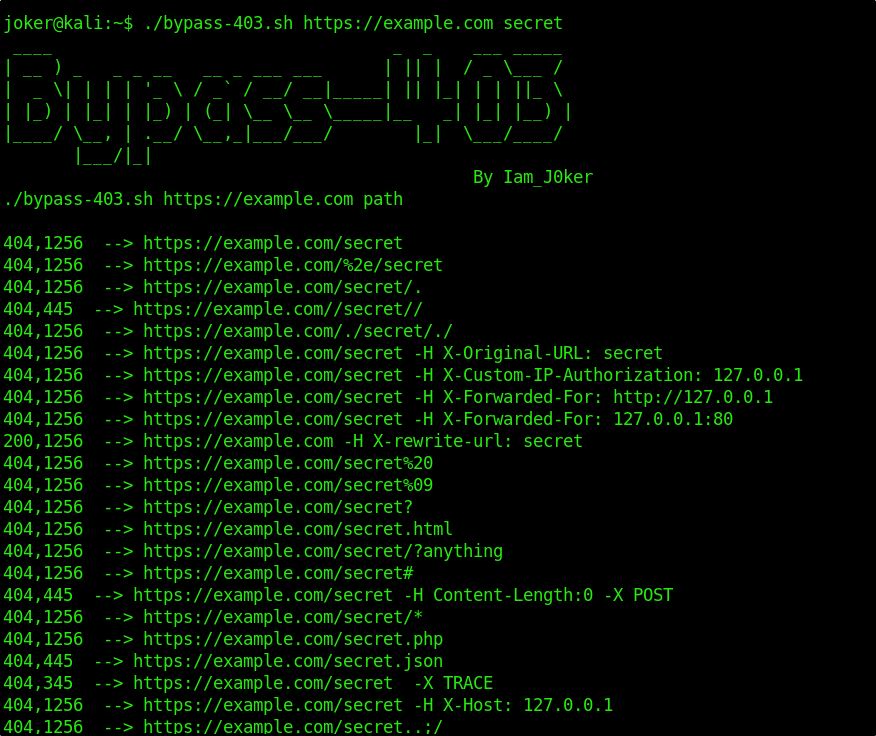 iamj0ker/bypass-403
A simple script just made for self use for bypassing 403
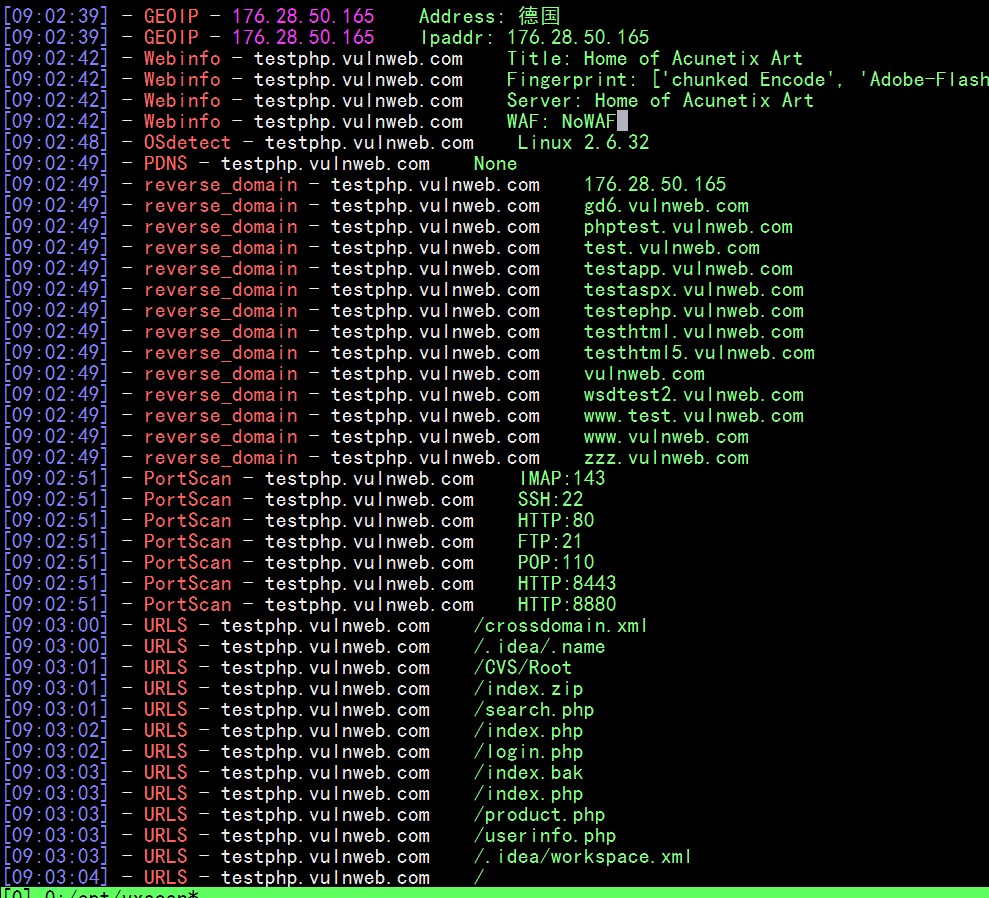 al0ne/vxscan
python3写的综合扫描工具,主要用来存活验证,敏感文件探测(目录扫描/js泄露接口/html注释泄露),WAF/CDN识别,端口扫描,指纹/服务识别,操作系统识别,POC扫描,SQL注入,绕过CDN,查询旁站等功能,主要用来甲方自测或乙方授权测试,请勿用来搞破坏。
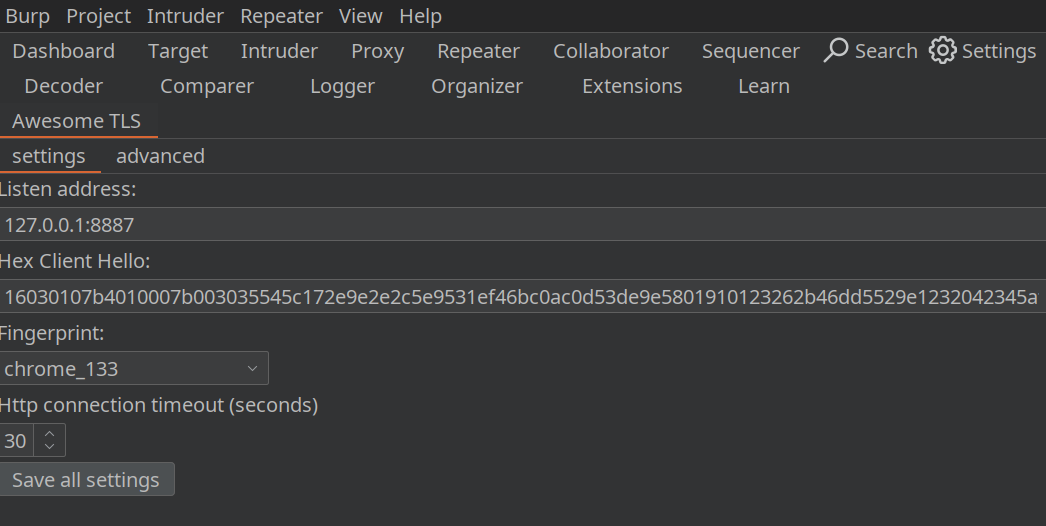 sleeyax/burp-awesome-tls
Burp extension to evade TLS fingerprinting. Bypass WAF, spoof any browser.
 lobuhi/byp4xx
40X/HTTP bypasser in Go. Features: Verb tampering, headers, #bugbountytips, User-Agents, extensions, default credentials...
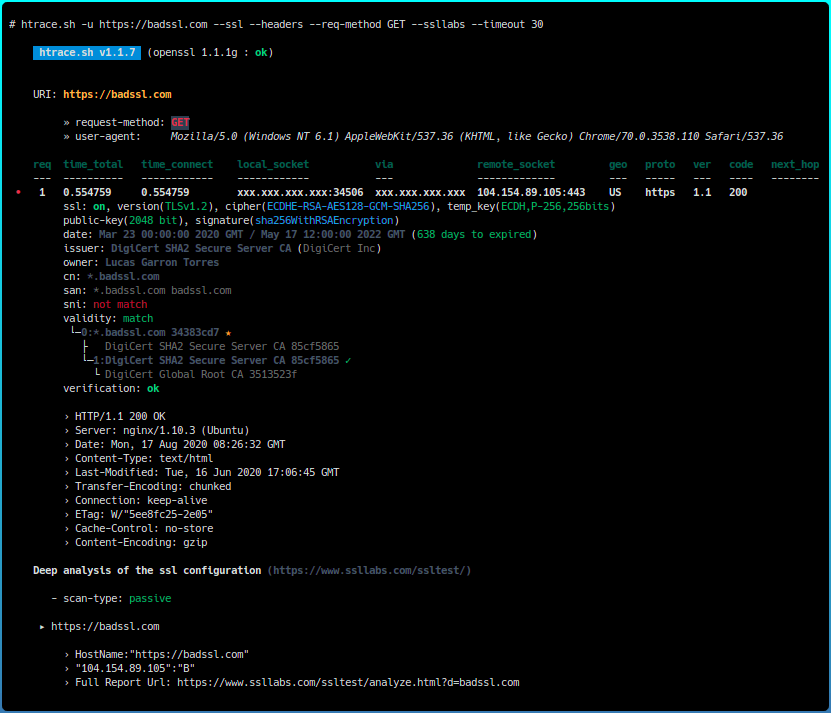 trimstray/htrace.sh
My simple Swiss Army knife for http/https troubleshooting and profiling.
 mandatoryprogrammer/thermoptic
A next-generation HTTP stealth proxy which perfectly cloaks requests as the Chrome browser across all layers of the stack.
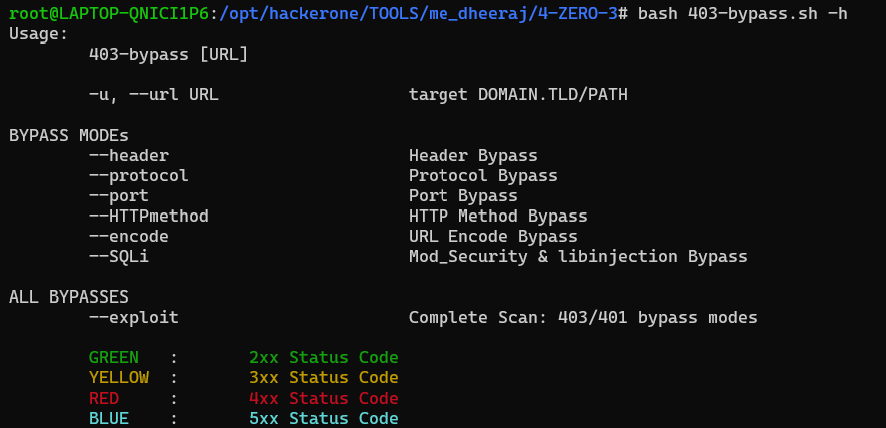 dheerajmadhukar/4-zero-3
403/401 Bypass Methods + Bash Automation + Your Support ;)
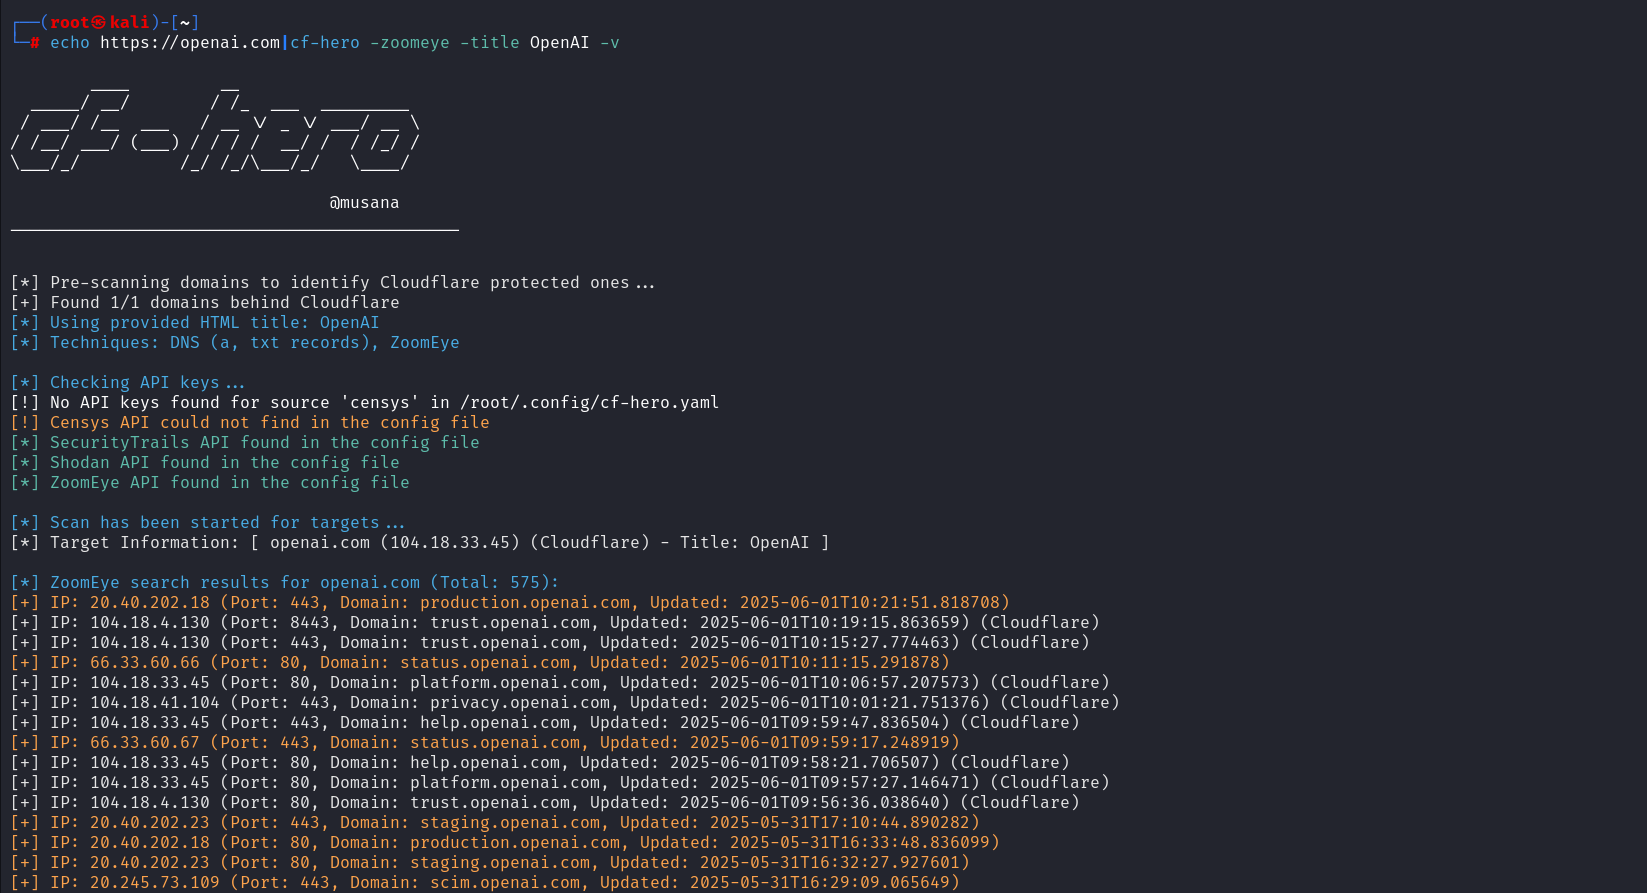 musana/cf-hero
CF-Hero is a reconnaissance tool that uses multiple data sources to discover the origin IP addresses of Cloudflare-protected web applications
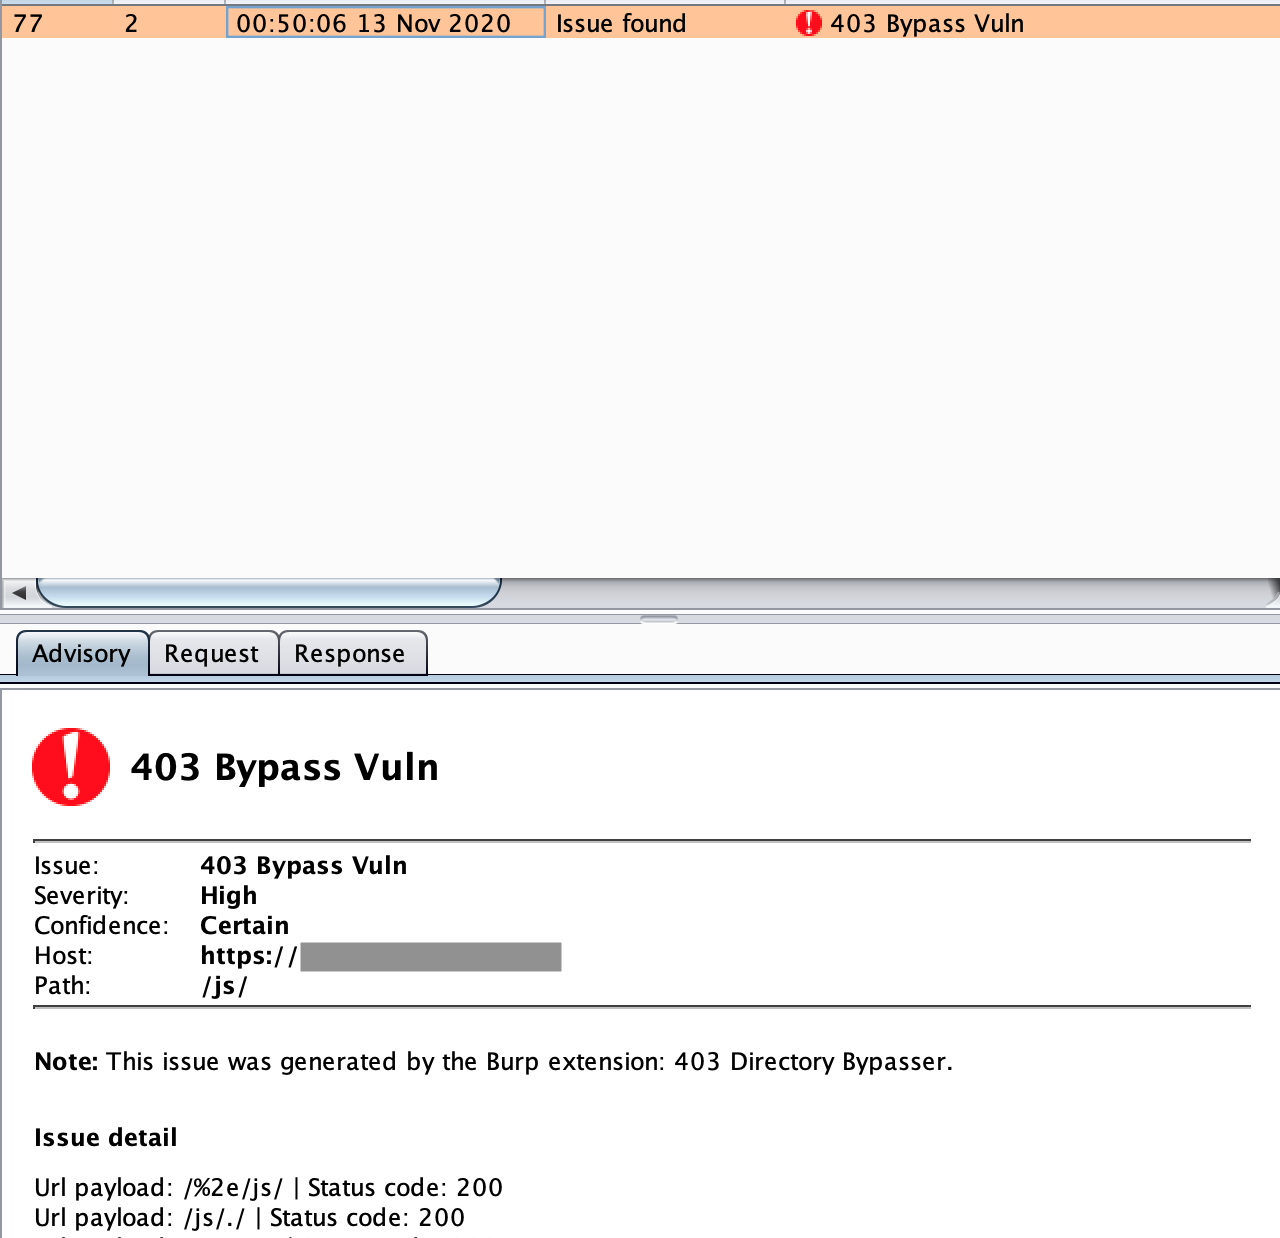 sting8k/burpsuite_403bypasser
Burpsuite Extension to bypass 403 restricted directory
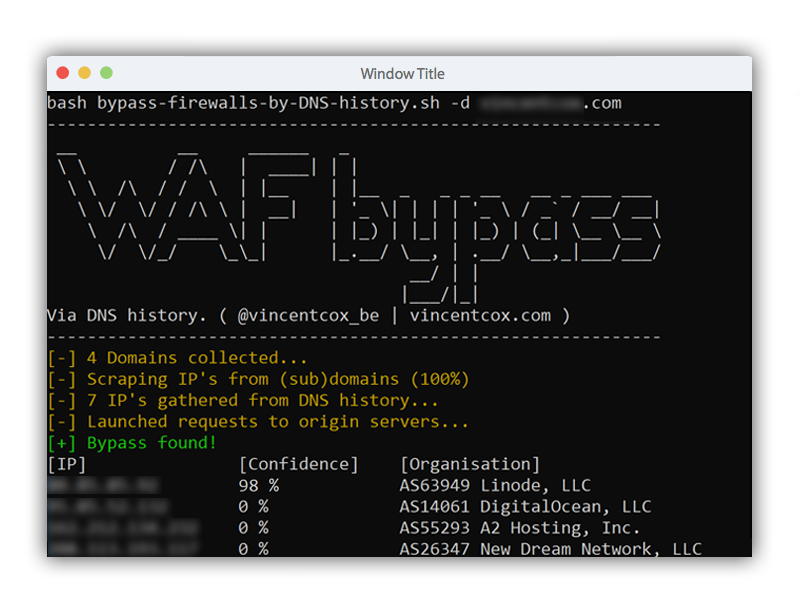 vincentcox/bypass-firewalls-by-dns-history
Firewall bypass script based on DNS history records. This script will search for DNS A history records and check if the server replies for that…
 hakluke/hakoriginfinder
Tool for discovering the origin host behind a reverse proxy. Useful for bypassing cloud WAFs!
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
 devploit/nomore403
🚫 Advanced tool for security researchers to bypass 403/40X restrictions through smart techniques and adaptive request manipulation. Fast. Precise.…