
sqlmap
 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
api-securityapi-security-testingcrawler+12
sqlmapproject/sqlmapAutomatic SQL injection and database takeover tool
 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
 commixproject/commix
Automated Αll-in-One OS command injection exploitation tool.
 hahwul/dalfox
Fast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…
 bhideki/cve-2026-87902
Python PoC and scanner for CVE-2026-87902, a WordPress core path traversal leading to LFI and PEAR-based RCE, with WAF bypass and automated…
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 ytkoka/impersonate-proxy
A local MITM proxy that lets you control TLS fingerprints (JA3/JA4), HTTP/2 fingerprints, HTTP header order, and User-Agent — all from a single YAML…
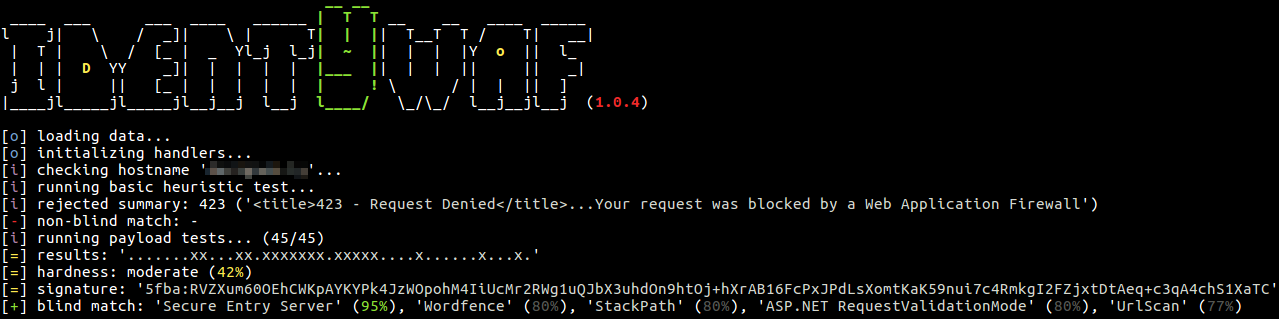 stamparm/identywaf
Blind WAF identification tool
 fzakaria/anubis-fetch
Like curl, but it gets past Anubis and Cloudflare bot-walls.
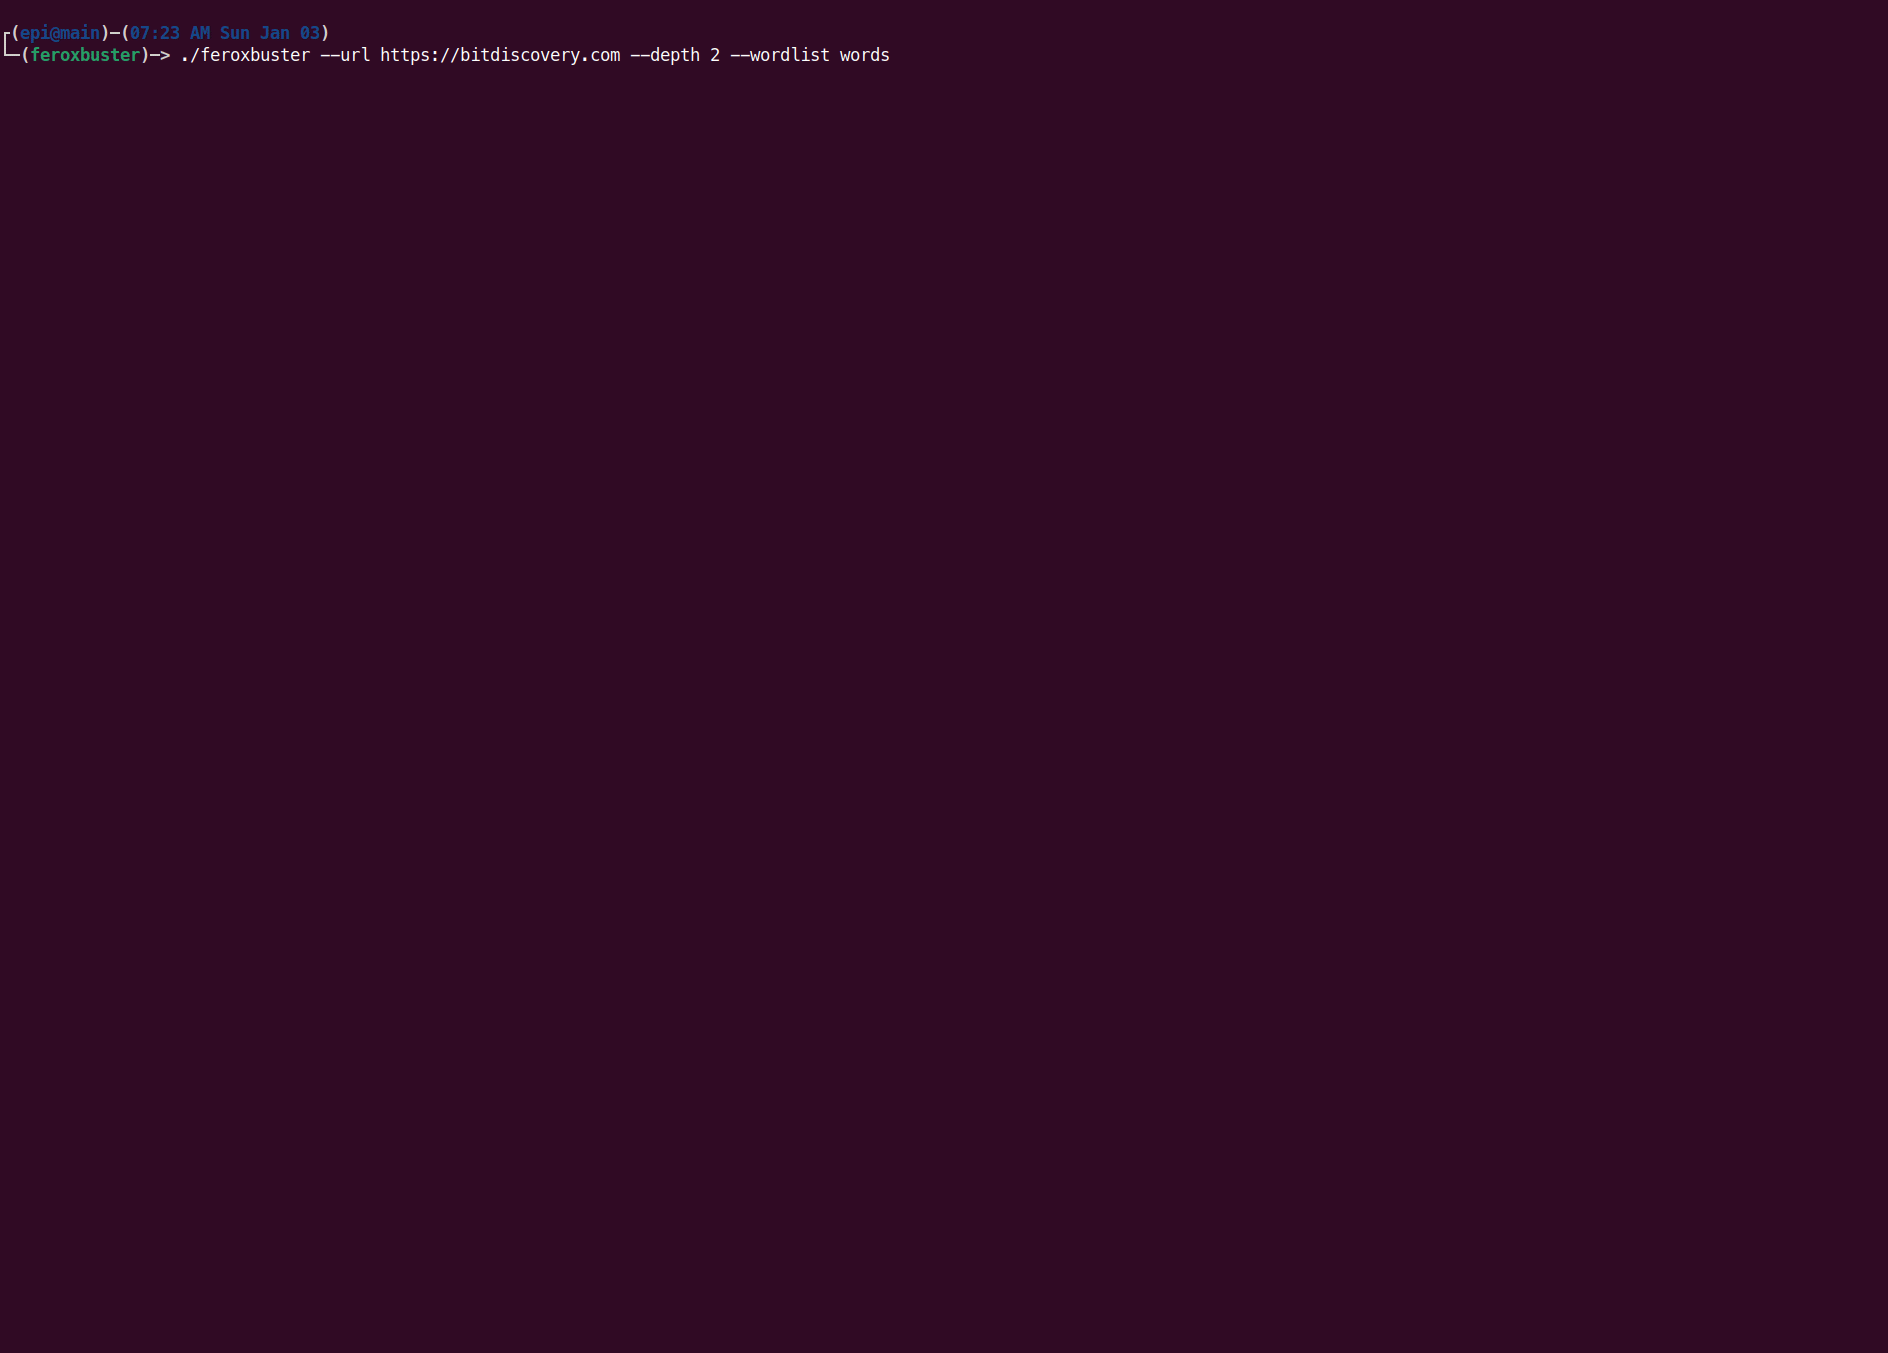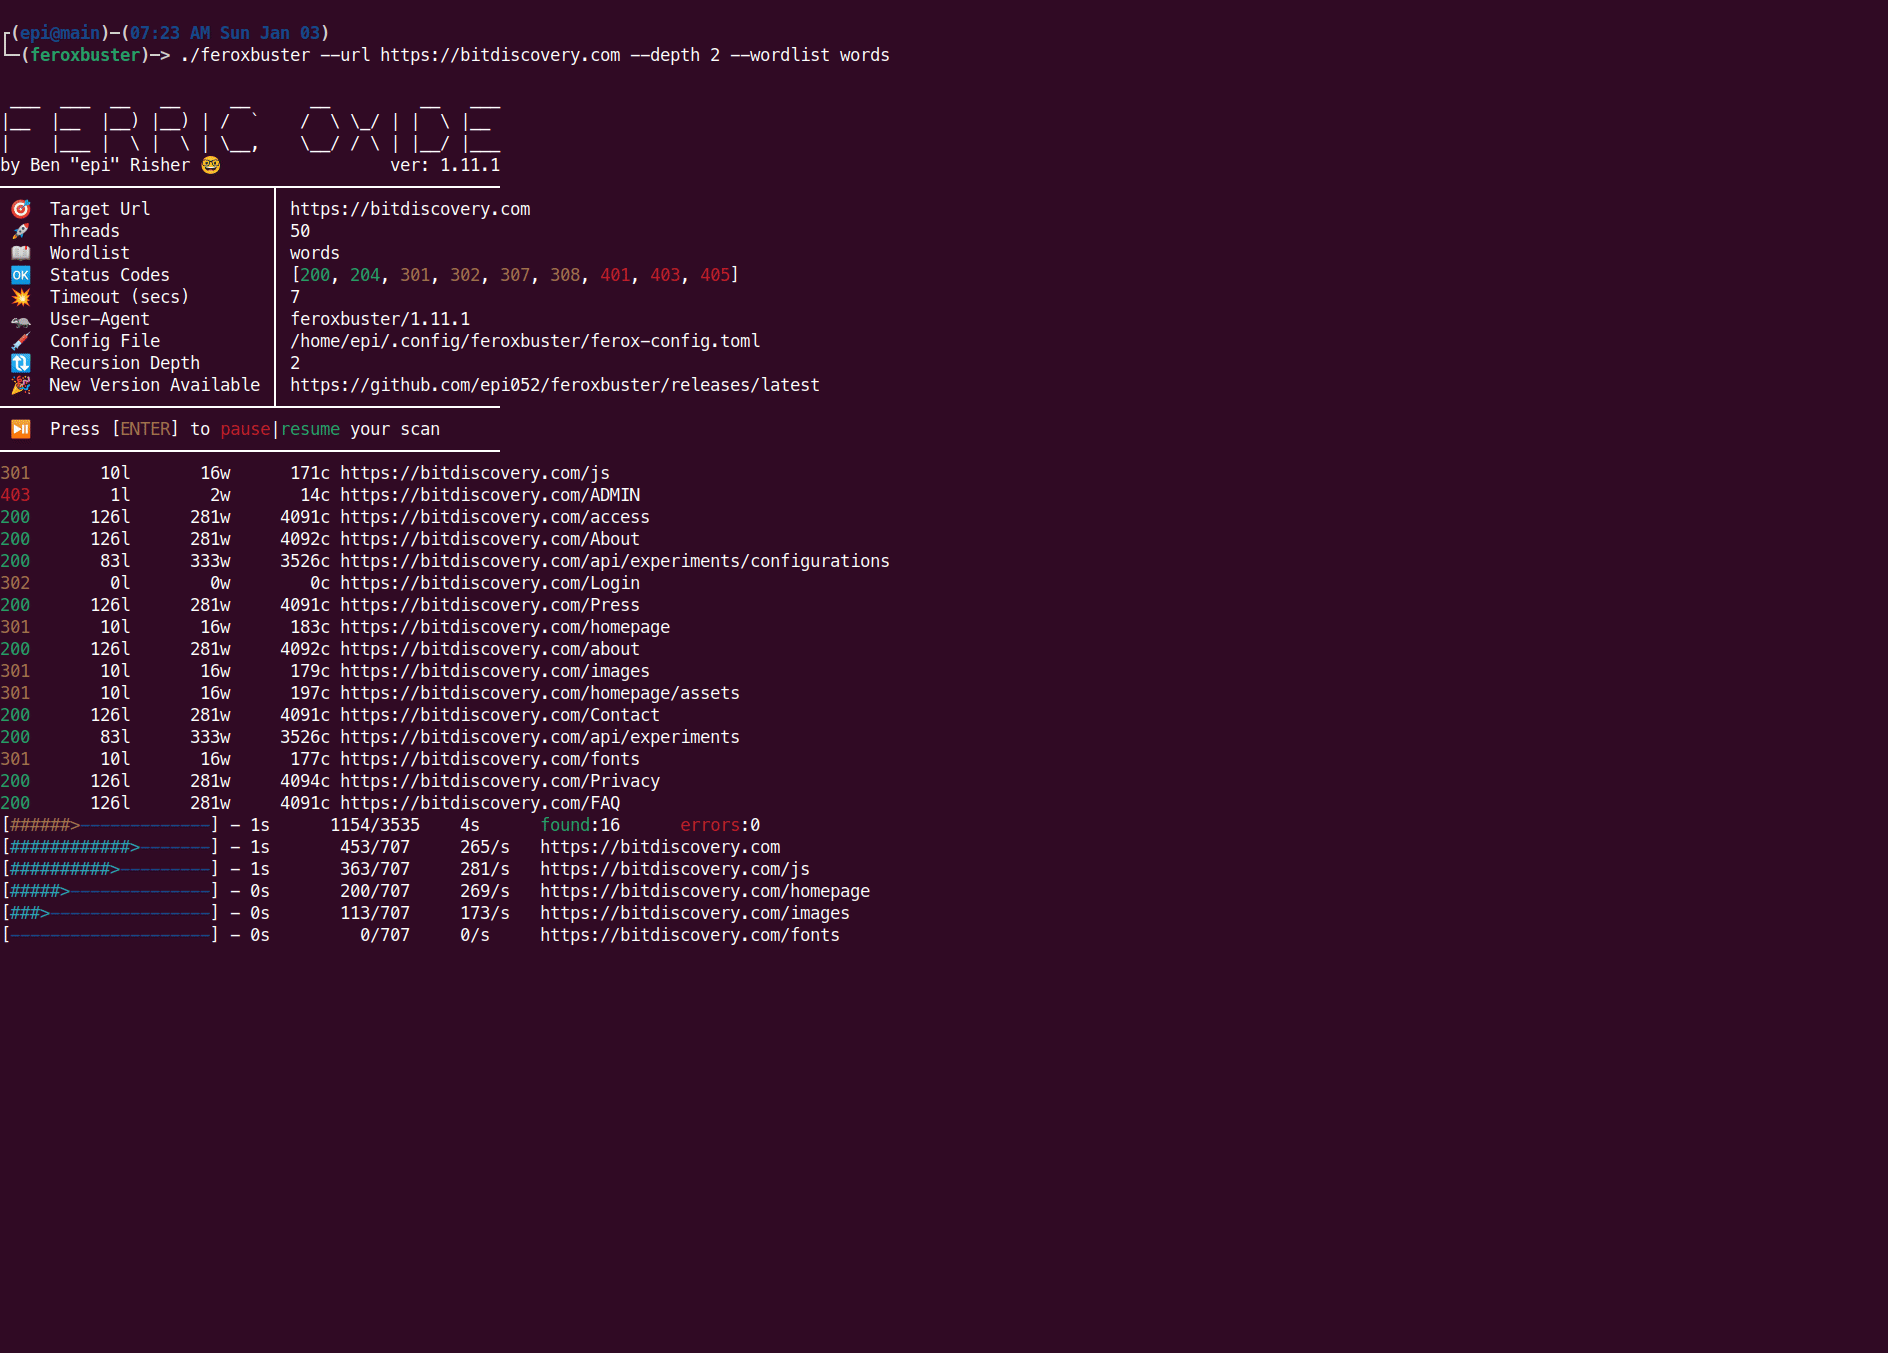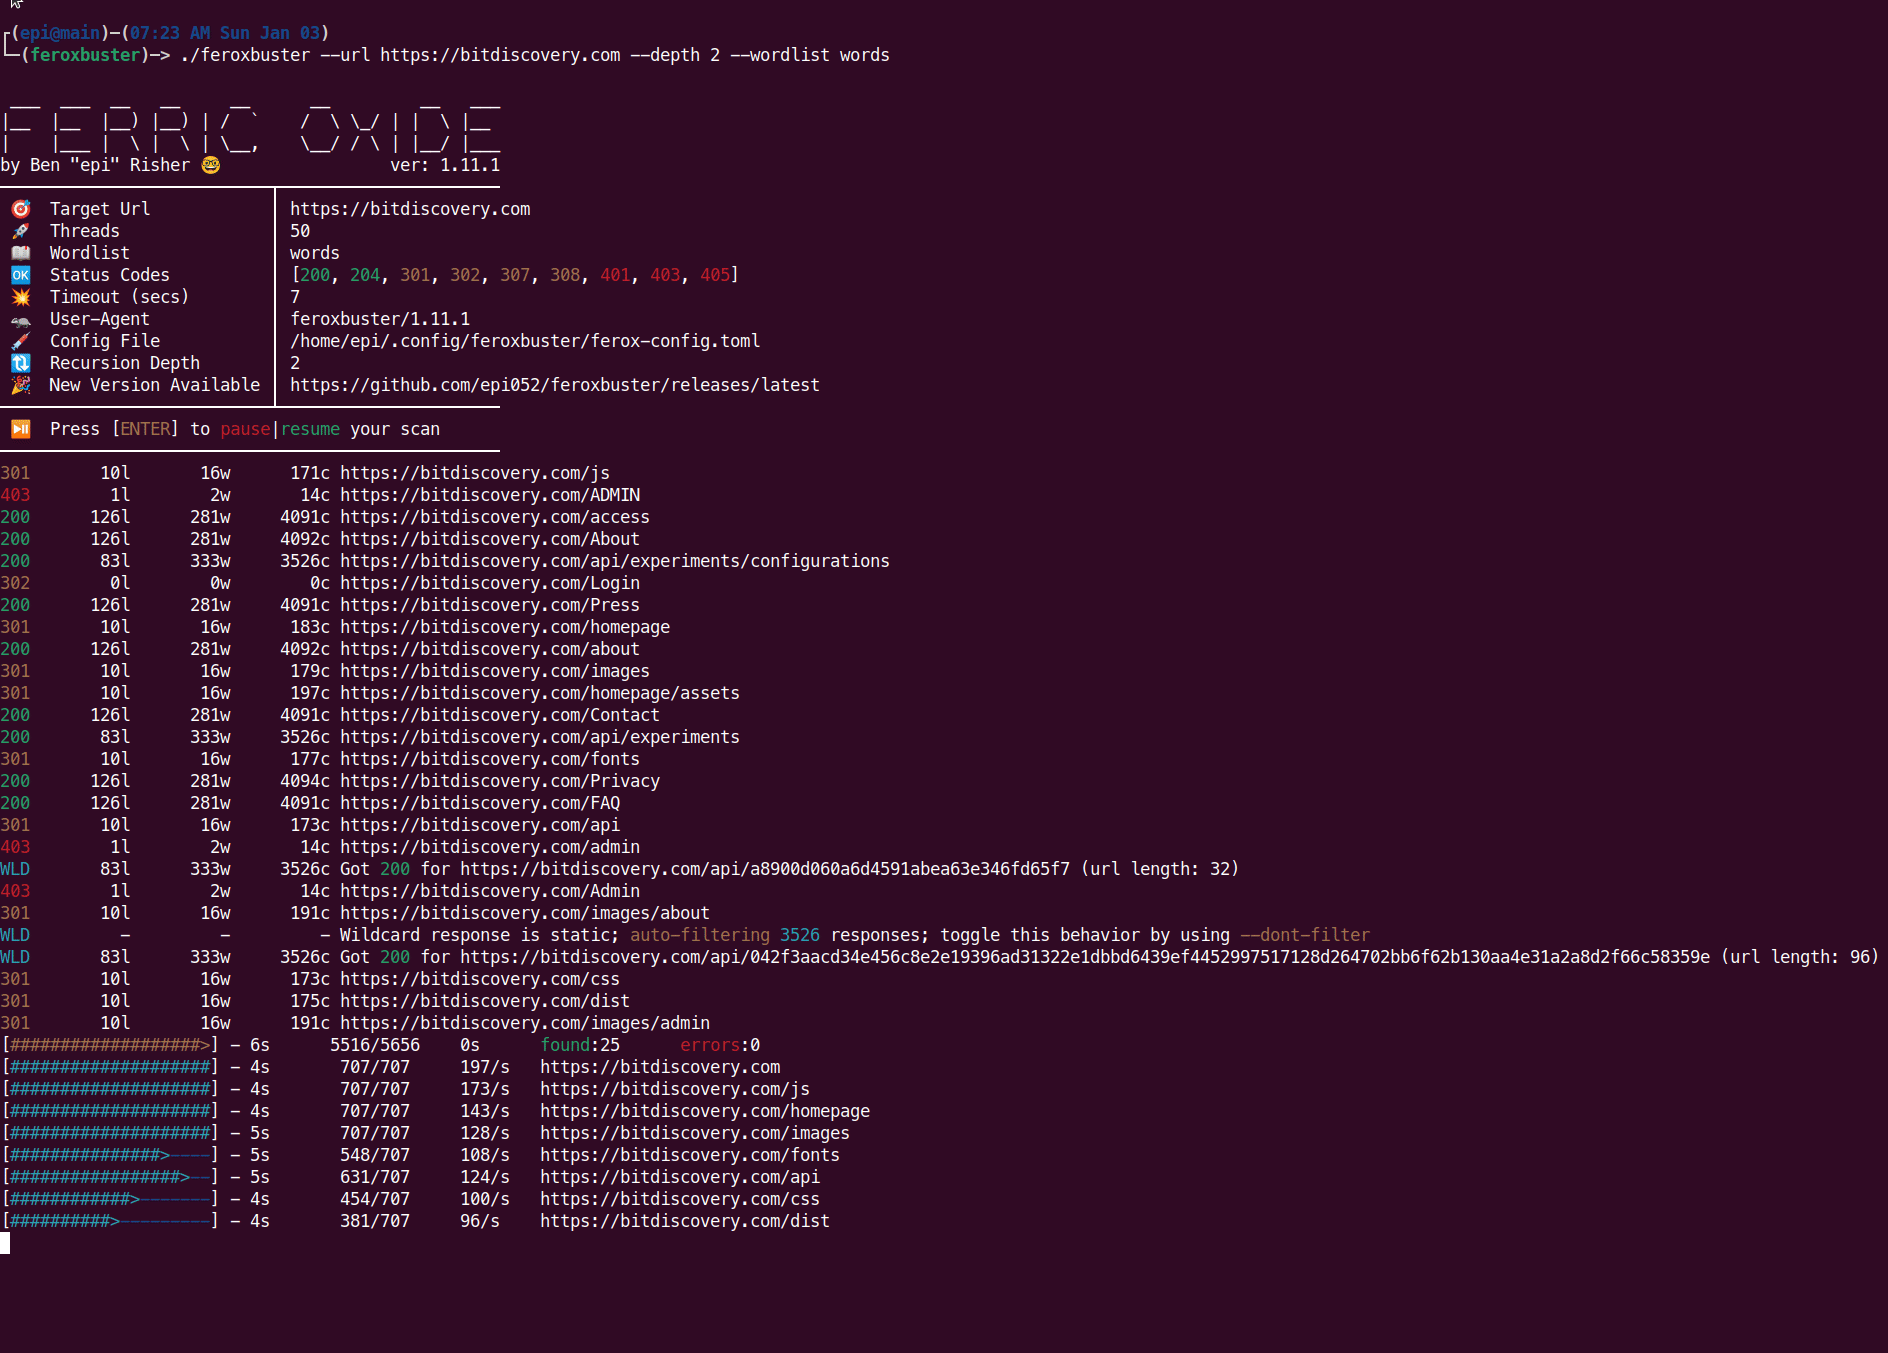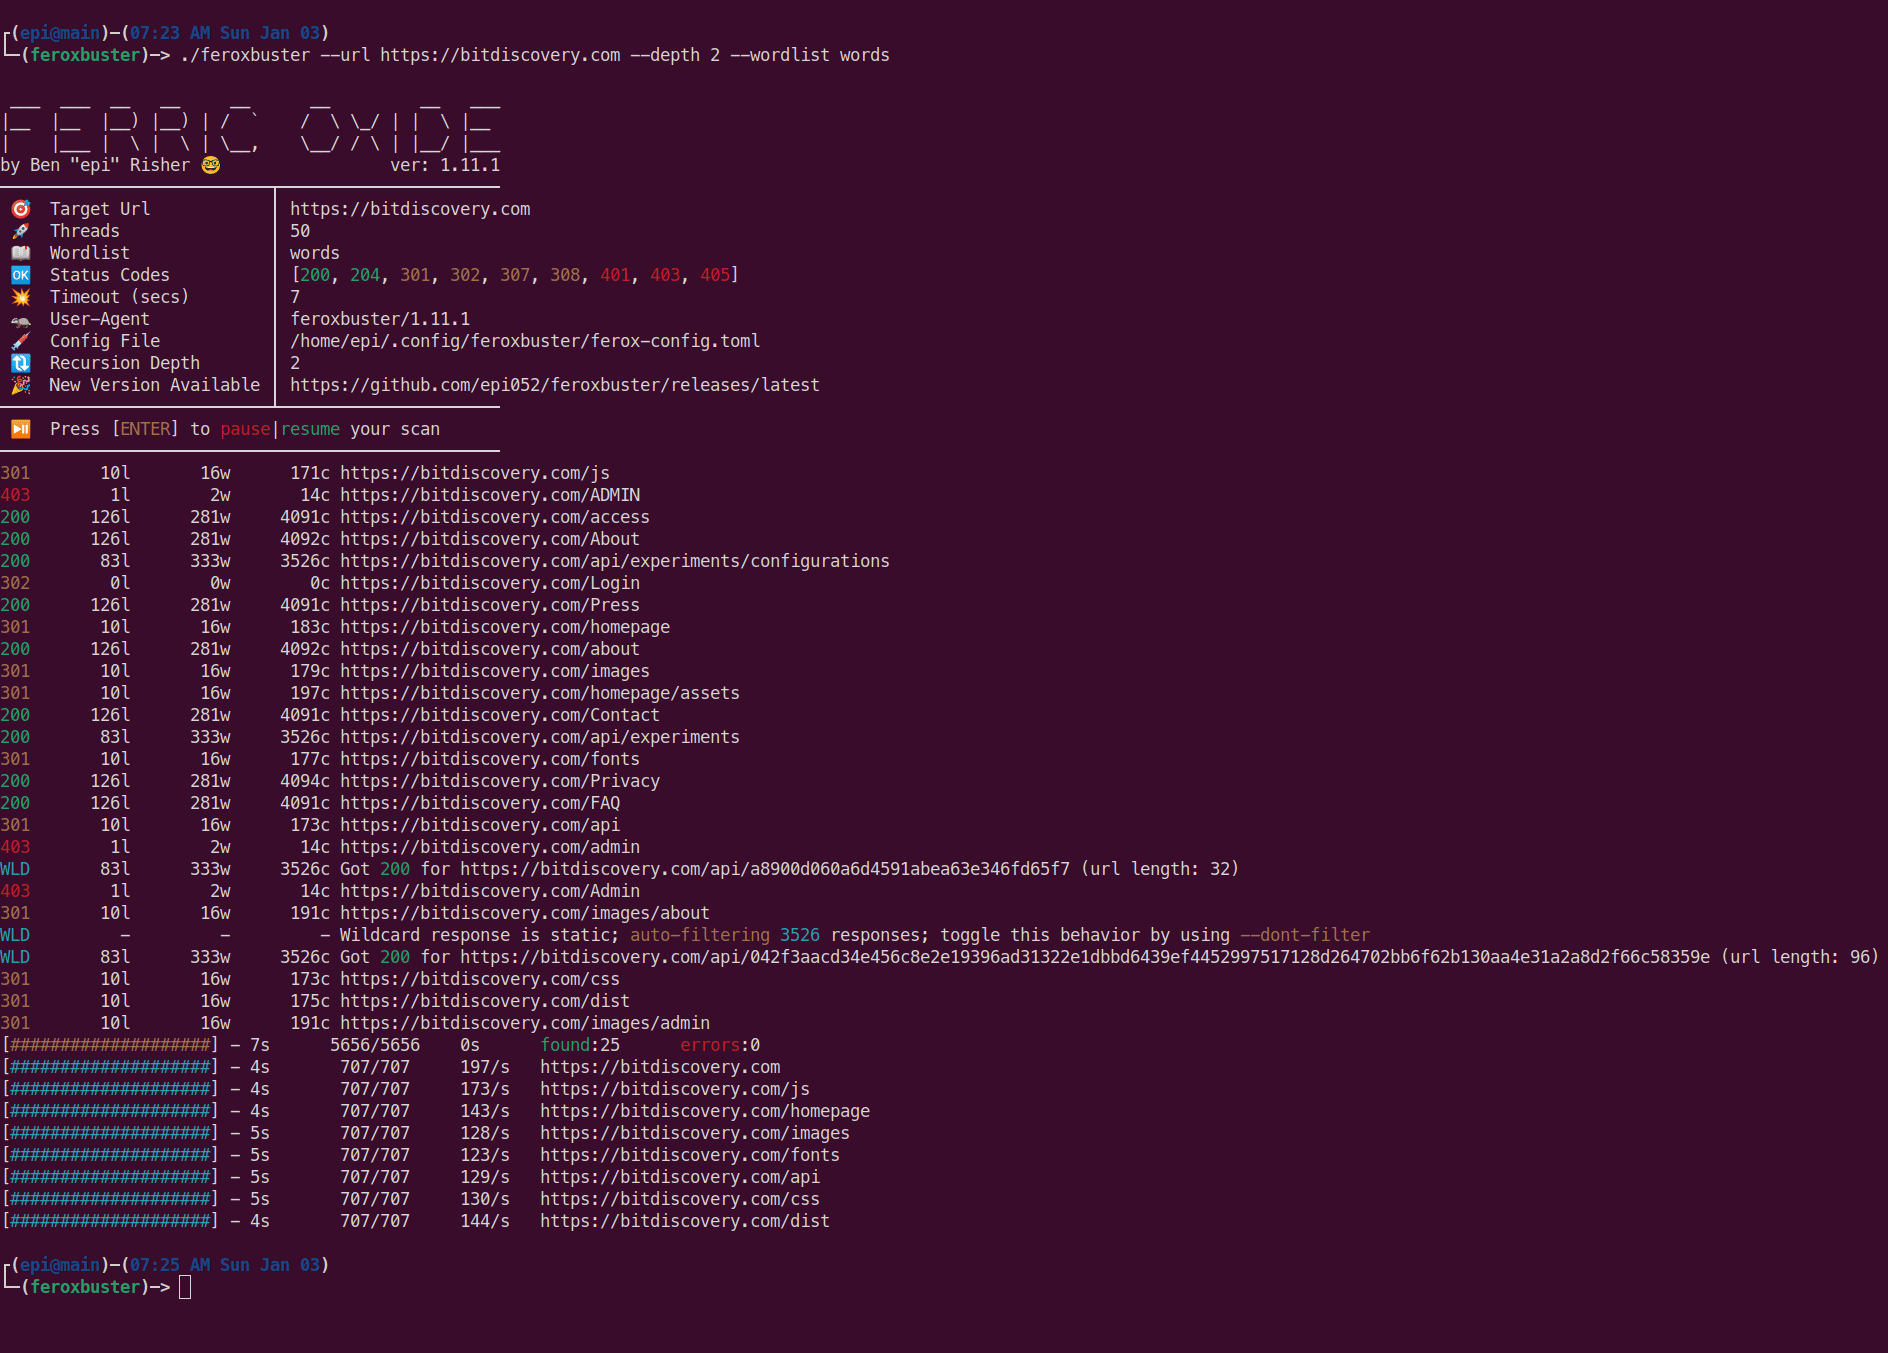 epi052/feroxbuster
A fast, simple, recursive content discovery tool written in Rust.
 khalilbijjou/wafninja
WAFNinja is a tool which contains two functions to attack Web Application Firewalls.
 g0d150ne/wp2shell
Modular WordPress pre-auth exploit framework chaining SQL injection and authentication bypass to deliver remote code execution, interactive shells,…
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
 hakluke/hakoriginfinder
Tool for discovering the origin host behind a reverse proxy. Useful for bypassing cloud WAFs!
 tc4dy/cve-2026-60206-poc-exploit
👾 CVE-2026-60206 - Oracle WebLogic SAML Auth Bypass Exploit Framework ⚡Bash & Python versions. Features: --detect safe check, --exploit…
 tc4dy/cve-2026-6875-poc-exploit
CVE-2026-6875 ServiceNow Pre-Auth RCE Framework 🔥 JS Injection → Sandbox Escape → RCE → Root. Features: --detect, --exec, reverse/interactive shell,…
 nemesida-waf/waf-bypass
Automated WAF security testing tool that detects false positives and false negatives using 15+ payload categories including SQLi, XSS, RCE, and…