
impersonate-proxy
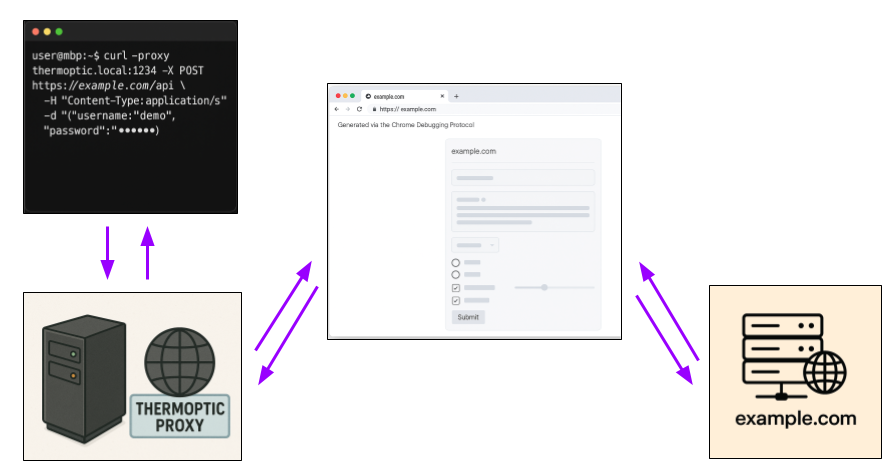
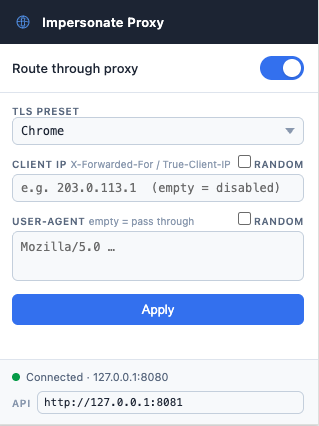
A local MITM proxy that lets you control TLS fingerprints (JA3/JA4), HTTP/2 fingerprints, HTTP header order, and User-Agent — all from a single YAML…

A local MITM proxy that lets you control TLS fingerprints (JA3/JA4), HTTP/2 fingerprints, HTTP header order, and User-Agent — all from a single YAML…

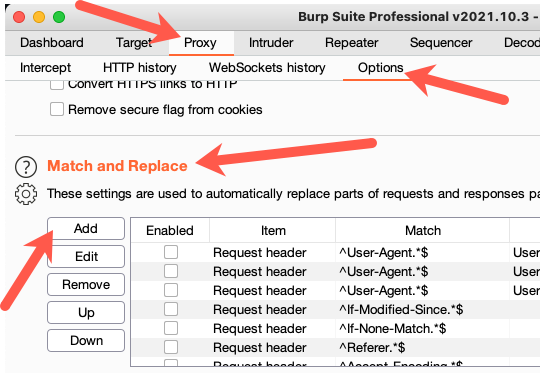
Burp extension to evade TLS fingerprinting. Bypass WAF, spoof any browser.

A next-generation HTTP stealth proxy which perfectly cloaks requests as the Chrome browser across all layers of the stack.

Exploit for Imperva Cloud WAF bypass using gzip Content-Encoding header to evade WAF rules on HTTP POST requests. Includes detection script and…

Demonstrates CVE-2022-31813 Apache HTTP Server bypass using X-Real-IP header manipulation to evade access controls, with a Docker-based test…

ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…

This project demonstrates a Web Application Firewall (WAF) simulation using Flask and a vulnerability checker for CVE-2017-5638. The WAF middleware…

Scanner for the Log4j vulnerability dubbed Log4Shell (CVE-2021-44228)

Python exploit for CVE-2025-64446 targeting FortiWeb WAF, enabling unauthorized user creation and privilege escalation through a crafted HTTP request.

An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.

Stop getting 403 Forbidden. A specialized httpx-like toolkit for WAF evasion.

CVE-2021-40346 PoC (HAProxy HTTP Smuggling)

Nmap NSE script for detecting Apache Log4j RCE (CVE-2021-44228) by injecting JNDI exploit payloads via HTTP headers or TCP/UDP sockets across…

Proof-of-concept for CVE-2024-34102 exploiting unauthenticated Magento XXE and WAF bypass by sending a crafted request to the…

Exploit for CVE-2021-45468, an Imperva WAF bypass.

Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…

Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…

Automated Web Application Firewall fingerprinting tool that identifies and detects over 200 WAF products by analyzing HTTP responses to normal and…