

CVE-2024-4879
 mr-r00t11/cve-2024-4879
CVE-2024-4879.py is a Python script designed to detect specific vulnerabilities in ServiceNow instances and dump database connection details if the…
database-securityexploitationinformation-gathering+3
4
mr-r00t11/cve-2024-4879CVE-2024-4879.py is a Python script designed to detect specific vulnerabilities in ServiceNow instances and dump database connection details if the…
 jdusane/cve-2024-4879
Python script designed to detect specific vulnerabilities in ServiceNow instances and dump database connection details if the vulnerability is found.…
 julioliraup/identificador-cve-2018-11759
Bash script to detect and exploit CVE-2018-11759 in Apache Tomcat instances, with audit logging of target load balancer details, internal addresses,…
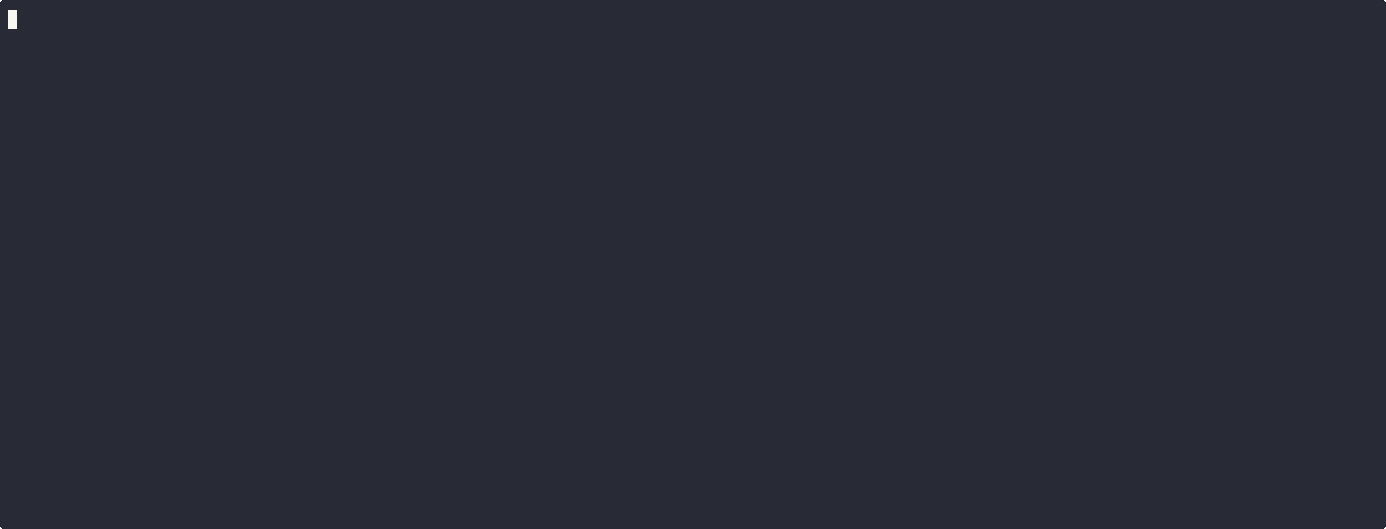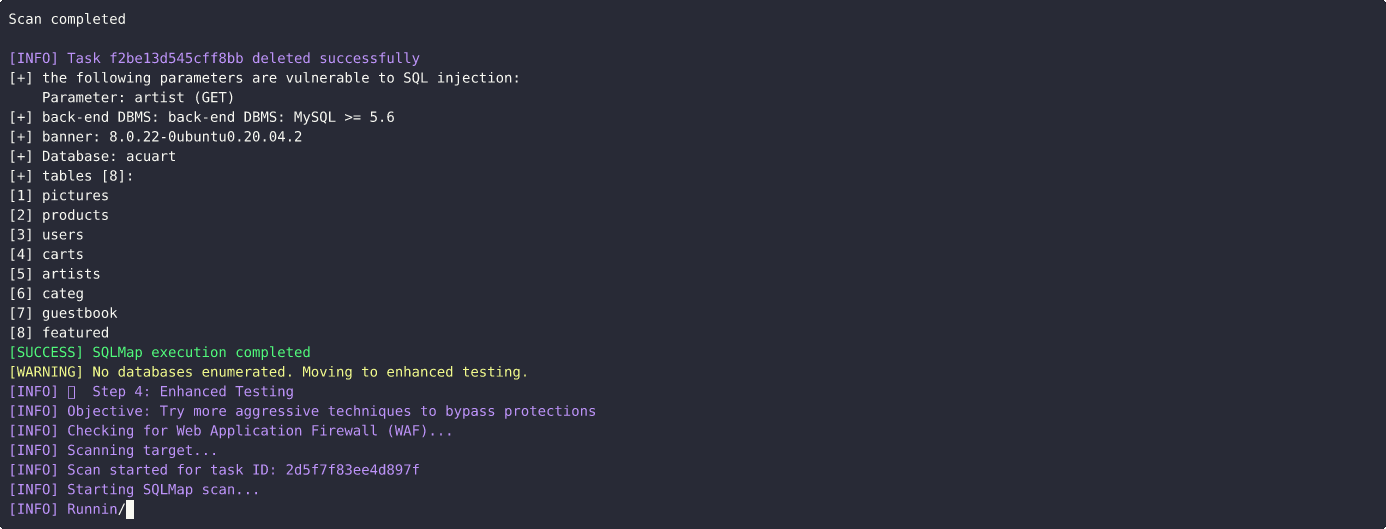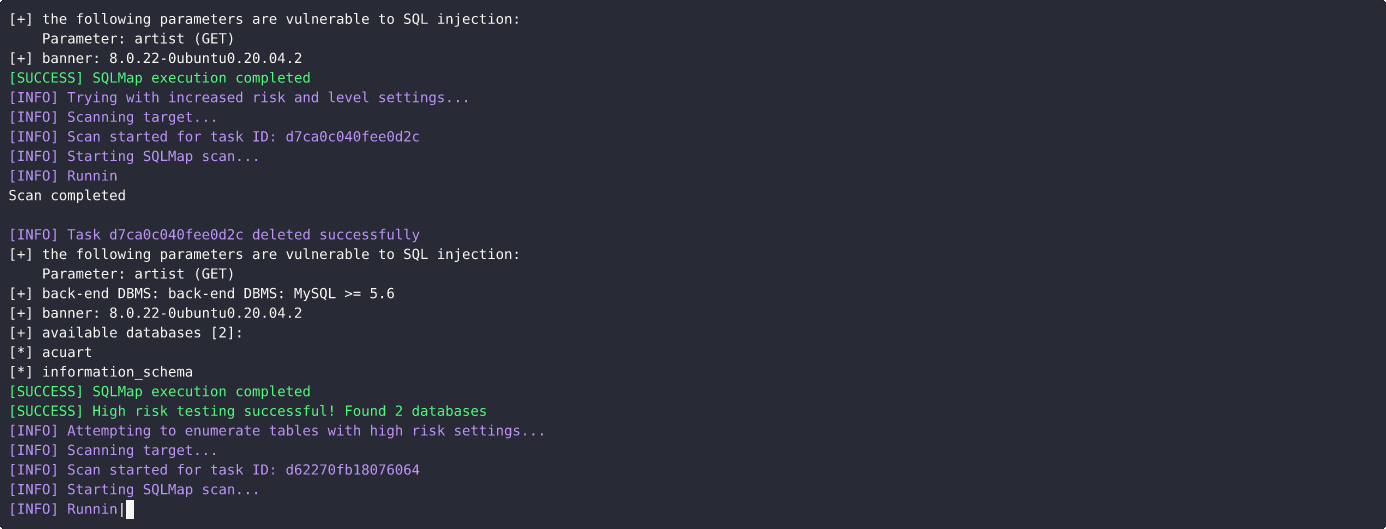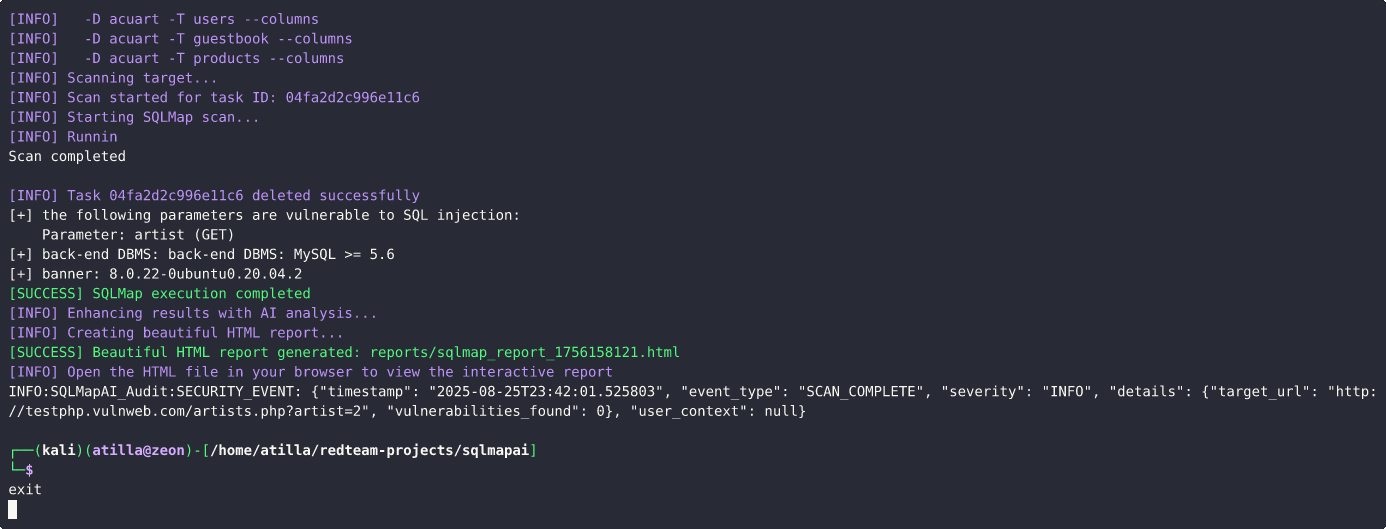 atiilla/sqlmap-ai
This script automates SQL injection testing using SQLMap with AI-powered decision making.
 ruppde/scan_cve-2020-29583
Scanner for Zyxel products which are potentially vulnerable due to an undocumented user account (CVE-2020-29583)
 watchtowrlabs/watchtowr-vs-fortiweb-cve-2025-25257
Detection artifact generator for FortiWeb CVE-2025-25257, exploiting unauthenticated SQL injection to achieve remote code execution via hex-encoded…
 keraattin/cve-2026-39842
Critical remote code execution vulnerability in OpenRemote's Rules Engine allows authenticated users with `write:rules` role to execute arbitrary…
 password123456/ssl-certificate-expiry-date-checker
Scans SSL/TLS certificates for expiry dates, issuer details, and OCSP status. Sends notifications via webhook, Telegram, or Slack. Supports proxy per…
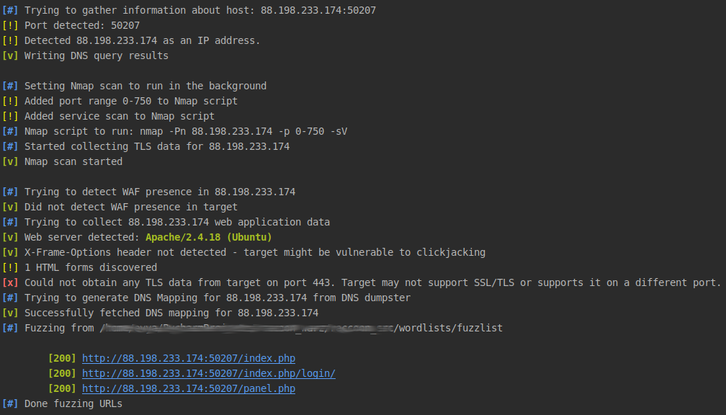 evyatarmeged/raccoon
A high performance offensive security tool for reconnaissance and vulnerability scanning
 pikpikcu/nuubi
Nuubi Tools (Information-ghatering|Scanner|Recon.)
 kal1gh0st/whatsapphack-rce
Exploit for CVE-2019-11932, a remote code execution vulnerability in WhatsApp via malicious GIF files. Includes proof-of-concept code and technical…
 kondordevsecuritycorp/cve-2026-34197
Exploit for Apache ActiveMQ RCE via Jolokia API (CVE-2026-34197) with command output capture, mass scanning, and auto-exploitation.
 mda1r/cve-2026-31278
CVE write-up for Active Directory credential exposure vulnerability in Suprema BioStar 2
 opsecramdan/react2shell-cve-2025-55182
Automated exploitation framework for CVE-2025-55182 (Next.js RCE) with subdomain enumeration, vulnerability scanning, payload generation, and…
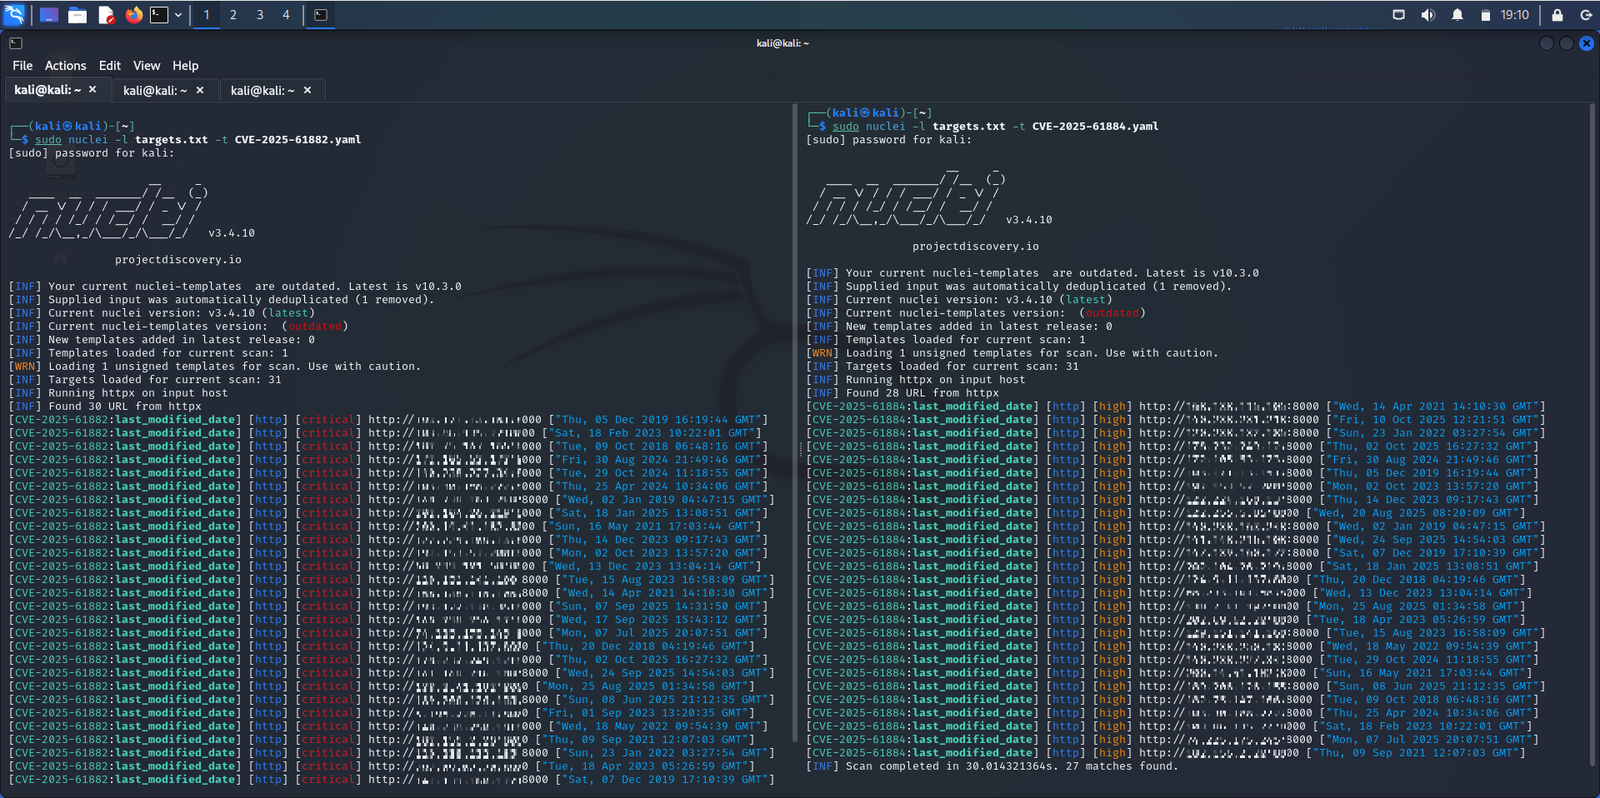 jrexploit/blackash-cve-2025-61884
Provides a detailed summary and detection guidance for CVE-2025-61884, an unauthenticated data disclosure vulnerability in Oracle E-Business Suite…
 zavisco/cve-2026-64849.yaml
Detects unauthenticated MLflow webhook SSRF (CVE-2026-64849) that accesses internal or cloud metadata services and leaks response details via…
 xiaoqimikko/jetty-line-check
CVE-2026-2332 and 4 more 2026 Jetty CVEs: which does your Jetty (or Spring Boot) build hit, and does the fixed version Jetty names even exist on…
 raptoratack/copyfail-scanner-cve-2026-31431
Scans systems for CVE-2026-31431 (CopyFile vulnerability), enumerates system details, evaluates exposure, reports vulnerable status, and optionally…