
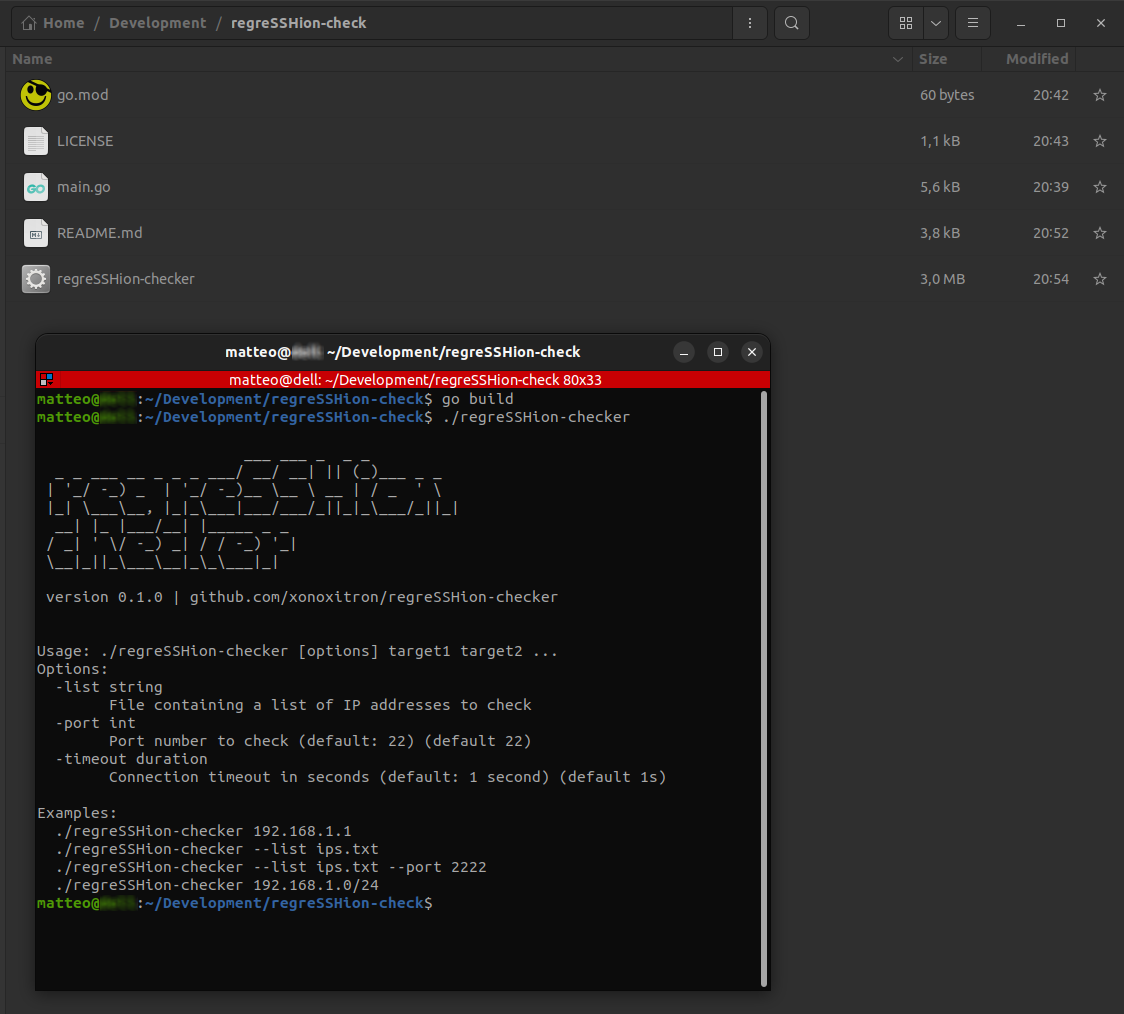
regreSSHion-checker
 xonoxitron/regresshion-checker
Quickly identifies servers vulnerable to OpenSSH 'regreSSHion' (CVE-2024-6387).
exploitationinformation-gatheringnetwork-security+3
10
xonoxitron/regresshion-checkerQuickly identifies servers vulnerable to OpenSSH 'regreSSHion' (CVE-2024-6387).
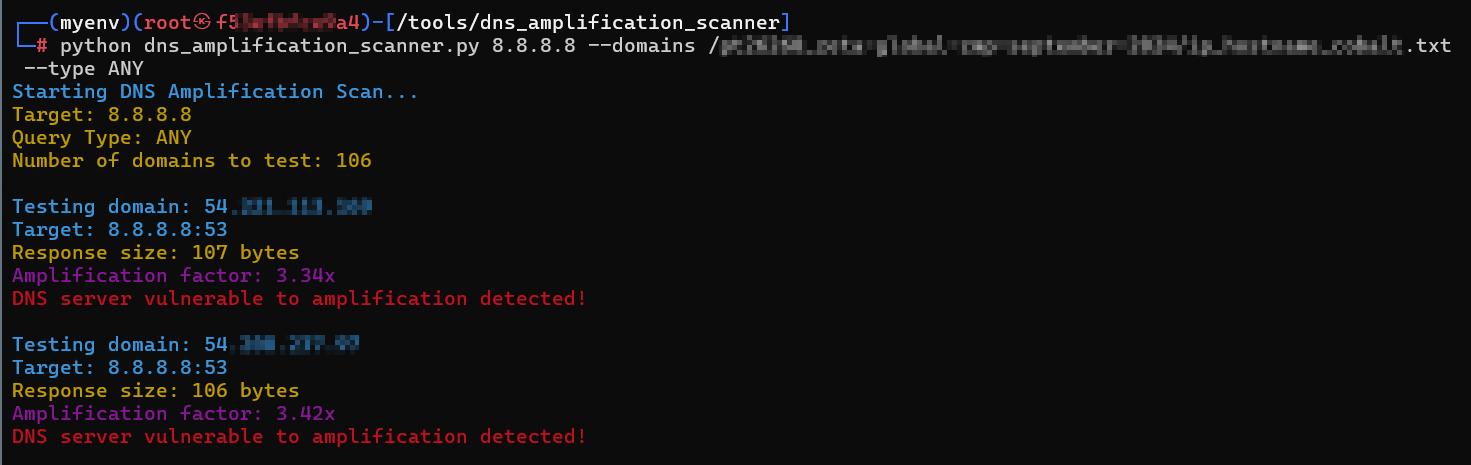 pcastagnaro/dns_amplification_scanner
This script checks if each domain from a given domain list is vulnerable to CVE-2006-0987
 sleepthegod/dns-zone-audit
This Bash script checks domains for DNS zone transfer misconfigurations (CVE-1999-0532). It queries name servers and attempts AXFR requests; if…
 hannob/snallygaster
Tool to scan for secret files on HTTP servers
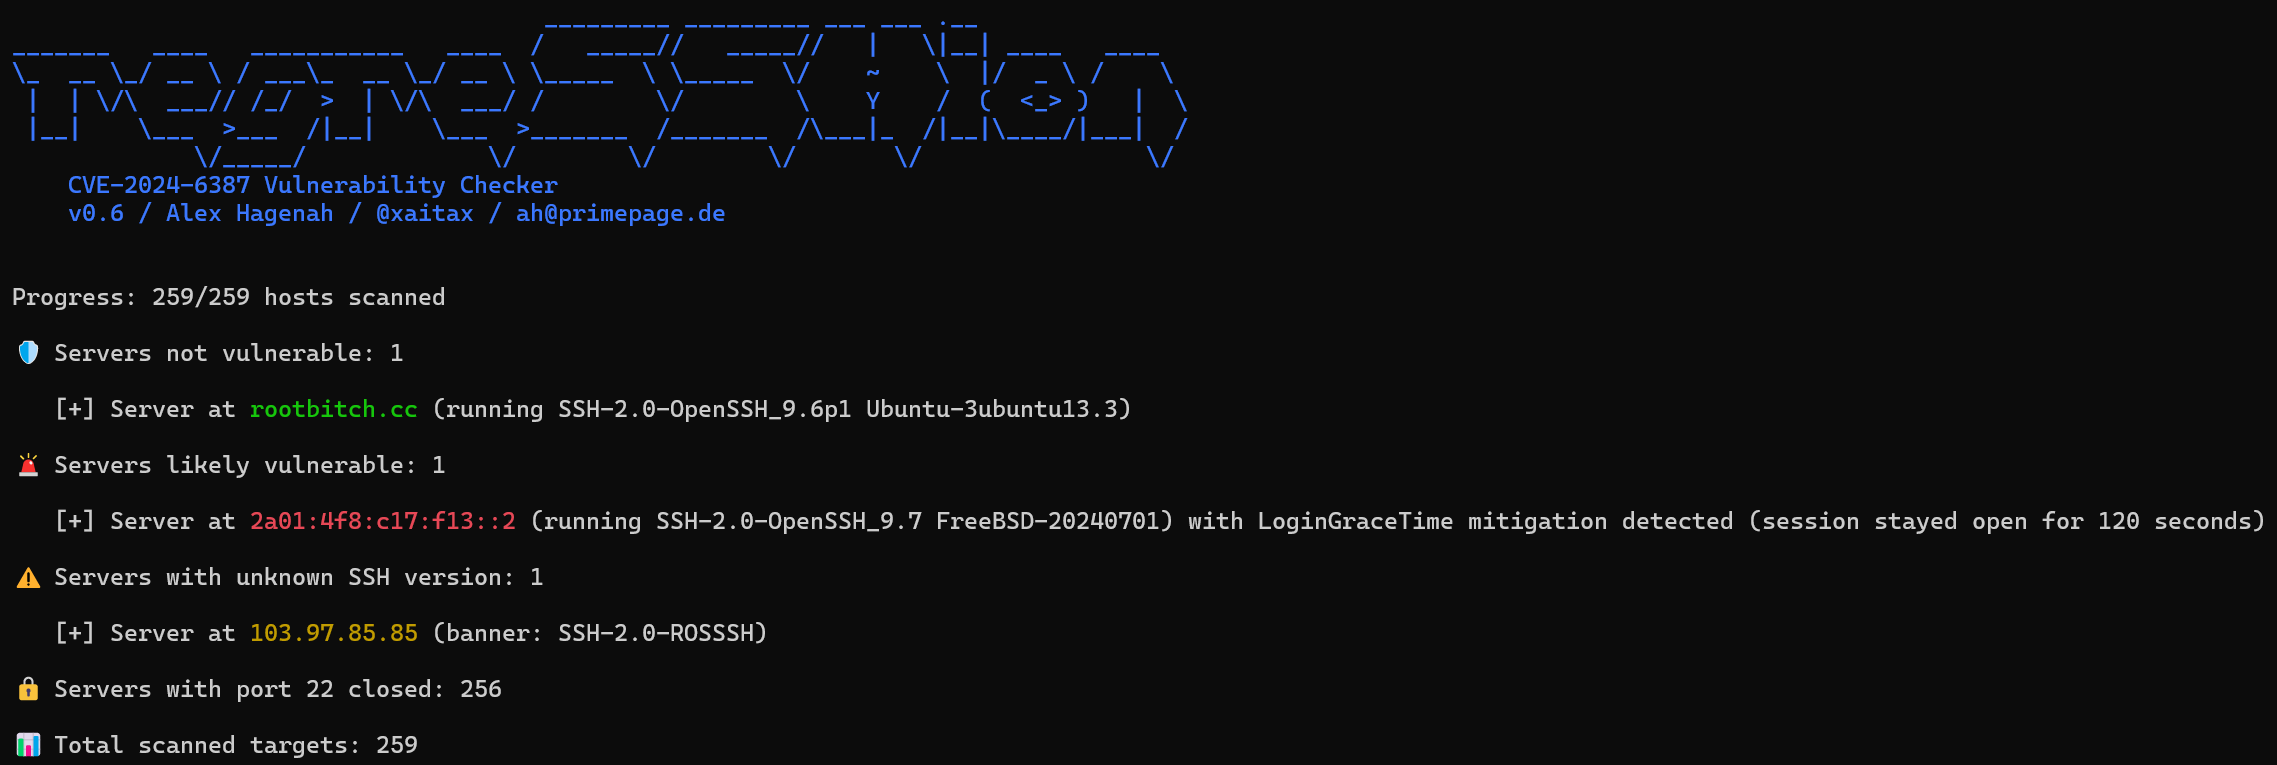 xaitax/cve-2024-6387_check
CVE-2024-6387_Check is a lightweight, efficient tool designed to identify servers running vulnerable versions of OpenSSH
 musana/fuzzuli
Domain-aware URL fuzzer that dynamically generates wordlists to discover exposed backup and sensitive files on web servers.
 xfreed0m/smtptester
small python3 tool to check common vulnerabilities in SMTP servers
 percx/praeda
Automated data harvesting tool for extracting sensitive information (backups, clones, address books) from web servers via targeted scanning and…
 graph-x/davscan
Fingerprints servers, finds exploits, scans WebDAV. May or may not also make coffee.
 jimywork/stretcher
Tool designed to help identify open Elasticsearch servers that are exposing sensitive information
 649/apache-struts-shodan-exploit
This tool takes advantage of CVE-2018-11776 and Shodan to perform mass exploitation of verified and vulnerable Apache Struts servers.
 dani87/ntpscanner
Scans NTP servers for CVE-2013-5211 NTP DDOS amplification vulnerability.
 sakurasamuraii/derailed
CVE-2021-40875: Tools to Inspect Gurock Testrail Servers for Vulnerabilities related to CVE-2021-40875.
 h0ffayyy/cve-2019-15043
Proof-of-concept scanner that checks Grafana servers for CVE-2019-15043 by verifying version and testing unauthenticated snapshot API access.
 wiggels/regresshion-check
CLI Tool to Check SSH Servers for Vulnerability to CVE-2024-6387
 cert-lv/cve-2020-0688
Scans networks for Microsoft Exchange servers vulnerable to CVE-2020-0688, using zmap for host discovery and TLS/version fingerprinting to identify…
 0xhav0c/cve-2013-5211
Python PoC scanner that detects NTP servers vulnerable to CVE-2013-5211 by sending monlist requests and identifying responses that indicate ntpd DoS…
 cybersecurityworks553/cve-2022-3602-and-cve-2022-3786
Python-based scanner that detects OpenSSL 3.0.0-3.0.6 servers vulnerable to CVE-2022-3602 and CVE-2022-3786 by checking client authentication…