

Elkeid
 bytedance/elkeid
Elkeid is an open source solution that can meet the security requirements of various workloads such as hosts, containers and K8s, and serverless. It…
cloud-securityconfiguration-auditingcontainer-security+6
2.7k
bytedance/elkeidElkeid is an open source solution that can meet the security requirements of various workloads such as hosts, containers and K8s, and serverless. It…
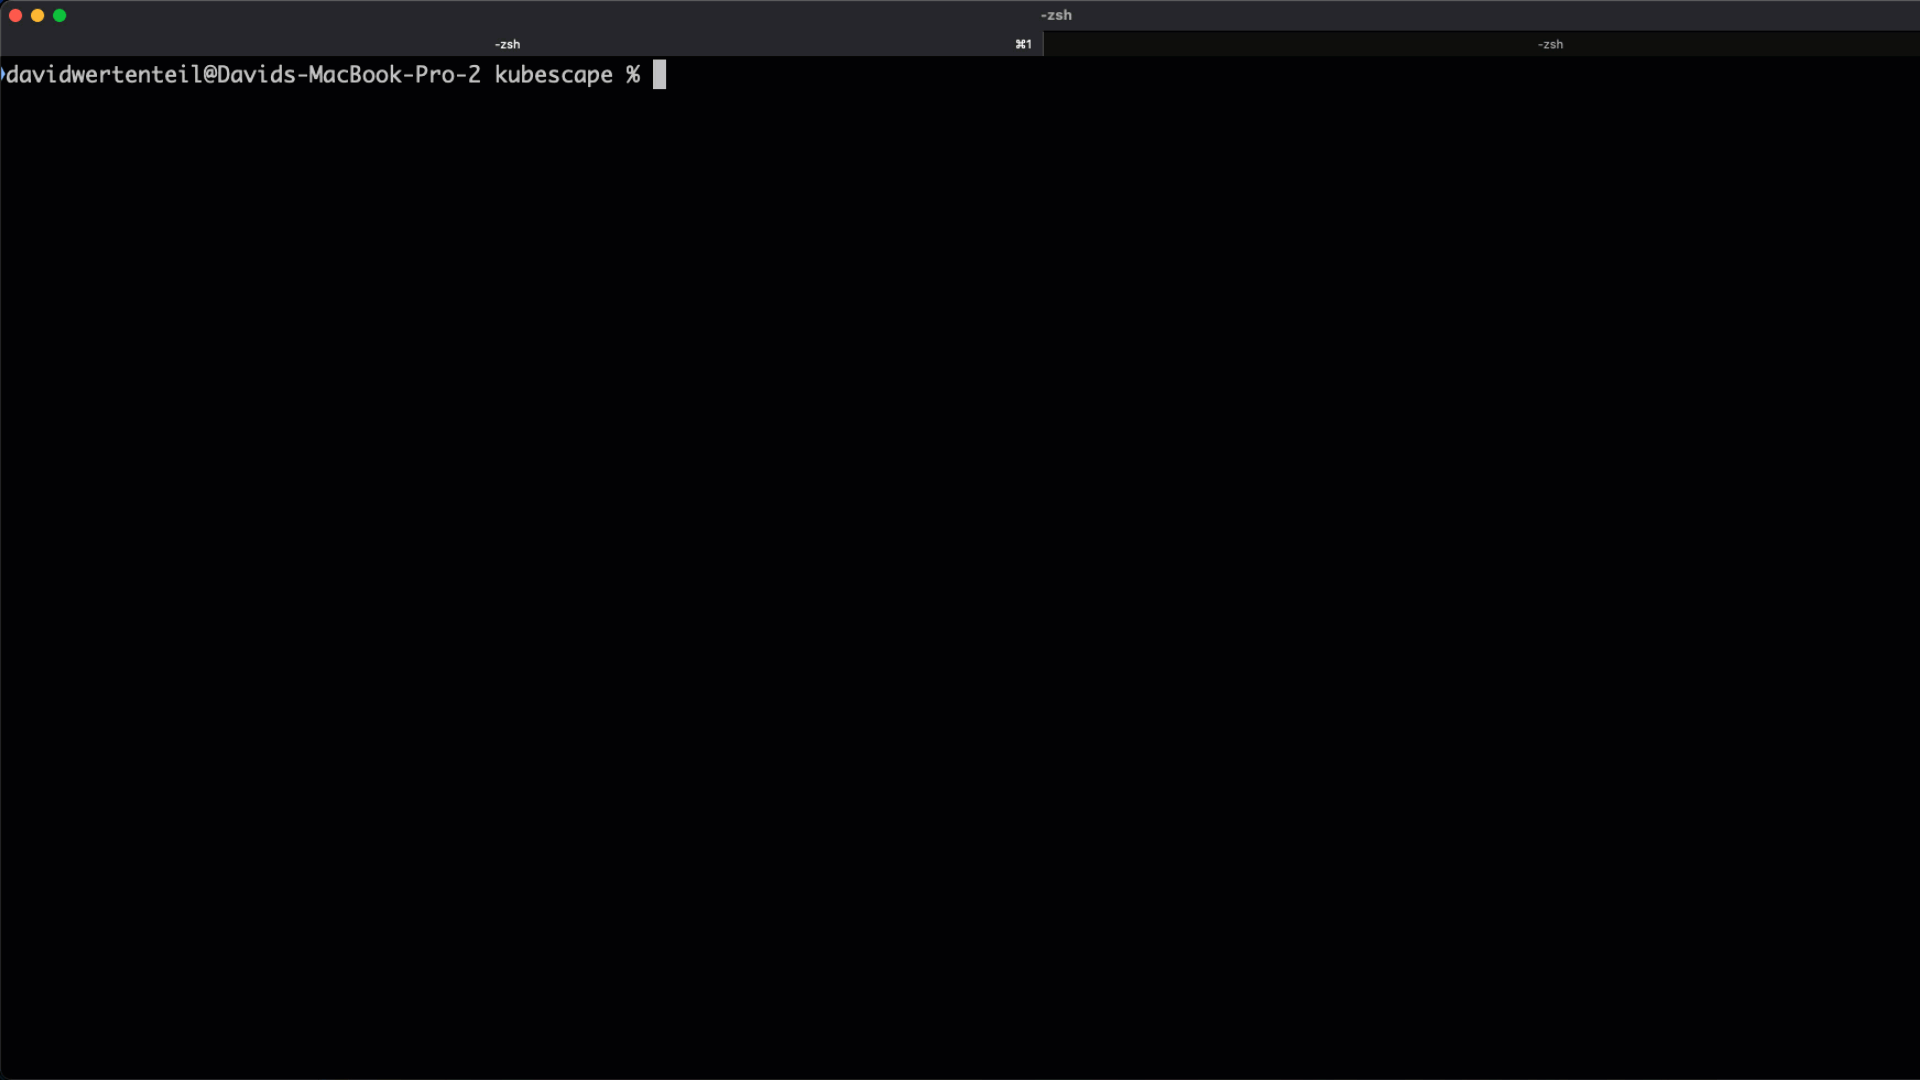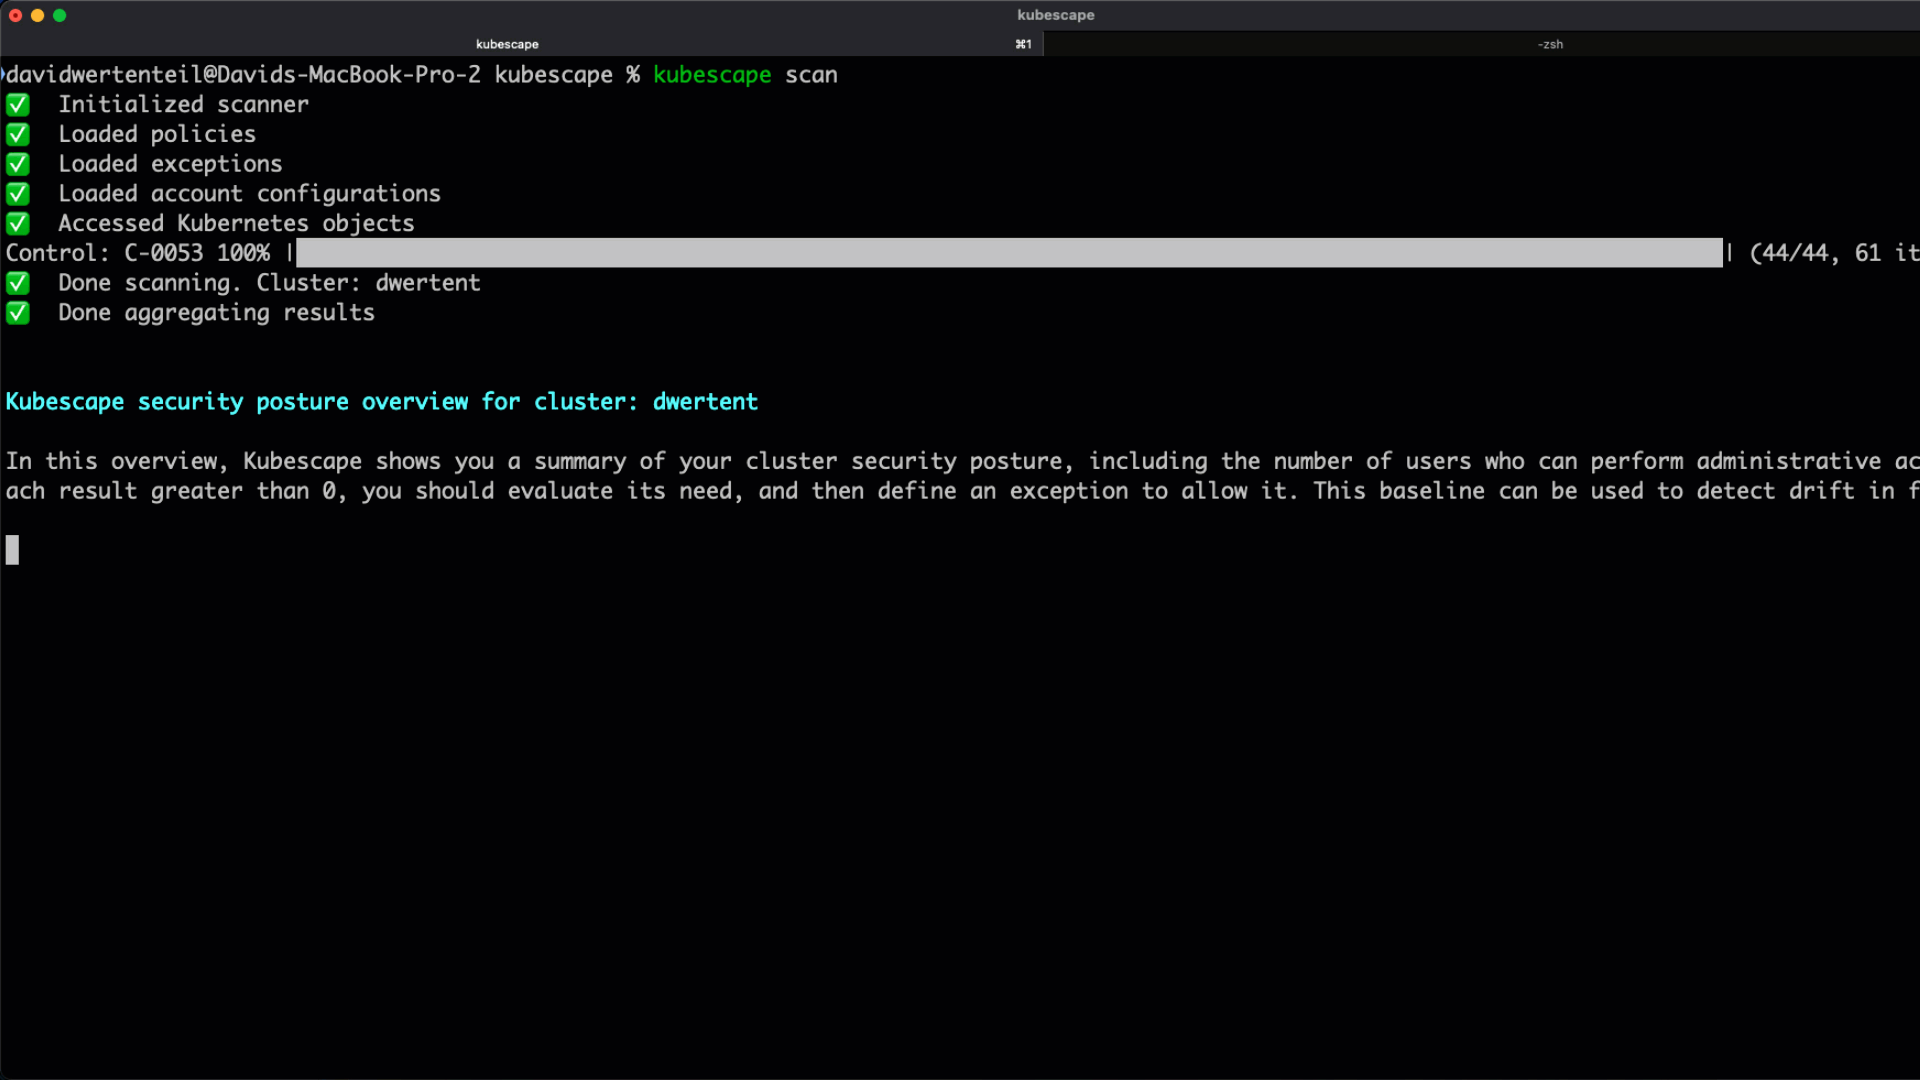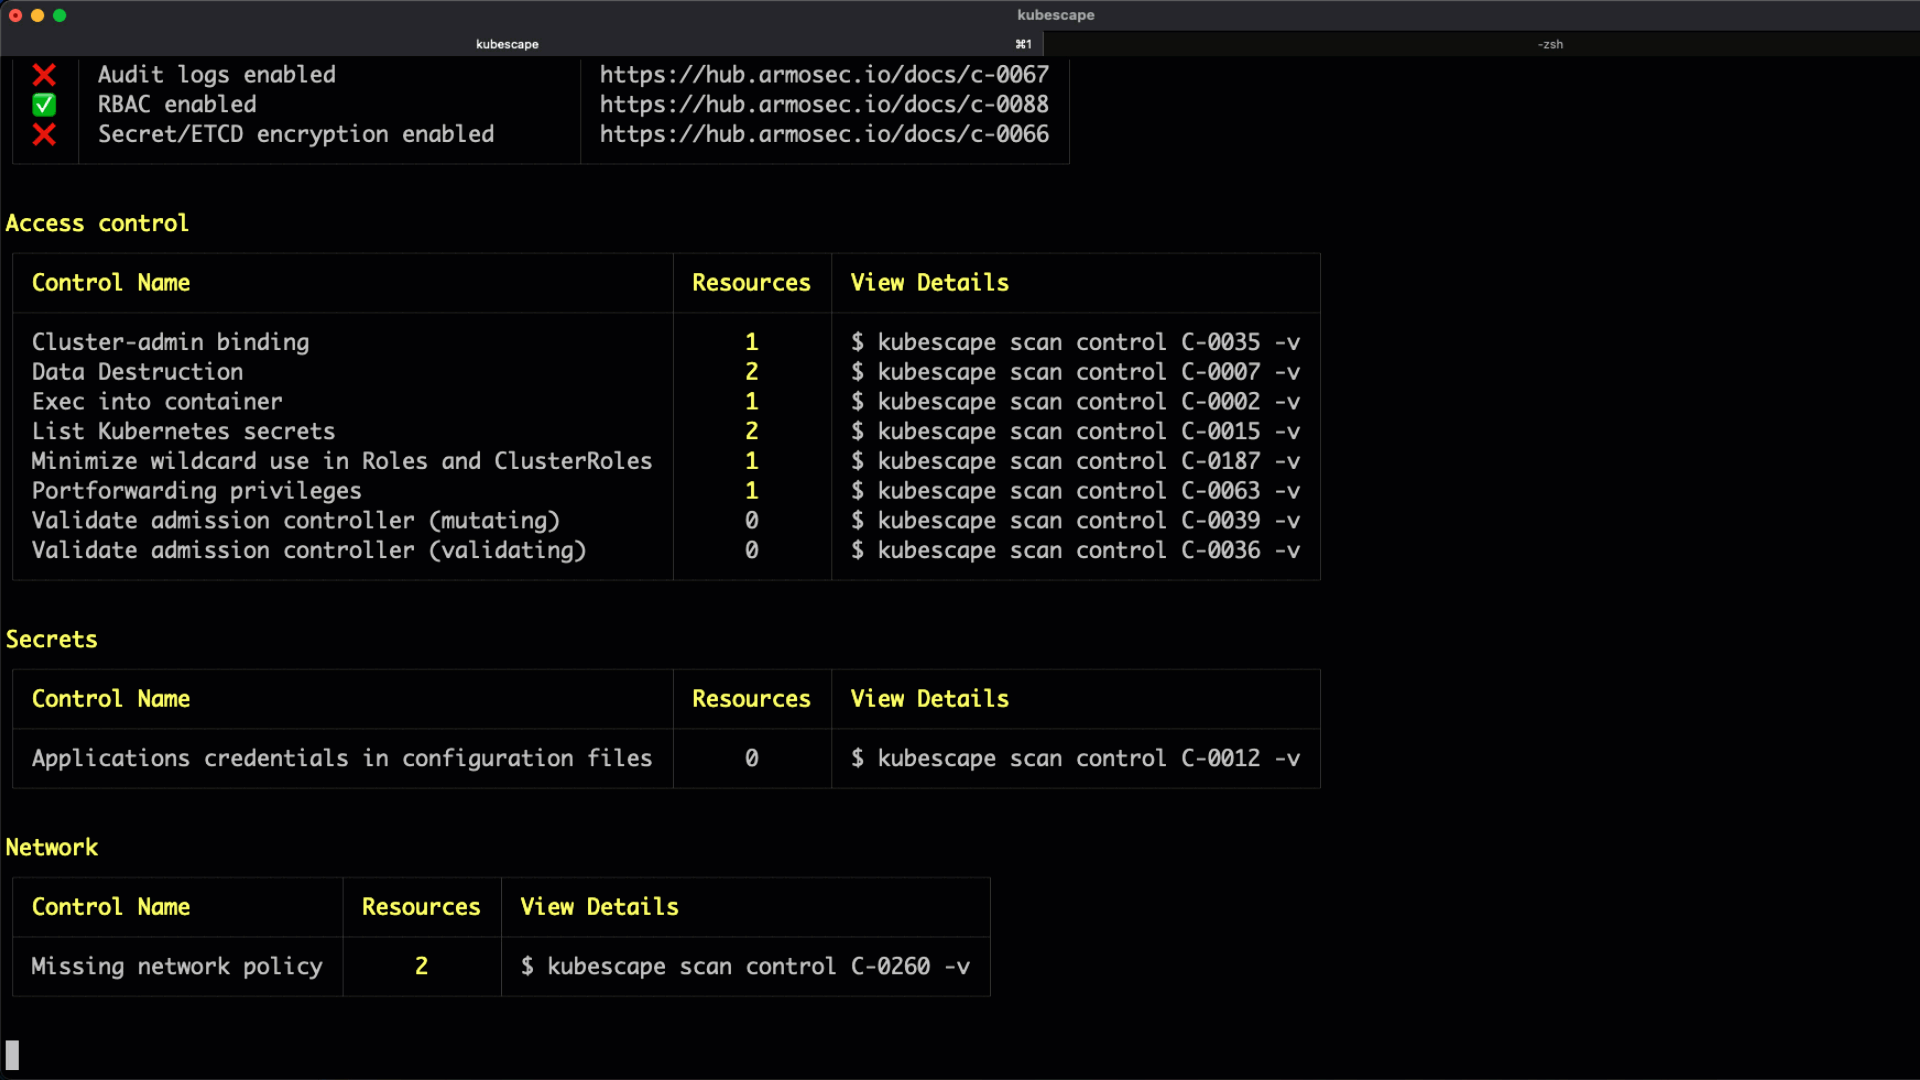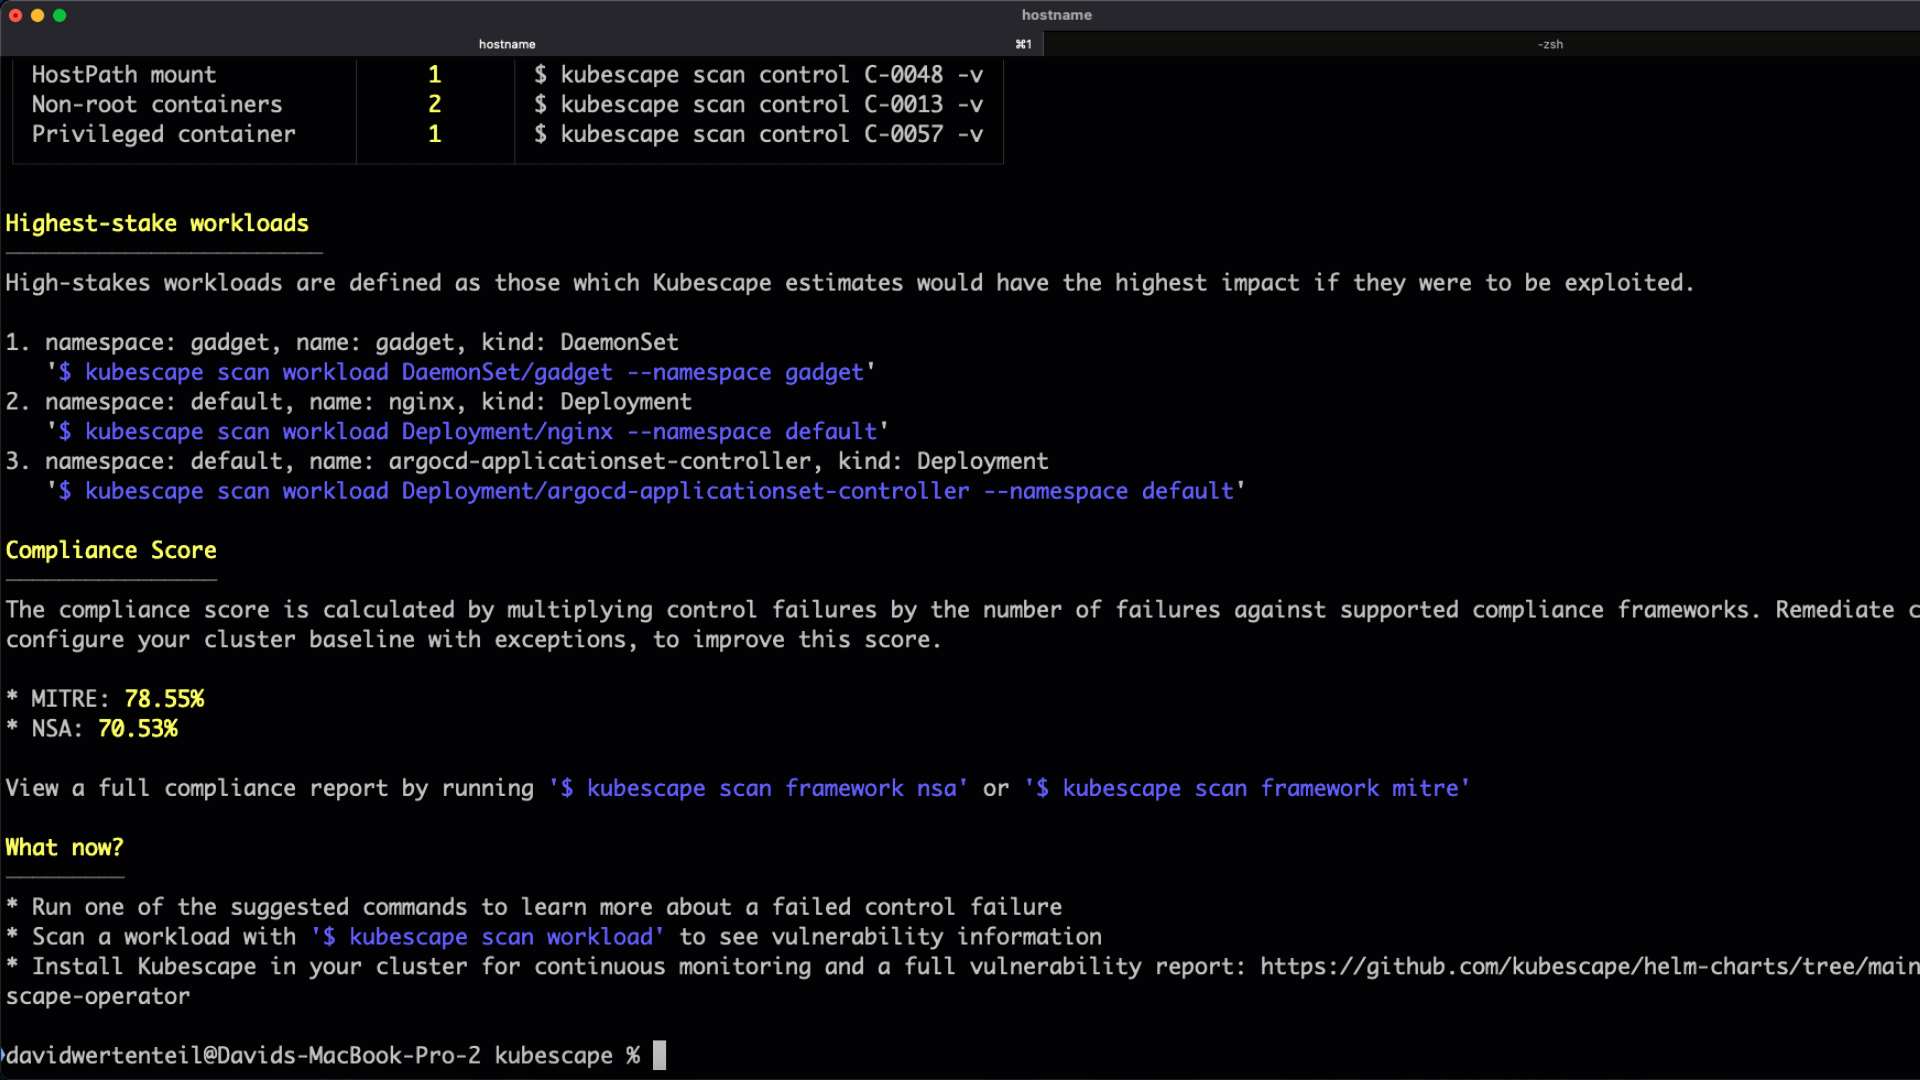 kubescape/kubescape
Open-source Kubernetes security platform scanning clusters, manifests, and images for misconfigurations, vulnerabilities, and compliance against NSA,…
 thestingr/cve-2025-68613-poc
Public PoC + Scanner and research for CVE-2025-68613: Critical RCE in n8n Workflow Automation via Expression Injection (CVSS 10.0). Includes…
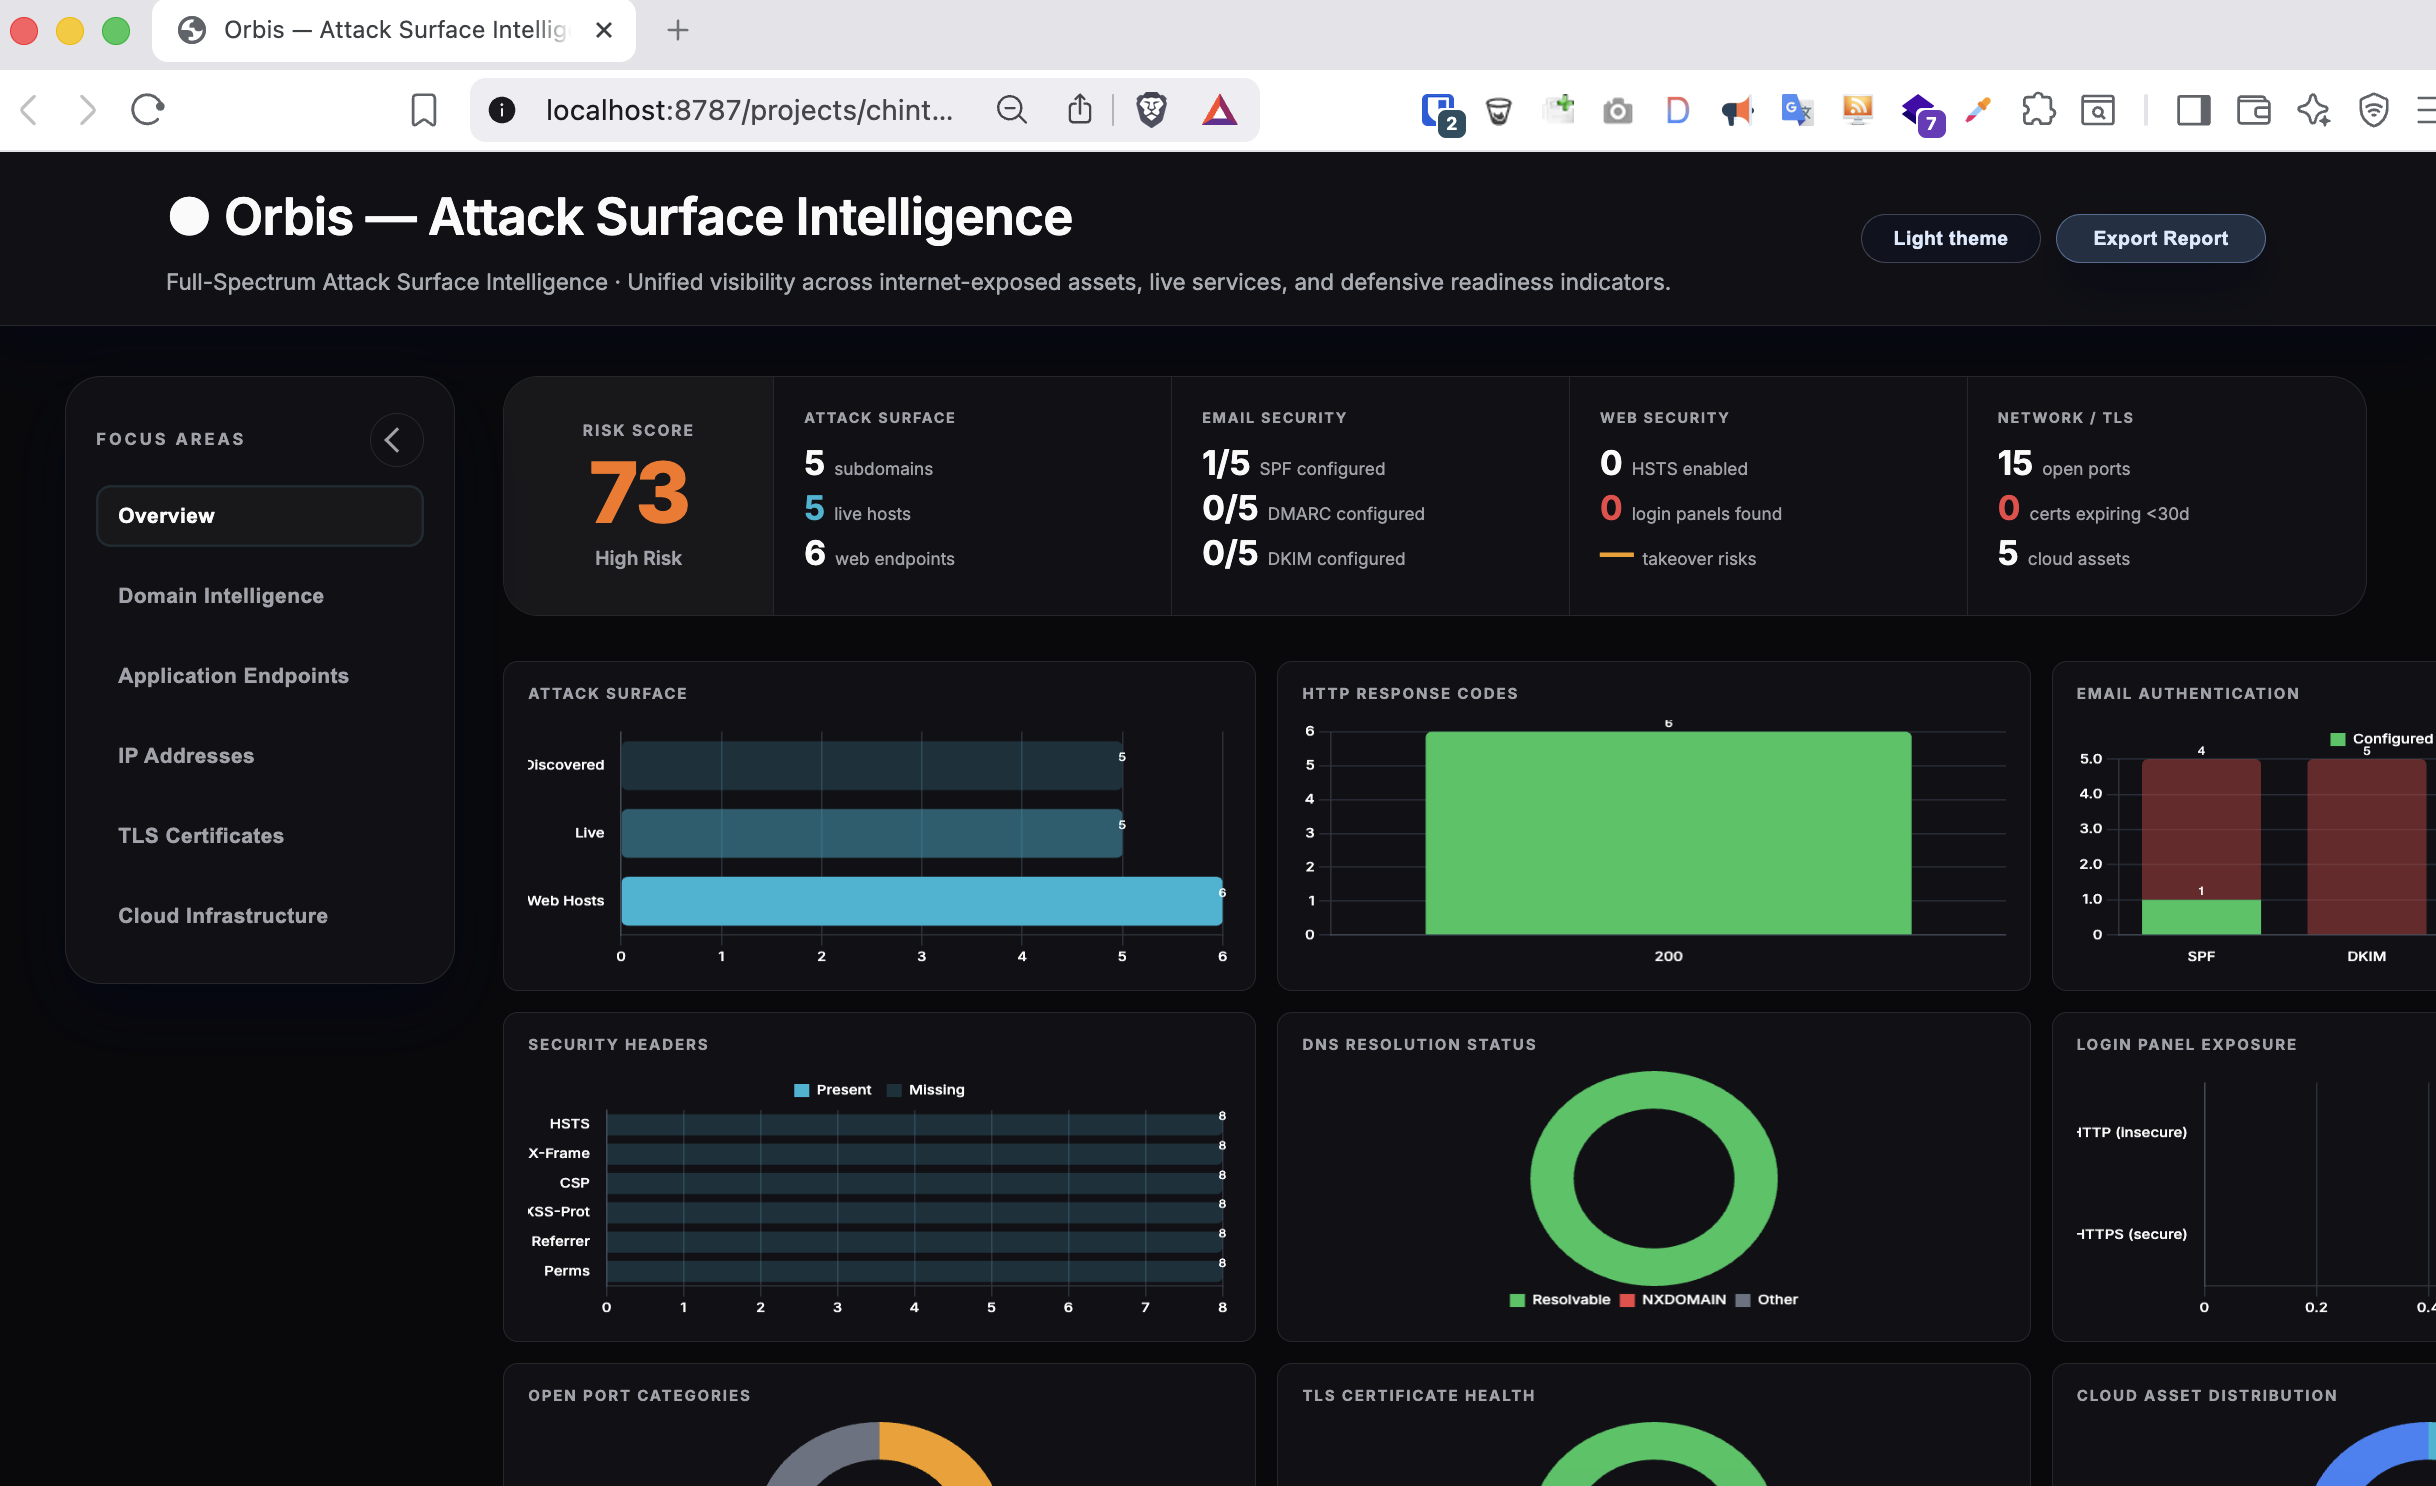 iamthefrogy/frogy2.0
Orbis is an full spectrum automated external attack surface intelligent toolkit.
 spider12223/penscope
Passive recon & attack surface mapper — zero requests sent
 kira2040k/php_code_analysis
Static PHP code scanner that detects SQL injection, XSS, SSRF, LFI, command injection, insecure deserialization, and other web vulnerabilities in…
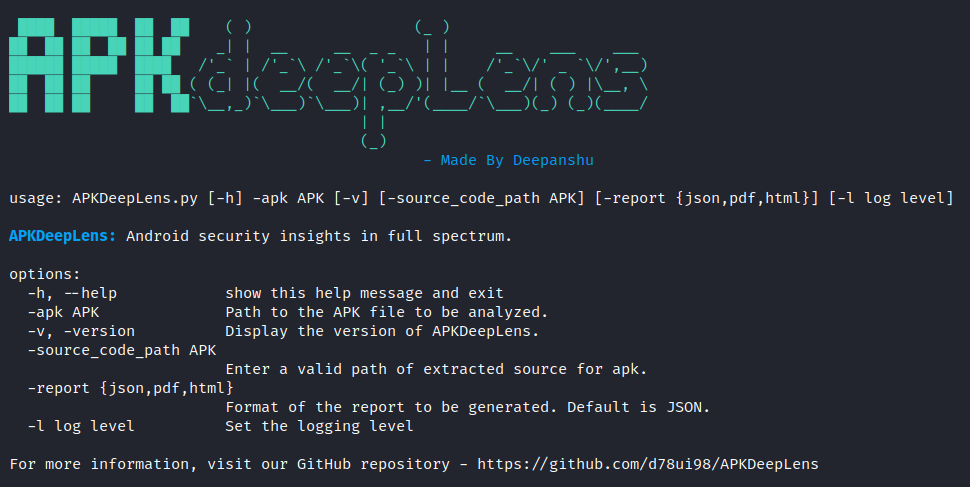 d78ui98/apkdeeplens
Android security insights in full spectrum.
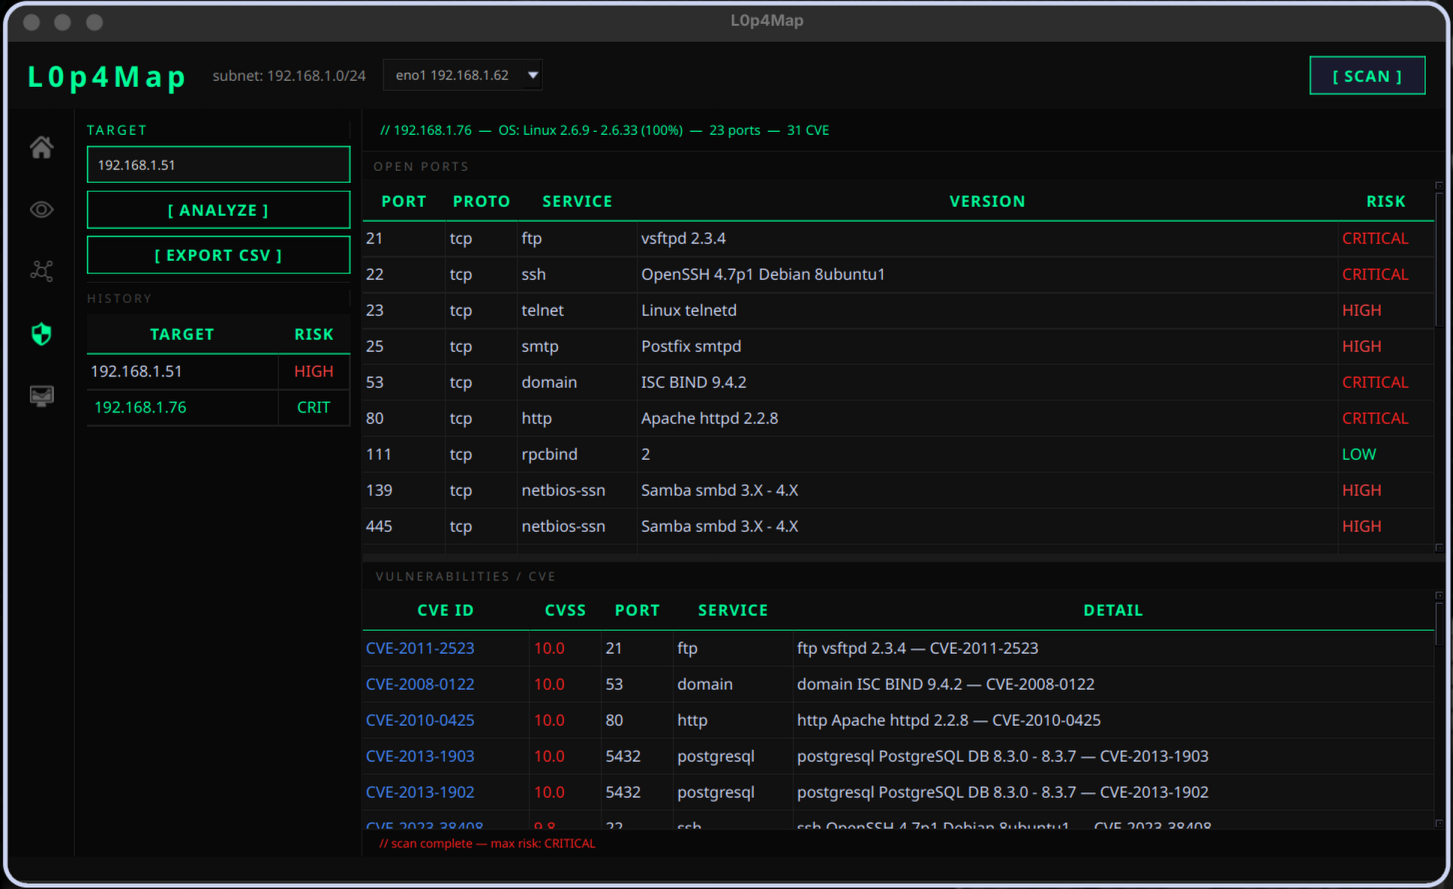 haxl0p4/l0p4map
Professional network monitoring & visualization tool. L0P4Map combines high-speed ARP discovery with full nmap integration and a real-time…
 bitquark/shortscan
Fast IIS short filename enumeration tool that identifies hidden files and directories via tilde vulnerability, with automatic full filename…
 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 spyboy-productions/omnisci3nt
Omnisci3nt is an open-source web reconnaissance and intelligence tool for extracting deep technical insights from domains, including subdomains, SSL…
 snovvcrash/divideandscan
Divide full port scan results and use it for targeted Nmap runs
 dirsoooo/recon
Recon is a script to perform a full recon on a target with the main tools to search for vulnerabilities. Created based on @ofjaaah and @Jhaddix…
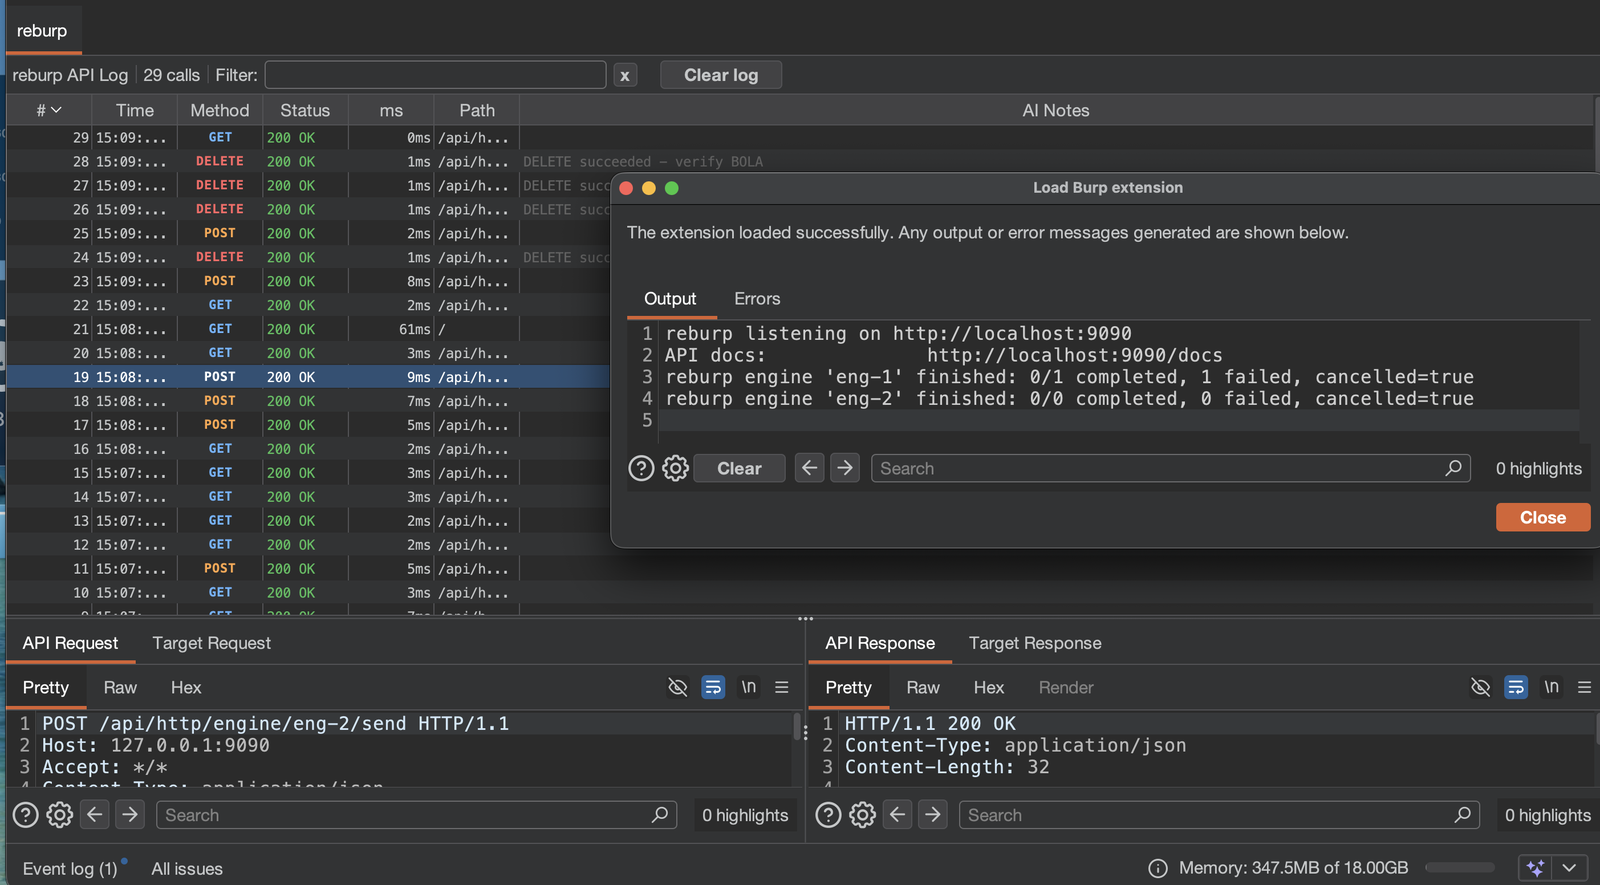 forefy/reburp
A Burp Suite extension that exposes the full Montoya API as a local REST API, with Swagger UI
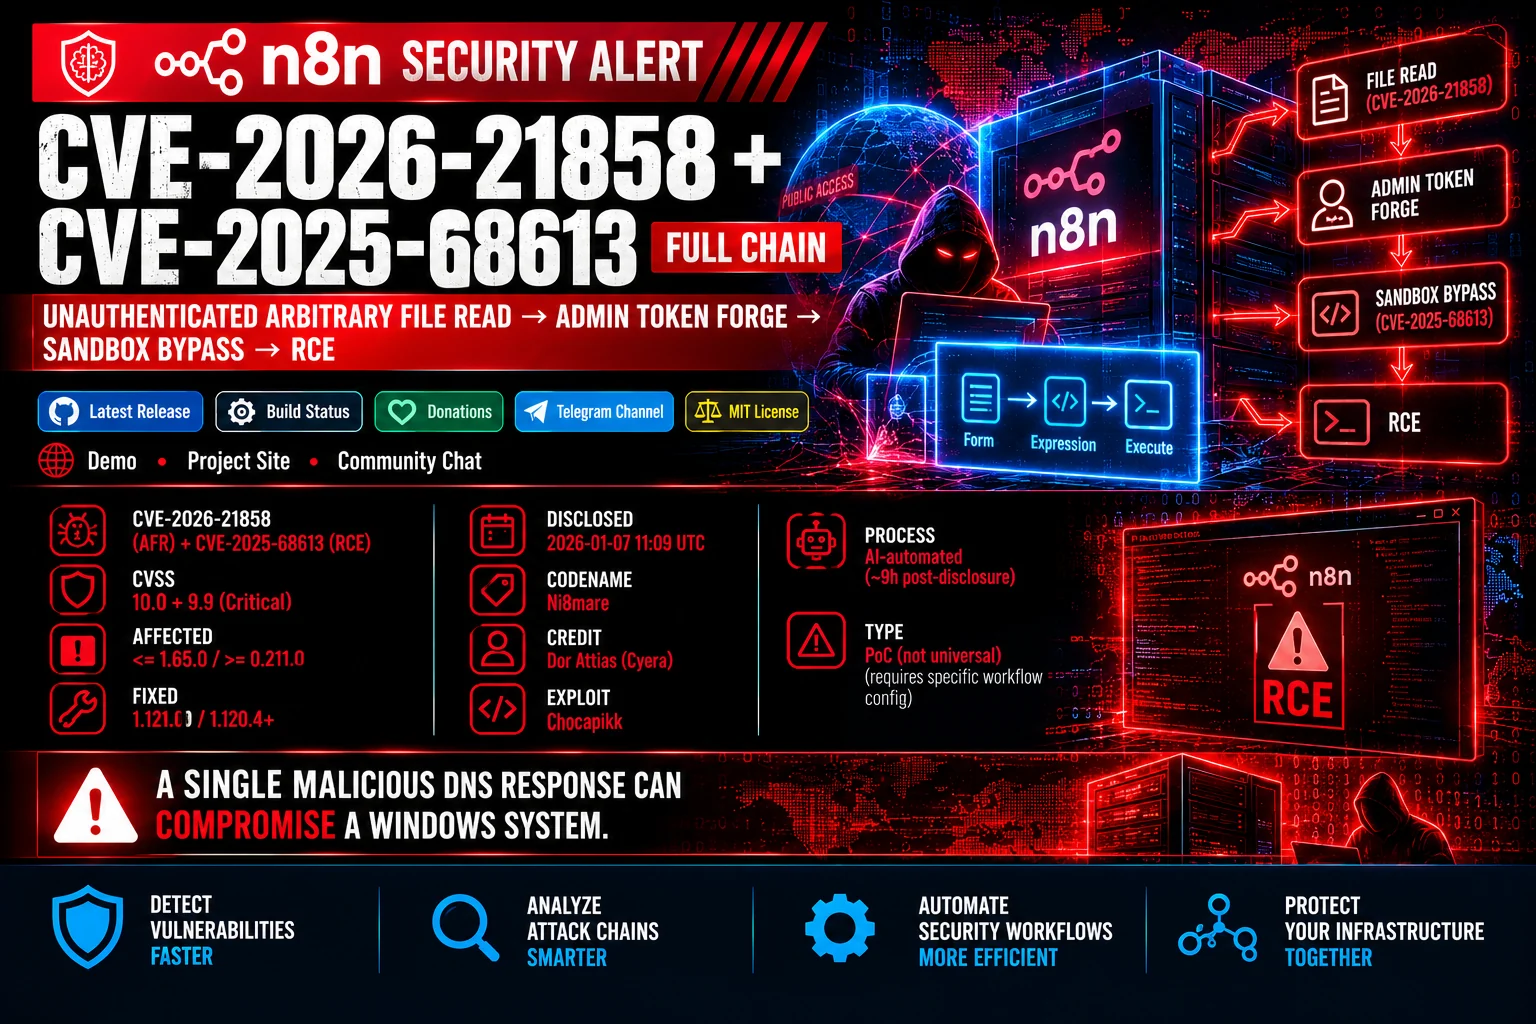 zerodayevil/cve-2026-21858-n8n-fullchain
🛡️ Official AI Security Tool module for CVE-2026-21858 + CVE-2025-68613 (n8n "Ni8mare" Unauthenticated Arbitrary File Read & Expression Injection…
 cspf-founder/api-scanner-docker
Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …
 tc4dy/cve-2026-58048-poc-exploit
👾 CVE-2026-58048 – cPanel Root SQL Execution Toolkit (CVSS 9.4) | Full Red/Blue Team Toolkit suite for unpatched cPanel & WHM 11.x. 2 tools: Safe…
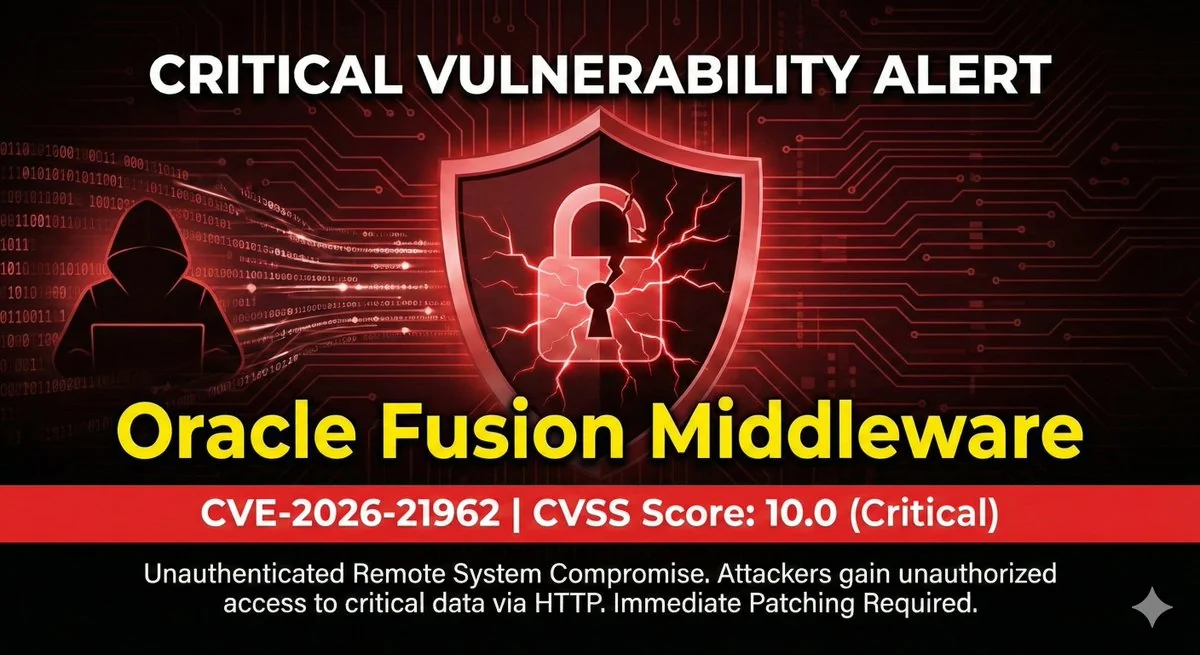 samael0x4/cve-2026-21962
Unauthenticated vulnerability that may allow remote attackers to compromise confidentiality and integrity, potentially leading to full system…